Paid vs. Free subcategories
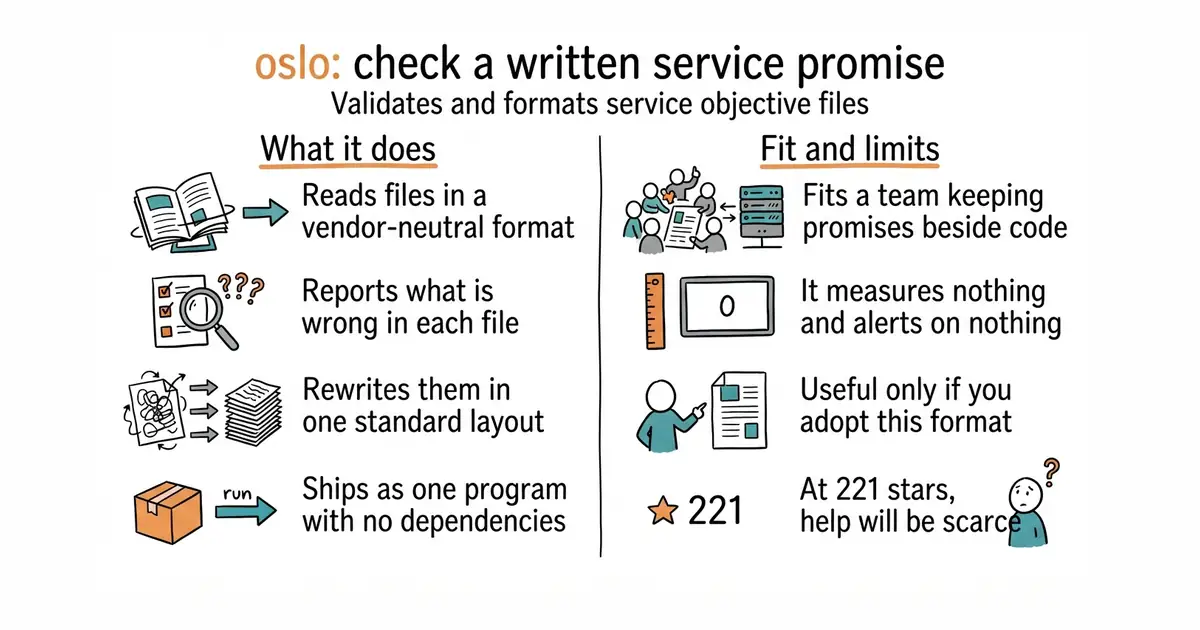

OpenSLO/oslo 💎 hidden gem
A command-line checker and formatter for files that state service level objectives.
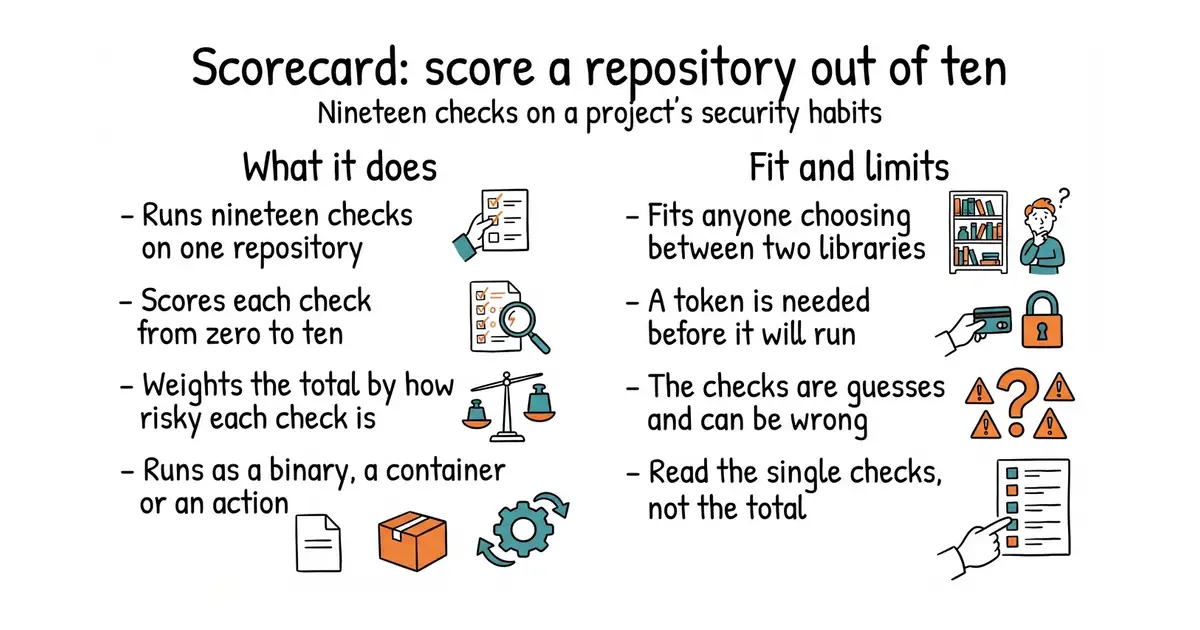

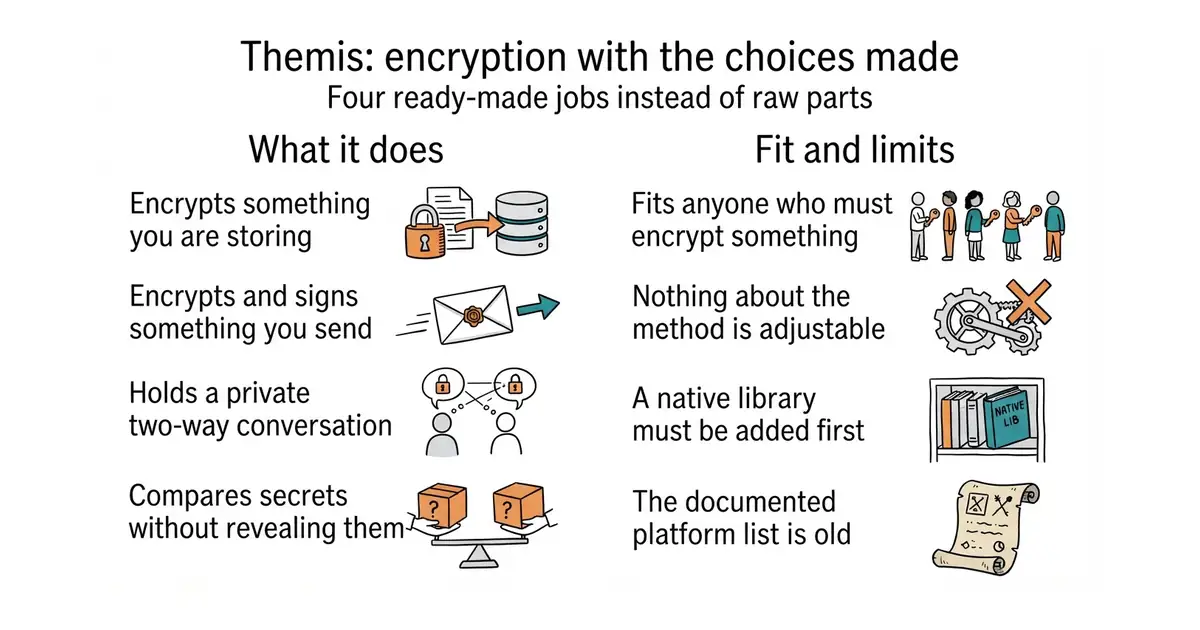

cossacklabs/themis 💎 hidden gem
Four ready-made encryption jobs with the choices already made, in fifteen languages.
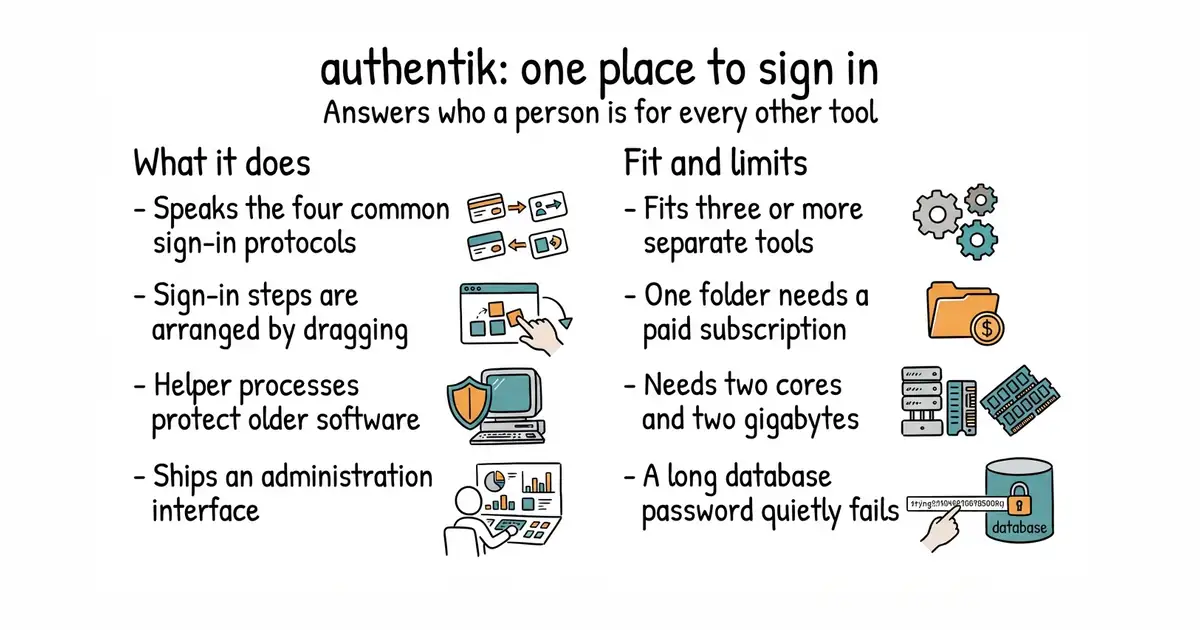

goauthentik/authentik
One place for people to sign in, which every other tool can ask instead of keeping its own passwords.
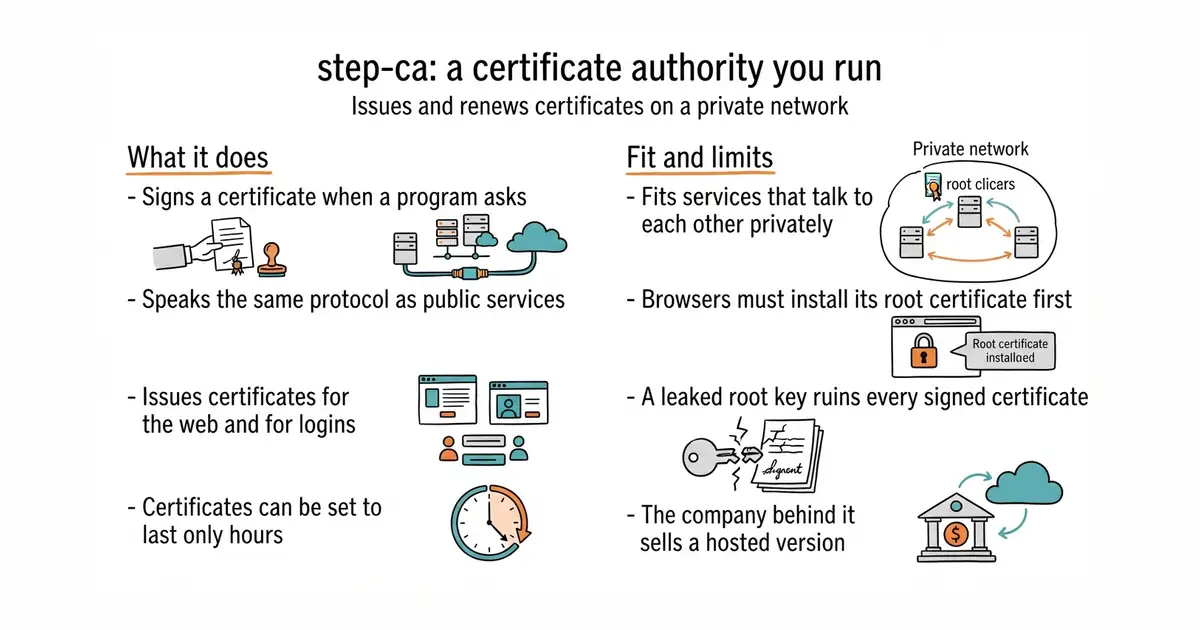

smallstep/certificates
A certificate authority you run yourself, for machines the public internet cannot reach.
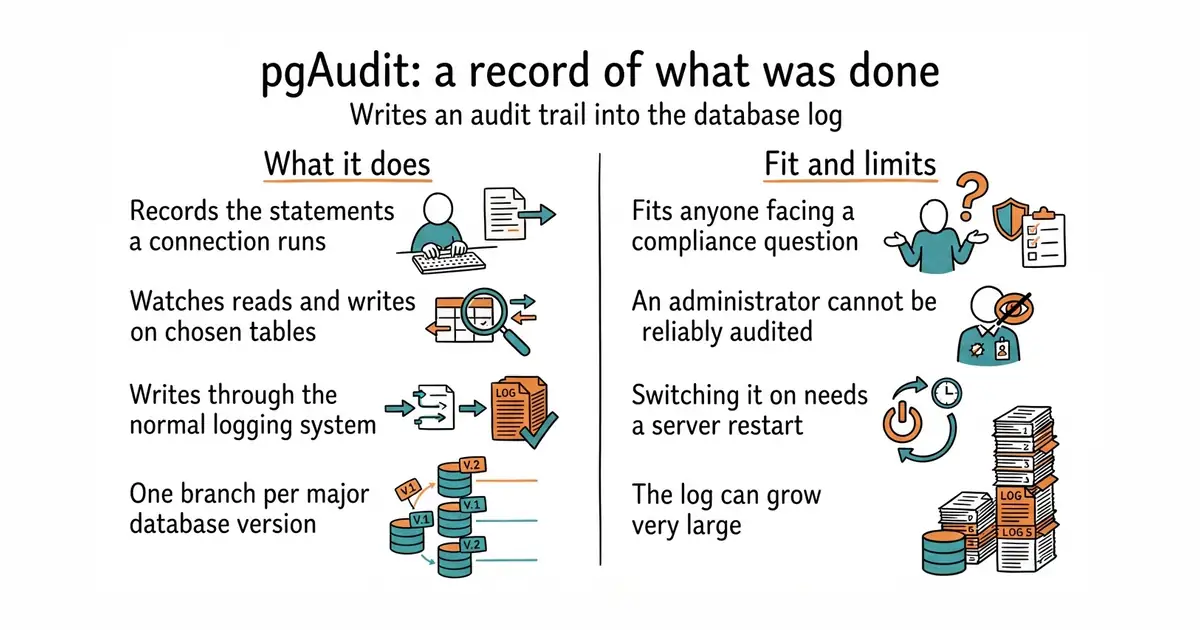

pgaudit/pgaudit 💎 hidden gem
A PostgreSQL extension that records what was done to the database, in the database's own log.
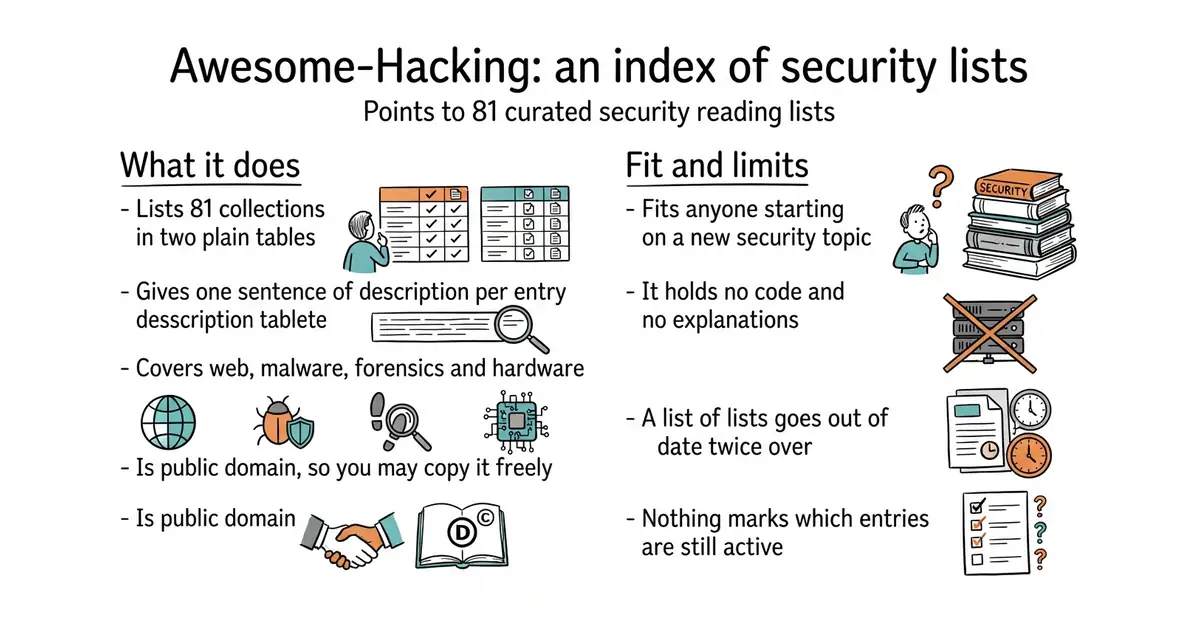

Hack-with-Github/Awesome-Hacking
An index of 81 curated security reading lists, with one line on each.
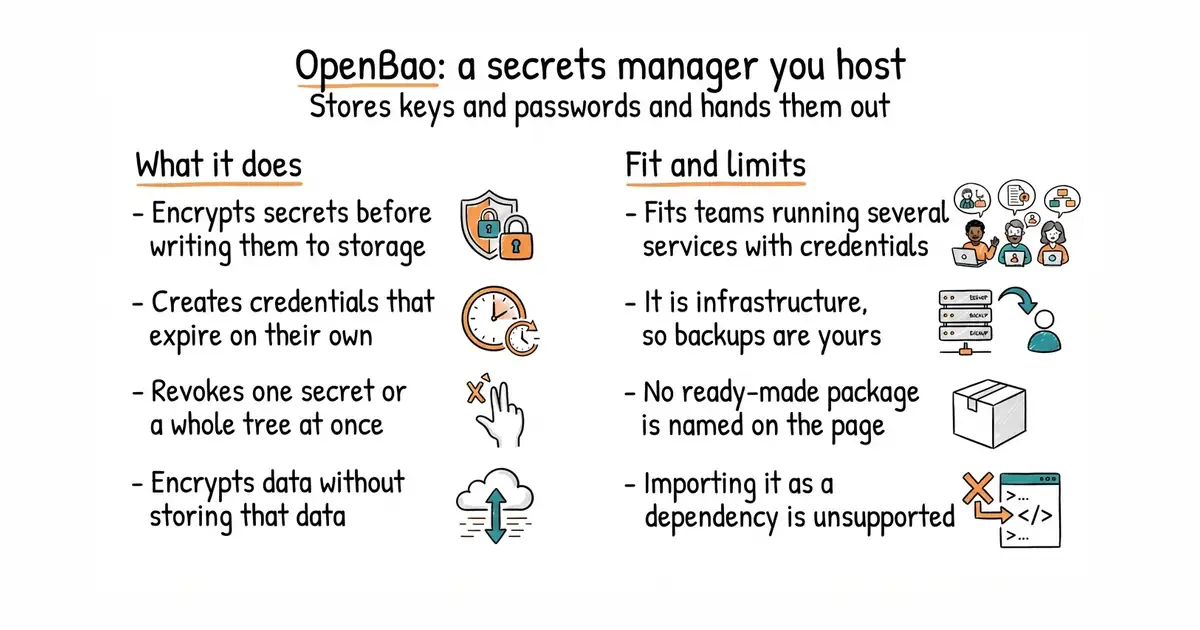

openbao/openbao
A secrets manager that stores keys and passwords, hands them out on request, and can revoke them.
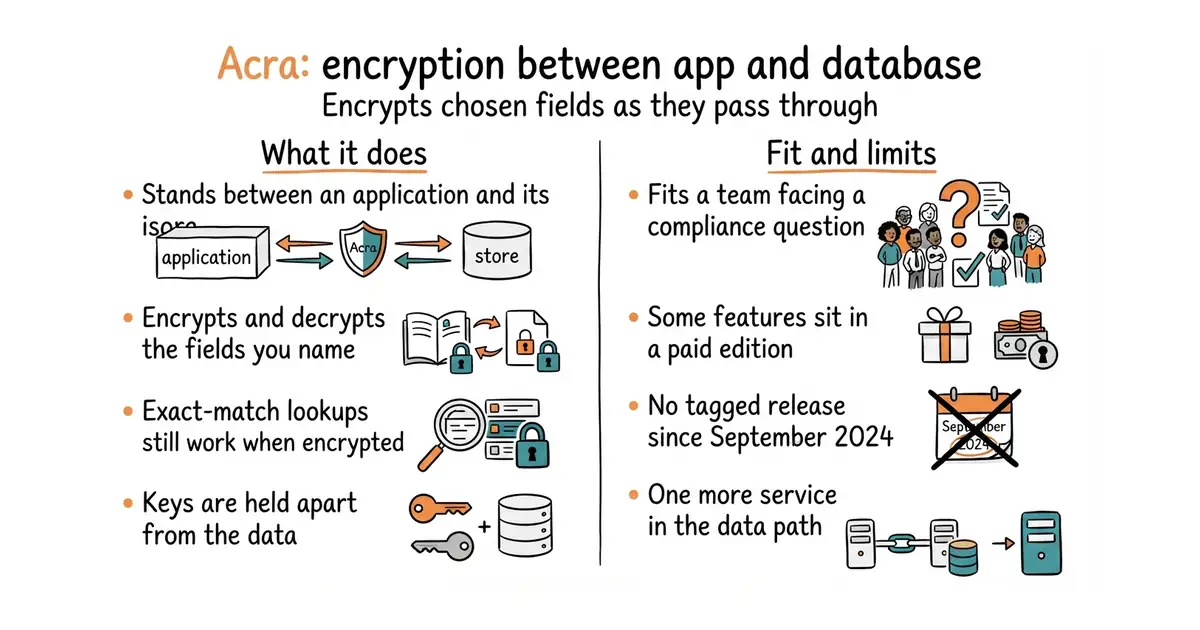

cossacklabs/acra 💎 hidden gem
A proxy that encrypts individual database fields on the way in and decrypts them on the way out.
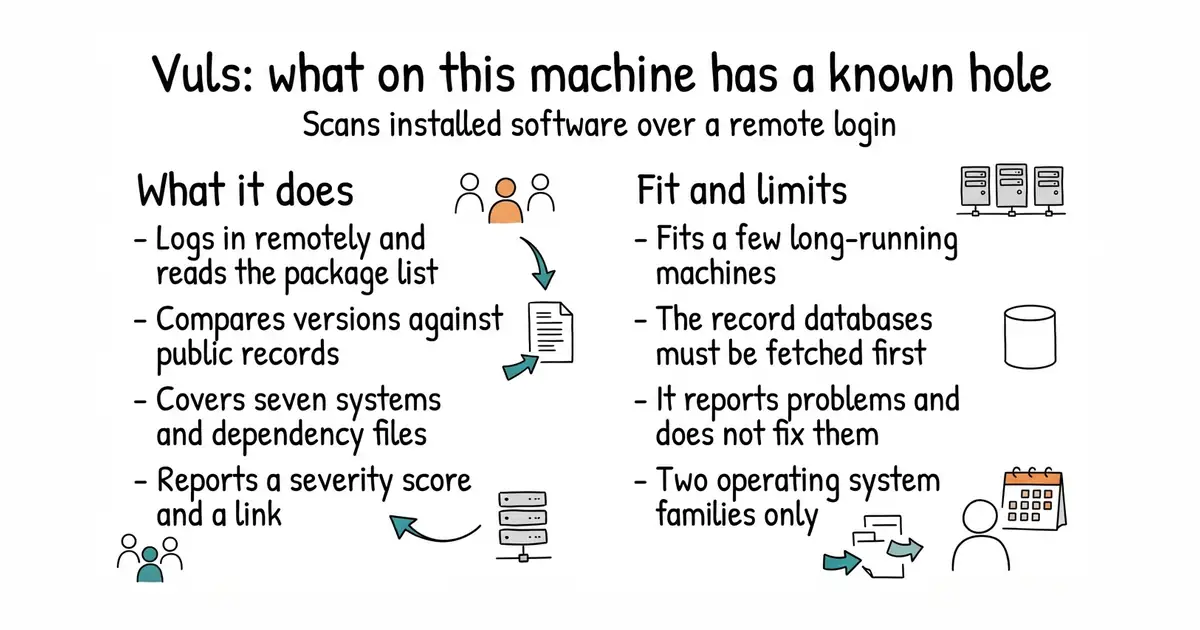

future-architect/vuls
Scans Linux machines over SSH for installed software with publicly reported security holes.
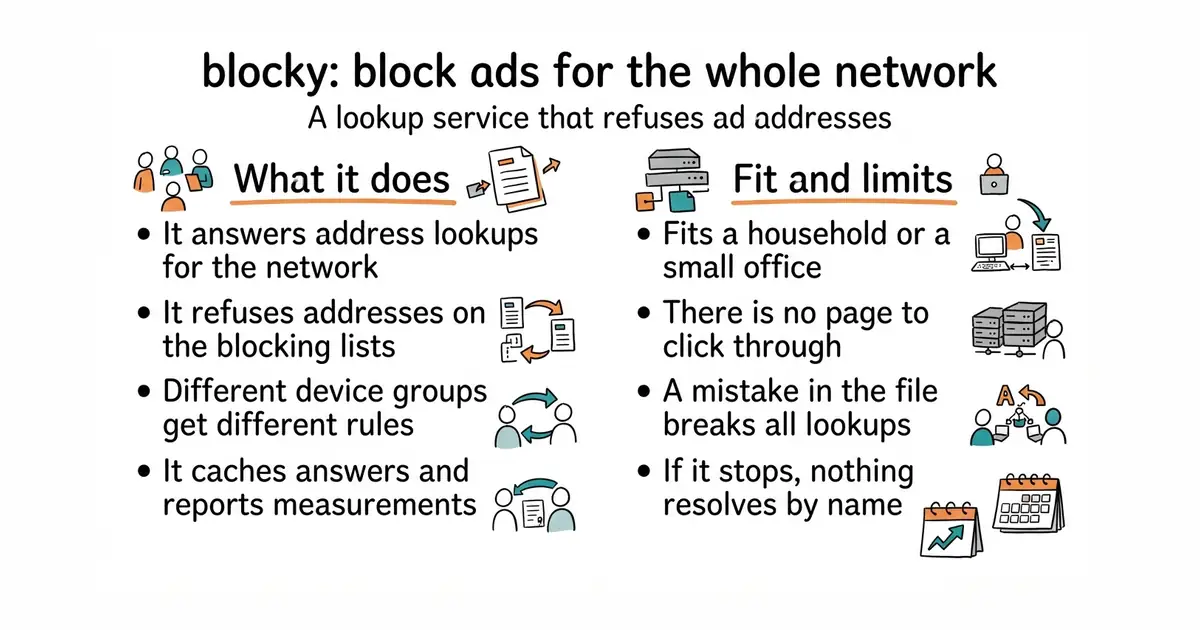

0xERR0R/blocky
A small DNS service for a home or office network that refuses to look up advertising and tracking addresses.
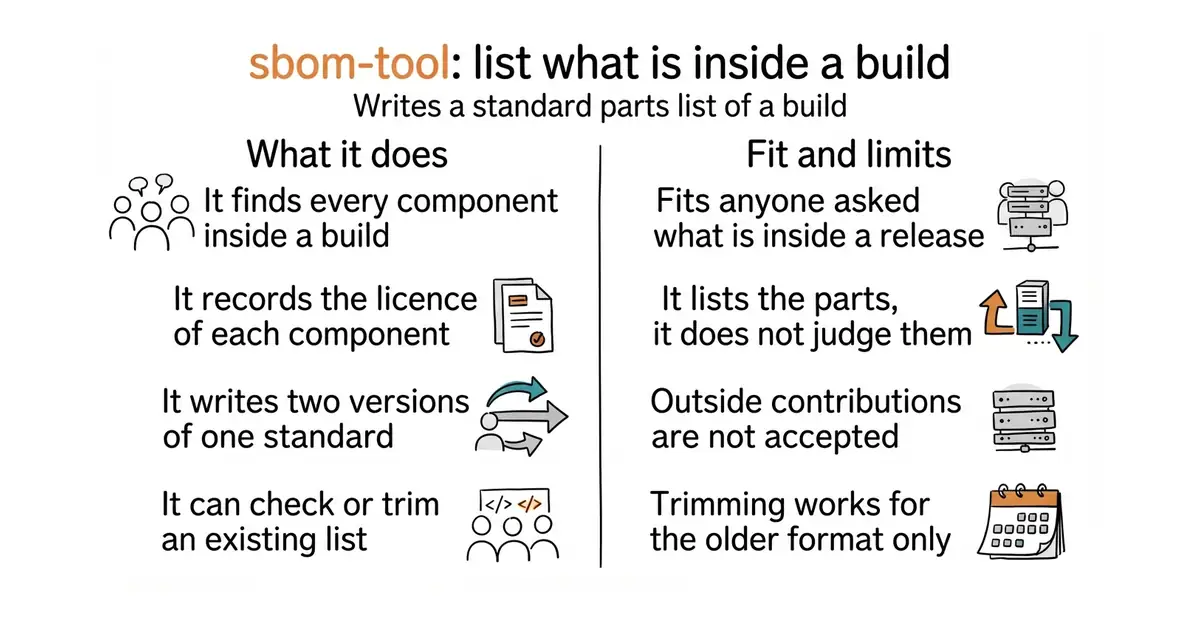

microsoft/sbom-tool 💎 hidden gem
Produces a standard parts list of every component inside a software build, with each component's licence.
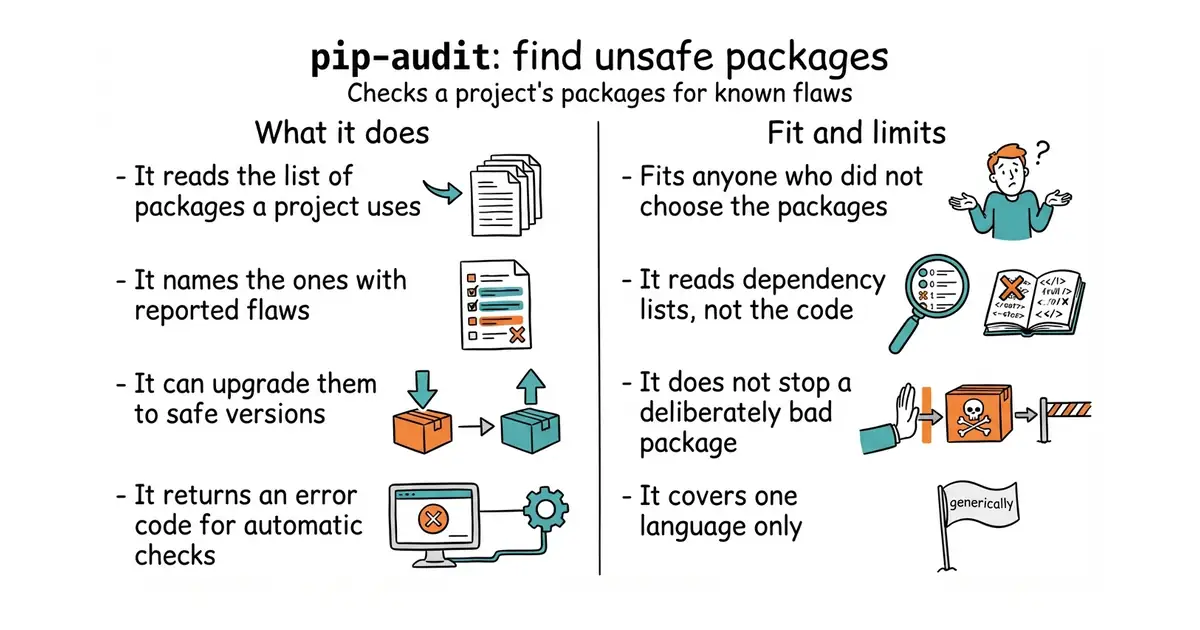

pypa/pip-audit 💎 hidden gem
Checks a Python project's packages against the public advisory database and names the ones with known security holes.
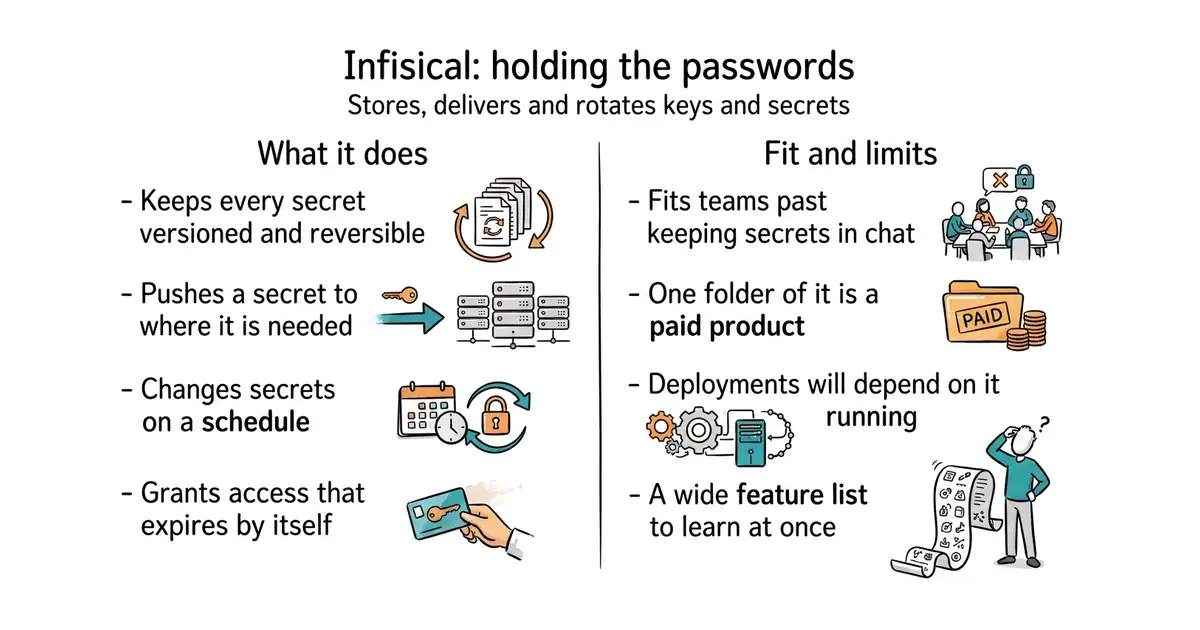

Infisical/infisical
A self-hosted store for passwords, keys and certificates, with automatic rotation and short-lived access.
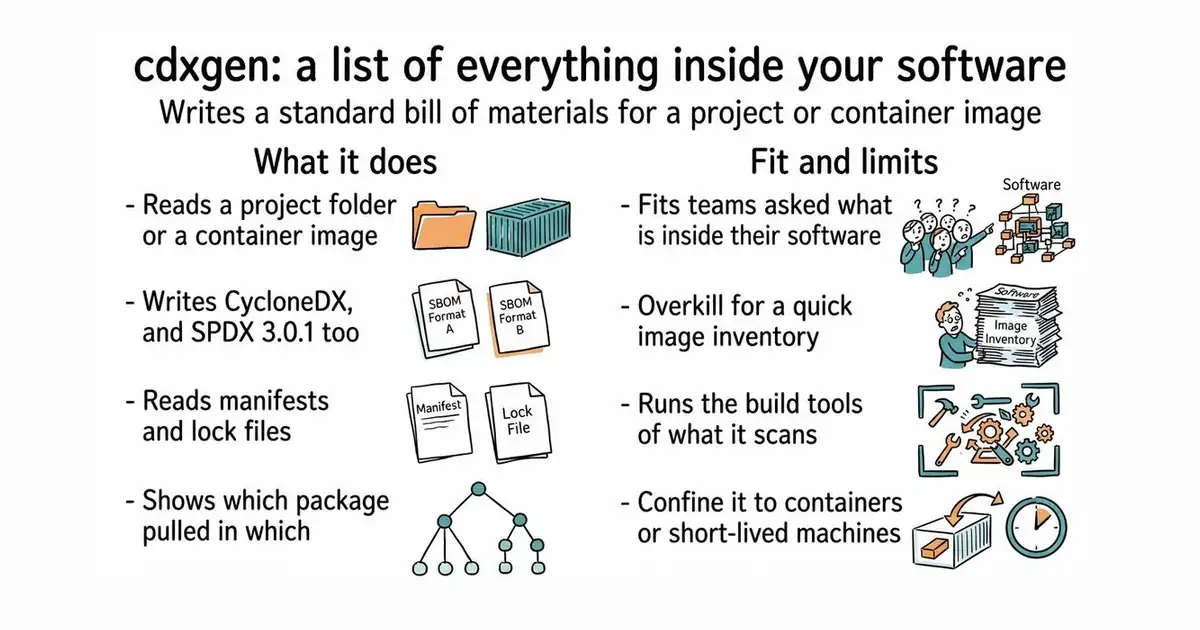

cdxgen/cdxgen 💎 hidden gem
Writes a standard list of every package inside a project or a container image, in both of the common formats.
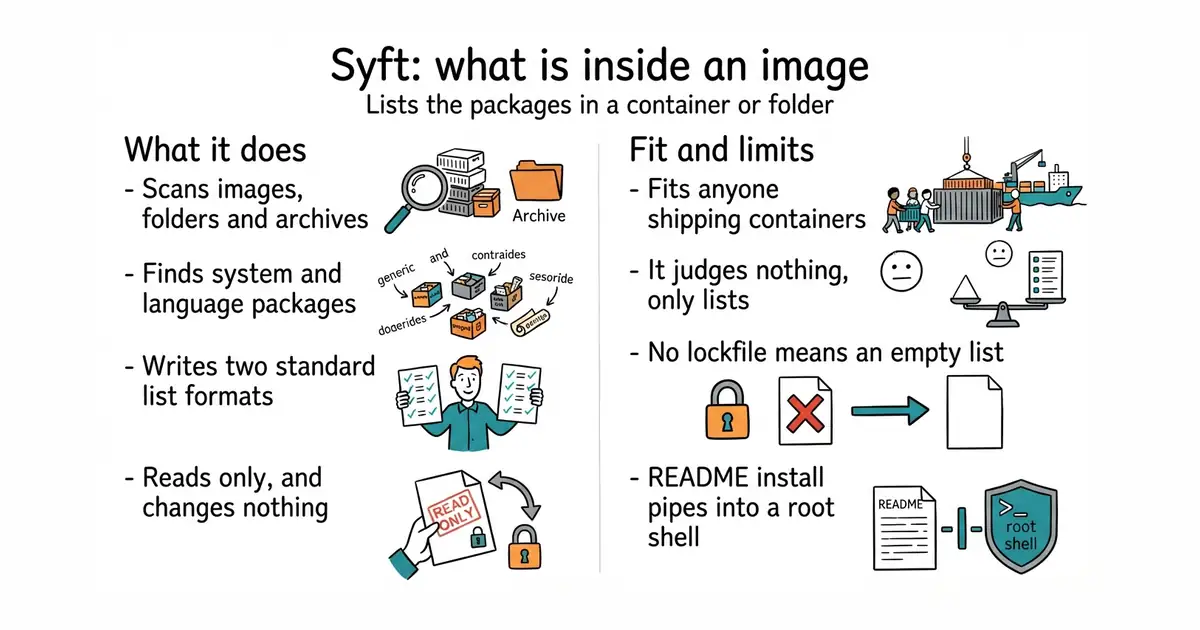

anchore/syft
Lists the packages inside a container image or a folder, as a standard bill of materials.
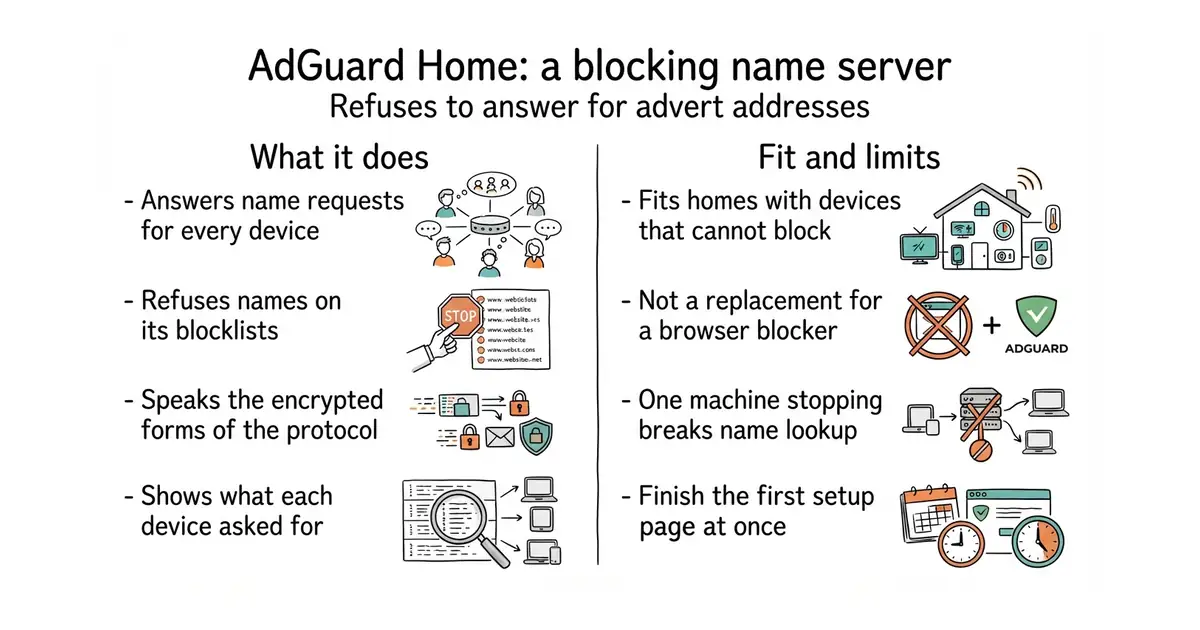

AdguardTeam/AdGuardHome
A home DNS server that refuses to answer for advertising and tracking addresses.
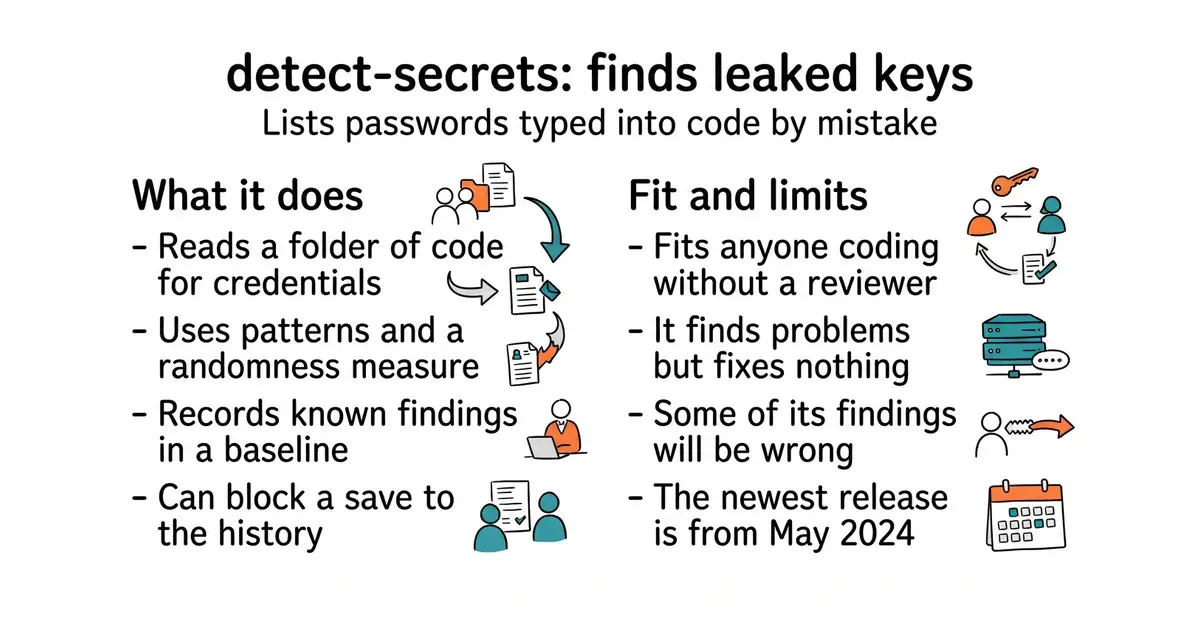

Yelp/detect-secrets
It lists the passwords and keys that were typed into code by mistake, and remembers the ones already known.

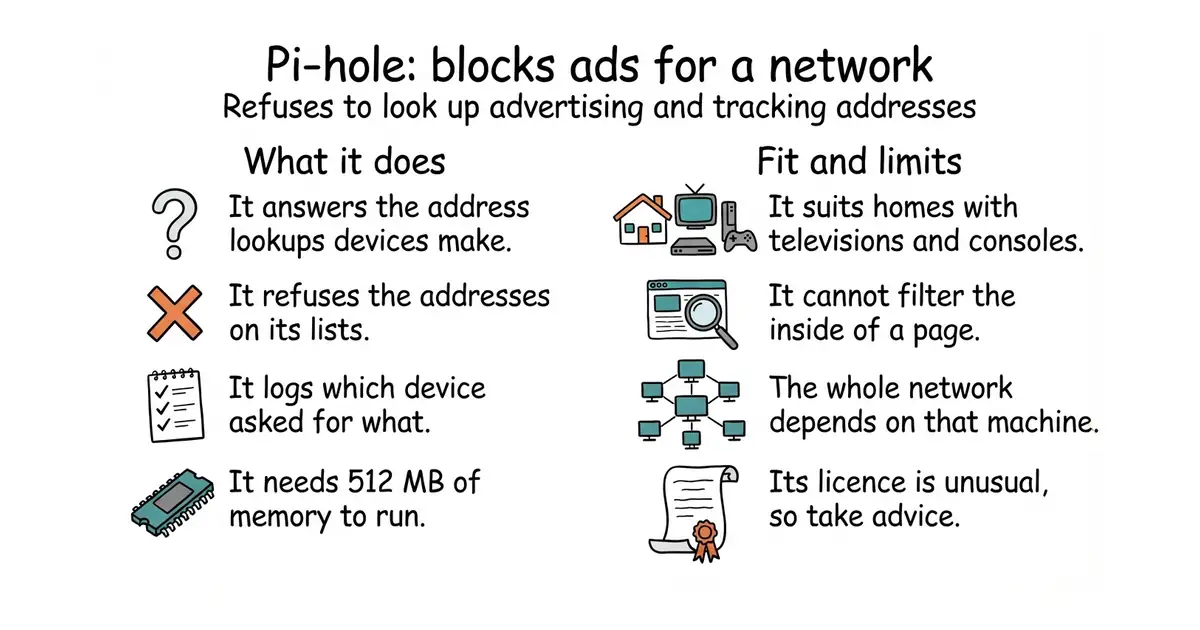

pi-hole/pi-hole
It blocks advertising and tracking for every device on a network by refusing to look up those addresses.
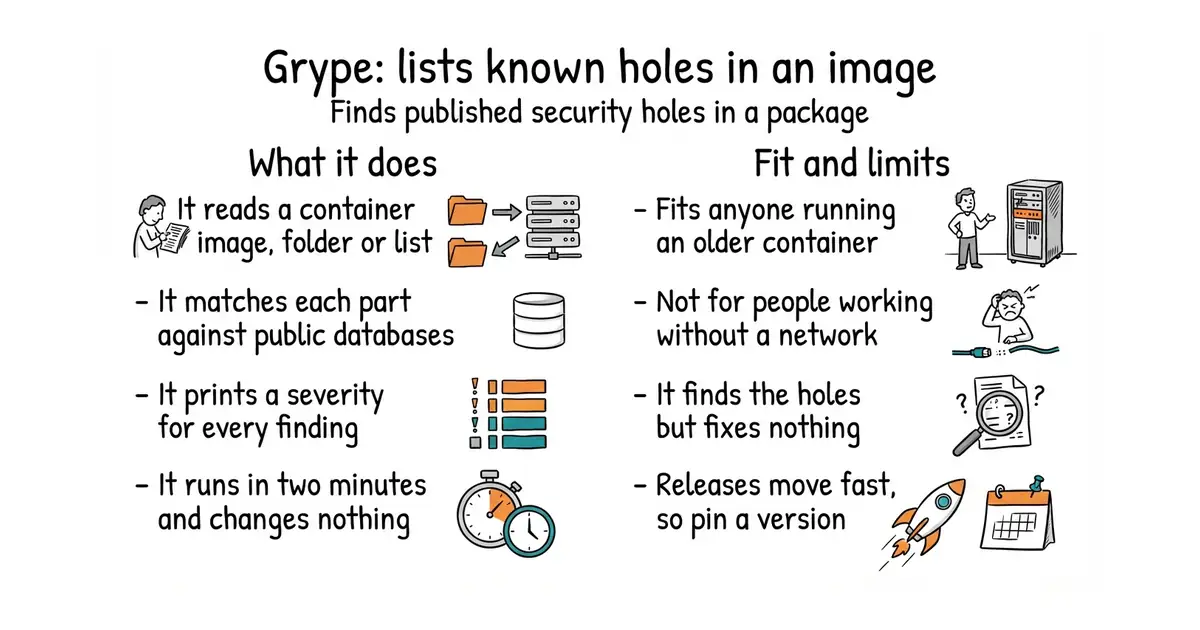

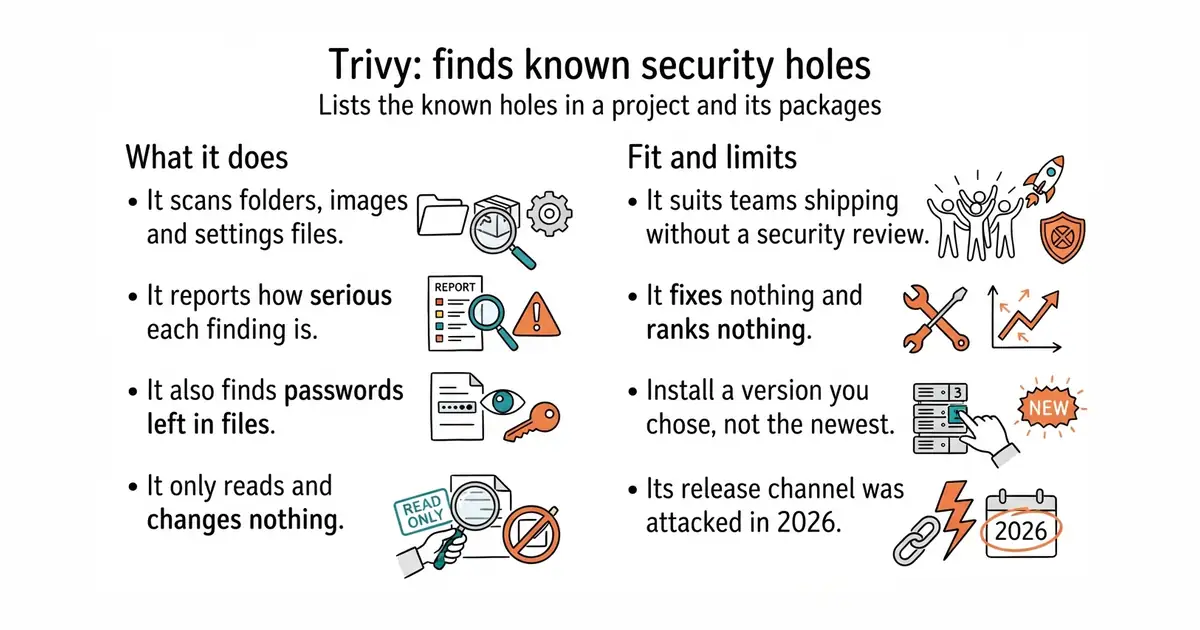
anchore/grype
It lists published security holes found in a container image, a folder, or a parts list of software.
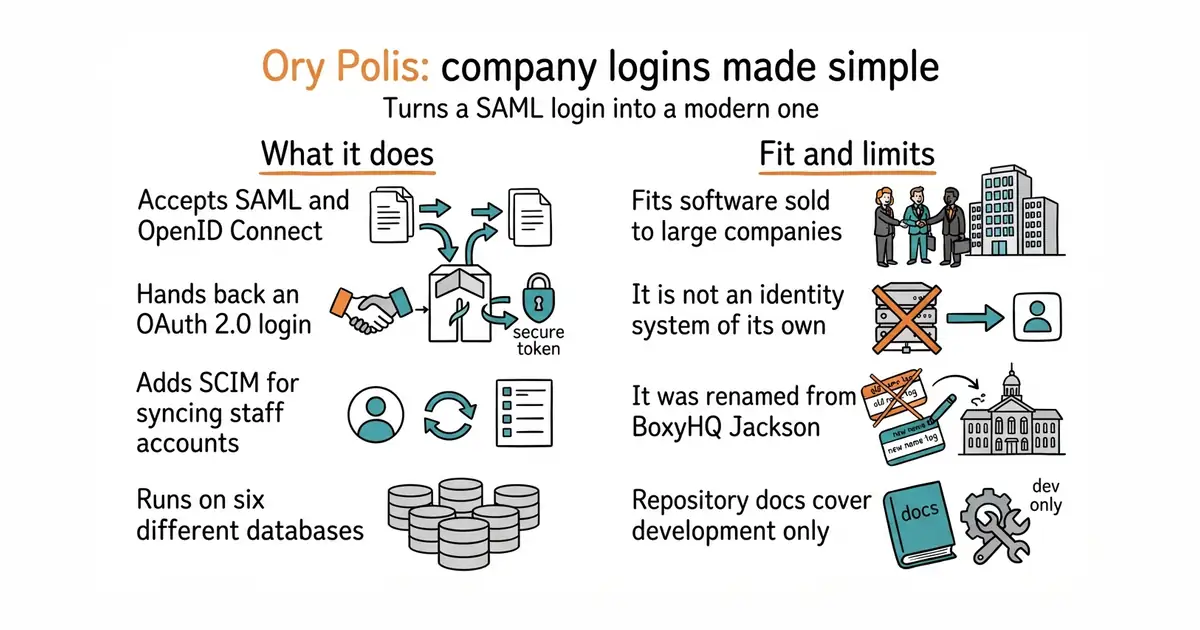

ory/polis
Translates a company's own single sign-on into the ordinary modern login an application already understands.
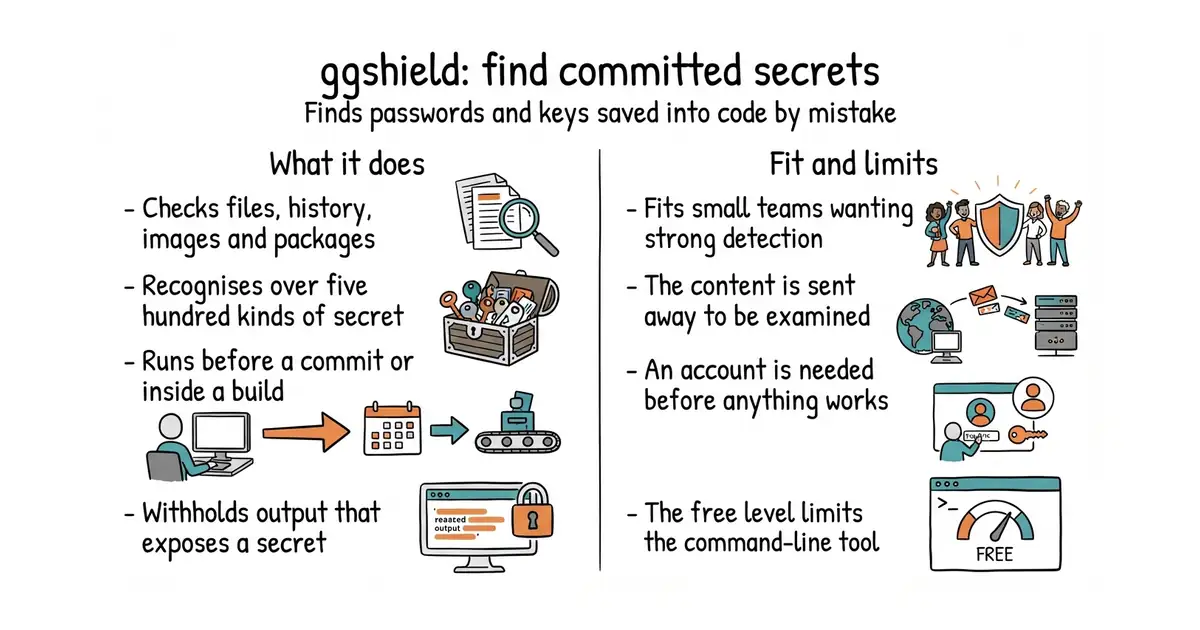

GitGuardian/ggshield 💎 hidden gem
Finds passwords and keys committed into code by mistake, using a company's hosted detection service.
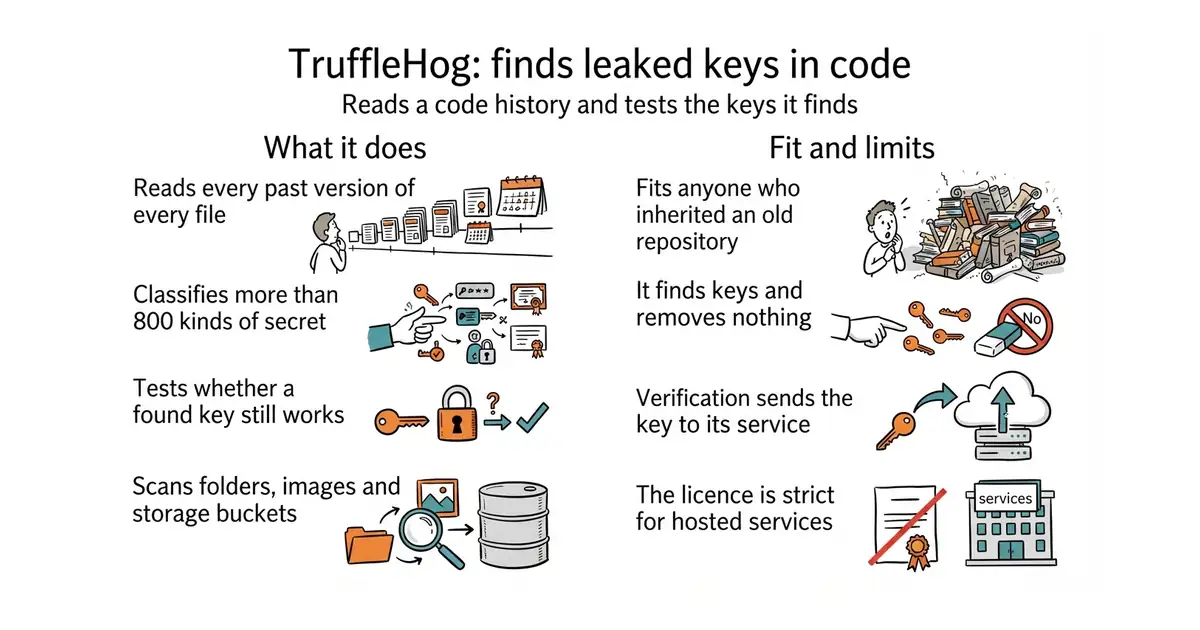

trufflesecurity/trufflehog
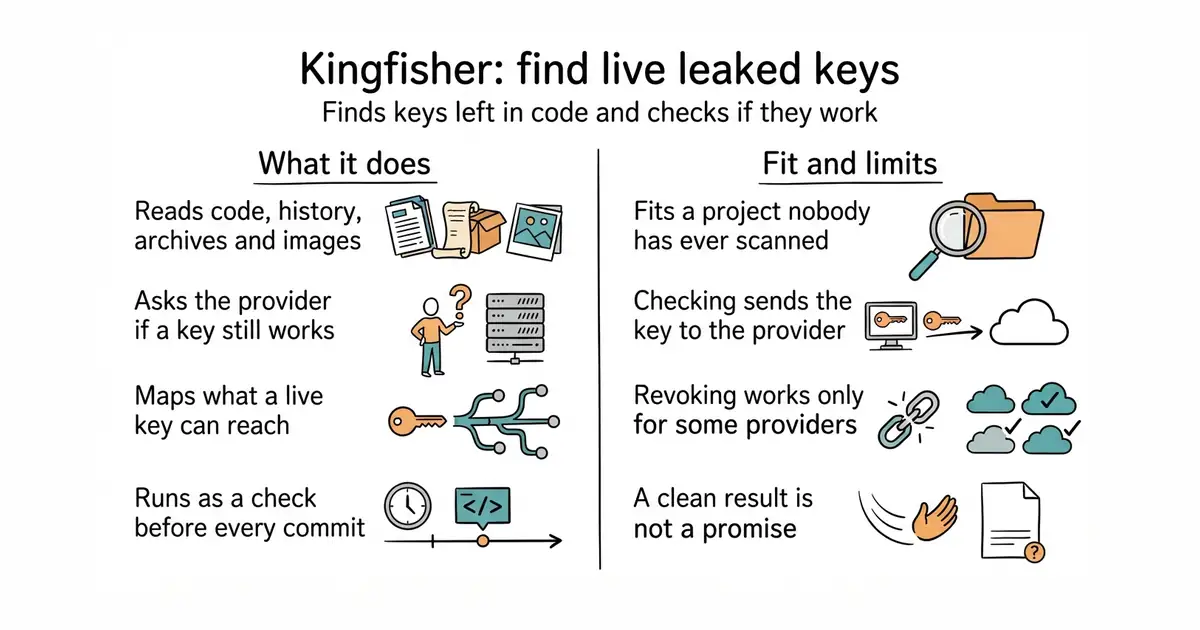
Finds passwords and keys in a code history and checks which of them still work.
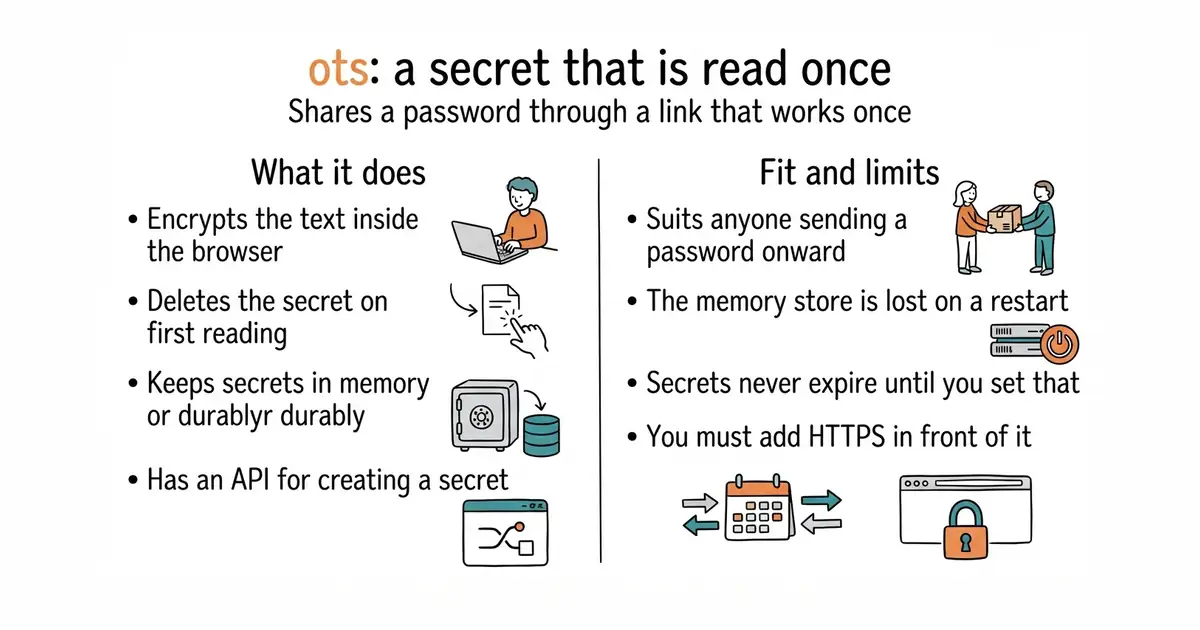

Luzifer/ots 💎 hidden gem
A one-time secret page: the text is encrypted in the browser, and it is destroyed the first time it is read.

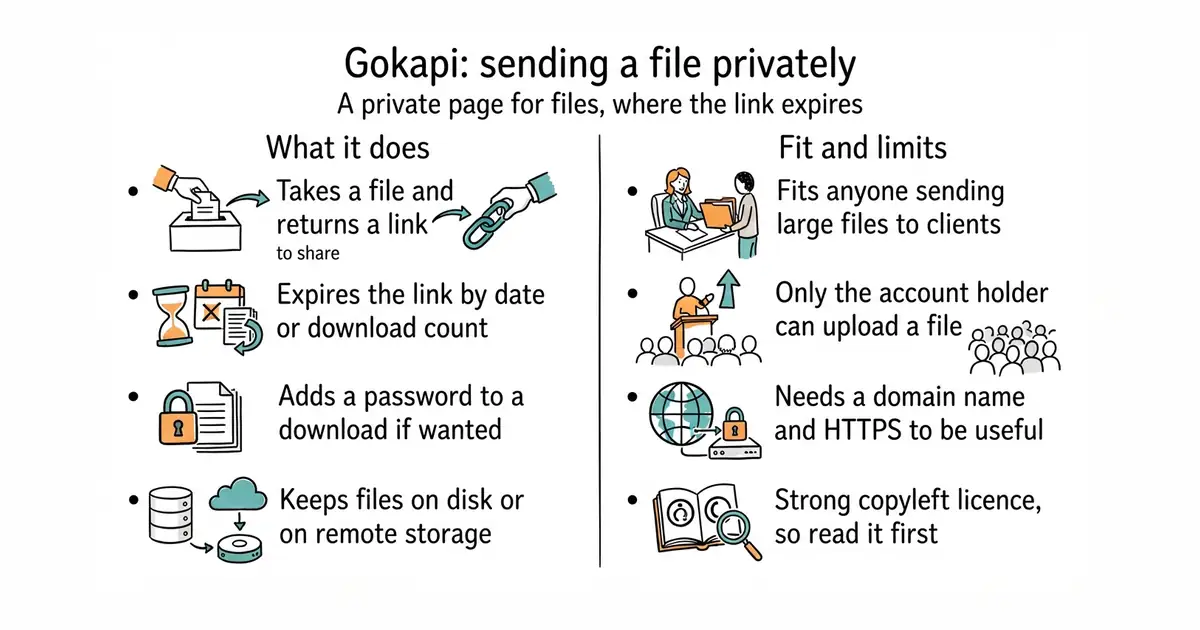

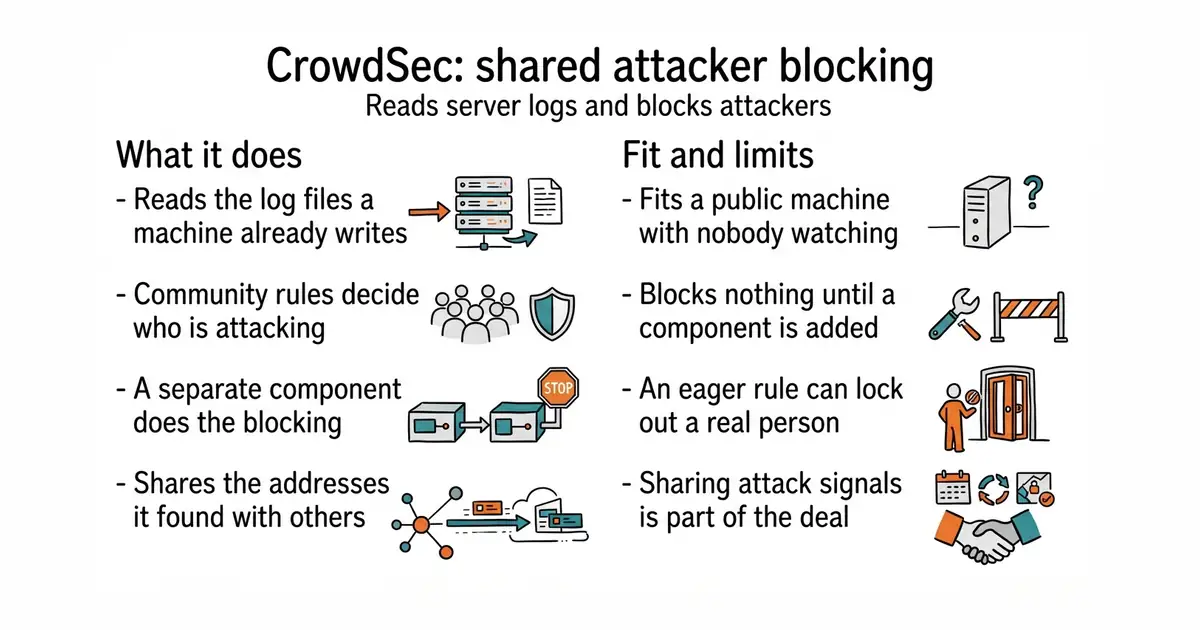

crowdsecurity/crowdsec
It reads a machine's own log files, decides who is attacking, blocks them, and shares what it found with everyone else running it.
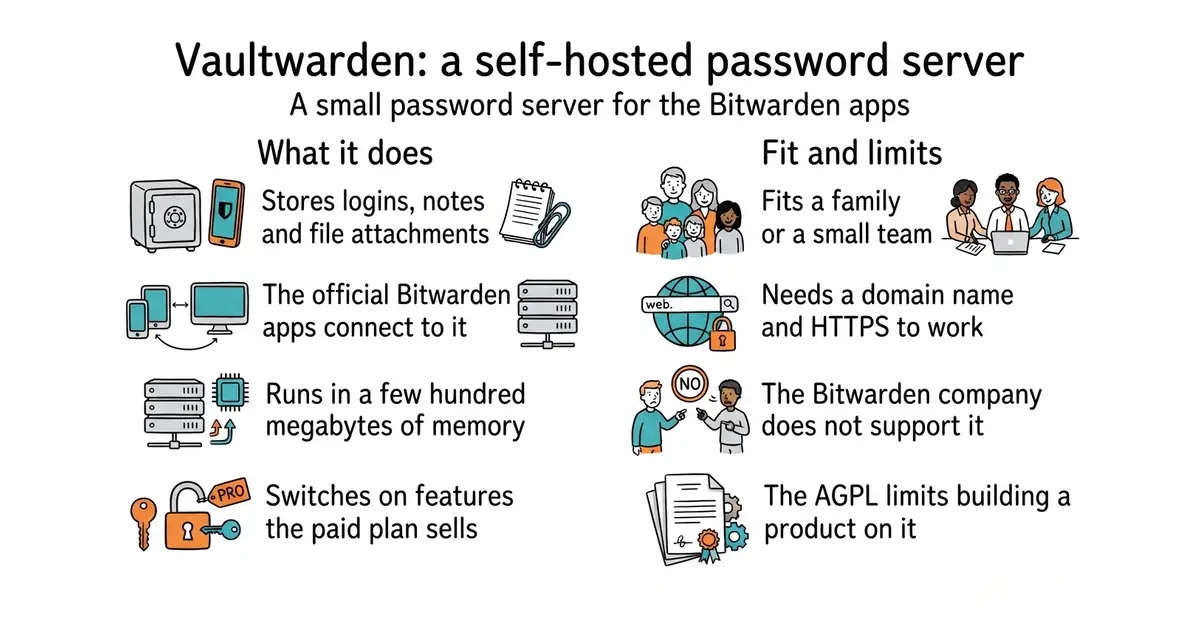

dani-garcia/vaultwarden
A password server that the official Bitwarden apps connect to, small enough to run on the cheapest machine that can be rented.
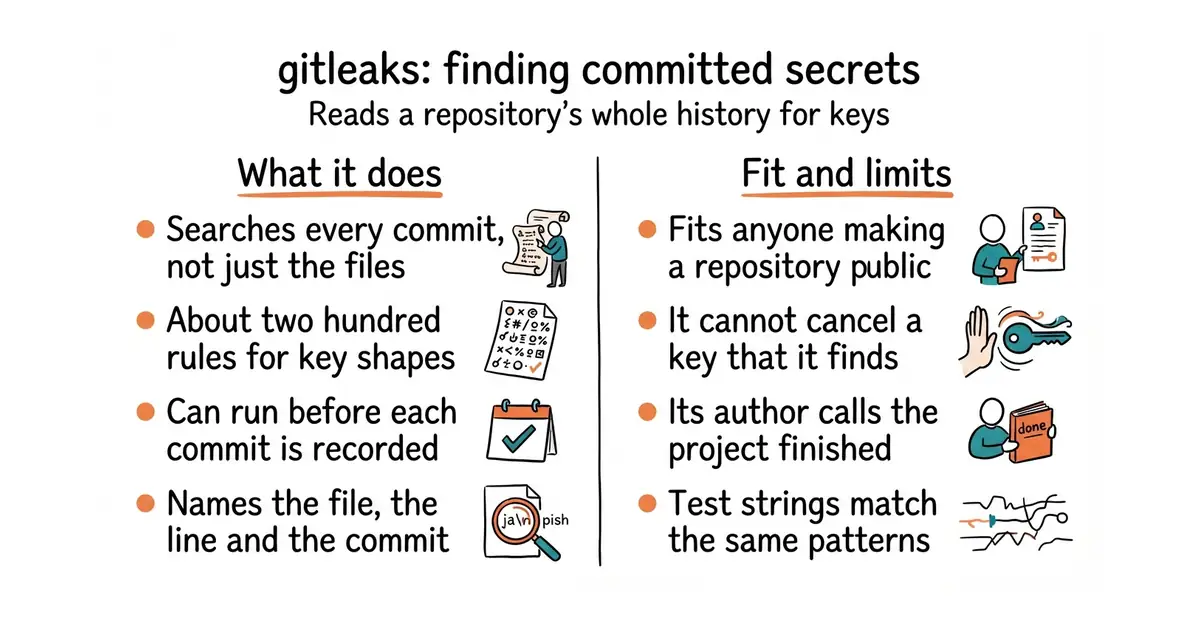

gitleaks/gitleaks
It searches a Git repository, including its whole history, for passwords and keys that were committed by mistake.
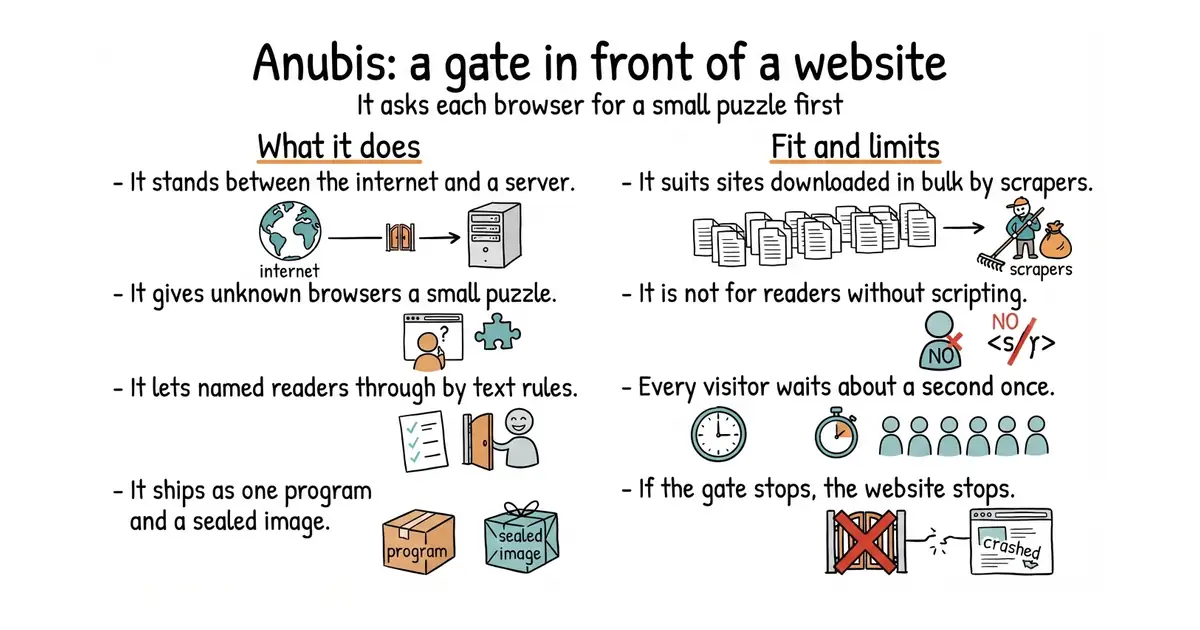

TecharoHQ/anubis
It makes a browser do a small piece of work before a page is served, which most scrapers will not pay for.


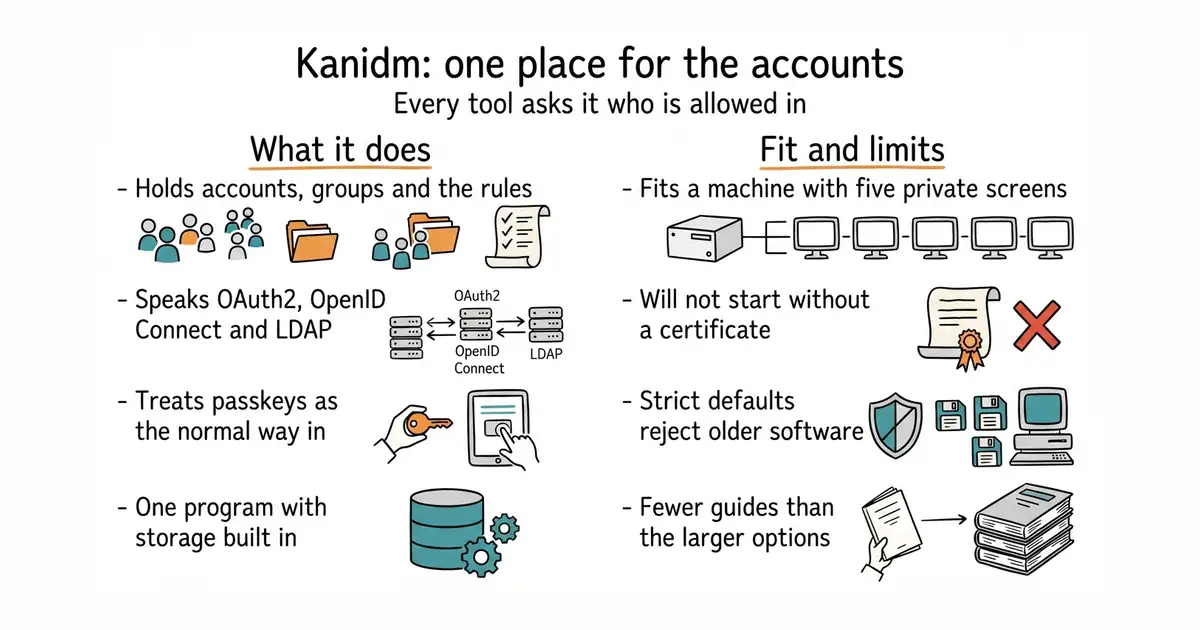

kanidm/kanidm
One place that holds the accounts, so every tool asks it instead of keeping its own passwords.

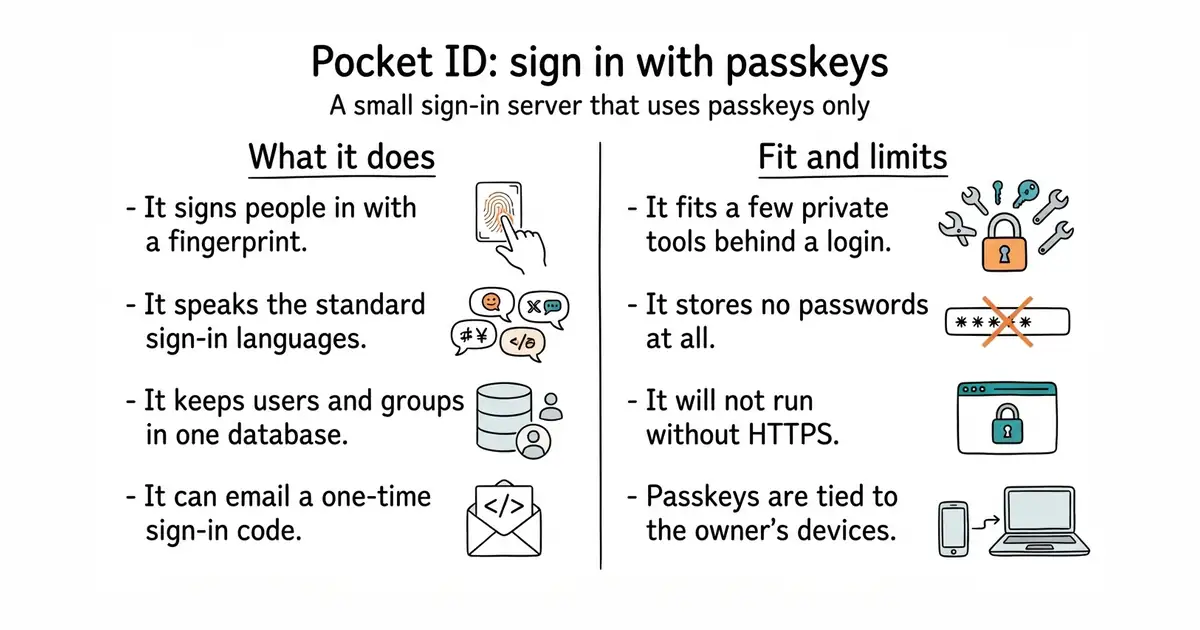

pocket-id/pocket-id
A small sign-in server that lets people log in with a fingerprint or a face instead of a password.

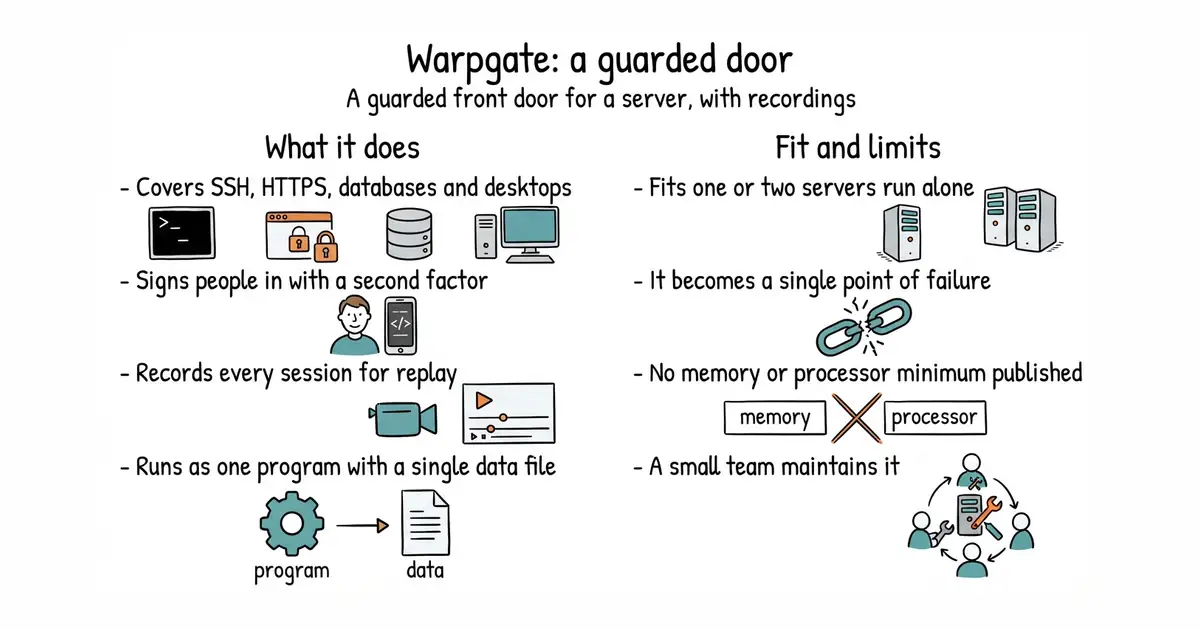

warp-tech/warpgate
A guarded front door for a server, with two-factor sign-in and a recording of every session.

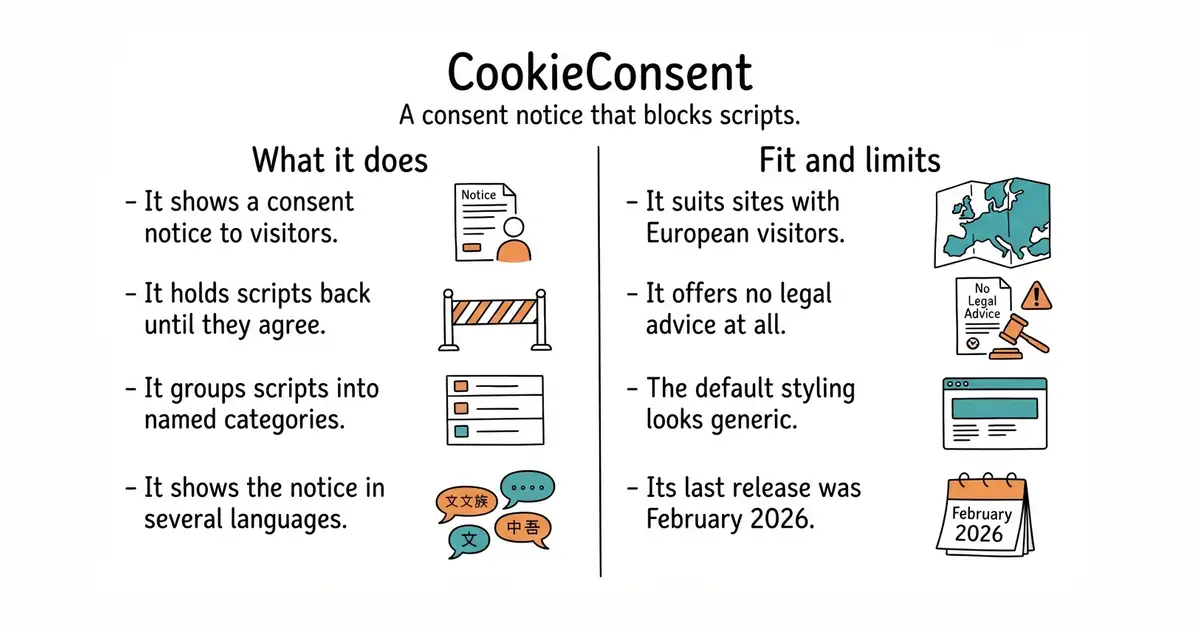

orestbida/cookieconsent
A consent notice that genuinely blocks scripts until the visitor agrees to them.
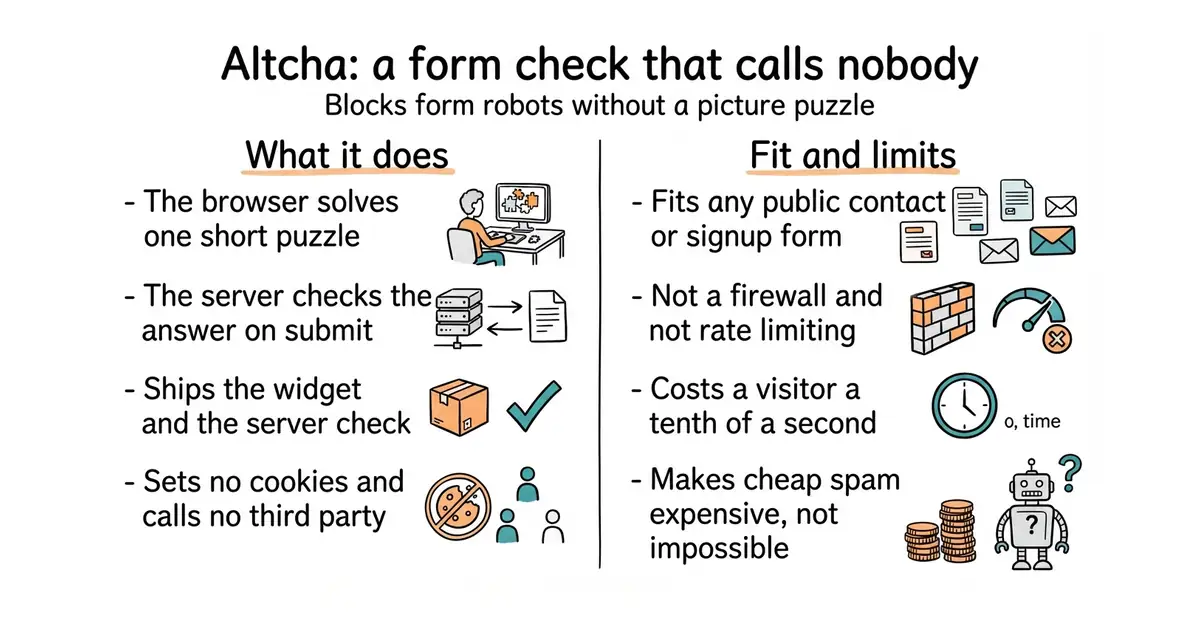

altcha-org/altcha 💎 hidden gem
A self-hosted replacement for picture puzzles on forms, using a small computation instead.
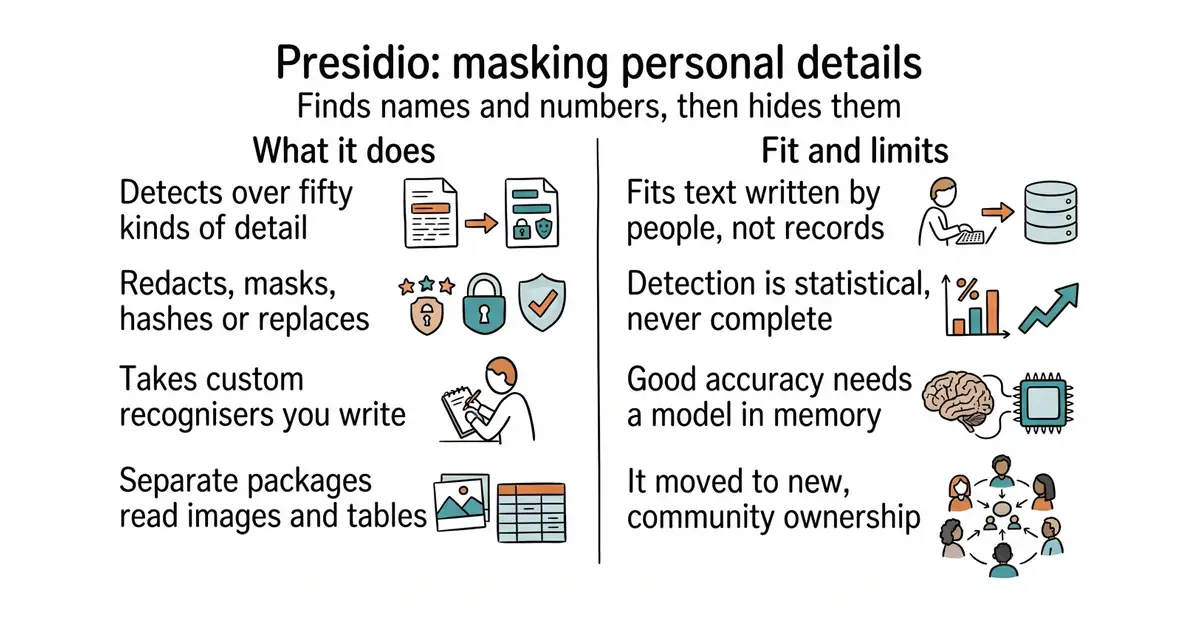

data-privacy-stack/presidio
A framework for detecting and removing personal data in text, images and tables.
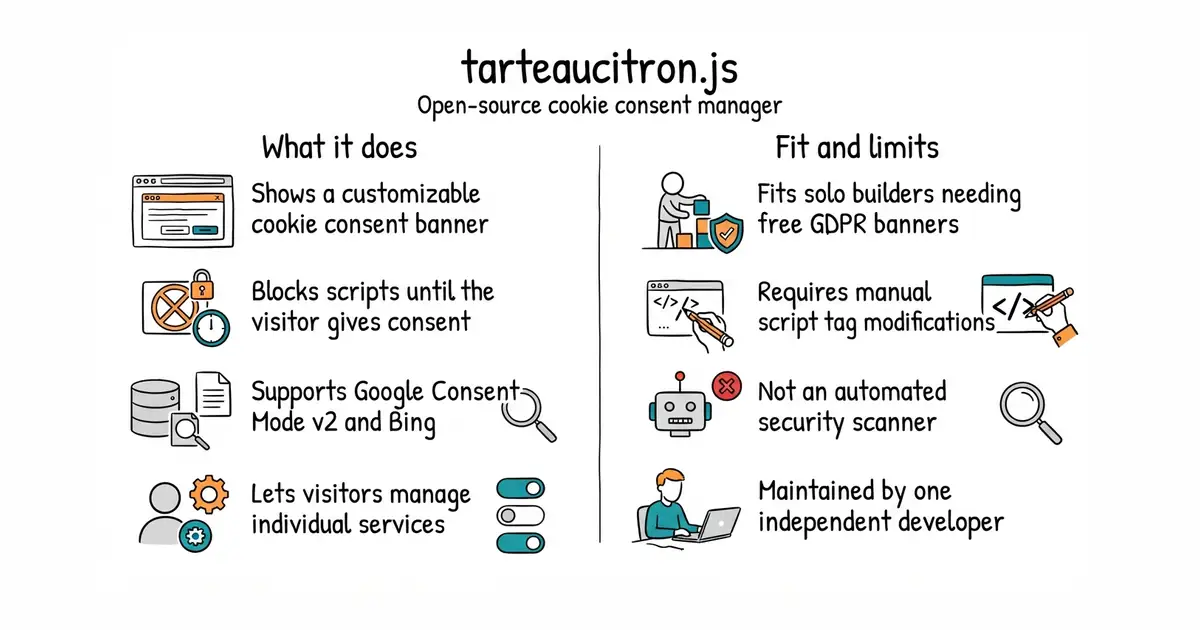

AmauriC/tarteaucitron.js
Open-source JavaScript cookie consent manager for GDPR / RGPD. Customizable banner, service-level controls and Google Consent Mode v2 support.
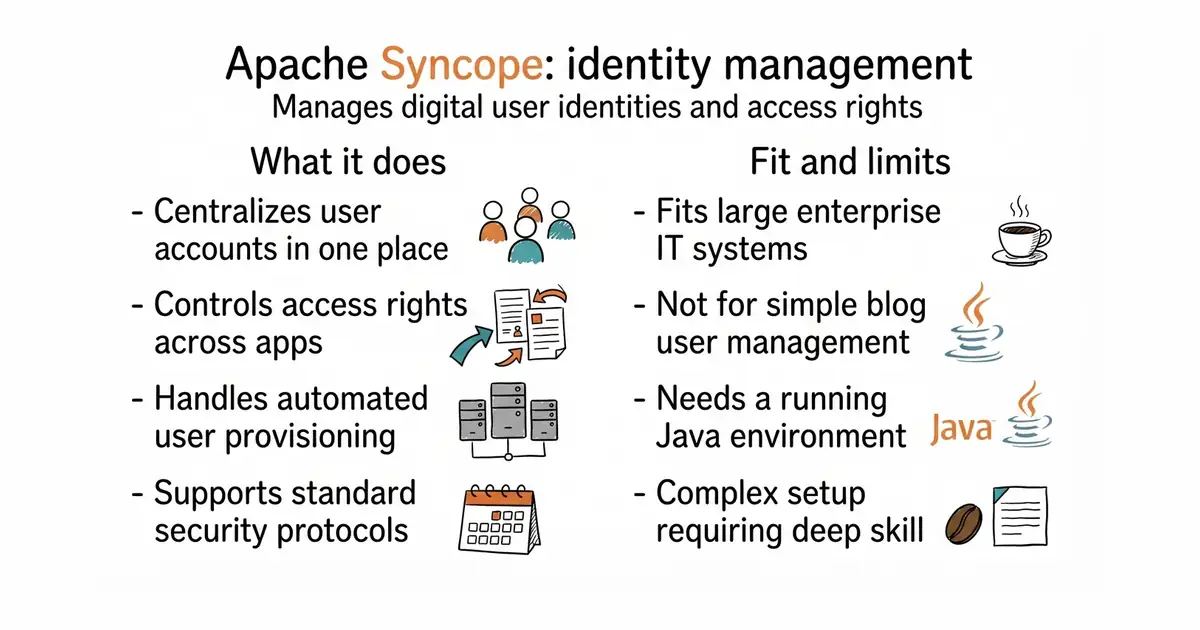

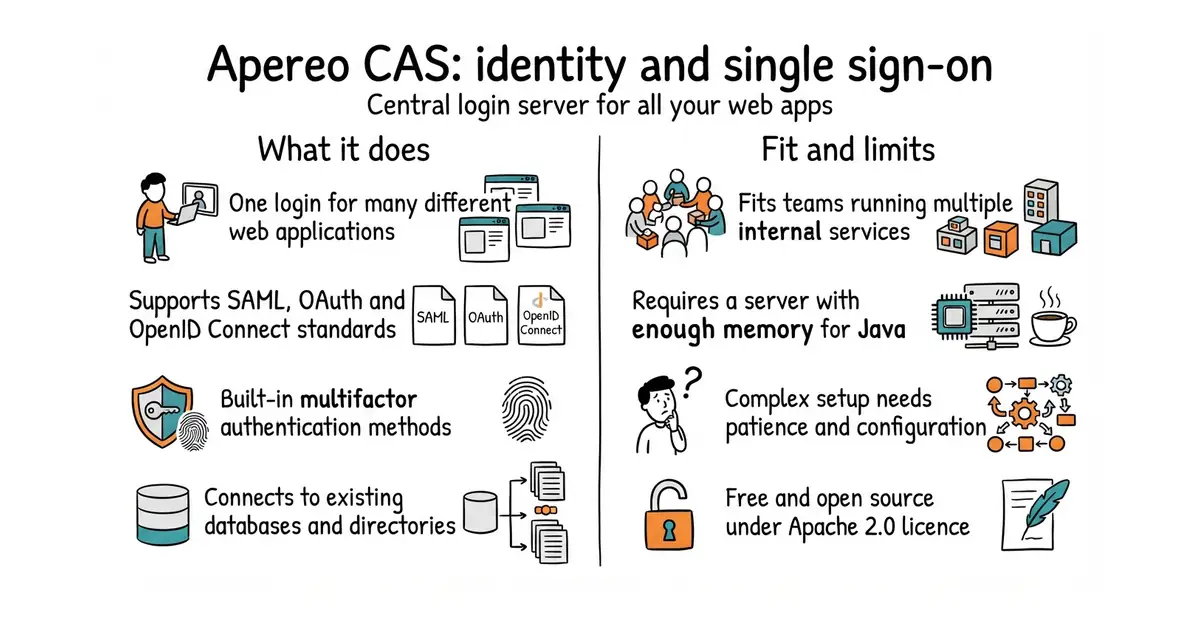

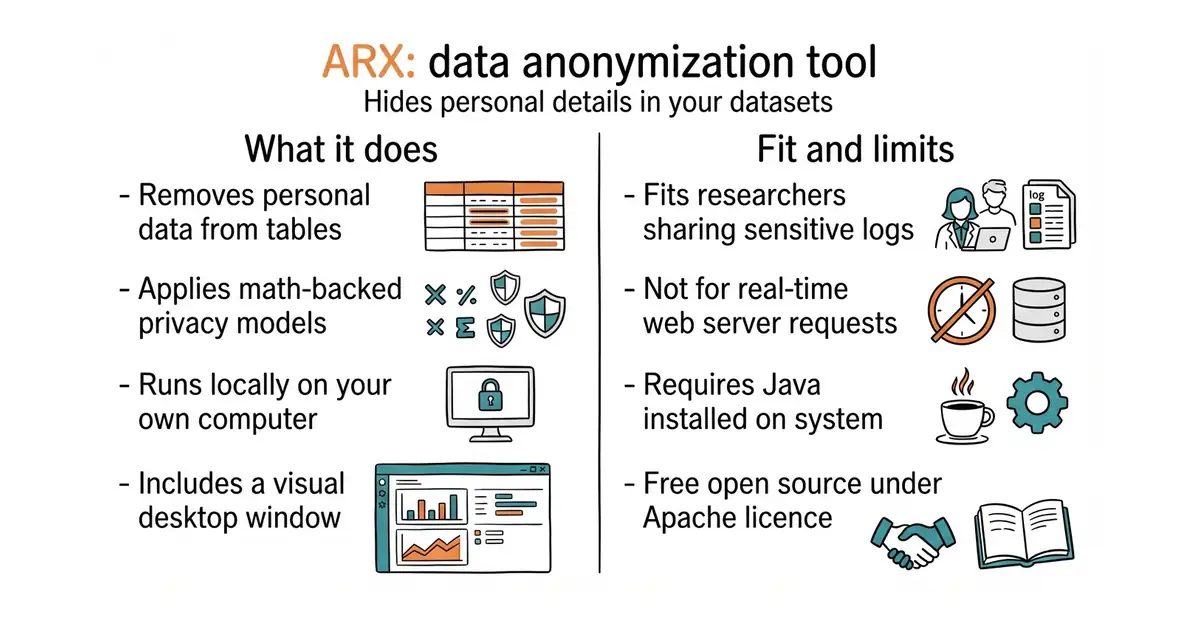

arx-deidentifier/arx
ARX is a comprehensive open source data anonymization tool aiming to provide scalability and usability. It supports various anonymization techniques, methods for analyzing data quality and re-identification risks and it supports well-known privacy models, such as k-anonymity, l-diversity, t-closeness and differential privacy.



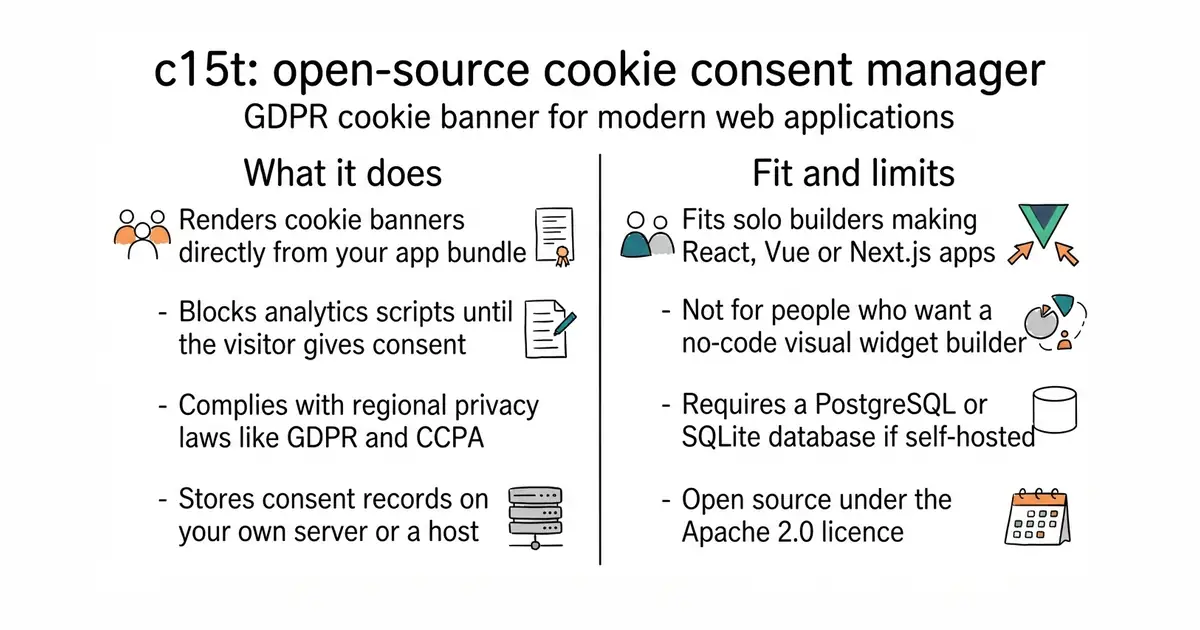

c15t/c15t
Open-source cookie consent manager and GDPR cookie banner for React, Next.js, Vue and JavaScript. Google Consent Mode v2 and IAB TCF.
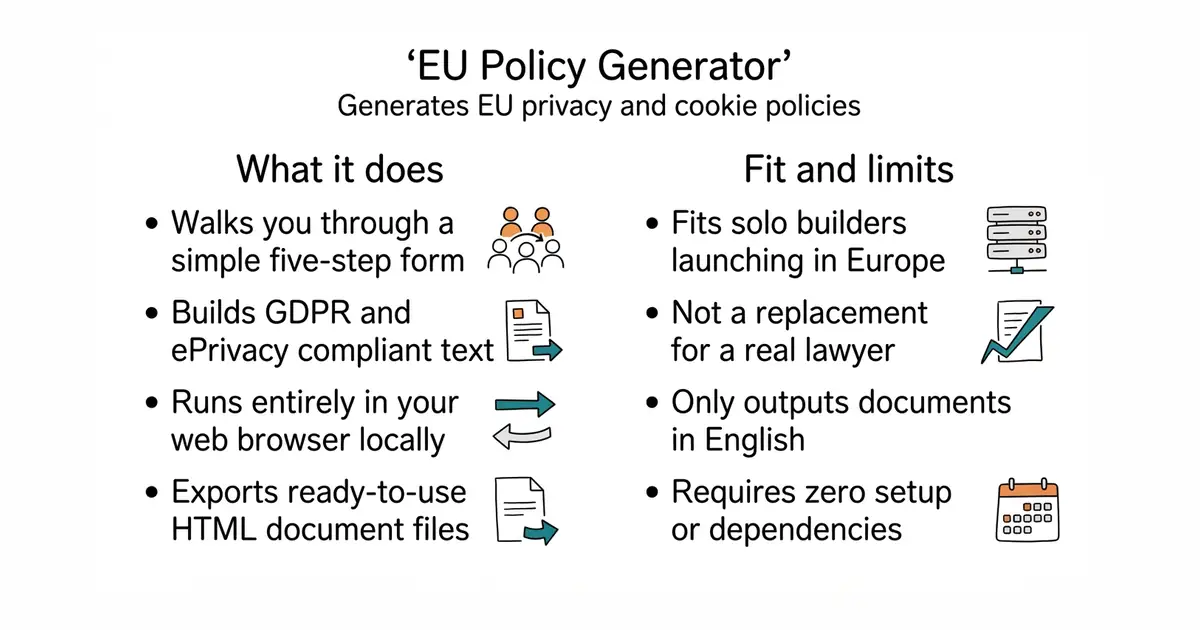
Carashen-data/eu-policy-generator
Free, open-source single-file HTML tool that generates GDPR & ePrivacy Directive compliant Privacy Policies and Cookie Policies for the EU market.
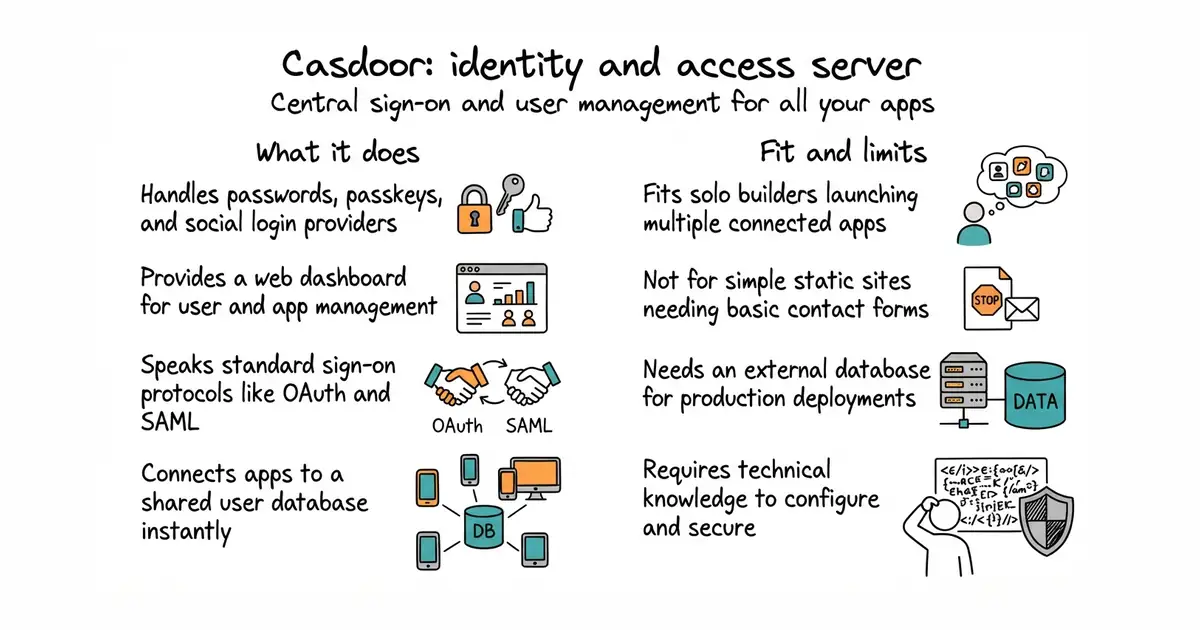

casdoor/casdoor
An open-source Agent-first Identity and Access Management (IAM) /LLM MCP & agent gateway and auth server with web UI supporting OpenClaw, MCP, OAuth, OIDC, SAML, CAS, LDAP, SCIM, WebAuthn, TOTP, MFA, Face ID, Google Workspace, Azure AD

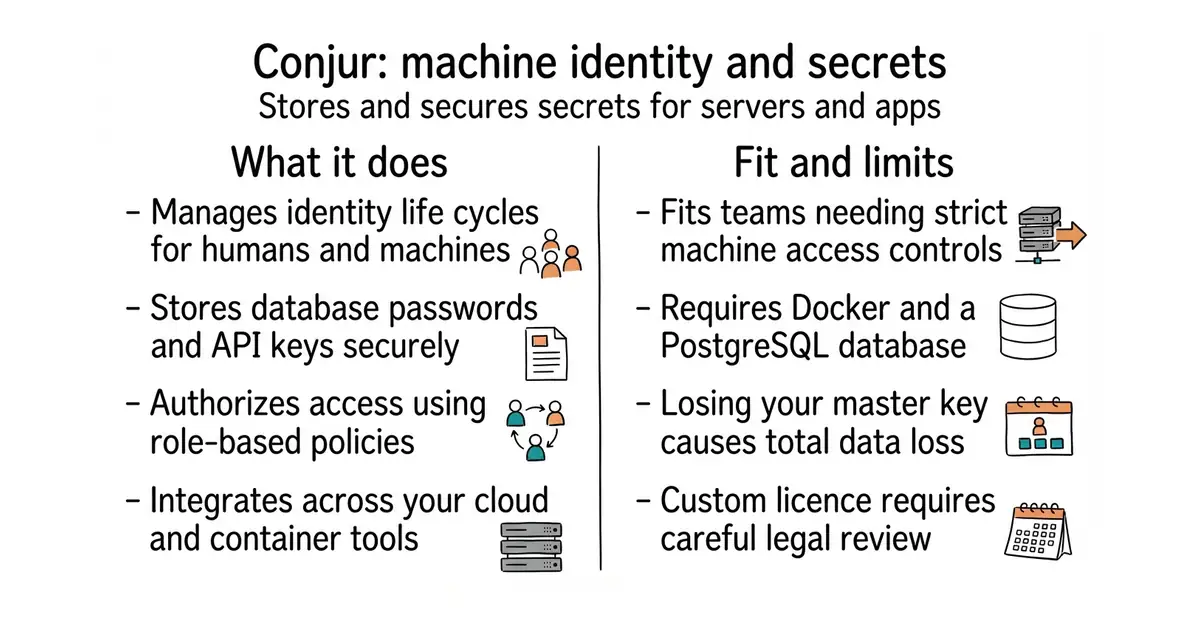

cyberark/conjur
CyberArk Conjur automatically secures secrets used by privileged users and machine identities
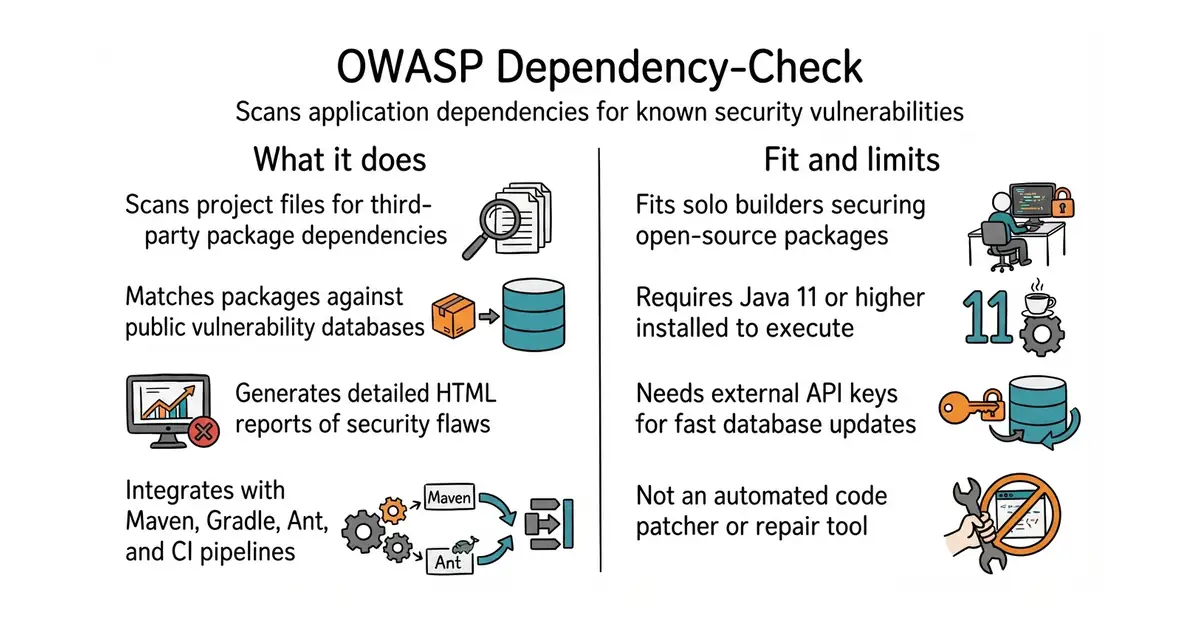

dependency-check/DependencyCheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
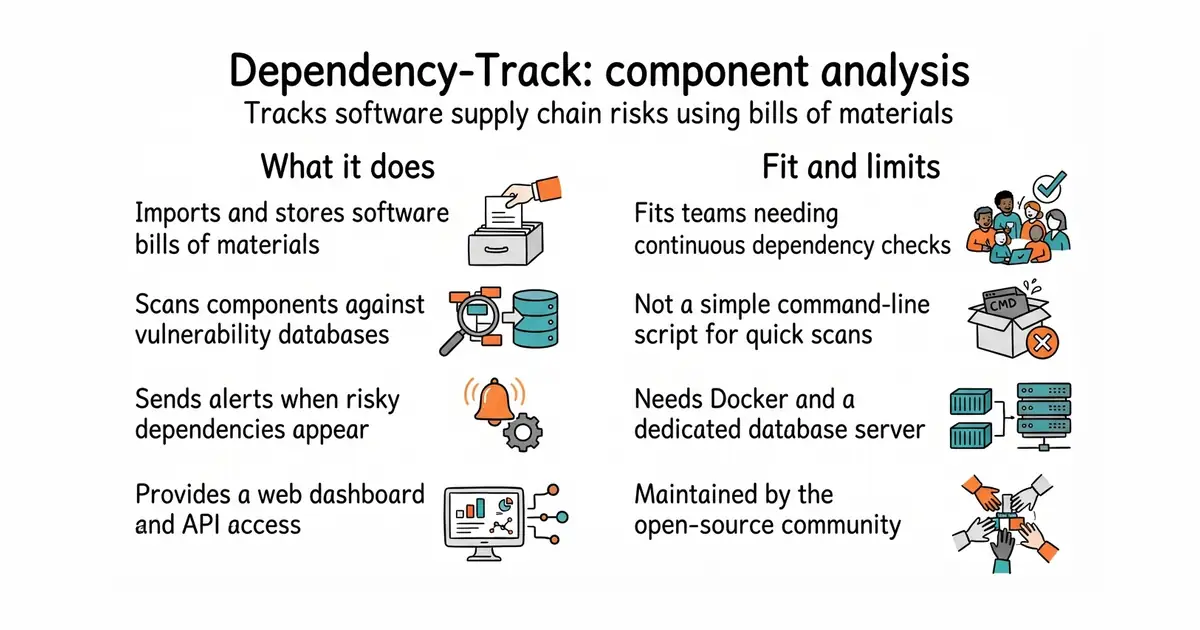

DependencyTrack/dependency-track
Dependency-Track is an intelligent Component Analysis platform that allows organizations to identify and reduce risk in the software supply chain.



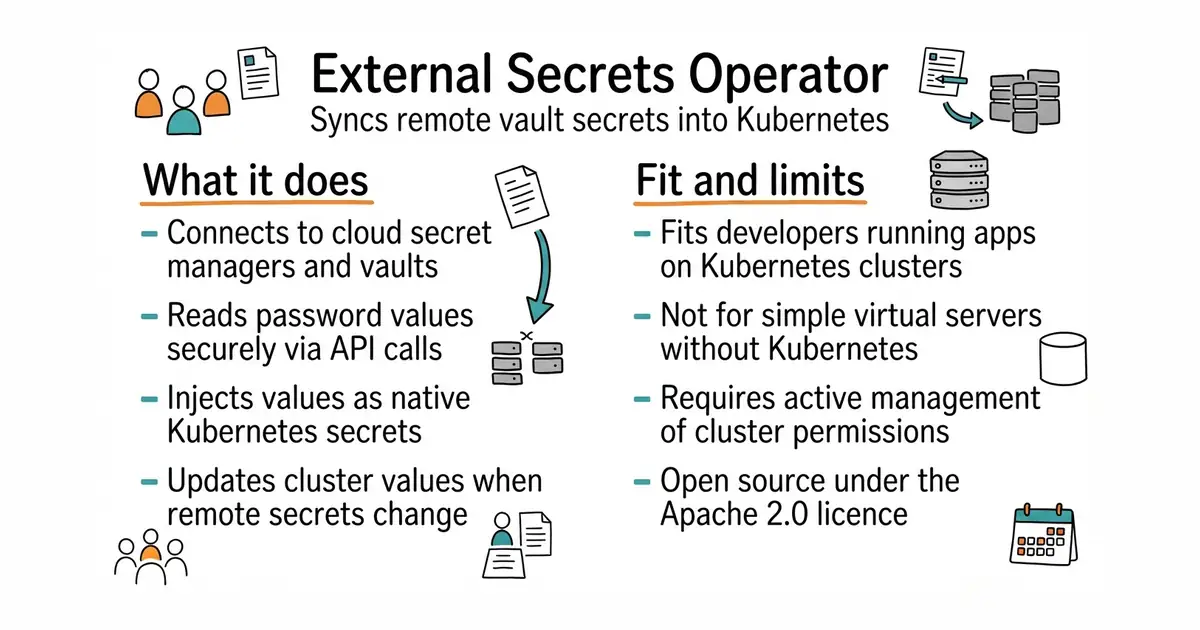

external-secrets/external-secrets
External Secrets Operator reads information from a third-party service like AWS Secrets Manager and automatically injects the values as Kubernetes Secrets.

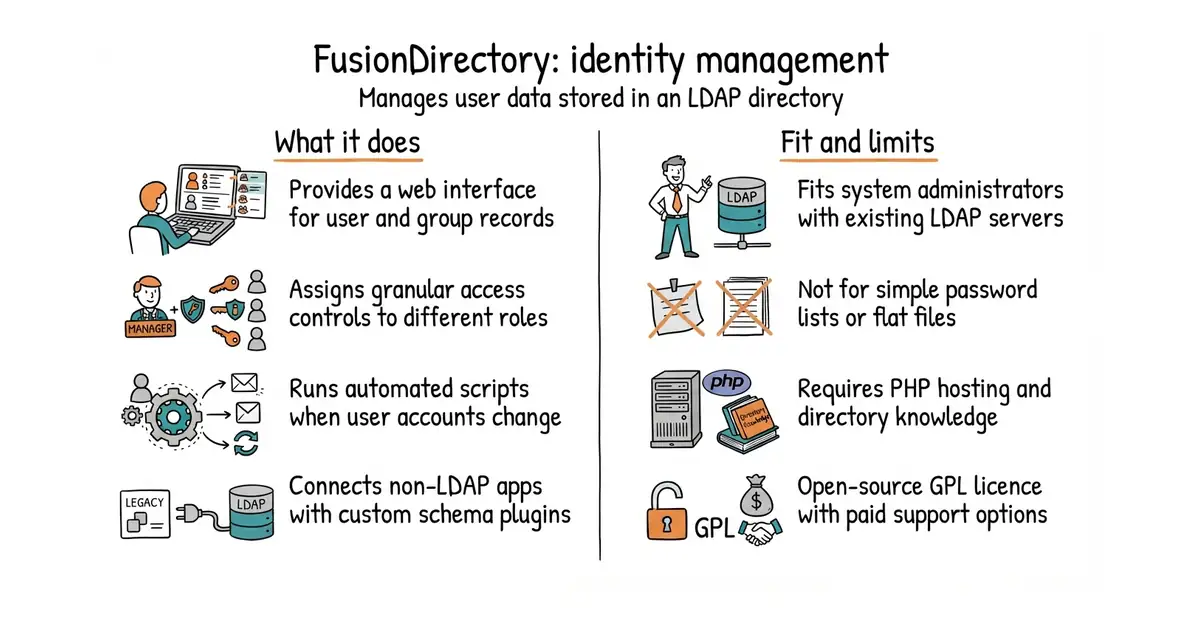

fusiondirectory/fusiondirectory
FusionDirectory is a modern, efficient and secure Identity Management (IAM) solution.

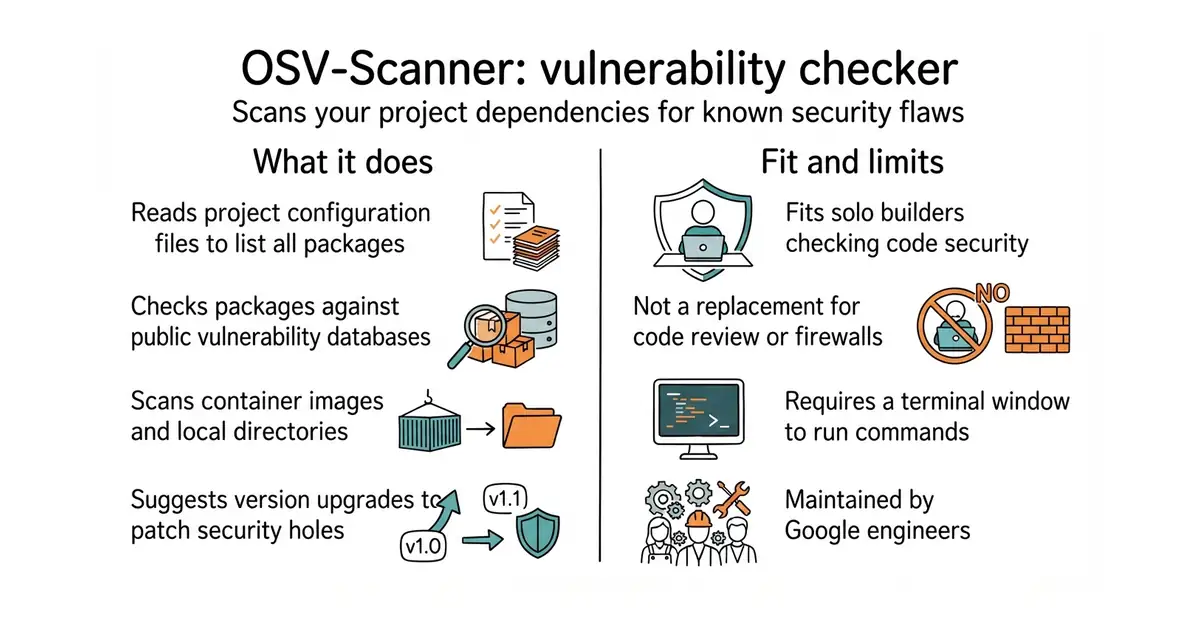

google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
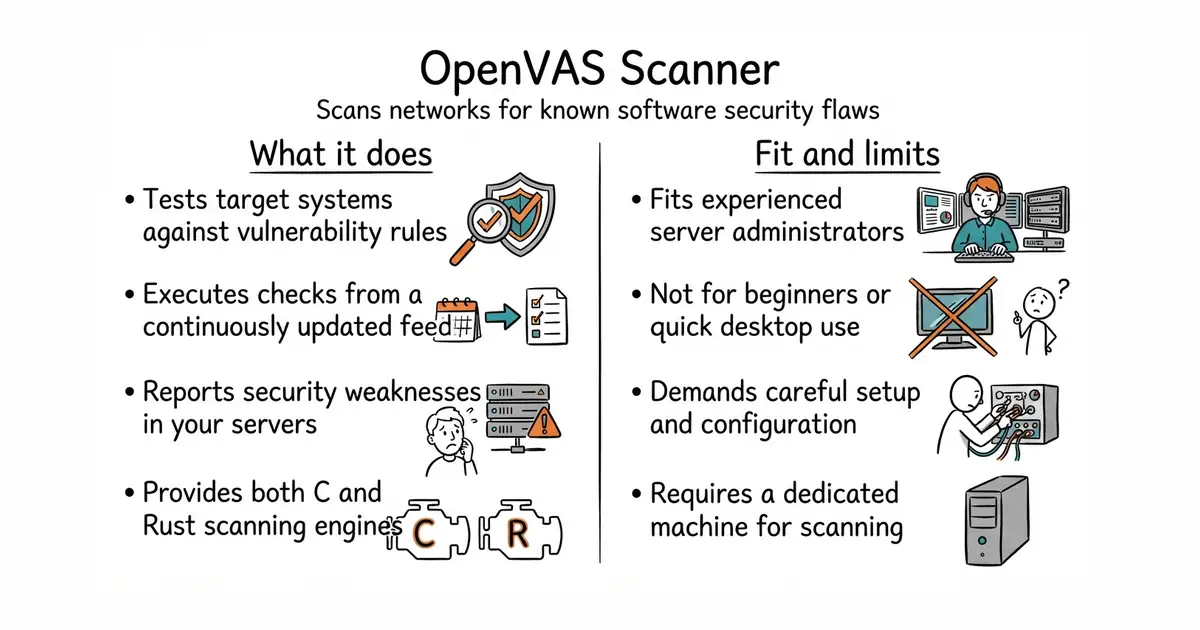

greenbone/openvas-scanner
This repository contains the scanner component for Greenbone Community Edition.

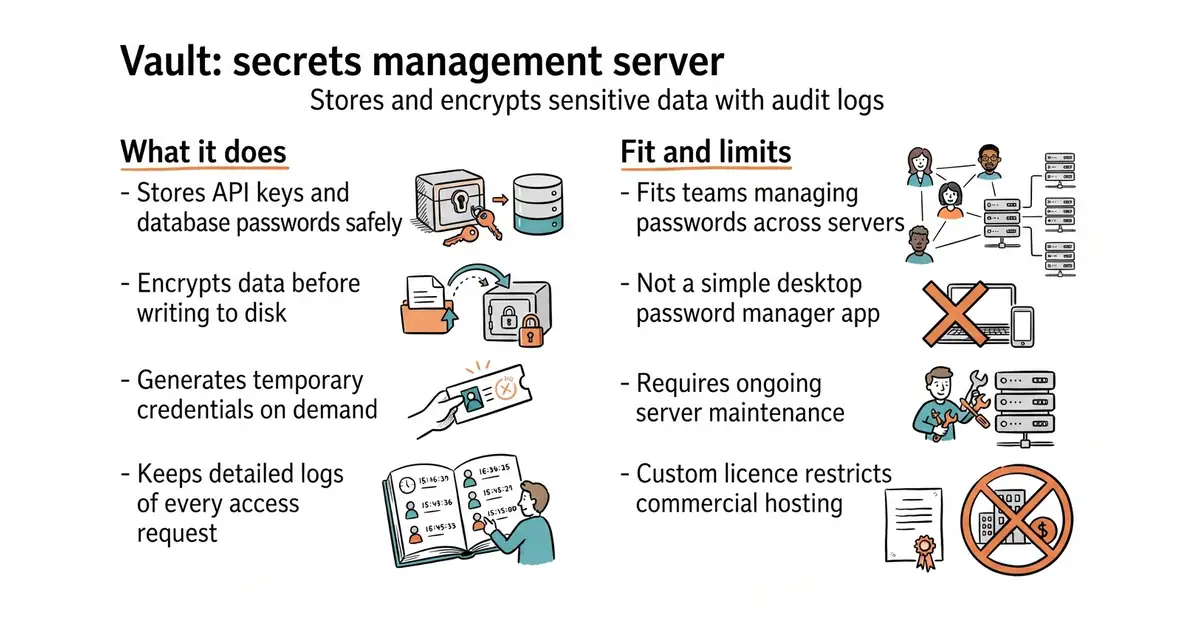

hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
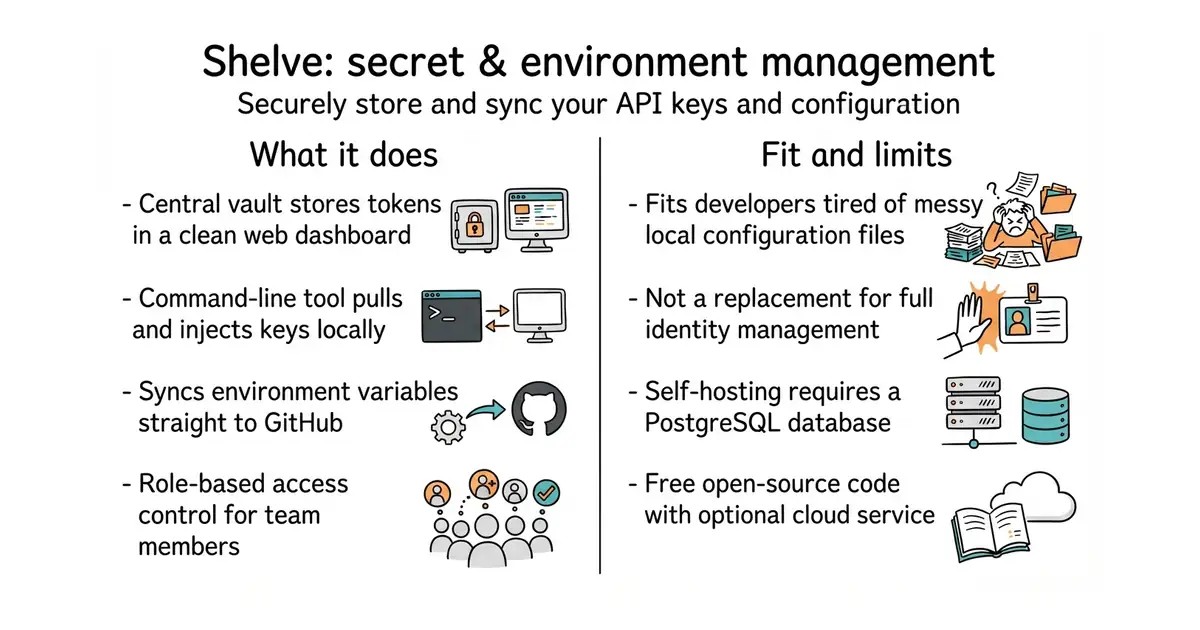

HugoRCD/shelve
Open-source secret & environment management. Secure, simple, collaborative. CLI & Github Sync
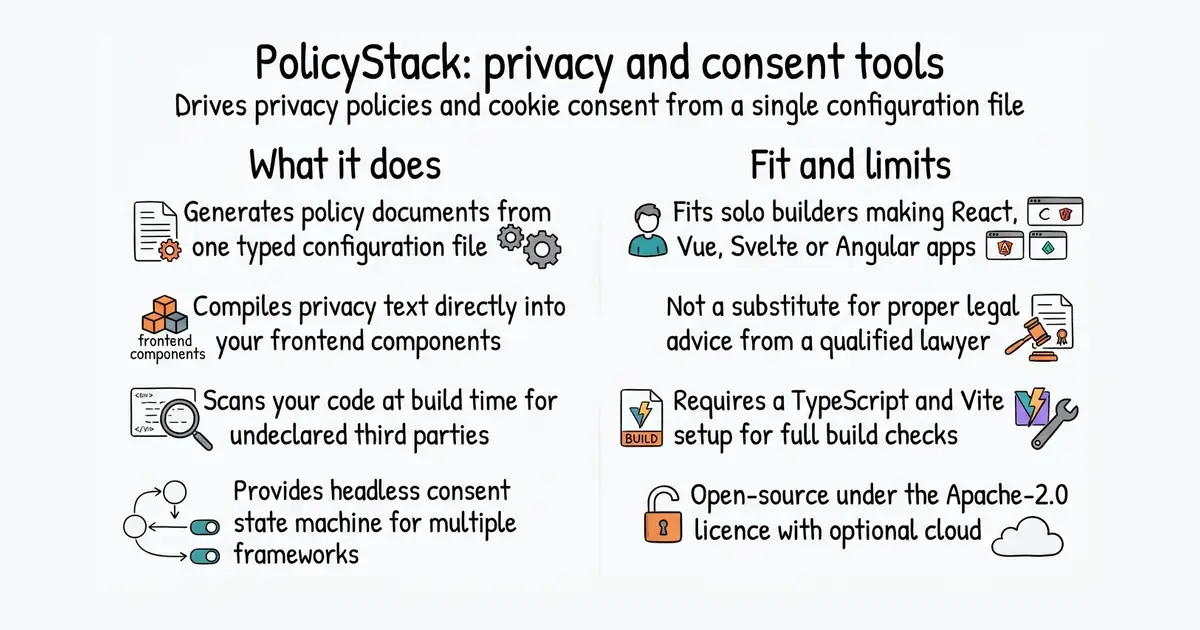

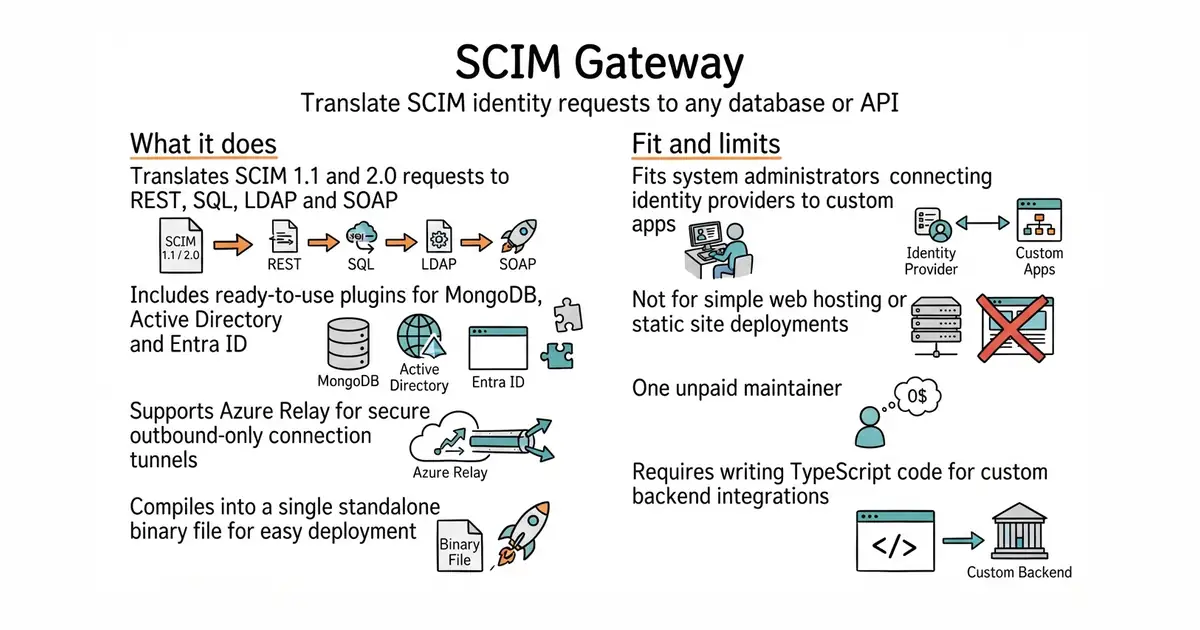

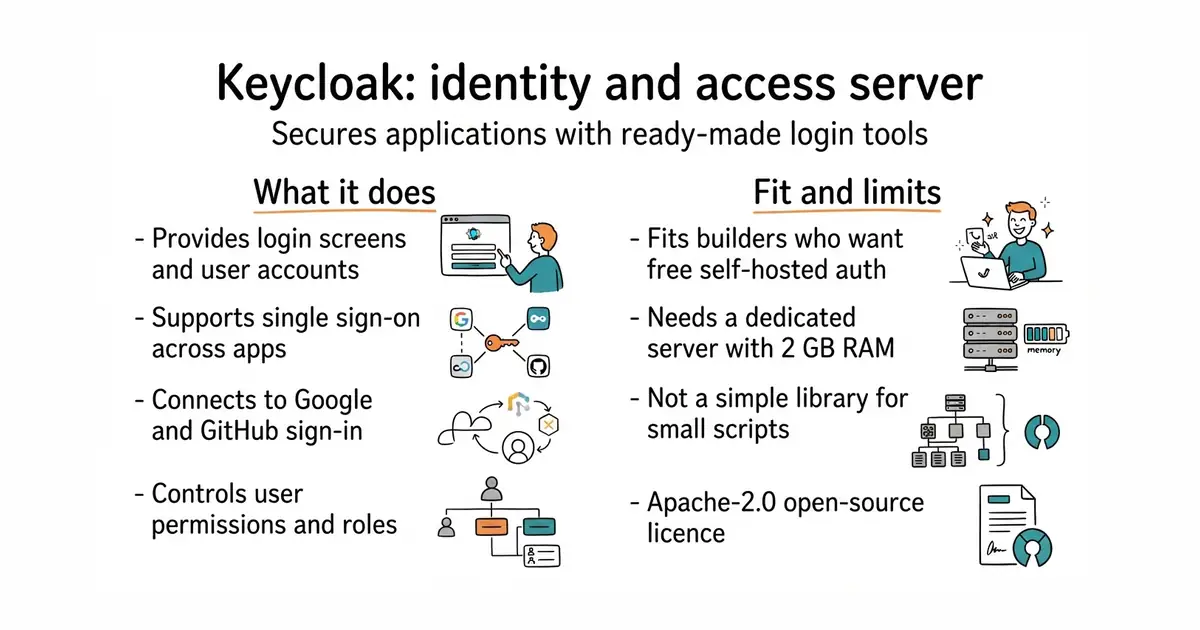

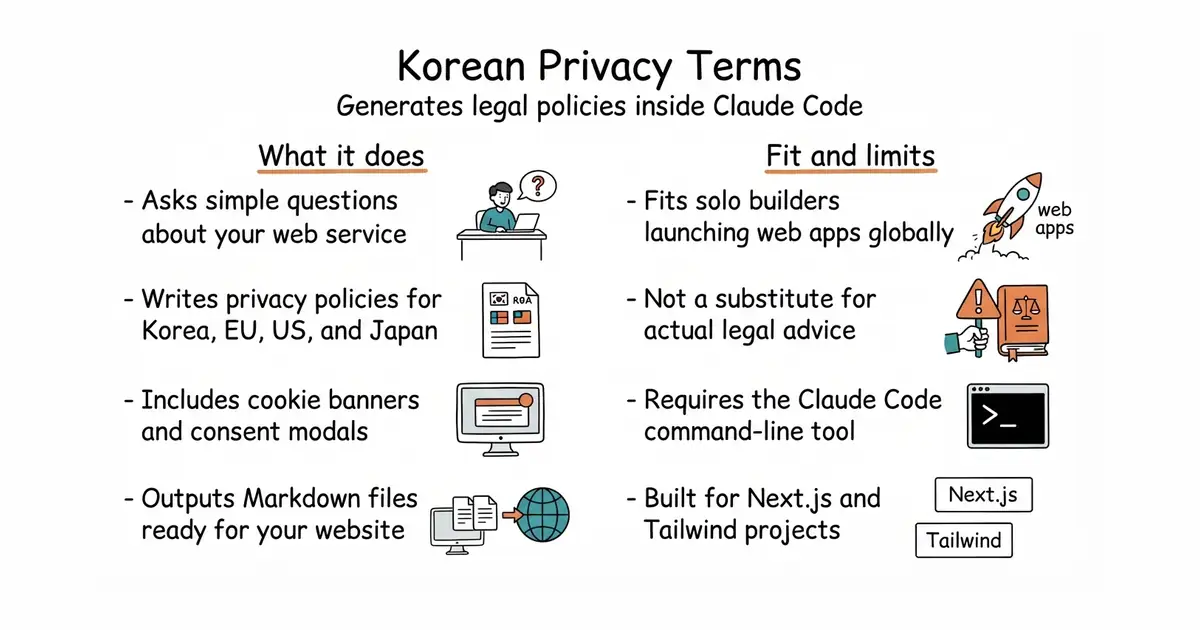

kimlawtech/korean-privacy-terms
한국 법령 기반 개인정보처리방침·이용약관 자동 생성 Claude Code 스킬. 2025.4.21 작성지침 및 2026.3 개정 법령 반영.


mr-tanta/ndpr-toolkit
Open-source React & TypeScript library for Nigeria Data Protection Act (NDPA) 2023 compliance. Cookie consent, DSR portal, DPIA, 72-hour breach notification, RoPA, lawful-basis, privacy-policy generator.
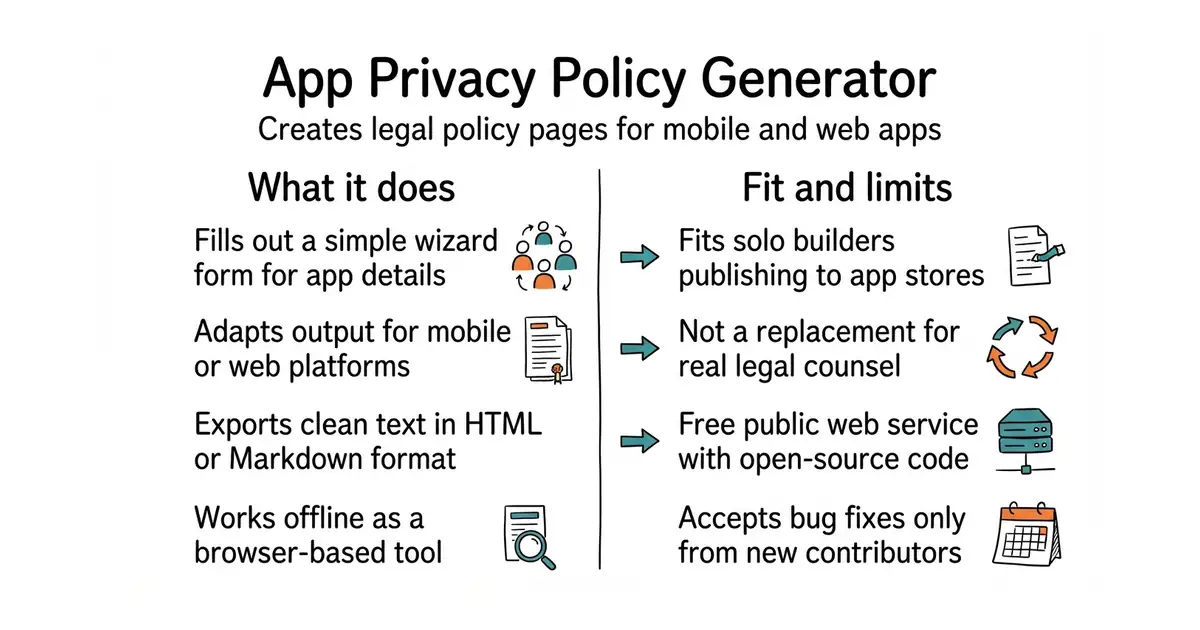

nisrulz/app-privacy-policy-generator
Generate a customized Privacy Policy and Terms of Use document for your mobile apps
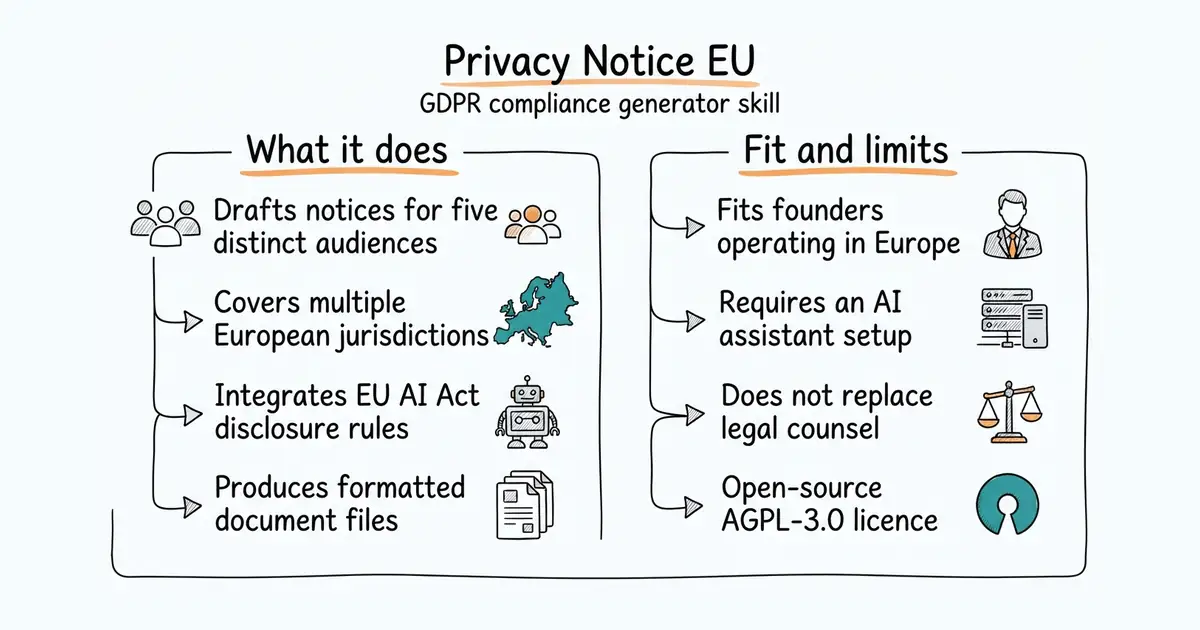
oliverschmidtprietz/GDPR-Privacy-Notice-EU
Pan-EU GDPR Privacy Notice Generator Agent Skill (open standard) — multi-jurisdiction drafting, 5 notice types, AI Act integration, audit-ready .docx output
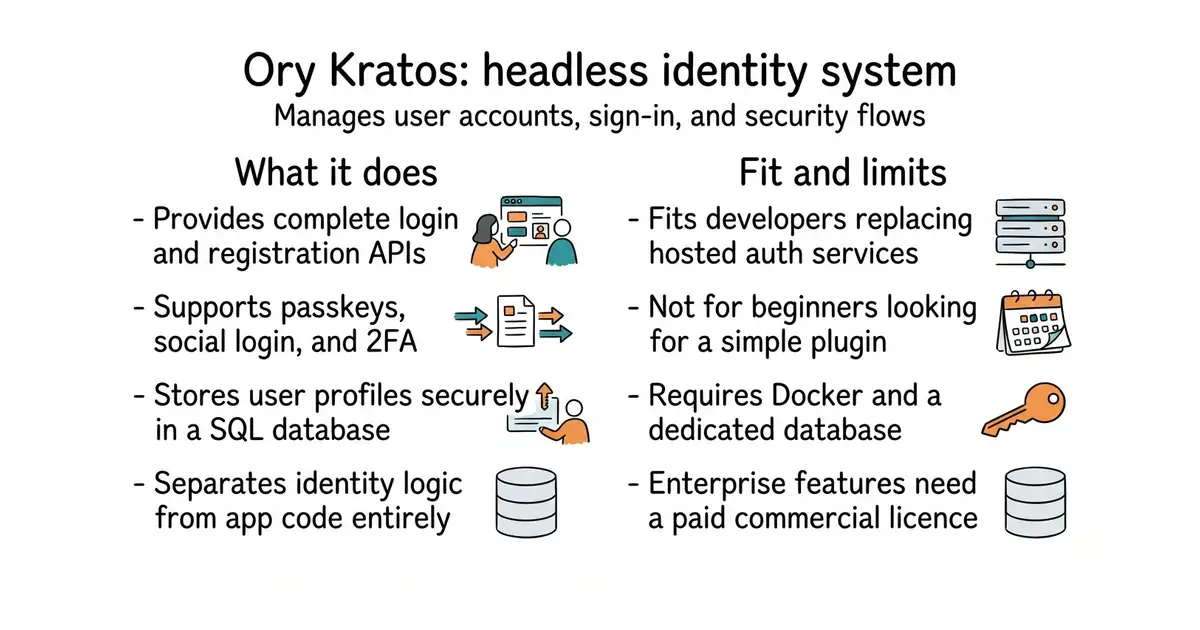

ory/kratos
Headless cloud-native authentication and identity management written in Go. Scales to a billion+ users. Replace Homegrown, Auth0, Okta, Firebase with better UX and DX. Passkeys, Social Sign In, OIDC, Magic Link, Multi-Factor Auth, SMS, SAML, TOTP, and more. Runs everywhere, runs best on Ory Network.

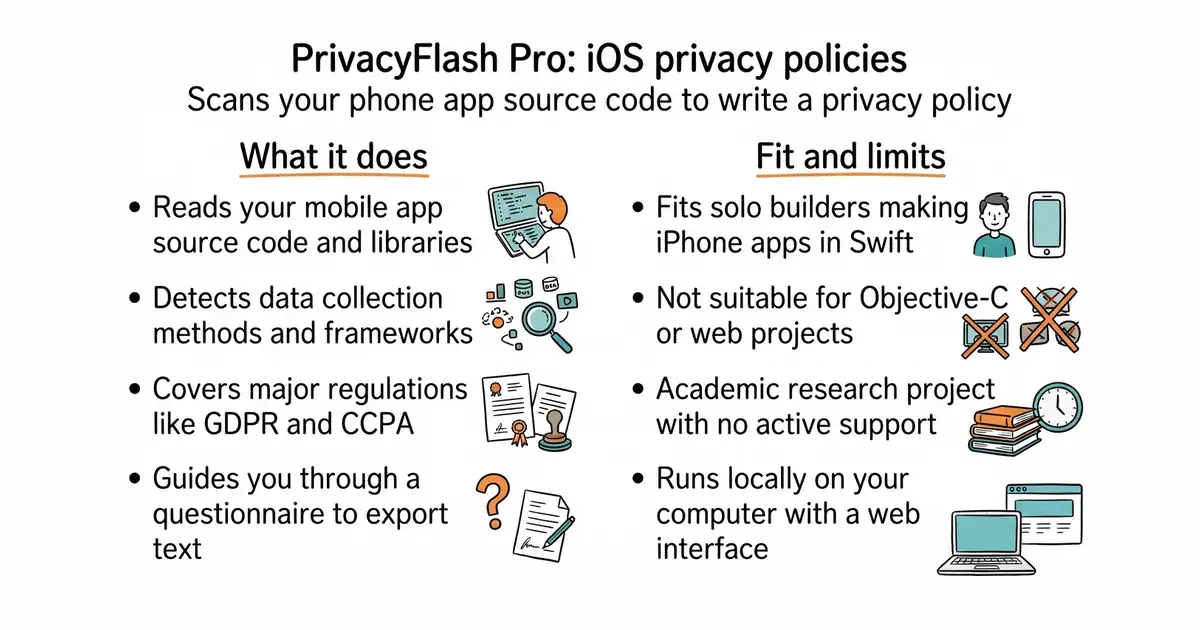

privacy-tech-lab/privacyflash-pro
Generate a privacy policy for your iOS app quickly and automatically
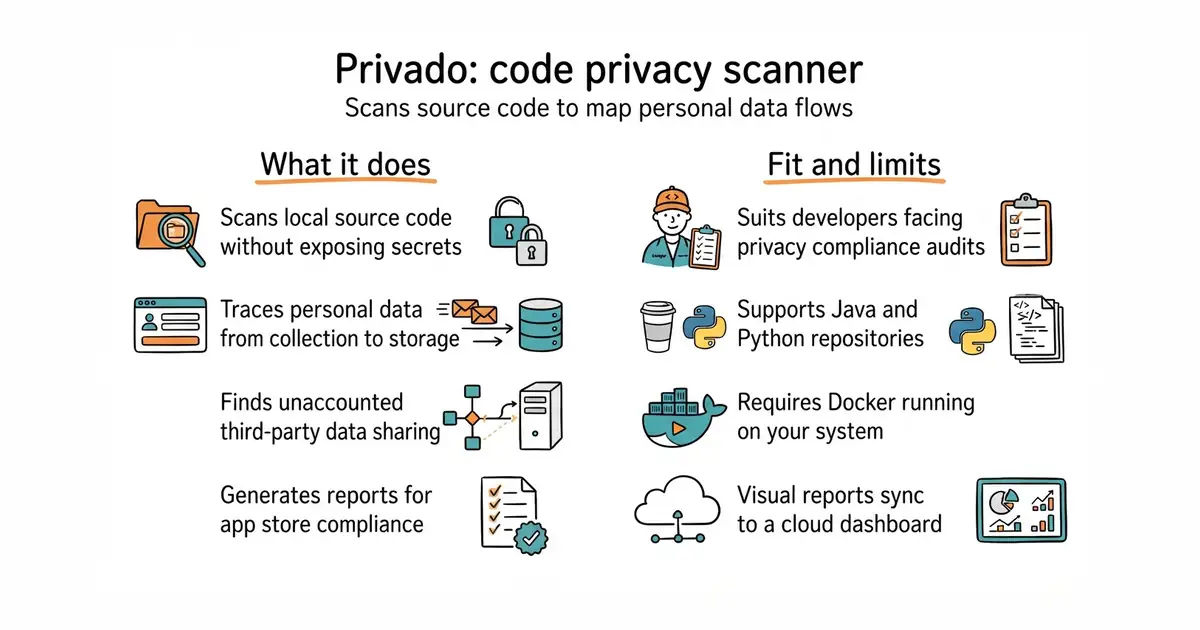

Privado-Inc/privado
Open Source Static Scanning tool to detect data flows in your code, find data security vulnerabilities & generate accurate Play Store Data Safety Report.
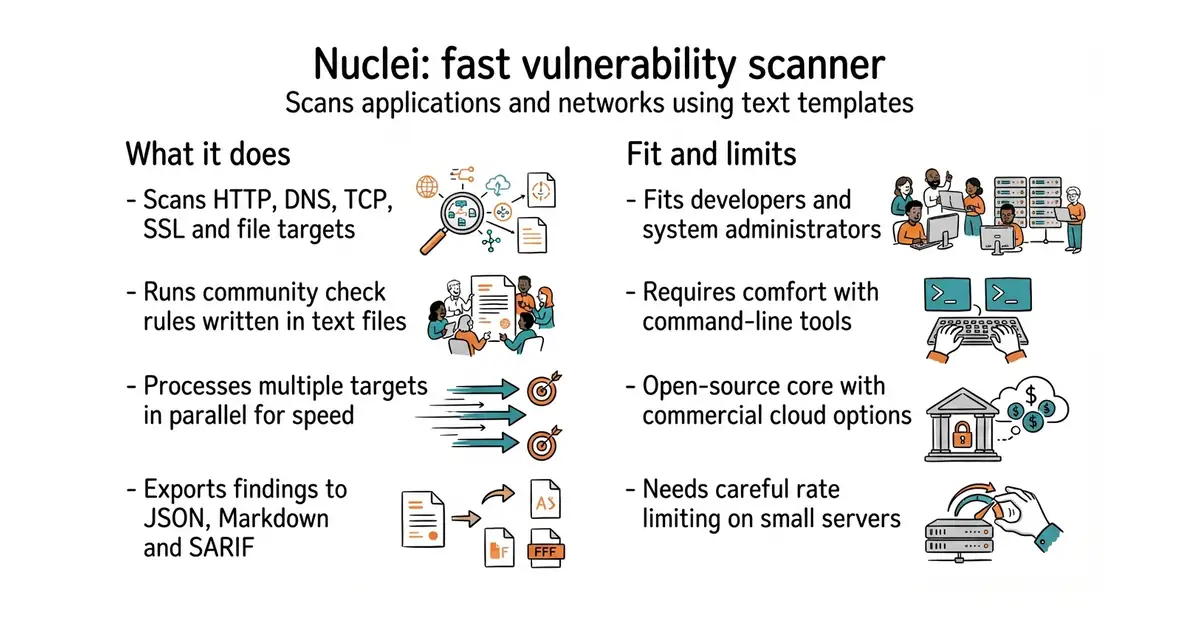

projectdiscovery/nuclei
Nuclei is a fast, customizable vulnerability scanner powered by the global security community and built on a simple YAML-based DSL, enabling collaboration to tackle trending vulnerabilities on the internet. It helps you find vulnerabilities in your applications, APIs, networks, DNS, and cloud configurations.
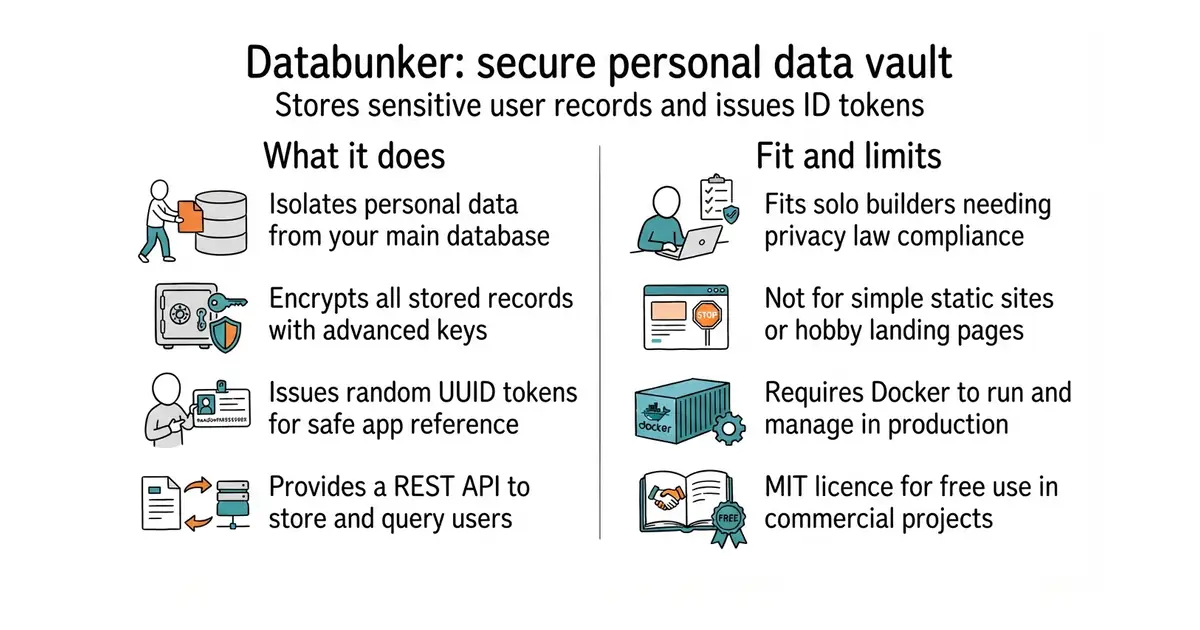

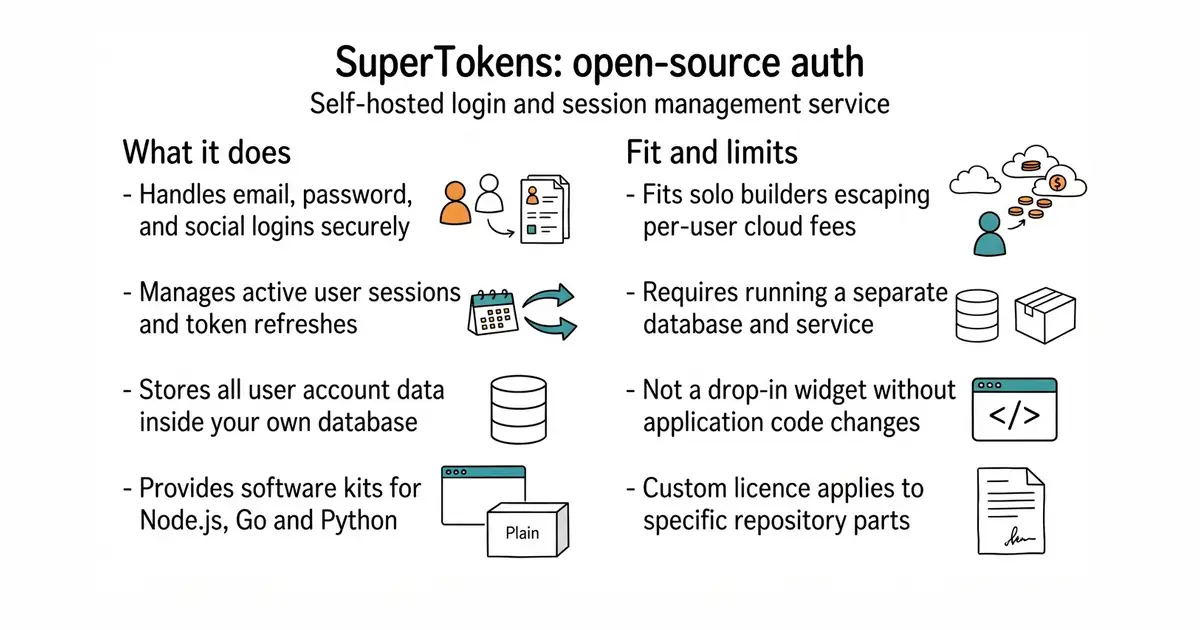

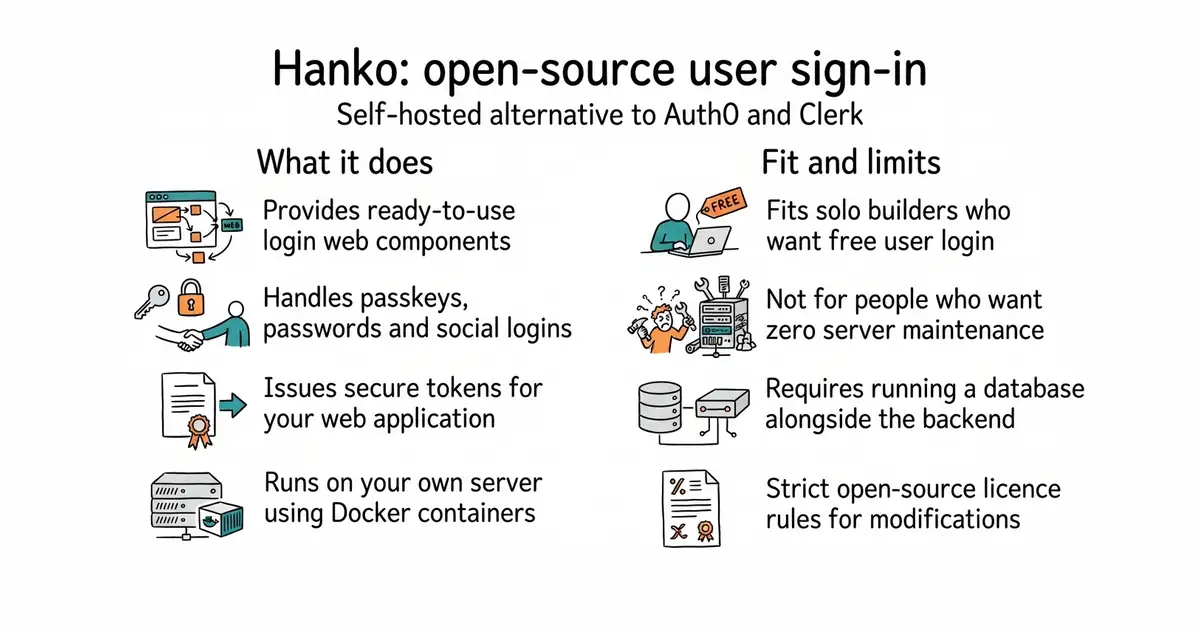

teamhanko/hanko
Modern authentication, on your terms. Open source alternative to Auth0, Clerk, WorkOS, Stytch.



No repository in this area carries every tag you picked.
Get the next edition in your inbox
A dozen repositories, opened and checked. The licence read, the last release dated, and the ones that did not make it named with the reason. It is the half most lists leave out.
No tracking pixels. One click to leave. The archive stays free either way.
We use your address to send the edition and nothing else. Confirm by email, leave in one click. How we handle it.
Suggest a repository
Any public GitHub repository, any size. If it is your own, that is welcome too. We read every suggestion, and some picks are made at random, so stars do not decide. Whatever we pick goes through the same checks as every other entry, and the review is written either way.
Thanks — it is in.
Every suggestion is read. The ones we pick appear in an edition, credited to you if you left a name.