5800 stars · Apache-2.0 (named in the About sidebar) · v5.6.0 (2026-10-12), read from /releases/latest as '12 Oct' and dated by the run · Track this in Scout
Scores a repository out of ten on nineteen measurable security habits, and names the ones it fails.
Radar check
What we found when we opened it. Every bar is one fact, with its date.
Last code pushed 26 Oct 2026, the same day before this check.
Latest release v5.6.0 on 12 Oct 2026.
Public since October 2020, about 6 years.
5,796 stars and 754 forks.
63 commits and 47 new issues in the last 90 days.
194 contributors. 62 pull requests merged in 90 days.
A security policy says how to report a problem. No published security advisories.
How the bars are scored
- Alive. Days since the last code push: a week or less 100, a month 90, three months 70, six months 50, a year 30, eighteen months 15, older 0.
- Releases. Age of the latest GitHub release, on a similar scale; no bar when the project publishes no releases.
- Maturity. Age of the project: eight years 100, five 90, three 70, two 55, one 40, six months 25, younger 10.
- Adoption. Stars on a log scale: 100,000 stars is 100, 10,000 is 80, 1,000 is 60, 100 is 40.
- Activity. Commits in the last 90 days: 300 or more 100, 100 85, 30 65, 10 45, any 25.
- Community. People who have contributed: 100 or more 100, 30 80, 10 60, 5 40, 2 25, one 10.
- Security. A published security policy 80, none 40; published advisories are listed, not scored.
Checked by Repo Radar on 26 Oct 2026 from the repository on GitHub. Covered in Edition 62.
▶Repo detailsthe review · specs · pros & cons · install
What it does
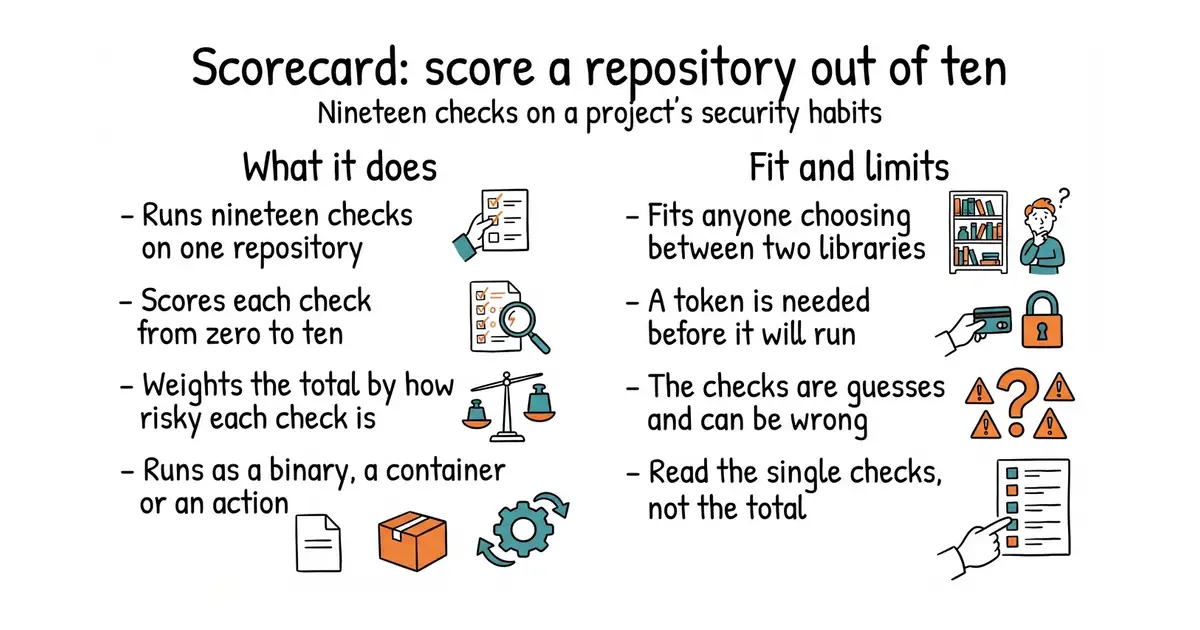
The default run performs nineteen checks, each scored from zero to ten and each carrying a risk level of critical, high, medium or low. The checks include Branch-Protection, Code-Review, Dangerous-Workflow, Pinned-Dependencies, Signed-Releases, Security-Policy, Token-Permissions, Fuzzing, SAST, Maintained and Vulnerabilities. The overall score is a weighted average, where a critical check counts ten, a high counts 7.5, a medium counts five and a low counts 2.5. It runs as a standalone binary, as a Docker image, as a GitHub Action that posts findings into the repository's security tab, and as a public interface at scorecard.dev with pre-computed scores for many well-known projects. Output is text or JSON. The project says plainly what it is not: the checks are heuristics with both false positives and false negatives, and the total is not a pass mark. A check can also return a question mark when it cannot decide.
Why it matters
Who it suits. Anyone choosing between two libraries that do the same job, and anyone maintaining a project who wants a list of concrete improvements rather than general advice. It suits a team that must answer a supplier questionnaire about the software it depends on. Skip it if you are treating the number as an answer rather than as a prompt, because the project itself says the score is not a requirement.
Verdict. Five minutes well spent, with one habit of mind attached. Version 5.6.0 was released on 12 October 2026 under the Apache-2.0 licence, from the Open Source Security Foundation. Run it on a dependency and read the individual checks rather than the total: "no security policy" and "dependencies not pinned" are specific and actionable, while the average of nineteen numbers is not. Two practical notes. GitHub limits unauthenticated requests, so a token is required — a personal access token with the public_repo scope is enough. The command-line tool officially supports macOS and Linux, and the project says Windows may have problems. For related work from the same foundation, ossf/allstar enforces these habits continuously instead of reporting them once.
- Nineteen specific, checkable habits rather than vague security advice.
- Runs as a binary, a container, a repository action or a lookup on the web.
- Pre-computed scores already exist for many well-known projects, so the first answer takes no setup.
- Needs a GitHub token, and some checks need a maintainer's token to see branch settings.
- Heuristics, with false positives and false negatives, which the project states openly.
- Windows support is described as possibly problematic, and the command-line build needs Go.
- ossf/allstar
1.5k stars, Apache-2.0; watches an organisation continuously and opens an issue, or corrects the setting, when a policy is broken.
Track this in Scout - ossf/cve-bin-tool
1.8k stars, GPL-3.0; a different question, scanning binaries and component lists for known vulnerabilities rather than judging development habits. The address intel/cve-bin-tool now redirects here.
Track this in Scout
# create a token with the public_repo scope at github.com/settings/tokens
export GITHUB_AUTH_TOKEN=your_token_here
docker run -e GITHUB_AUTH_TOKEN \
  ghcr.io/ossf/scorecard:stable \
  --repo=github.com/pdfminer/pdfminer.six