In simple English
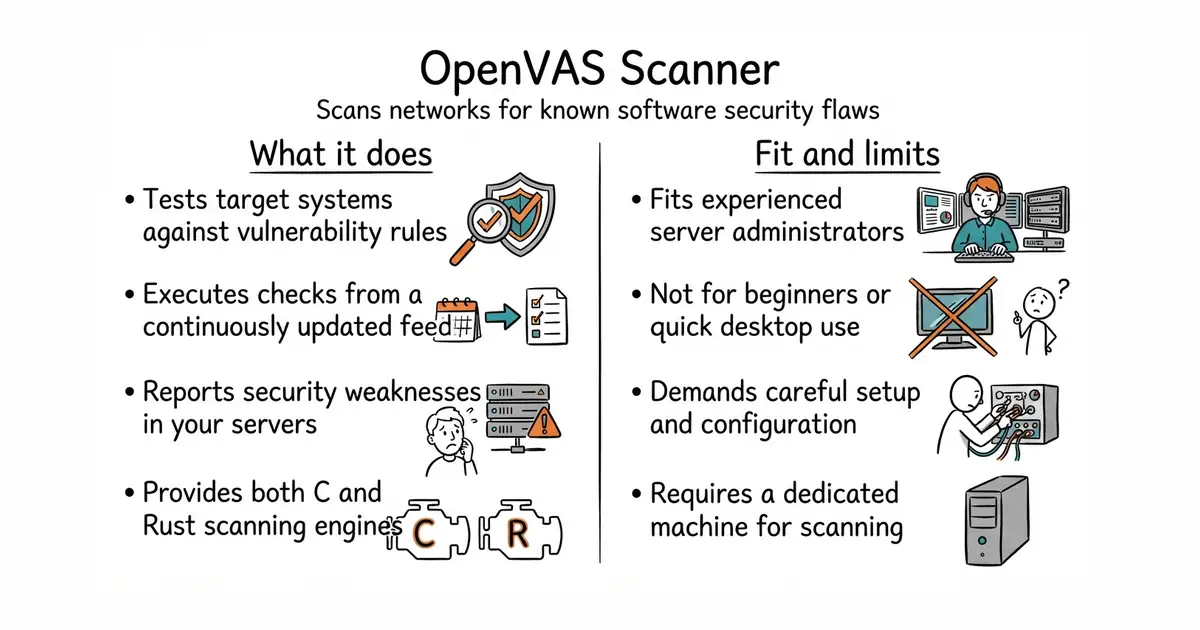
This tool checks your servers and network for security holes. It runs a large list of known software flaws against your systems. You use it to find weak spots before attackers do. Setting it up takes considerable patience and technical knowledge. It is free to use under an open source licence.
What it is
This repository contains the scanning engine for Greenbone Community Edition, a popular vulnerability assessment system. It tests target systems against a continuously updated feed of security checks and reports what needs fixing.
What it is good for
Solo builders who manage their own servers and need a comprehensive security audit to find exposed software bugs and misconfigurations.
- Runs thousands of detailed vulnerability tests against your servers.
- Part of a well-known open source security assessment platform.
- Actively maintained with regular updates to detection rules.
- Very difficult to set up and configure for a non-programmer.
- Requires a powerful server with substantial memory to run large scans.
- GPL-2.0 licence places restrictions if you modify and distribute the code.
manual security auditing and commercial vulnerability scanners
Docker
- bee-san/RustScan21k stars
Fast port scanner that discovers open ports before running vulnerability tools.
- projectdiscovery/nuclei32k stars
Template-based vulnerability scanner for finding security flaws in web applications.


- smallstep/certificates9.0k stars
A certificate authority you run yourself, for machines the public internet cannot reach.
- michelp/pgsodium614 stars
A PostgreSQL extension that brings libsodium's encryption functions into SQL, with a root key the database cannot read back.
- pgaudit/pgaudit1.7k stars
A PostgreSQL extension that records what was done to the database, in the database's own log.
cmake .
make install