In simple English
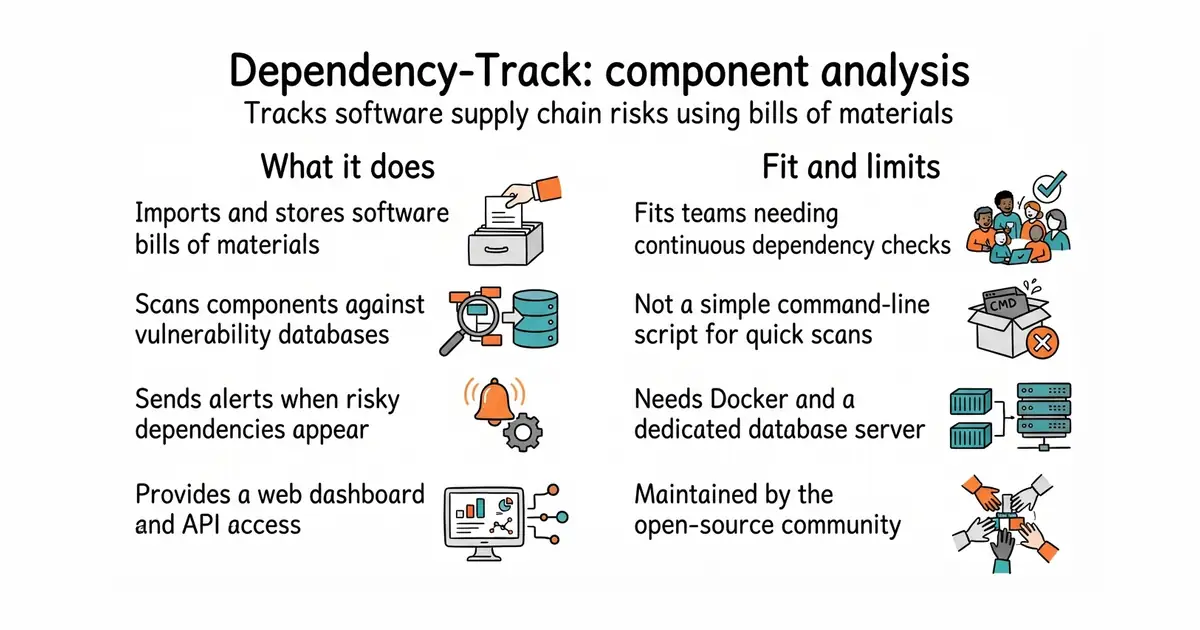
Modern software relies on hundreds of external pre-written packages. If one of those packages has a security flaw, your entire app is at risk. This tool keeps a central inventory of every component in your software. It checks those components against vulnerability databases every day. If a match appears, it alerts you so you can update the code. It is free to run on your own server, but it needs regular maintenance and a dedicated database.
What it is
Dependency-Track is an open-source component analysis platform. It processes Software Bill of Materials (SBOM, a machine-readable list of all software components inside an application) files to spot risks in your supply chain.
What it is good for
Solo builders and teams who need to prove security compliance to enterprise clients, or anyone who wants a single dashboard to monitor hundreds of open-source dependencies across multiple projects.
- Monitors thousands of components automatically against public vulnerability databases.
- Provides a clean web dashboard and API for CI/CD pipelines.
- Uses standard SBOM formats like CycloneDX so it works with most build tools.
- Requires Docker (a way to run a program inside its own sealed box, so it cannot break anything else on your server) and a separate PostgreSQL database to run.
- Needs at least 2 to 4 GB of memory, so check your server has room.
- Heavy setup process for non-programmers who just want a simple scanner.
manual security audits and scattered dependency checkers
GitHub Actions
- anchore/grype13k stars
A command-line vulnerability scanner for container images and files, whereas this is a full self-hosted server platform.

- smallstep/certificates9.0k stars
A certificate authority you run yourself, for machines the public internet cannot reach.
- michelp/pgsodium614 stars
A PostgreSQL extension that brings libsodium's encryption functions into SQL, with a root key the database cannot read back.
- pgaudit/pgaudit1.7k stars
A PostgreSQL extension that records what was done to the database, in the database's own log.
docker compose up -d