In simple English
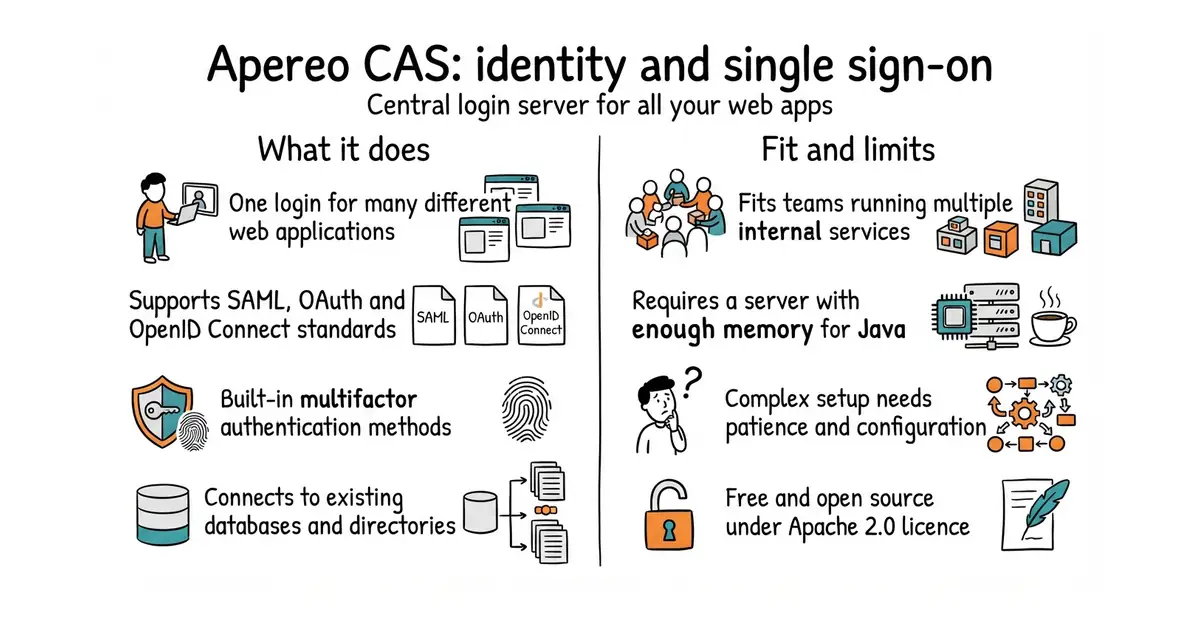
This tool lets people log in once and access many different web apps. It is a central server for user accounts, passwords and security checks. You can run it on your own server for free. It supports major login standards like SAML, OAuth and OpenID Connect. Setting it up takes patience and knowledge of Java server tools.
What it is
Apereo CAS is an enterprise single sign-on server built on Java, Spring Boot (a tool for building web apps in Java quickly) and Spring Cloud (a toolkit for building connected services). It acts as the central hub where users type their passwords before going to your other applications.
What it is good for
Teams that run multiple web apps and want users to log in just once across all of them. It removes the need to build separate login pages for every new service you launch.
- Supports almost every known authentication protocol and method out of the box.
- Free and open source with a large community of active users and regular updates.
- Can store user data in databases, LDAP directories or cloud services you already use.
- Requires a server with enough memory to run Java applications smoothly.
- Complex configuration files can take hours to understand and get right.
- Not a beginner project if you have never managed a Java web server before.
building custom login systems or paying for commercial identity providers
Spring Boot (a way to build web apps in Java quickly) for building custom authentication extensions
- keycloak/keycloak37k stars
An open source identity and access management server with a built-in admin console, written in Java.
- authelia/authelia29k stars
A lighter single sign-on portal and multi-factor authentication server written in Go.


- pgaudit/pgaudit1.7k stars
A PostgreSQL extension that records what was done to the database, in the database's own log.
- openbao/openbao8.6k stars
A secrets manager that stores keys and passwords, hands them out on request, and can revoke them.
- future-architect/vuls12k stars
Scans Linux machines over SSH for installed software with publicly reported security holes.
docker run --rm -p 8080:8080 \
  -e SERVER_SSL_ENABLED=false -e SERVER_PORT=8080 \
  apereo/cas:8.0.2