In simple English
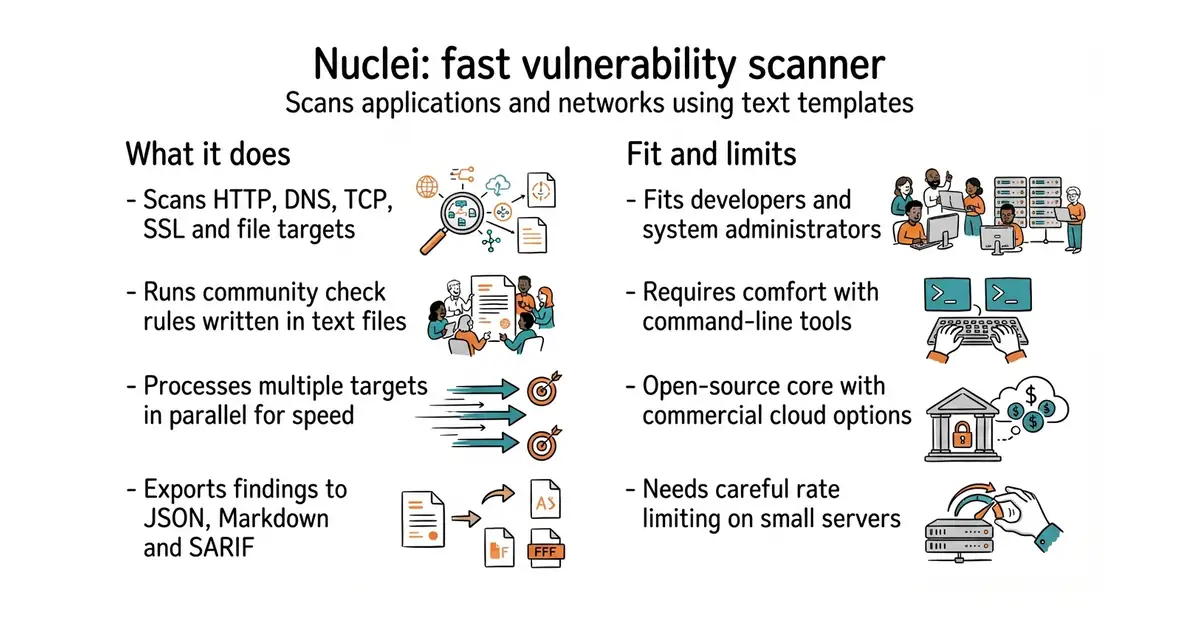
Nuclei is a security scanner that checks your web applications, servers and network for known flaws and bad configurations. It reads check rules written in a simple text format called YAML (a human-friendly way to write data and configuration settings). You run it from your command line to test a single website or a whole list of domains. It costs nothing to use the main open-source version, but you need some comfort with the terminal to set it up.
What it is
Nuclei is an open-source vulnerability scanner built in Go (a compiled programming language designed for fast, concurrent network services). It uses community-created check templates to find security holes without raising many false alarms.
What it is good for
It helps solo developers and system administrators run automated security checks on their infrastructure before hackers find the same weaknesses.
- Runs checks very quickly across large lists of targets in parallel.
- Uses simple text files for test rules, making custom checks easy to write.
- Backed by an active global community that constantly adds new security checks.
- Requires Go (a programming language for building software) version 1.27.3 or newer to install from source.
- Running aggressive scans against networks you do not own can trigger legal trouble.
- Failing to tune concurrency settings can overwhelm small servers and cause downtime.
Traditional closed-source security scanners and manual penetration testing.
Used together with httpx (a fast tool for probing web servers) to gather target lists before scanning.
- zaproxy/zaproxy16k stars
An open-source web application security scanner with a graphical interface and automated testing tools.
- sqlmapproject/sqlmap39k stars
An automated tool that specifically detects and exploits SQL injection flaws rather than general vulnerabilities.


- smallstep/certificates9.0k stars
A certificate authority you run yourself, for machines the public internet cannot reach.
- michelp/pgsodium614 stars
A PostgreSQL extension that brings libsodium's encryption functions into SQL, with a root key the database cannot read back.
- pgaudit/pgaudit1.7k stars
A PostgreSQL extension that records what was done to the database, in the database's own log.
go install -v github.com/projectdiscovery/nuclei/v3/cmd/nuclei@latest