1.3k stars · Apache-2.0 | v2.13.0, 13 Oct 2026 | [mongodb.github.io/kingfisher](https://mongodb.github.io/kingfisher/) · v2.13.0 (2026-10-13) · Track this in Rising ↗
Finds keys left in code, then checks which of them still work.
Radar check
What we found when we opened it. Every bar is one fact, with its date.
Last code pushed 20 Oct 2026, 8 days before this check.
Latest release v2.14.0 on 20 Oct 2026.
Public since May 2025, a little over 1 year.
1,275 stars and 124 forks.
185 commits and 43 new issues in the last 90 days.
20 contributors. 37 pull requests merged in 90 days.
A security policy says how to report a problem. No published security advisories.
How the bars are scored
- Alive. Days since the last code push: a week or less 100, a month 90, three months 70, six months 50, a year 30, eighteen months 15, older 0.
- Releases. Age of the latest GitHub release, on a similar scale; no bar when the project publishes no releases.
- Maturity. Age of the project: eight years 100, five 90, three 70, two 55, one 40, six months 25, younger 10.
- Adoption. Stars on a log scale: 100,000 stars is 100, 10,000 is 80, 1,000 is 60, 100 is 40.
- Activity. Commits in the last 90 days: 300 or more 100, 100 85, 30 65, 10 45, any 25.
- Community. People who have contributed: 100 or more 100, 30 80, 10 60, 5 40, 2 25, one 10.
- Security. A published security policy 80, none 40; published advisories are listed, not scored.
Checked by Repo Radar on 26 Oct 2026 from the repository on GitHub. Covered in Edition 16.
▶Repo detailsthe review · specs · pros & cons · install
What it does
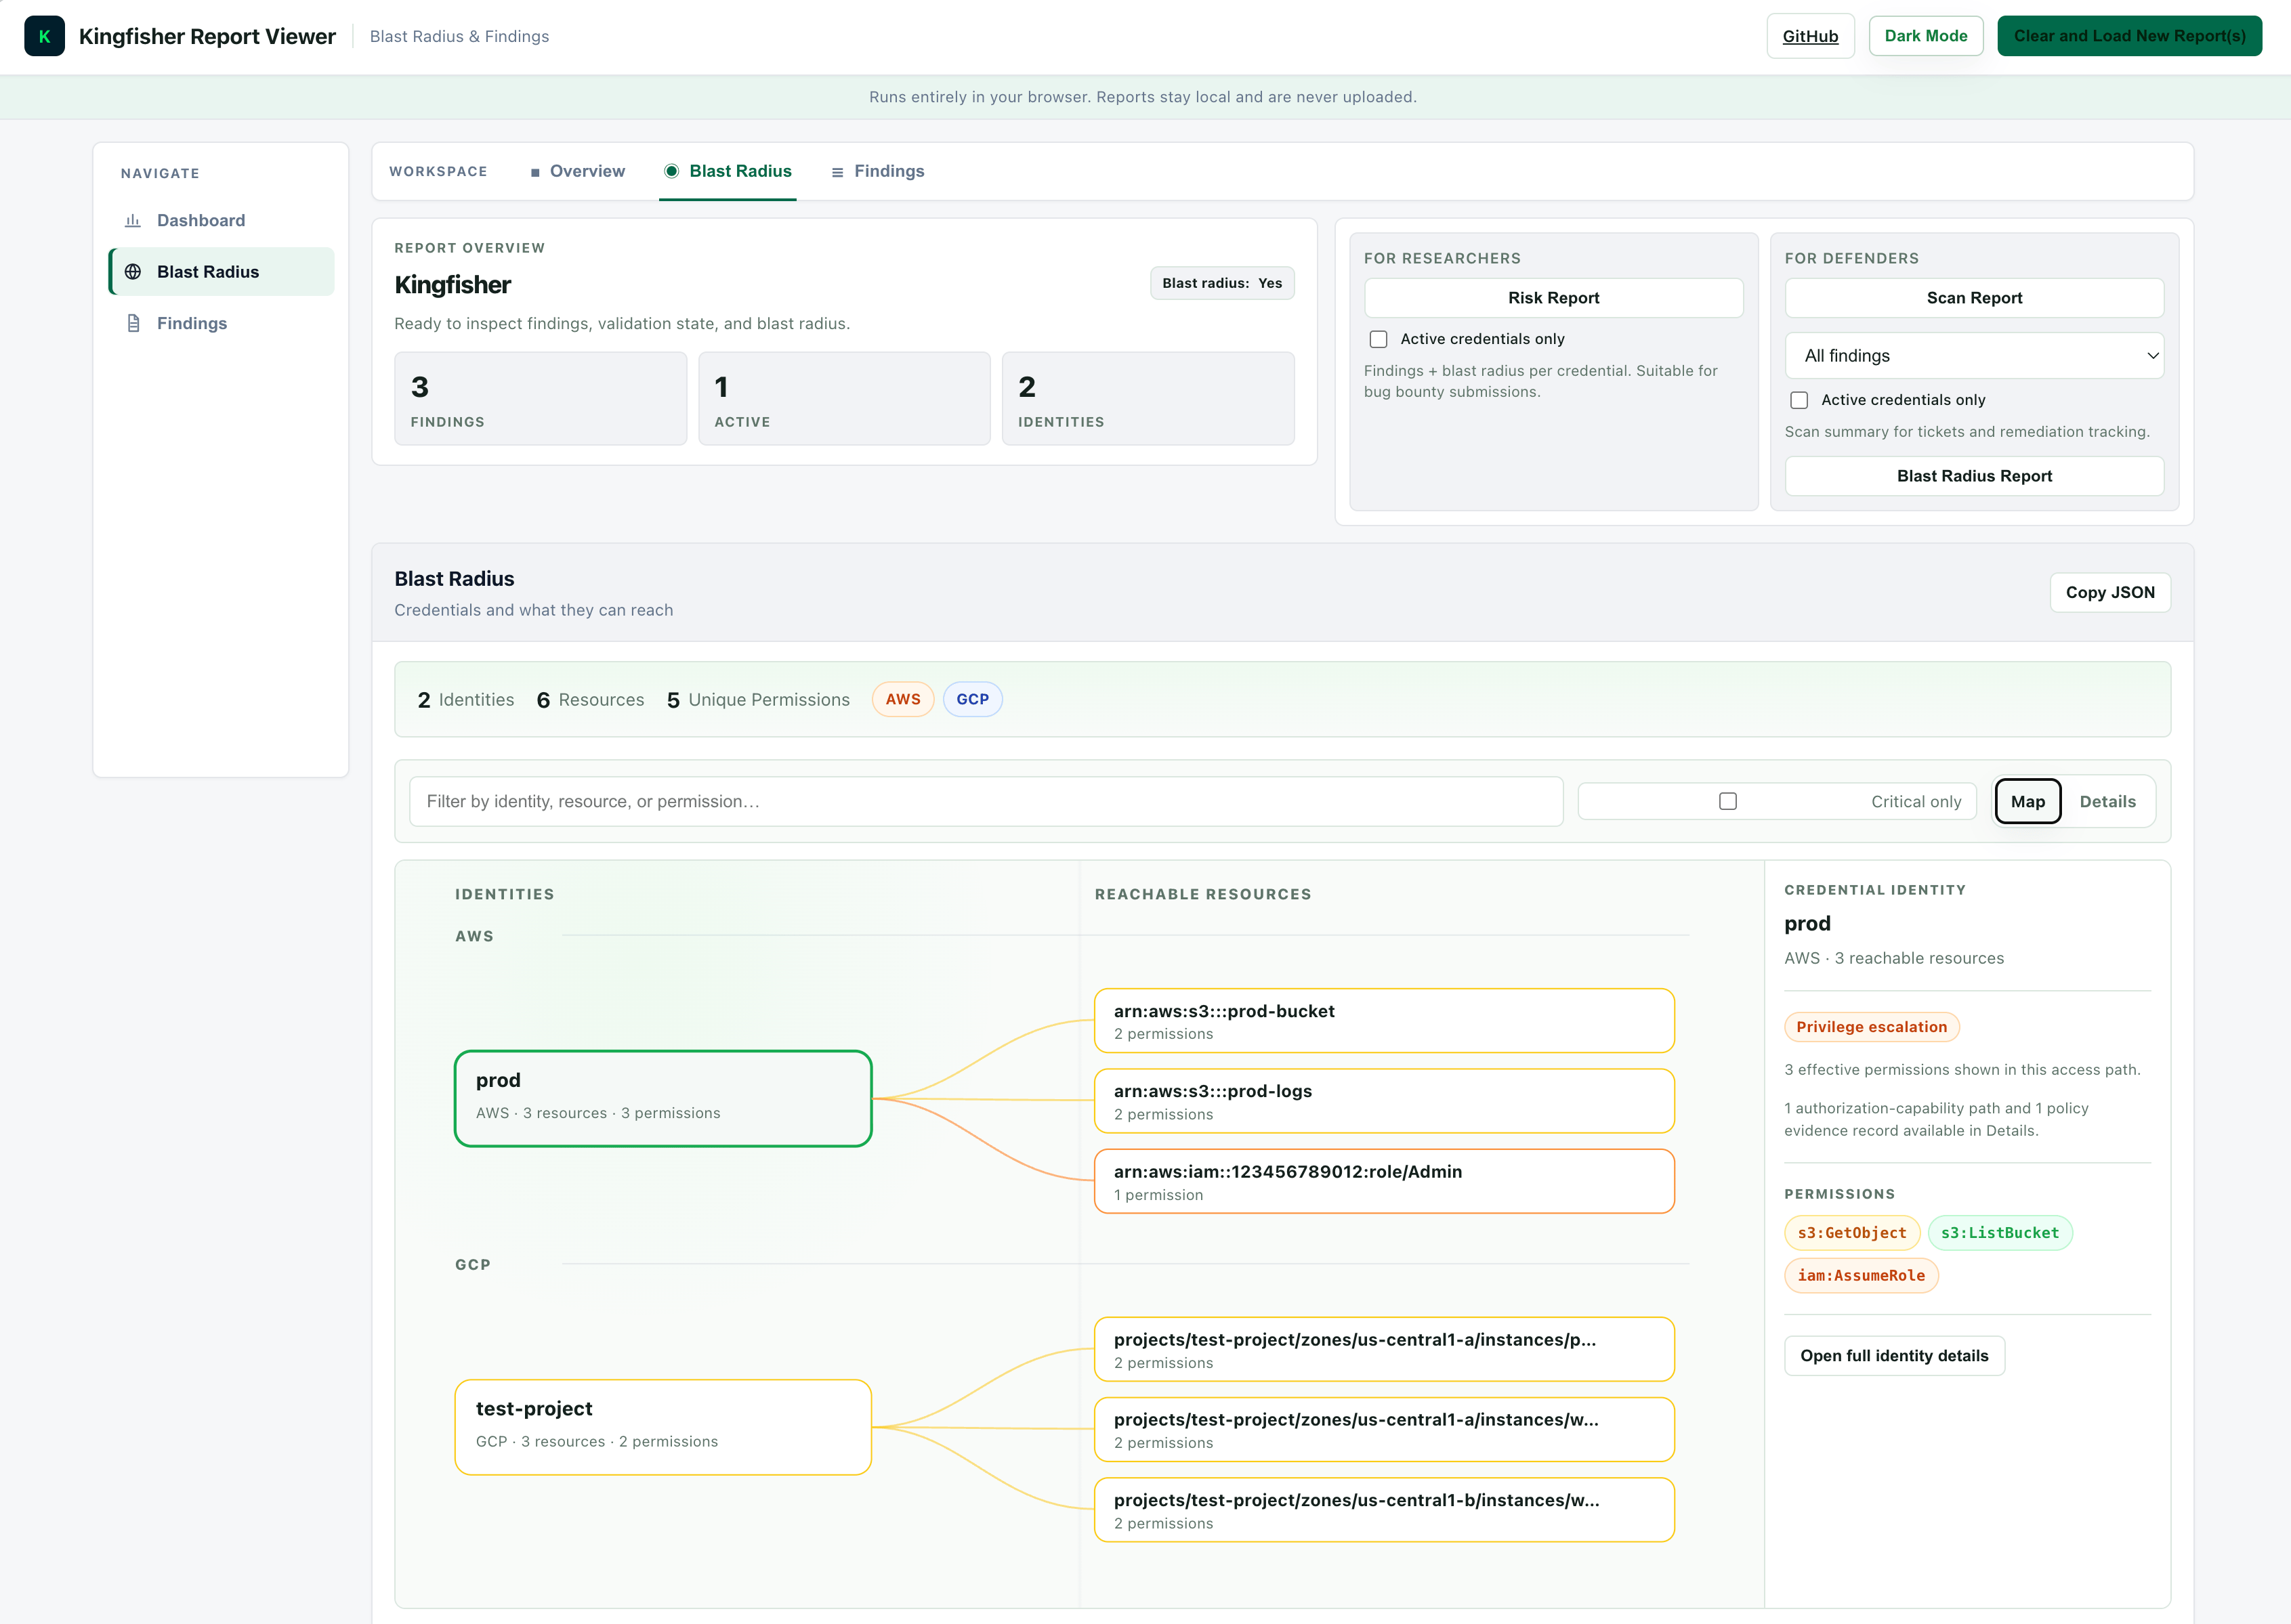
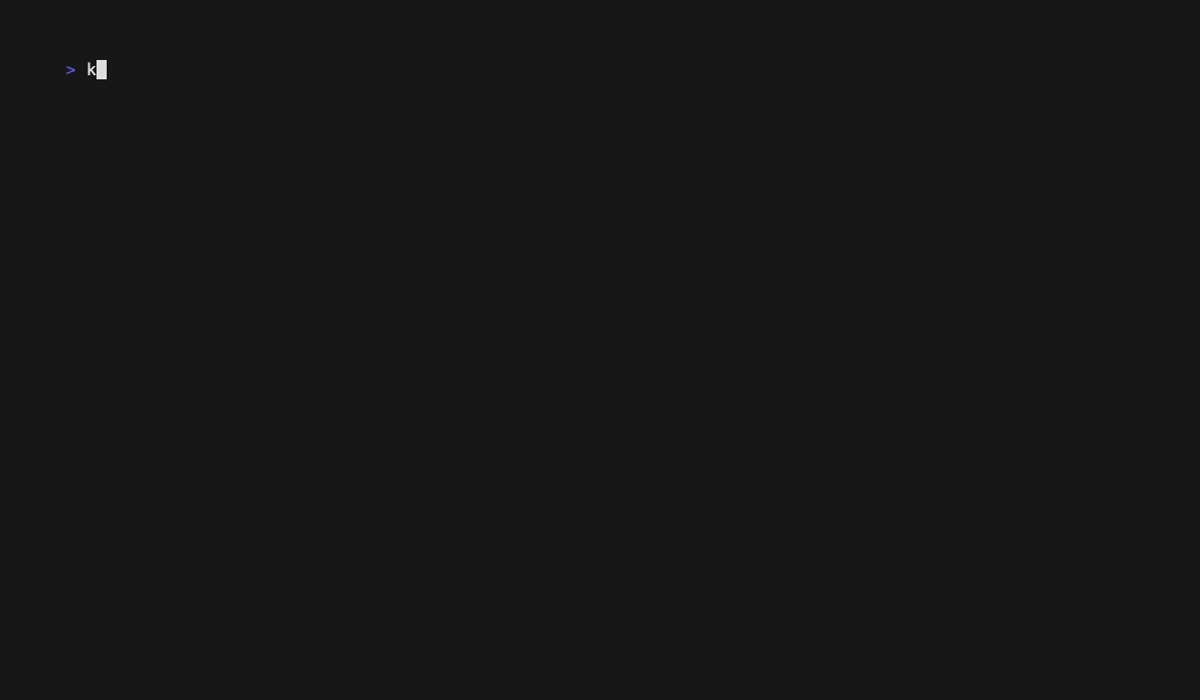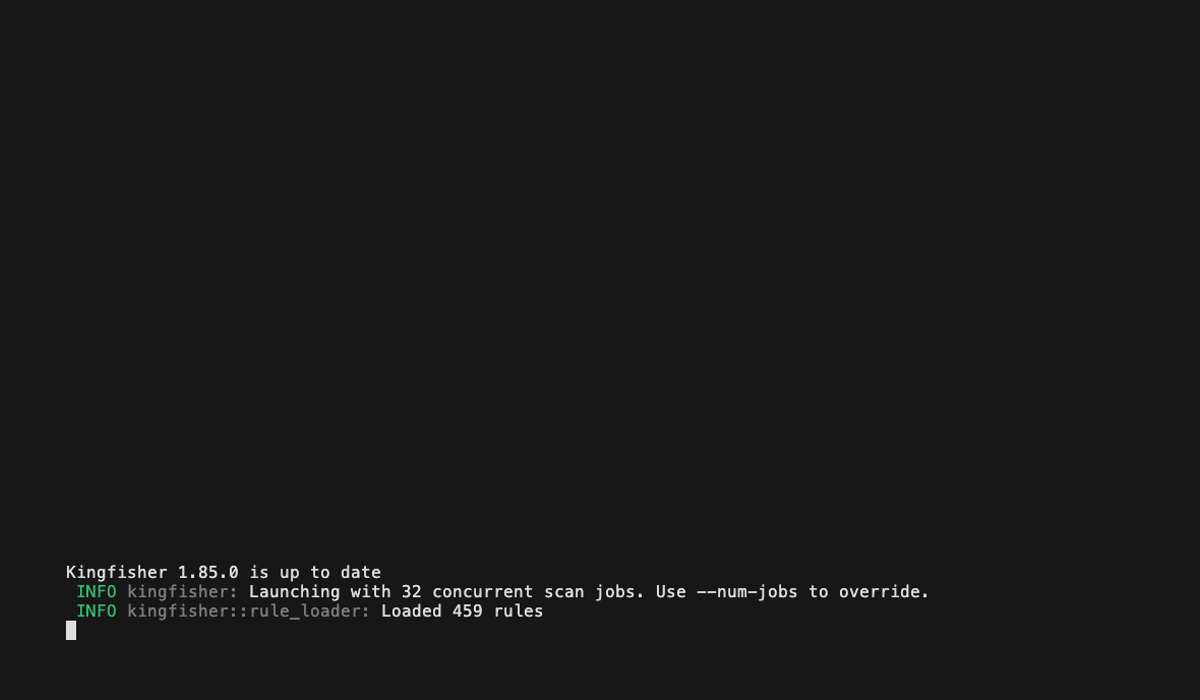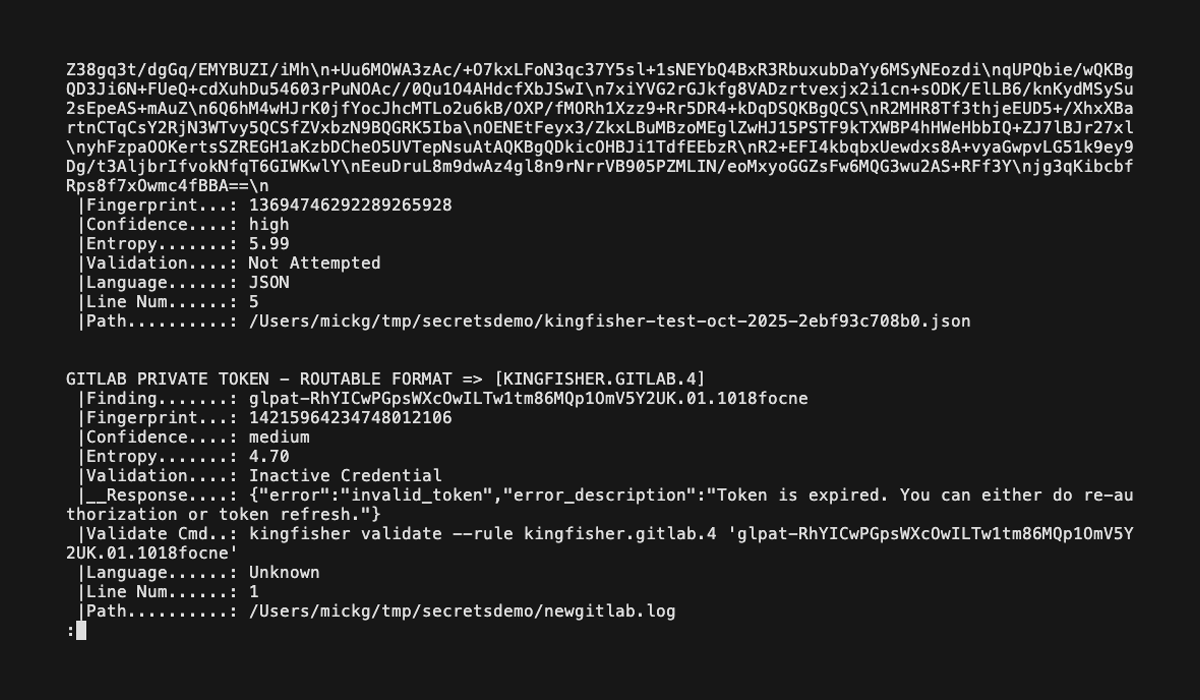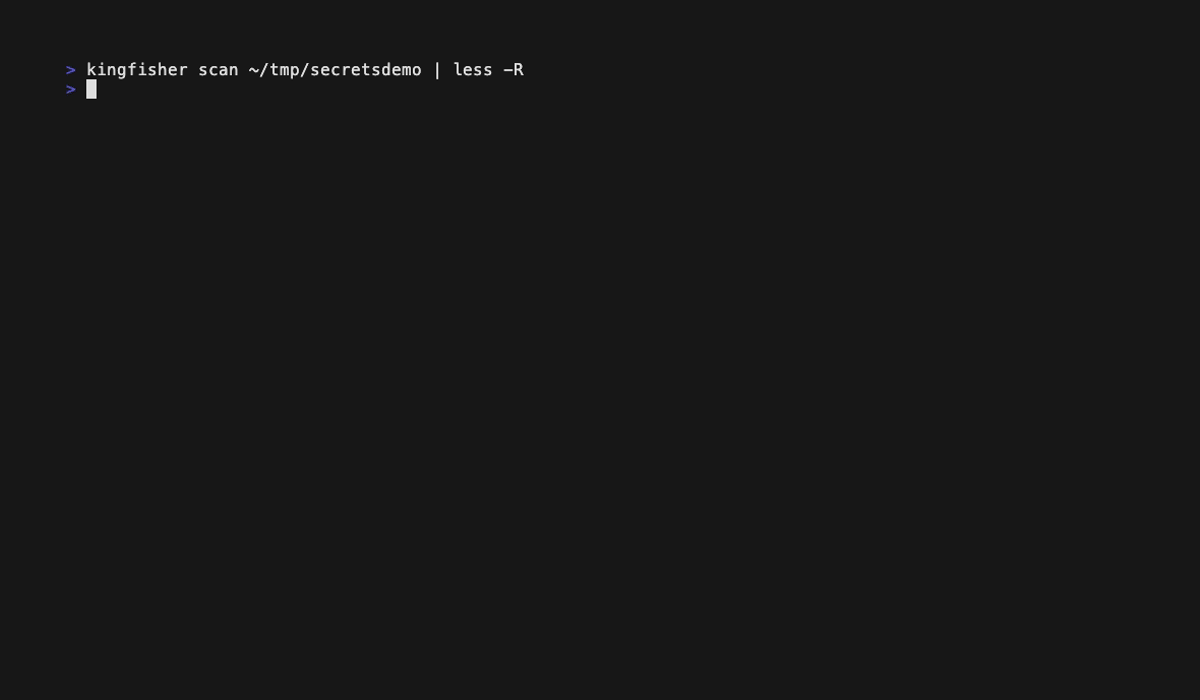
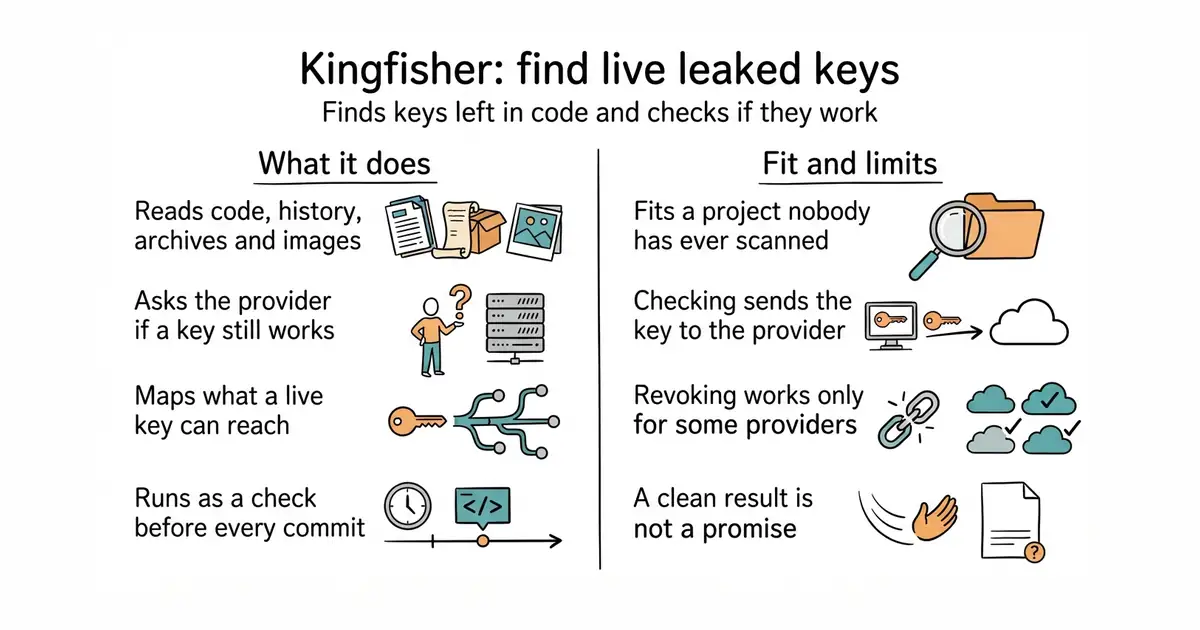
Kingfisher is a command-line secret scanner written in Rust. It reads source code, the full Git history, cloud storage, container images, archives and developer platforms, and matches what it finds against hundreds of built-in rules. For the providers it supports it then calls the provider to ask whether each credential is still active, so a finding becomes a yes or a no rather than a maybe. For 43 providers it also maps what a live credential can reach, using read-only calls, so the size of a leak is visible. It offers a browser viewer for sorting through findings, and for some providers it can revoke a key outright. It understands staged files, so it can run as a check before every commit. Every feature is in the free release and there is no paid tier. It is not a running service: it starts, finishes and exits, with no database and no port of its own.
Why it matters
Who it suits. It fits any project where one person has been the only one touching the code for a long time, because that is exactly the case where nobody has ever checked. It also fits a team that wants a check before each commit rather than a quarterly audit. The output is what makes it useful: a plain scanner produces a worry, and this produces a short to-do list in priority order. Skip the validation part when scanning somebody else's code without written permission, and skip the whole thing if the work has never held a credential in the first place.
Verdict. Worth ten minutes tonight, ahead of anything else in this edition. Nothing is installed if you use the container, nothing is left running, and the result is immediately actionable. The one thing to think about before running it: checking whether a key is live means sending that key to the provider, which is reasonable on code you own and may not be on a client's. --no-validate turns it off and the scan still works. Run it once over every repository you own, then add it as a commit check so a key never reaches the history again. gitleaks/gitleaks is the lighter alternative if live checking is not wanted at all.
Summary (Key Points)from the README
Key features
- Broad scan targets: Covers local files, Git history, GitHub, GitLab, Azure Repos, Bitbucket, Gitea, Hugging Face, Docker, Jira, Confluence, Slack, Teams, Postman, AWS S3, Google Cloud Storage, and Azure Blob Storage.
- Live validation: Checks which discovered credentials are actually active, separating live credentials from static candidates.
- Blast-radius mapping: The `--blast-radius` flag (alias `--access-map`) maps supported credentials to their effective identity, permissions, reachable roles or service accounts, and affected resource scopes, across all 43 providers.
- Opt-in revocation: Revokes supported credentials from the CLI, where Kingfisher has a bounded provider workflow. Revocation can contain a leaked token even when its owner is unknown.
- Archive and file coverage: Extracts and scans tar.gz, bz2, xz, ZIP-family containers (including docx, xlsx, jar, and epub), asar, HWP, and EGG files, plus SQLite table rows and Python .pyc/.pyo string constants.
- Flexible output and triage: Produces human-readable, TOON, JSON, JSONL, SARIF, BSON, and HTML reports. The `kingfisher view` command opens a local browser viewer that also merges Gitleaks and TruffleHog reports.
- Custom rules and baselines: Accepts Betterleaks TOML and Kingfisher YAML rules via `--rules-path`, supports offline checksum verification for custom rules, and can baseline known findings to suppress them.
- Embedding: Offers a Python SDK (`kingfisher-secret-scanner`, imported as `kingfisher_sdk`) and Rust crates for in-process scanning, validation, and revocation.
Ways to install
| Platform or method | What it needs | Effort |
|---|---|---|
| Pre-built binaries | Not stated in README | Not stated in README |
| Docker | Docker; the viewer runs at localhost:7890 | Not stated in README |
| mise | Not stated in README | Not stated in README |
| Windows | Not stated in README | Not stated in README |
| Pre-commit hook | Pre-commit | Not stated in README |
| Source build | A repository checkout | Not stated in README |
| Python module | uv (`uv add kingfisher-secret-scanner`) | Not stated in README |
| Rust library | Crate `kingfisher-scanner` | Not stated in README |
Important
- Live requests to providers: Validation and blast-radius mapping make authorized requests to provider APIs, so use them only on accounts you are authorized to inspect.
- Revocation is opt-in: Responders should confirm the target and the operational impact before revoking, and revocation only works for providers with a bounded workflow.
- Blast-radius scope: Mapping covers supported credentials only, and some providers have bounded analysis, such as Bedrock discovery and a Google API-key probe allowlist.
- Rule sources: Detection rules come mainly from the Betterleaks catalog, with selected Veles detectors filling gaps.
- Authentication setup: Cloud and SaaS scans need credentials. Jira and Confluence Cloud tokens also require the account email, and Azure Blob requires exactly one of the SAS, account-key, or Entra-token variables unless the container is public.
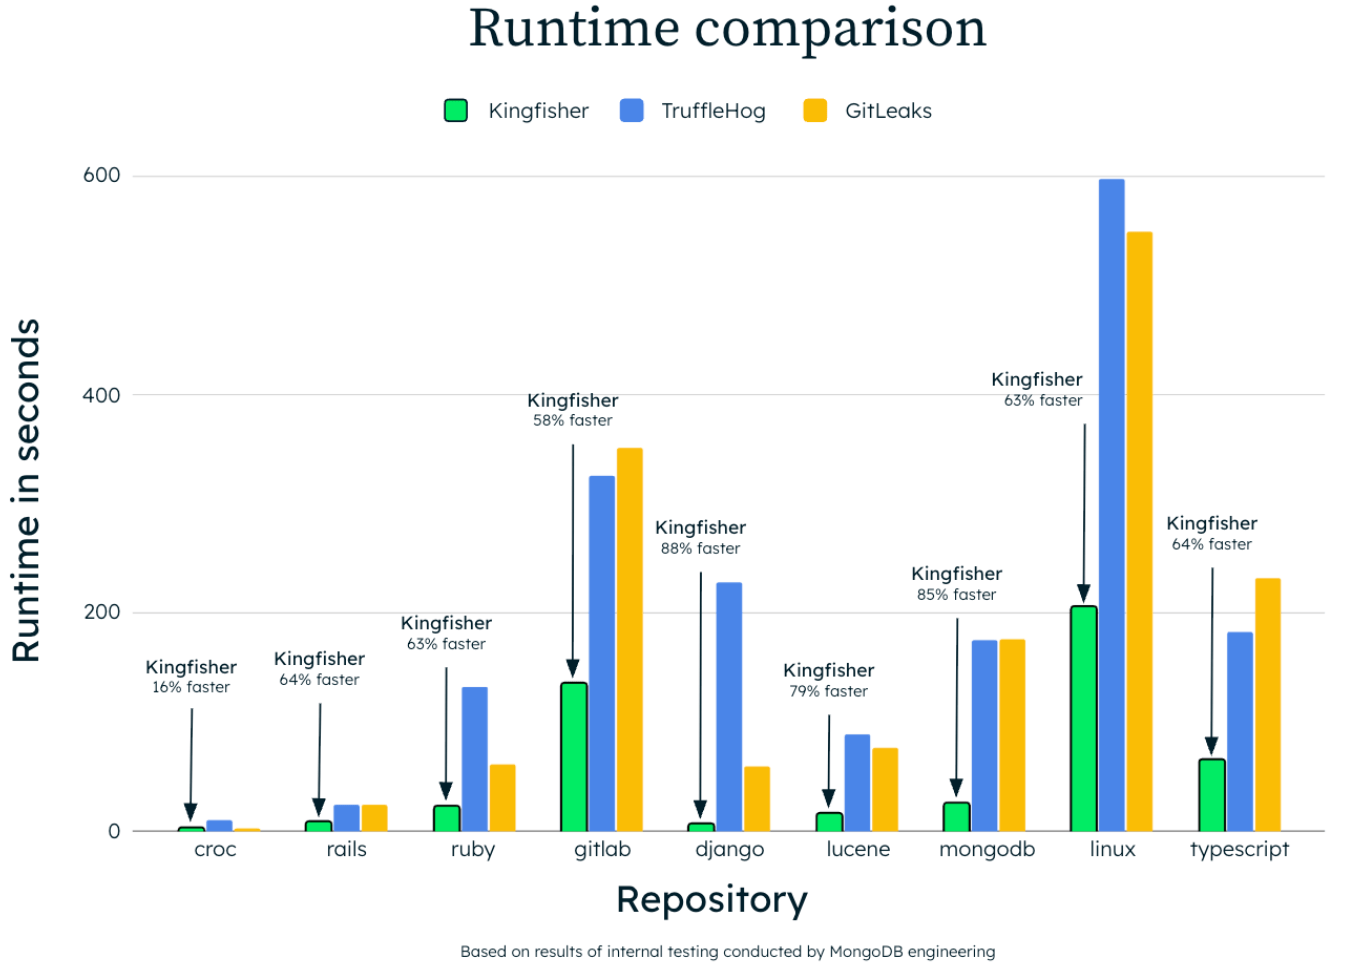
- Performance claim: The speed claim comes from the project's own published benchmark suite.
Written by an AI model from the project’s README; not part of the review, and it can be wrong.
- Nothing is left alive. It is one program, you run it, it finishes and exits. No database, no server, no port.
- The licence is the plain Apache 2.0, not MongoDB's usual SSPL. Commercial use is allowed with no added conditions.
- It knows about staged files, so it can run before every commit and stop a key ever reaching the history.
- Checking whether a key is live means sending that key to the provider. On code you own that is reasonable. On somebody else's it may not be.
- Revoking only works where the provider has a bounded workflow for it, so most credential types still have to be changed by hand.
- A clean result is not a promise. It finds the shapes it has rules for, and a home-made token format may match none of them.
docker run --rm -v "$PWD":/src ghcr.io/mongodb/kingfisher:latest scan /src