In simple English
Your code uses third-party packages that can contain hidden security flaws. This tool scans your project folders and lists known security holes in your dependencies. It points you to official warnings so you can fix them before hackers find them. The software is free to run and works on your own computer or build server. You need to spend time keeping it updated and getting free API keys to make it run fast.
What it is
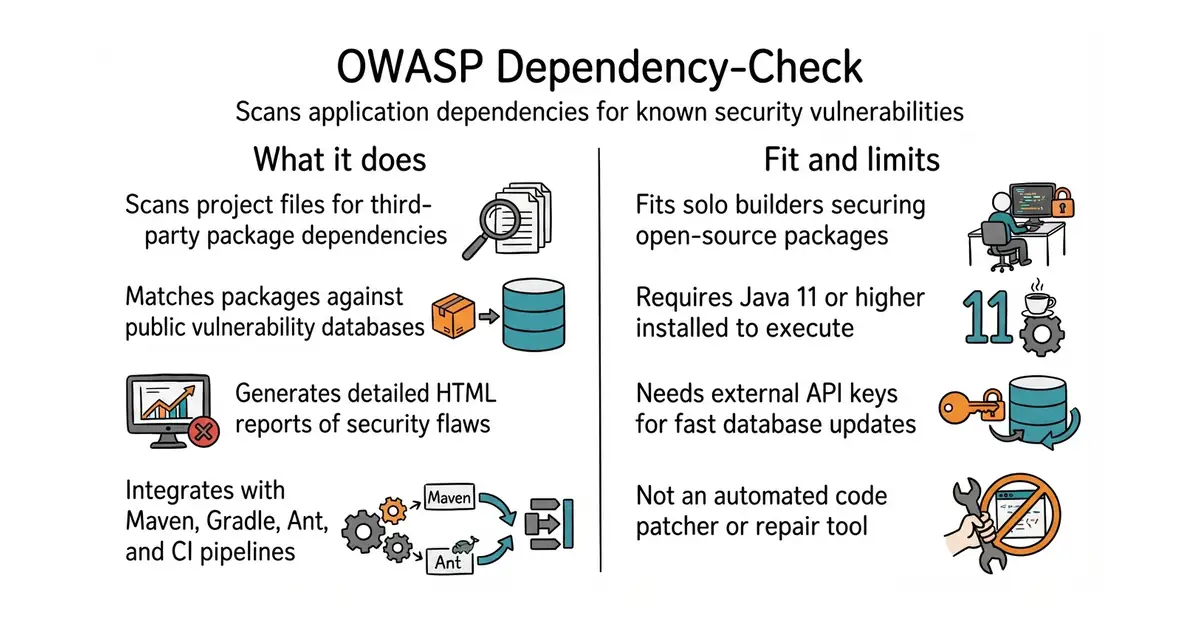
OWASP Dependency-Check (a security scanner that inspects third-party software libraries to find known flaws) checks your project files against public vulnerability databases. It produces an HTML report that lists every vulnerable package and links to official advisory entries.
What it is good for
Solo builders who want to check their web applications or backend services for vulnerable open-source packages before deploying them to production.
- Integrates directly into popular build tools like Maven, Gradle, Ant, and Jenkins.
- Provides a standalone command-line interface and official Docker containers for easy running.
- Generates clear HTML reports detailing every found vulnerability and matching advisory.
- Requires Java 11 or higher installed on your system to run properly.
- Updates will be extremely slow without a free API key from the National Vulnerability Database.
- Large initial database downloads and local file caches require sufficient disk space.
Manual checks of third-party package versions against security advisories
Jenkins
- anchore/grype13k stars
A vulnerability scanner for container images and filesystems that offers fast matching against multiple databases.
- aquasecurity/trivy39k stars
A comprehensive security scanner that detects vulnerabilities in container images, file systems, and git repositories.


- smallstep/certificates9.0k stars
A certificate authority you run yourself, for machines the public internet cannot reach.
- michelp/pgsodium614 stars
A PostgreSQL extension that brings libsodium's encryption functions into SQL, with a root key the database cannot read back.
- pgaudit/pgaudit1.7k stars
A PostgreSQL extension that records what was done to the database, in the database's own log.
VERSION=$(curl -s https://dependency-check.github.io/DependencyCheck/current.txt)
curl -Ls "https://github.com/dependency-check/DependencyCheck/releases/download/v$VERSION/dependency-check-$VERSION-release.zip" --output dependency-check.zip