In simple English
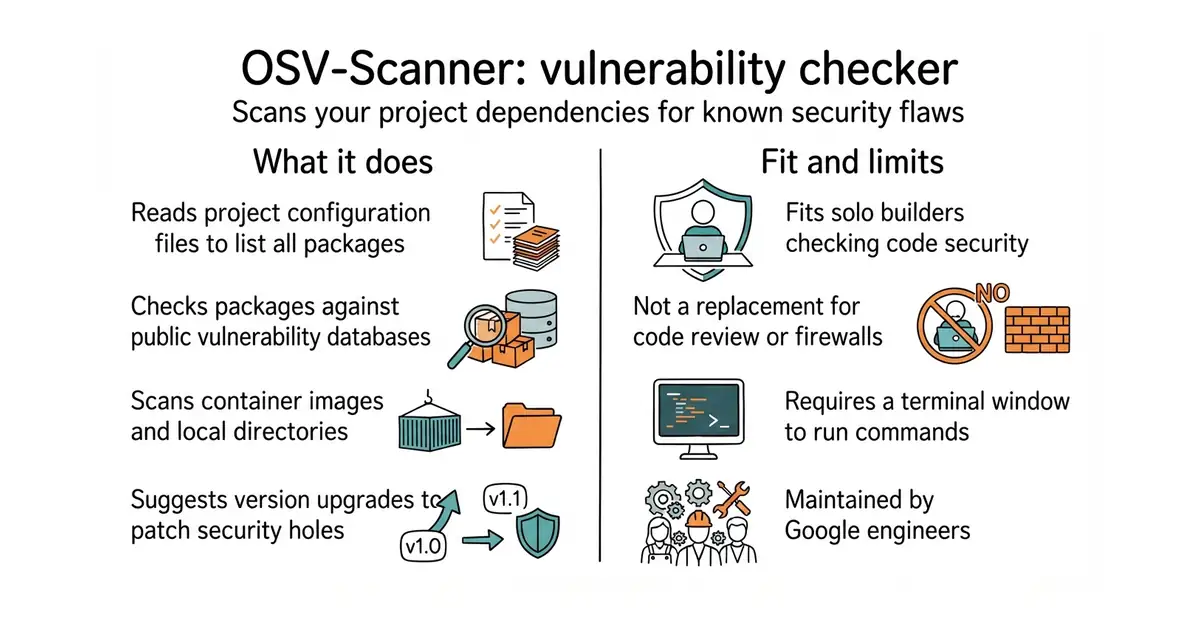
When you write software, you borrow pre-made pieces of code from other people. Sometimes these pieces have security flaws that hackers can exploit. This tool checks every piece of code you use against a giant public list of known dangers. It tells you if your project is at risk and how to fix it. It runs on your own computer and costs nothing to use.
What it is
OSV-Scanner is a command-line tool (a program that runs in your terminal window and takes text commands) created by Google. It reads your project files and queries vulnerability databases to find outdated or dangerous code.
What it is good for
Solo builders who want to check their code for security holes before releasing it to the public, without paying for commercial security scanners.
- Scans code across many languages including Python, JavaScript, Go, and Rust.
- Can run completely offline if you download the database files first.
- Suggests specific version upgrades to fix vulnerable packages.
- Requires comfort using the command line and terminal windows.
- Needs an active internet connection to fetch the latest vulnerability data by default.
- Experimental fix features can occasionally alter project files in unexpected ways.
manual security audits
GitHub Actions
- anchore/grype13k stars
Another popular command-line scanner that finds security flaws in container images and project dependencies.
- aquasecurity/trivy39k stars
A comprehensive security scanner for containers, file systems, and code repositories with similar breadth.


- smallstep/certificates9.0k stars
A certificate authority you run yourself, for machines the public internet cannot reach.
- michelp/pgsodium614 stars
A PostgreSQL extension that brings libsodium's encryption functions into SQL, with a root key the database cannot read back.
- pgaudit/pgaudit1.7k stars
A PostgreSQL extension that records what was done to the database, in the database's own log.
go install github.com/google/osv-scanner/v2/cmd/osv-scanner@latest