Overview
Summary
The useful answer before the supporting detail.
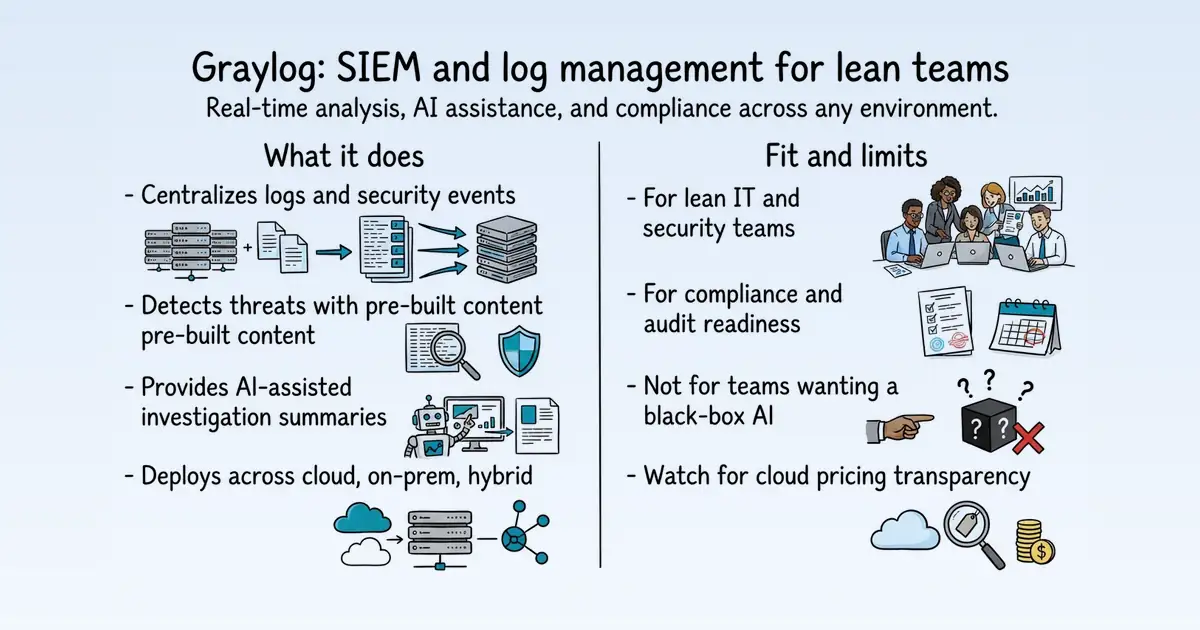
Graylog is a SIEM and log management platform designed for lean IT and security teams, offering real-time analysis, alerting, and compliance capabilities S67. It solves the problem of noisy alerts and complex, costly SIEM tools by providing pre-built content, AI assistance, and predictable pricing S67 S10. The platform delivers practical value through centralized log visibility, faster investigations, and flexible deployment across cloud, on-premises, and hybrid environments S1 S67.
Product identity and positioning
Name, category, positioning, audience, and first-party claims.
- Identity: Graylog is a SIEM and enterprise log management platform S67.
- Core purpose: It helps lean teams manage logs, detect threats, and meet compliance without excessive cost or complexity S67 S10.
- Intended users: IT operations, DevOps, security teams, and compliance auditors S10.
- Product scope: A platform offering log management, SIEM, and security analytics across cloud and self-managed deployments S1 S67.
- Positioning: Graylog positions itself as a cost-effective, scalable alternative to traditional SIEMs S1 S67.
- Claimed distinction: It claims full feature parity across environments and AI-assisted capabilities S10 S67.
Use cases and audiences
Who the product serves and the jobs it is designed to handle.
| Audience | Practical use case |
|---|---|
| IT operations teams | Monitor system health and analyze logs in real time to act faster S1. |
| Security analysts | Detect threats and investigate incidents with context-rich detection S1. |
| Compliance and audit teams | Retrieve exact records for auditors without full restores S10. |
| DevOps/SRE teams | Manage Kubernetes clusters and containerized environments S1. |
| Lean security teams | Reduce alert fatigue and prioritize threats with risk scoring S67. |
Traffic and search
SEO analysis
Collected Oct 22, 2026graylog.org: an estimated 120,400 total monthly visits and about 10,673 monthly organic visits across 3,162 ranking keywords. Scout crawled 15 pages and measured a technical health score of 96/100.
Search summary
The useful answer before the supporting detail.
Optimize operations with cutting-edge SIEM and detailed log management solutions. graylog.org: an estimated 120,400 total monthly visits and about 10,673 monthly organic visits across 3,162 ranking keywords. Scout crawled 15 pages and measured a technical health score of 96/100.
- Total traffic (modeled): 120,400 monthly visits across all channels.
- Organic search traffic (estimated): 10,673 monthly visits from search.
- Strongest sampled ranking: graylog at position 1.
- Leading page in the collected evidence: https://graylog.org/.
- Closest measured organic competitor: capterra.com.sg, appearing 1 times in the sampled first-page SERPs.
- Technical crawl: 15 pages, health score 96/100.
Website intelligence — Collected evidence
Company identity and positioning
| Page type | Evidence | Source |
|---|---|---|
| other | Optimize operations with cutting-edge SIEM and detailed log management solutions. | https://graylog.org/ |
| other | SIEM and Log Management for the AI Era. | https://graylog.org/ |
| other | Built for lean teams with enterprise challenges. | https://graylog.org/ |
| other | Most platforms are built for a team and a budget you don’t have. Results or resources — something gets compromised. Graylog is built for the people covering security, IT, and audit: one platform, at a cost of ownership that makes sense. And AI that explains itself instead of asking to be trusted. | https://graylog.org/ |
| other | [Why Traditional SIEMs Fail Lean Teams Highlight | https://graylog.org/ |
| other | Security Teams | https://graylog.org/ |
| other | Why lean security teams need clarity, not more coverage, to stop alert fatigue and reduce risk](https://graylog.org/resources/why-traditional-siems-fail-lean-security-teams/) | https://graylog.org/ |
| other | Learn More→ | https://graylog.org/ |
| other | Industry Trend Report: Rethinking Identity for Lean Security Teams | https://graylog.org/ |
| other | How lean security teams are moving beyond noisy alerts to detect identity misuse earlier.](https://graylog.org/resources/too-much-access-too-little-insight/) | https://graylog.org/ |
| other | The SIEM and Log Management Platform for the AI Era | https://graylog.org/ |
| other | Graylog 7.2: AI-Ready Triage, Smarter Platform Management, and the New Graylog Collector](https://graylog.org/post/graylog-7-2-ai-ready-triage-smarter-platform-management-and-the-new-graylog-collector) | https://graylog.org/ |
Domain performance
Modeled total traffic, six-month trend, engagement, countries, and domain identity.
Total website traffic
| Month | Modeled visits |
|---|---|
| 2026-04 | 174,566 |
| 2026-05 | 158,297 |
| 2026-06 | 160,142 |
| 2026-07 | 159,727 |
| 2026-08 | 123,190 |
| 2026-09 | 120,400 |
Top visitor countries
| Country | Name | Traffic share |
|---|---|---|
| US | United States | 15.1% |
| DE | Germany | 8.7% |
| RU | Russia | 7.5% |
| TW | Taiwan | 4.9% |
| ID | Indonesia | 4.4% |
Domain identity
| Signal | Value |
|---|---|
| Registered | Aug 10, 2009 |
| Last changed | Aug 12, 2026 |
| Expires | Aug 10, 2027 |
| WHOIS server | — |
| DNSSEC | Signed |
| Nameservers | sreeni.ns.cloudflare.com, yichun.ns.cloudflare.com |
Website capture
Organic keywords
Top keywords and an independent Google result page.
Top organic keywords
| Keyword | Volume | CPC | Estimated value |
|---|---|---|---|
| graylog | 11,490 | $2.03 | $7,620 |
| настройка graylog nxlog sidecar windows | 1,210 | $0.00 | $690 |
| gray log | 730 | $4.81 | $660 |
| graylog 7.1.9 | 300 | $0.00 | $560 |
| graylog server url | 230 | $0.00 | $430 |
Independent Google result page
Query: graylog
| Position | Title | URL | Description |
|---|---|---|---|
| 1 | Graylog | SIEM & Enterprise Log Management | https://graylog.org/ | Centralized log management without compromise — faster insights, lower costs, and full visibility across your environment. Graylog Open. Collect, store, search, ... |
| 2 | Graylog2/graylog2-server: Free and open log management | https://github.com/graylog2/graylog2-server | Graylog is a free and open log management platform. You can read more about the project on our website and check out the documentation on the documentation site ... |
| 3 | Graylog Reviews & Ratings 2026 | Gartner Peer Insights | https://www.gartner.com/reviews/product/graylog-868566820 | Graylog is a log management and analysis platform that delivers impressive functionality without the cost and complexity often associated with enterprise-grade ... |
| 4 | Graylog, Inc. | https://www.linkedin.com/company/graylog | Graylog: Empowering Threat Detection & Incident Response Solutions with Cutting-Edge Technology At Graylog, we specialize in delivering top-notch Threat ... |
| 5 | Opinions On Graylog? : r/sysadmin | https://www.reddit.com/r/sysadmin/comments/qn88wd/opinions_on_graylog/ | So, I’m planning on implementing Graylog on a syslog server in AWS for production use. I was curious if anyone has had good or bad experiences with ... |
| 6 | What is Graylog? | https://medium.com/@gouthamr102/graylog-5265748cace0 | Graylog is defined in terms of log management platform for collecting, indexing, and analyzing both structured and unstructured data from ... |
| 7 | AWS Marketplace - Graylog, Inc. - Amazon.com | https://aws.amazon.com/marketplace/pp/prodview-ddqy3pxlmrmz2 | Graylog delivers AI-powered SecOps and centralized log management without compromise, giving lean security and IT operations teams faster insights, ... |
Important pages
Pages earning the most estimated search traffic in the sample.
Website intelligence — Collected evidence
Prioritized website intelligence pages
| Type | Page | Words | Change | URL |
|---|---|---|---|---|
| other | Graylog \ | static | 1,425 | new |
| pricing | Graylog Pricing Plans & Features Comparison | 1,956 | new | https://graylog.org/pricing/ |
| features | Graylog UEBA Anomaly Detection \ | playwright | 1,496 | new |
Features
| Page type | Evidence | Source |
|---|---|---|
| features | We value your privacy | https://graylog.org/feature/anomaly-detection/ |
| features | This website or its third-party tools process personal data. You can opt out of the sale of your personal information by clicking on the “Do Not Sell or Share My Personal Information” link. | https://graylog.org/feature/anomaly-detection/ |
| features | Do Not Sell or Share My Personal Information | https://graylog.org/feature/anomaly-detection/ |
| features | Opt-out Preferences | https://graylog.org/feature/anomaly-detection/ |
| features | We use third-party cookies that help us analyse how you use this website, store your preferences, and provide the content and advertisements that are relevant to you. However, you can opt out of these cookies by checking "Do Not Sell or Share My Personal Information" and clicking the "Save My Preferences" button. Once you opt out, you can opt in again at any time by unchecking "Do Not Sell or Share My Personal Information" and clicking the "Save My Preferences" button. | https://graylog.org/feature/anomaly-detection/ |
| features | Cancel Save My Preferences | https://graylog.org/feature/anomaly-detection/ |
| features | Your opt-out preference has been honored. | https://graylog.org/feature/anomaly-detection/ |
| features | Banner closes automatically in s... | https://graylog.org/feature/anomaly-detection/ |
| features | Powered by 0 | https://graylog.org/feature/anomaly-detection/ |
| features | [Skip to content](#content) | https://graylog.org/feature/anomaly-detection/ |
| features | [Webinar: What's New in Graylog 7.2 \ | playwright |
| features | [](#ekit_modal-popup-05cbf26) | https://graylog.org/feature/anomaly-detection/ |
| features | 0 | https://graylog.org/feature/anomaly-detection/ |
| features | Contact Us | https://graylog.org/feature/anomaly-detection/ |
| features | UEBA Anomaly Detection | https://graylog.org/feature/anomaly-detection/ |
| features | User and Entity Behavior Analytics (UEBA) Anomaly Detection uses machine learning to detect unusual behavior in real time. It continuously learns what "normal" activity looks like, helping security teams spot insider threats, credential misuse, and data leaks before they happen. Unlike rule-based systems, Graylog adapts to new risks, catching threats that traditional detection methods miss. | https://graylog.org/feature/anomaly-detection/ |
| features | Graylog UEBA Anomaly Detection Highlights: | https://graylog.org/feature/anomaly-detection/ |
| features | Detect Insider Threats in Real-Time | https://graylog.org/feature/anomaly-detection/ |
| features | AI-driven analytics identify credential misuse and data exfiltration before damage occurs. | https://graylog.org/feature/anomaly-detection/ |
| features | Reduce False Positives | https://graylog.org/feature/anomaly-detection/ |
Pricing and plans
| Page type | Evidence | Source |
|---|---|---|
| pricing | Graylog Pricing | https://graylog.org/pricing/ |
| pricing | From 10 GB/day on daily volume or 100 GCUs on annual consumption | https://graylog.org/pricing/ |
| pricing | Contact Sales | https://graylog.org/pricing/ |
| pricing | Multi-year subscriptions lock your rate for the full term, so there’s no annual renegotiation and no mid-term increase. Three and five years are both common. One year is available if you’d rather stay flexible, and a term can be structured as a ramped volume when you’re rolling out in stages. | https://graylog.org/pricing/ |
| pricing | Graylog Pricing Frequently Asked Questions | https://graylog.org/pricing/ |
| pricing | Graylog licenses processed data volume in the active data tier. Two models are available: daily volume (capacity), measured in gigabytes per day, and annual consumption, measured in Graylog Consumption Units (GCUs). Entry points are 10 GB per day and 100 GCUs. Device count, user count, and total stored data do not affect licensing. | https://graylog.org/pricing/ |
| pricing | What's the difference between daily volume and annual consumption? | https://graylog.org/pricing/ |
| pricing | Daily volume (capacity) licenses a per-day processing rate, starting at 10 GB per day. Annual consumption licenses an estimated yearly total, starting at 100 GCUs, drawn down as data is processed. Daily volume is best for those with predicatable and consistent log volume. Consumption is best for those with unpredictable log volume and environments that experience heavy variation due to seasonality or other factors. | https://graylog.org/pricing/ |
| pricing | A GCU is a Graylog Consumption Unit. Consumption-based subscriptions have a fixed annual platform subscription fee and a variable amount of Graylog Consumption Units. A single GCU can be redeemed for 20 GB of Graylog Security or 25 GB of Graylog Enterprise. GCU’s are typically purchased in bundles and volume discounts apply. The closest analogy is a pre-paid gift card. | https://graylog.org/pricing/ |
| pricing | Graylog licenses are annual subscription. Published starting prices are annual figures, not monthly. | https://graylog.org/pricing/ |
| pricing | Volume discounts are built into the pricing structure. The per-unit rate decreases at each licensing tier. | https://graylog.org/pricing/ |
| pricing | One to five year subscription terms are available. Multi-year terms lock in prices, eliminating the need to negotiate annually and preventing price increases during the term. Term length does not change licensed volume, unless the contract is structured as a ramped volume. | https://graylog.org/pricing/ |
| pricing | Can I move between daily volume and annual consumption? | https://graylog.org/pricing/ |
| pricing | Data routed to the data lake does not count toward the license while it remains there. To use it, you include the data lake in a search, review the results, and select what data to retrieve. Retrieved data counts toward daily volume or annual consumption at that point. | https://graylog.org/pricing/ |
| pricing | For self-managed customers, archive data was processed and counted at ingest, so retrieval carries no additional license cost. This differs from the data lake, where data is routed in before processing and counts when retrieved. For Cloud customers, it depends on the retention terms in your contract. The default is 90 days of live data and 1 year of retention for Graylog Cloud. | https://graylog.org/pricing/ |
| pricing | Is Graylog Open free, and are there volume limits? | https://graylog.org/pricing/ |
| pricing | Graylog Open is free permanently. It is not a trial. There is no daily ingest cap and no volume limit of any kind. It is source-available under the Server Side Public License (SSPL) and has a narrower feature set than the paid licenses. | https://graylog.org/pricing/ |
| pricing | Graylog Accelerator, the guided onboarding service, is included with every paid license. On-demand training is free and available to anyone. Live training, custom training, Professional Services, and Technical Account Management are paid add-ons available to licensed customers. | https://graylog.org/pricing/ |
| pricing | Questions about pricing? | https://graylog.org/pricing/ |
Integrations and supported platforms
No supporting public-page evidence was collected for this category.
Product and company updates
No supporting public-page evidence was collected for this category.
Rank tracking
Persistent keyword baselines and position movement.
This analysis created the first position baseline at 2026-10-22T12:36:09.184Z. Movement appears after the next fresh analysis using the same location and language.
Features
Features and capabilities
Core functions and evidence-backed product capabilities.
| Capability | What it does |
|---|---|
| Real-time log analysis | Parse, enrich, and analyze logs across the entire environment in real time S10. |
| AI dashboard summaries | Converts complex visualizations into plain-language insights for faster decision-making S1. |
| Data lake integration | Stores years of logs on AWS or Azure Blob without counting against license S10. |
| Pre-built compliance content | Activates framework-specific dashboards, parsing rules, and alerts from day one S10. |
| Threat prioritization | Groups alerts into incidents weighted by asset value and risk amplifiers S67. |
| MCP server integration | Connects Graylog with preferred LLMs for AI-assisted analysis and automation S10. |
| Forwarder health monitoring | Surfaces input issues before they become data gaps S10. |
Integrations and ecosystem
Connected products, exports, APIs, and workflow compatibility.
| Integration or interface | Type | What it enables |
|---|---|---|
| AWS Security Hub | Integration | Forward log alerts and detection signals for centralized incident response S1. |
| AWS Security Lake | Integration | Filter, preview, and retrieve data directly, reducing noise and storage costs S10. |
| Qualys and Tenable | Integration | Ingest vulnerability scan data for unified threat and vulnerability visibility S1. |
| REST API | API | Provides flexible API access for centralized log visibility S1. |
| MCP server | AI interface | Connects Graylog with preferred LLMs for AI-assisted analysis S10. |
| AWS PrivateLink | Integration | Secure private connectivity keeping data off the public internet S1. |
Pricing
Pricing and plans
Published plans, free access, trials, credits, and pricing limitations.
| Plan or offer | Verified price and billing | Included | Limits |
|---|---|---|---|
| Open | Free S144 | Source-available, self-managed S67 | No volume limit S144 |
| Enterprise | $15,000 per year S144 | Data tiering, archive, SSO and LDAP, AI dashboard summaries S144 | From 10 GB/day or 100 GCUs/year S144 |
| Security | $18,000 per year S144 | Adds SIEM detection, anomaly detection, investigations S144 | From 10 GB/day or 100 GCUs/year S144 |
| Graylog Cloud | Contact sales S144 | Default 90 days live data, 1 year retention S144 | Not published S144 |
Competition
Competitive landscape
Domains competing for the same organic search demand.
Sampled competitors
| Competitor | First-page appearances | Sampled queries | Average position | Queries observed |
|---|---|---|---|---|
| capterra.com.sg | 1 | 1 | 1 | graylog |
| reddit.com | 1 | 1 | 4 | graylog |
| go2docs.graylog.org | 1 | 1 | 5 | graylog |
| github.com | 1 | 1 | 5 | graylog open |
| youtube.com | 1 | 1 | 6 | graylog |
| hub.docker.com | 1 | 1 | 6 | graylog open |
| gartner.com | 1 | 1 | 7 | graylog |
| medium.com | 1 | 1 | 9 | graylog open |
Website intelligence — Collected evidence
Customers, testimonials, and first-party review claims
No supporting public-page evidence was collected for this category.
Independent review sources discovered
No links to supported independent review platforms were discovered on the collected pages.
Backlink profile
Authority and referring-domain signals.
Backlink comparison profile
- Domain rating: 77/100
- Backlinks: 65,571
- Referring domains: 6,161
- Dofollow backlinks: 59.0%
- Dofollow referring domains: 66.0%
Collection decision
The Scout search index remains intentionally excluded from automatic Scout analysis. This Scout traffic model profile costs 5 credits (0.5 cents) and is included in the first comparison run so its usefulness can be judged before the recurring collection is finalized.
AI visibility
Measured ChatGPT and Google AI mentions with cited sources.
AI-assistant referral traffic
- Estimated current generative-AI referral share: 2.5%
| Month | Traffic share | Source |
|---|---|---|
| — | — | All AI assistants |
Website intelligence — Collected evidence
Site-stated AI capabilities
| Page type | Evidence | Source |
|---|---|---|
| other | SIEM and Log Management for the AI Era. | https://graylog.org/ |
| other | Most platforms are built for a team and a budget you don’t have. Results or resources — something gets compromised. Graylog is built for the people covering security, IT, and audit: one platform, at a cost of ownership that makes sense. And AI that explains itself instead of asking to be trusted. | https://graylog.org/ |
| other | The SIEM and Log Management Platform for the AI Era | https://graylog.org/ |
| other | Graylog 7.2: AI-Ready Triage, Smarter Platform Management, and the New Graylog Collector](https://graylog.org/post/graylog-7-2-ai-ready-triage-smarter-platform-management-and-the-new-graylog-collector) | https://graylog.org/ |
| other | Learn More → | https://graylog.org/ |
| features | User and Entity Behavior Analytics (UEBA) Anomaly Detection uses machine learning to detect unusual behavior in real time. It continuously learns what "normal" activity looks like, helping security teams spot insider threats, credential misuse, and data leaks before they happen. Unlike rule-based systems, Graylog adapts to new risks, catching threats that traditional detection methods miss. | https://graylog.org/feature/anomaly-detection/ |
| features | UEBA (User and Entity Behavior Analytics) Anomaly Detection is a security solution that uses machine learning to identify unusual behaviors in real-time. It helps detect insider threats, credential misuse, and data leaks by continuously learning what normal activity looks like. | https://graylog.org/feature/anomaly-detection/ |
| features | UEBA uses machine learning to refine detection models, reducing false positives by continuously learning from data. This minimizes alert fatigue for security teams and ensures only real threats trigger alerts. | https://graylog.org/feature/anomaly-detection/ |
| features | User and Entity Behavior Analytics (UEBA) Anomaly Detection uses machine learning to detect unusual behavior in real time. It continuously learns what "normal" activity looks like, helping security teams spot insider threats, credential misuse, and data leaks before they happen. Unlike rule-based systems, Graylog adapts to new risks, catching threats that traditional detection methods miss. | https://graylog.org/feature/anomaly-detection/ |
| features | AI-driven analytics identify credential misuse and data exfiltration before damage occurs. | https://graylog.org/feature/anomaly-detection/ |
| features | Machine Learning eliminates alert fatigue by dynamically refining detection models. | https://graylog.org/feature/anomaly-detection/ |
These are first-party product claims, not independent measurements of AI-search visibility.
Marketing opportunities
Actions calculated directly from the collected evidence.
| Opportunity | Recommended action | Evidence |
|---|---|---|
| Competitor gap | Review the sampled queries where capterra.com.sg appears. | 1 first-page appearances across graylog |
Website intelligence — Collected evidence
Website evidence gaps
- integrations: no usable public page was collected; verify whether the site publishes this evidence.
- customers: no usable public page was collected; verify whether the site publishes this evidence.
- reviews: no usable public page was collected; verify whether the site publishes this evidence.
- changes: no usable public page was collected; verify whether the site publishes this evidence.
- identity: no usable public page was collected; verify whether the site publishes this evidence.
- technical: no usable public page was collected; verify whether the site publishes this evidence.
Trust and proof
Customers, proof, and reviews
Published proof, customer signals, and review evidence.
Independent reviews
| Platform | Page | How it was found | Note |
|---|---|---|---|
| G2 | Graylog Reviews & Product Details | Grounded web search | 3/21/2024 3.5 out of ... I like that Graylog reads logs, and the filtering options they offer. It is easy to deploy to the client's environment. Customer support in Graylog ... ### 116 Graylog Reviews 4.4 out of 5 |
| GetApp | Graylog 2026 Pricing, Features, Reviews & Alternatives / GetApp | Grounded web search | ## Graylog reviews Overall rating 4.6 /5 32 Positive reviews 84 Rating breakdown - Value for money - Ease of use - Features - Customer support - Likelihood to recommend 8.44/10 Rating distribution 5 4 3 2 1 22 7 3 |
| The HFT Guy | 250 GB/day of logs with Graylog: Lessons Learned | Grounded web search | 1. debugging & postmortem 2. security and activity analysis 3. regulations ... 1) ElasticSearch cannot do join nor processing (ala mapreduce) 2) Log fields have weak typing 3) Many applications send erroneous or poorly formatted data (e.g. nginx) |
| graylog.org | Graylog / SIEM & Enterprise Log Management | Grounded web search | gets compromised. Graylog is built for the people covering security, IT, and audit: one platform, at a cost of ownership that makes sense. And AI that explains itself instead of asking to be trusted. ... ## REVIEWER RATING 4.6 out of 5 across 52 reviews |
Customer proof
| Proof type | Named customer or source | Evidence |
|---|---|---|
| Case study | Gameforge | customer case study — Graylog is helping Gameforge’s application developers and system administrators manage more than 20 games being delivered across more than 2,000 servers. (Graylog Helps Gameforge Transform DevOps Success Into Happy Gamers) |
| Case study | PROS | customer case study — activities, the PROS operations team needed a cost-effective log solution to allow operations to easily conduct fast and scalable searches to drill down into the log data. (CUSTOMERS WITH MEANINGFUL DATA (PROS Case Study)) |
Independent mentions
- Ask HN: What do you use for Log Management? — Using Graylog at my current job and it's working well so far. ... FWIW, Graylog is not SaaS but can/should/must be installed on-premise: https://www.graylog ... Graylog is working quite well for us so far. https://www.graylog.org/
- I'll allow it. Years later, I'm still miffed at Graylog... — (centralized logging engine) for having required MongoDB for a small bit of auth and meta storage that could’ve easily been done in MySQL or ... ), forcing the need for that much more ops work for a small Mongo cluster for HA. Everyone deprecating the
- Graylog vs Sentry / TrustRadius — is the best solution possible. It's easy to configure and "just works." Above everything else, it's ... The only thing I hold against it is the fact that it's Linux-based ... m pretty sure that we would have had a logging server years earlier if I had
- Centralising logs with rsyslog and parsing them with Graylog extractors / Hacker News — , a pattern fails silently if it doesn't match a log entry while parsing incoming entries. That's why Graylog requires you to load a log entry example when creating an extractor, and let you try it while defining the pattern (with the "Try" button next to
External links were grounded in one live web search. Search snippets are leads, not independently scraped page content; rejected links remain available in Review evidence.
Company, security, and trust
Ownership, policies, security signals, and public trust evidence.
| Signal | Finding | Source |
|---|---|---|
| Company and ownership | "Graylog helped us replace legacy SIEM headaches with a lightweight, centralized platform that’s easy to use and easy to scale. Our team feels empowered, not overwhelmed. " | source |
| Contact and support | Not published on the collected pages. | — |
| Legal and privacy | Cancel Save My Preferences | source |
| Security and compliance | SOC 2 Type 2–certified environment for compliance and assurance | source |
| Uptime and status page | AI-assisted compliance, detection, and response your team can operate, powered by the Verascend™ Incident System. | source |
| Domain registered | 2009-08-10 | — |
| Domain expires | 2027-08-10 | — |
Not found on the collected pages: contact and support. This only means Scout did not find it on the pages it read; it says nothing about the company itself.
Documentation and product updates
Help resources, product guidance, and visible changes over time.
| Resource or update | Type | What is available | Date or freshness |
|---|---|---|---|
| Graylog / SIEM & Enterprise Log Management | Changelog | Public product change history. (source) | Not dated |
| Graylog / SIEM & Enterprise Log Management | Product update | Product update is publicly available. (source) | Not dated |
Not found in the collected public sources: public roadmap, status page, separate help center or knowledge base.
Technical
Technical and delivery signals
Delivery model, platforms, API, data ownership, reliability claims and release activity.
| Signal | Finding | Source |
|---|---|---|
| Delivery model (cloud, self-hosted, desktop, browser extension) | Available as cloud, self-managed, on-premises, and hybrid S67. | S67 |
| Platforms and apps | Full feature parity across AWS, GCP, Azure, on-premises, and hybrid S10. | S10 |
| API and extensibility (API, SDK, webhooks, MCP, plugins) | Offers REST API access and MCP server integration S1 S10. | S1 S10 |
| Data ownership and export | Data lake stores logs on AWS or Azure Blob S10. | S10 |
| Performance and reliability claims | 99.9% uptime SLA for cloud S1. | S1 |
| Release activity | Graylog 7.2 and 7.1 releases announced S67. | S67 |
Measured infrastructure
Domain, certificate, and hosting signals, measured directly.
| Signal | Finding |
|---|---|
| Domain registered | 2009-08-10 — Cloudflare, Inc. |
| Domain expires | 2027-08-10 |
| TLS certificate | Let's Encrypt, valid, expires 2026-12-11 |
| Security headers | HSTS, CSP, X-Content-Type-Options, X-Frame-Options, Referrer-Policy |
| Server header | cloudflare |
| Mail handled by | smtp.google.com |
| Nameservers | sreeni.ns.cloudflare.com, yichun.ns.cloudflare.com |
Not measurable: wayback: rate limited by archive.org, ladder stopped after 1 probe(s); rdap: exceeded the overall budget; wayback: exceeded the overall budget; tls: exceeded the overall budget; dns: exceeded the overall budget; headers: exceeded the overall budget. A gap here means the lookup was unavailable, not that the finding is negative.
Technical site audit
A bounded multi-page crawl with page-level issues and URLs.
Scout — Bounded technical crawl
- Pages crawled: 15 of 15 maximum
- Technical health: 96/100
- Critical issues: 0
- Warnings: 10
- Notices: 2
Issues
Crawled pages
| Status | Title | H1s | Words | Response | URL |
|---|---|---|---|---|---|
| 200 | Graylog \ | SIEM & Enterprise Log Management | 0 | 1766 | 40 ms |
| 200 | Simplified SIEM & Robust Cybersecurity for Enterprises | 1 | 1998 | 45 ms | https://graylog.org/products/security/ |
| 200 | Advanced Log Management & Real-Time Analysis | 1 | 2020 | 35 ms | https://graylog.org/products/enterprise/ |
| 200 | Centralized Log Management \ | Advanced Features & Tools | 1 | 2135 | 56 ms |
| 200 | Graylog Cloud: Secure & Cost-Effective Log Management | 1 | 1300 | 45 ms | https://graylog.org/products/cloud/ |
| 200 | Paid vs. Open: Smarter, Scalable, Secure. | 3 | 1141 | 26 ms | https://graylog.org/open-vs-paid/ |
| 200 | Try Graylog | 0 | 658 | 38 ms | https://graylog.org/try-graylog/ |
| 200 | Arti \ | Graylog Concierge | 0 | 493 | 49 ms |
| 200 | Blog | 1 | 1156 | 27 ms | https://graylog.org/blog/ |
| 200 | May the Logs Be With You: Graylog 7.1 Is Here | 1 | 1390 | 3,022 ms | https://graylog.org/post/may-the-logs-be-with-you-graylog-7-1-is-here/ |
| 200 | Graylog 7.2: AI-Ready Triage, Smarter Platform Management, and the New Graylog Collector | 1 | 1417 | 23 ms | https://graylog.org/post/graylog-7-2-ai-ready-triage-smarter-platform-management-and-the-new-graylog-collector/ |
| 200 | How to Use Data Lakes to Reduce SIEM Costs and Strengthen Investigations | 1 | 1235 | 23 ms | https://graylog.org/post/how-to-use-data-lakes-to-reduce-siem-costs-and-strengthen-investigations/ |
| 200 | AI | 2 | 1973 | 38 ms | https://graylog.org/feature/ai/ |
| 200 | Graylog Access Control & Audit Logs – Secure & Compliant | 1 | 1721 | 25 ms | https://graylog.org/feature/access-control-audit-logs/ |
| 200 | Graylog UEBA Anomaly Detection \ | Real-Time Threat Prevention | 1 | 1715 | 35 ms |
This is a bounded Scout crawl. Core Web Vitals and Lighthouse scores are not claimed unless a dedicated performance audit is connected.
Search Console and Analytics
First-party search and behavioral data connection state.
Modeled acquisition channels
| Channel | Estimated share |
|---|---|
| direct | 32.4% |
| search | 53.0% |
| search organic | 53.0% |
| search paid | 0.0% |
| social | 1.3% |
| social organic | 0.9% |
| social paid | 0.4% |
| referrals | 9.5% |
| paid referrals | 0.5% |
| 0.8% | |
| gen ai | 2.5% |
| affiliate | 0.0% |
| other | 0.0% |
First-party connections
| Integration | Status | Data available after connection |
|---|---|---|
| Google Search Console | Not connected | Clicks, impressions, CTR, average position, queries, pages, countries, and devices |
| Google Analytics | Not connected | Organic sessions, engagement, landing pages, conversions, geography, and devices |
No first-party Search Console or Analytics numbers are shown until the site owner authorizes the corresponding Google account. Scout traffic model values above are modeled estimates, not private analytics totals.
Limits and method
Limitations and open questions
Known constraints and missing evidence from the collected pages.
The collected pages do not mention specific competitors by name. Evidence gaps include lack of detailed pricing for Graylog Cloud, no explicit customer counts, and limited independent review data beyond Gartner Peer Insights. Open questions remain about the full scope of AI capabilities and the specifics of the Verascend Incident System S67.
Sources, method, and limitations
Evidence inventory, collection method, provider use, and constraints.
This report is based on 6 collected pages from graylog.org, including product pages, pricing, and feature pages. The evidence catalog includes 180 entries from static and browser rendering rendering, with external proof search for Gartner reviews. Limitations: not all 15 pages were collected, and some external review content was not scraped in full.
- Official Websitehttps://graylog.org/Verified
- Official Websitehttps://graylog.org/products/cloud/Verified
- Official Websitehttps://graylog.org/products/enterprise/Verified
- Pricing Pagehttps://graylog.org/pricing/Verified
- Official Websitehttps://graylog.org/feature/Verified
- Official Websitehttps://graylog.org/feature/access-control-audit-logs/Verified
- Review Sitehttps://www.g2.com/products/graylog/reviewsVerified
- Review Sitehttps://www.getapp.com/security-software/a/graylog/Verified
- Articlehttps://devops.com/graylog-helps-gameforge-transform-devops-success-into-happy-gamersVerified
- Articlehttps://news.ycombinator.com/item?id=12682566Verified
- Articlehttps://news.ycombinator.com/item?id=19159016Verified
- Review Sitehttps://thehftguy.com/2016/09/12/250-gbday-of-logs-with-graylog-lessons-learned/Verified
- Articlehttps://graylog.org/wp-content/uploads/2022/08/611fe780e0bf2608964ccb40_Graylog_PROS_Case_Study_B_high.pdfVerified
- Articlehttps://www.trustradius.com/compare-products/graylog-vs-sentryVerified
- Articlehttps://news.ycombinator.com/item?id=17006824Verified