Overview
Summary
The useful answer before the supporting detail.
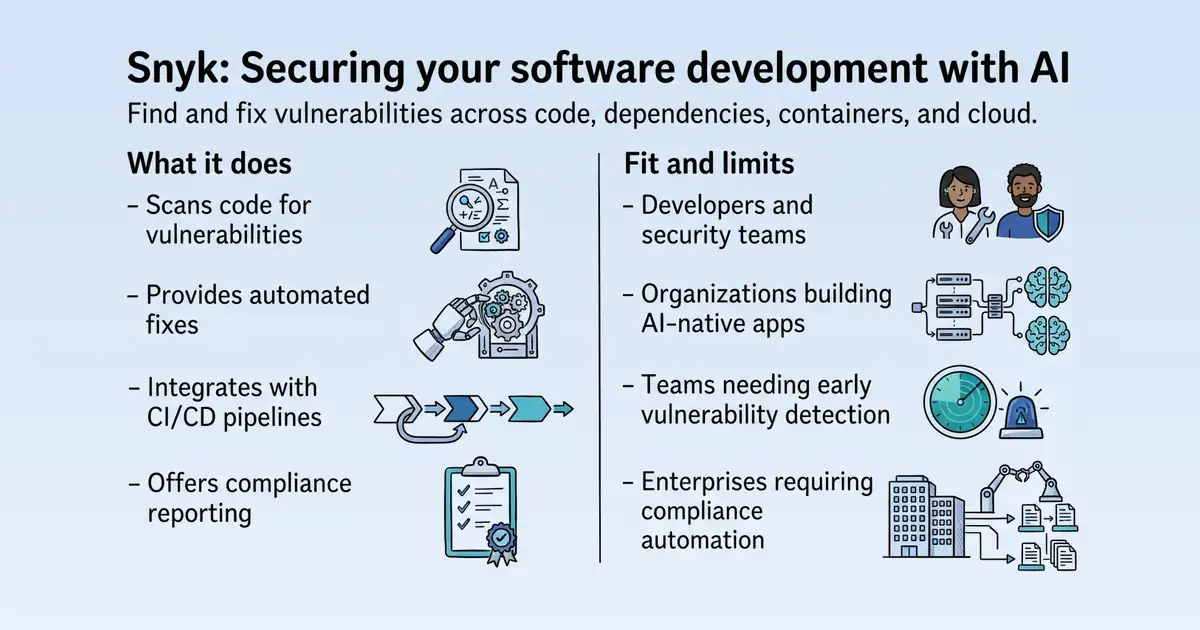
Snyk is an AI-native developer security platform that secures how software is built and how AI-native systems operate S1. It helps developers and security teams find and fix vulnerabilities across code, dependencies, containers, and cloud infrastructure, integrating into existing workflows S1. The platform reduces mean time to remediate and enables continuous security monitoring throughout the SDLC S18 S23.
Product identity and positioning
Name, category, positioning, audience, and first-party claims.
- Identity: Snyk is an AI-native developer security platform S1.
- Core purpose: It helps organizations secure software development and AI-native systems S1.
- Intended users: Developers and security teams who need to build fast while staying secure S1.
- Product scope: A platform covering application security, cloud security, and supply chain security S1.
- Positioning: Snyk positions itself as the AI security platform for the age of AI S1.
- Claimed distinction: Snyk claims a unique combination of developer-first tooling and AI-powered security intelligence S1.
Use cases and audiences
Who the product serves and the jobs it is designed to handle.
| Audience | Practical use case |
|---|---|
| Developers | Find and fix vulnerabilities early in the development cycle with IDE plugins and CLI S14 S66. |
| Security teams | Prioritize and manage vulnerabilities with Snyk Essentials S18. |
| DevOps teams | Integrate security scans into CI/CD pipelines to prevent vulnerable code from reaching production S23. |
| Compliance officers | Automate compliance checks and generate audit-ready reports S31. |
Traffic and search
SEO analysis
Collected Oct 23, 2026snyk.io: an estimated 800,911 total monthly visits and about 61,256 monthly organic visits across 14,623 ranking keywords. Scout crawled 15 pages and measured a technical health score of 97/100.
Search summary
The useful answer before the supporting detail.
Every AI-building team faces one question: can you trust what you're shipping? Snyk secures the code AI writes, the agents it runs, and the apps it builds. snyk.io: an estimated 800,911 total monthly visits and about 61,256 monthly organic visits across 14,623 ranking keywords. Scout crawled 15 pages and measured a technical health score of 97/100.
- Total traffic (modeled): 800,911 monthly visits across all channels.
- Organic search traffic (estimated): 61,256 monthly visits from search.
- Strongest sampled ranking: 14.2 15 at position 1.
- Leading page in the collected evidence: https://snyk.io/solutions/application-security/.
- Closest measured organic competitor: medium.com, appearing 3 times in the sampled first-page SERPs.
- Technical crawl: 15 pages, health score 97/100.
Website intelligence — Collected evidence
Company identity and positioning
| Page type | Evidence | Source |
|---|---|---|
| features | Every AI-building team faces one question: can you trust what you're shipping? Snyk secures the code AI writes, the agents it runs, and the apps it builds. Get started for free or book a demo. | https://snyk.io/ |
| features | Machine-speed threats have eliminated the luxury of backlog. AI attacks chain multiple vulnerabilities autonomously — no human in the loop. What used to be a contained vulnerability becomes a full platform compromise before an analyst finishes reading the alert. | https://snyk.io/ |
| features | Security teams have no inventory of the models, workflows, or agents running in production. AI-native components are embedded everywhere — and you cannot enforce policy, pass an audit, or respond to an incident for systems you didn't know existed. | https://snyk.io/ |
| features | The Snyk AI Security Platform | https://snyk.io/ |
| features | Snyk is how organizations answer the one question every AI-building team faces: can we trust what we're shipping? The AI Security Platform secures the code AI writes, the agents it runs, and the applications it builds — from inception to production. | https://snyk.io/ |
| features | [Learn More](/platform/ "Learn More") | https://snyk.io/ |
| features | for issues prevented upstream in development with Snyk | https://snyk.io/ |
| features | for issues found in runtime with Snyk compared to prior solutions | https://snyk.io/ |
| features | that were redundant with Snyk, that customers consolidated onto Snyk’s platform | https://snyk.io/ |
| features | Why customers trust Snyk | https://snyk.io/ |
| features | > “Every company is moving toward AI, and security has to move with it. Snyk is ready to support our AI initiatives by protecting us as we adopt and experiment with AI. That's exactly the kind of partner we want for this next phase.” | https://snyk.io/ |
| features | > "We want our developers to be enabled with all the metadata about their known CVEs… and Snyk helps us take a systematic and methodical approach to triage the impact of CVEs in our codebase." | https://snyk.io/ |
Website intelligence — Scout synthesis
- Snyk positions itself as an AI Security Platform that secures code, agents, and applications, with a homepage headline "Unleash AI Innovators — Securely" W3.
- The platform addresses three core AI security problems: machine-speed threats, AI-generated code vulnerabilities, and lack of AI inventory W11W12W13W14.
- Snyk's platform includes Agentic Development Security (ADS), AI Security Posture Management (AI-SPM), and Continuous Offensive Security (COS) W82W86W90.
- Pricing is consumption-based for enterprise (credits) and flat-rate for small teams, starting at $25/month W26W27.
- Snyk integrates with Google Cloud's Gemini Code Assist, allowing developers to run security scans via `@Snyk` prompts in the IDE W98W118.
- Scout inference: Snyk's messaging has shifted heavily toward AI-native security, which may resonate with enterprises adopting AI coding tools but could alienate traditional AppSec buyers seeking conventional SAST/SCA solutions.
Domain performance
Modeled total traffic, six-month trend, engagement, countries, and domain identity.
Total website traffic
| Month | Modeled visits |
|---|---|
| 2026-04 | 1,229,170 |
| 2026-05 | 1,081,486 |
| 2026-06 | 1,055,593 |
| 2026-07 | 965,254 |
| 2026-08 | 849,565 |
| 2026-09 | 800,911 |
Top visitor countries
| Country | Name | Traffic share |
|---|---|---|
| US | United States | 29.5% |
| IN | India | 8.4% |
| GB | United Kingdom | 7.3% |
| DE | Germany | 4.5% |
| AU | Australia | 3.5% |
Domain identity
| Signal | Value |
|---|---|
| Registered | May 27, 2015 |
| Last changed | Aug 12, 2026 |
| Expires | May 27, 2027 |
| WHOIS server | whois.nic.io |
| DNSSEC | — |
| Nameservers | a9-64.akam.net, a7-67.akam.net, a26-66.akam.net, a1-49.akam.net, a22-65.akam.net, a16-64.akam.net |
Website capture
Organic keywords
Top keywords and an independent Google result page.
Top organic keywords
| Keyword | Volume | CPC | Estimated value |
|---|---|---|---|
| snyk | 35,120 | $15.18 | $13,540 |
| hanime | 1,295,350 | $0.29 | $7,200 |
| hanimetv | 21,250 | $1.27 | $5,560 |
| synk | 12,970 | $3.11 | $5,350 |
| krutidev to unicode | 59,480 | $0.00 | $3,330 |
Independent Google result page
Query: 14.2 15
| Position | Title | URL | Description |
|---|---|---|---|
| 1 | next 14.2.15 | https://security.snyk.io/package/npm/next/14.2.15 | Information next is a react framework. Affected versions of this package are vulnerable to Use of Cache Containing Sensitive L Cross-site Scripting (XSS) |
| 2 | Componentpedia: next : 14.2.15 issues and vulnerabilities | https://www.meterian.io/components/nodejs/next/14.2.15/ | 14.2.15 issues and vulnerabilities. Check your open source dependency risks. Get immediate insight about security, stability and licensing ... |
| 3 | Should i keep using v.14 or should i move to v.15? : r/nextjs | https://www.reddit.com/r/nextjs/comments/1ocaihj/should_i_keep_using_v14_or_should_i_move_to_v15/ | So, I've been using nextjs 14.2.5 for more than a year, I work in a small company and it's up to me to change or update the stack. |
| 4 | Next.js 14.2 | https://nextjs.org/blog/next-14-2 | Next.js 14.2 includes development, production, and caching improvements. Including new configuration options, 99% Turbopack tests passing, ... |
| 5 | Request for backporting security fixes to Next.js 14.2.x due ... | https://github.com/vercel/next.js/discussions/93868 | Providing a stable backport for the 14.2.x line (essentially an LTS branch) would allow teams the necessary window to properly test and execute the 15.x ... |
| 6 | Middleware vulnerability Next.js | CVE-2025-29227 | https://www.stormshield.com/news/security-alert-next-js-cve-2025-29927-stormshield-products-response/ | A critical authentication bypass vulnerability impacting the Next.js middleware has been reported. bypass Next.js authorization mechanisms. ... |
| 7 | Next.js | https://endoflife.date/nextjs | Next.js is an open-source React framework developed by Vercel. It offers server-side rendering, static site generation, and client-side ... |
| 8 | next | https://www.npmjs.com/package/next?activeTab=versions | Next.js enables you to create full-stack web applications by extending the latest React features, and integrating powerful Rust-based ... |
| 9 | Known vulnerabilities in Next.js 14.2.30 | https://www.cybersecurity-help.cz/vdb/soft/vercel/nextjs/14.2.30/ | Next.js 14.2.30 is affected by 30 vulnerabilities: 6 high, 21 medium, 3 low Critical High Medium Low. Switch to another version. |
| 10 | Next.js and Security Vulnerability CVE-2025–29927 | With Ehxb | https://ehxb.medium.com/next-js-and-security-vulnerability-cve-2025-29927-with-ehxb-16e5ea3d9b4b | CVE-2025–29927 is a high-severity vulnerability discovered by Rachid and Yasser Allam that affects Next.js versions before 14.2.25 and 15.2.3. |
Important pages
Pages earning the most estimated search traffic in the sample.
Website intelligence — Collected evidence
Prioritized website intelligence pages
| Type | Page | Words | Change | URL |
|---|---|---|---|---|
| features | Snyk AI Security Platform \ | Snyk | static | 946 |
| pricing | Snyk Plans and Pricing \ | Get a Custom Quote \ | Snyk | static |
| pricing | Credit Based Billing Details \ | static | 2,701 | new |
| features | Snyk AI Security Platform \ | Snyk | static | 1,012 |
| features | Snyk and Google Gemini: AI Security and Code Assist \ | playwright | 1,770 | new |
| features | Evo Continuous Offensive Security: Find Your Flaws at Machine Speed Before Attackers Do \ | static | 130 | new |
| features | Snyk in 30: Platform \ | static | 128 | new |
| features | Securing AI at Scale: Operationalizing the AI Security Fabric \ | static | 135 | new |
| features | Cybersecurity Compliance Tools \ | Snyk | static | 814 |
| features | DeepCode AI \ | AI Security for SAST \ | Snyk AI \ | Snyk |
| features | Snyk Deployment Options \ | Snyk | static | 939 |
| features | Secure Coding with IDE Plugins \ | Snyk | static | 515 |
| features | Trusted Developer Security Training \ | Snyk Learn \ | Snyk | static |
| features | Security and Governance Solution \ | static | 572 | new |
| features | Industry-Leading Security Intelligence Platform & Proprietary Research \ | static | 514 | new |
Features
| Page type | Evidence | Source |
|---|---|---|
| features | [Skip to main content](#main-content) | https://snyk.io/ |
| features | Snyk launches Evo Agentic AppSec. See how to run the program, not the backlog → | https://snyk.io/ |
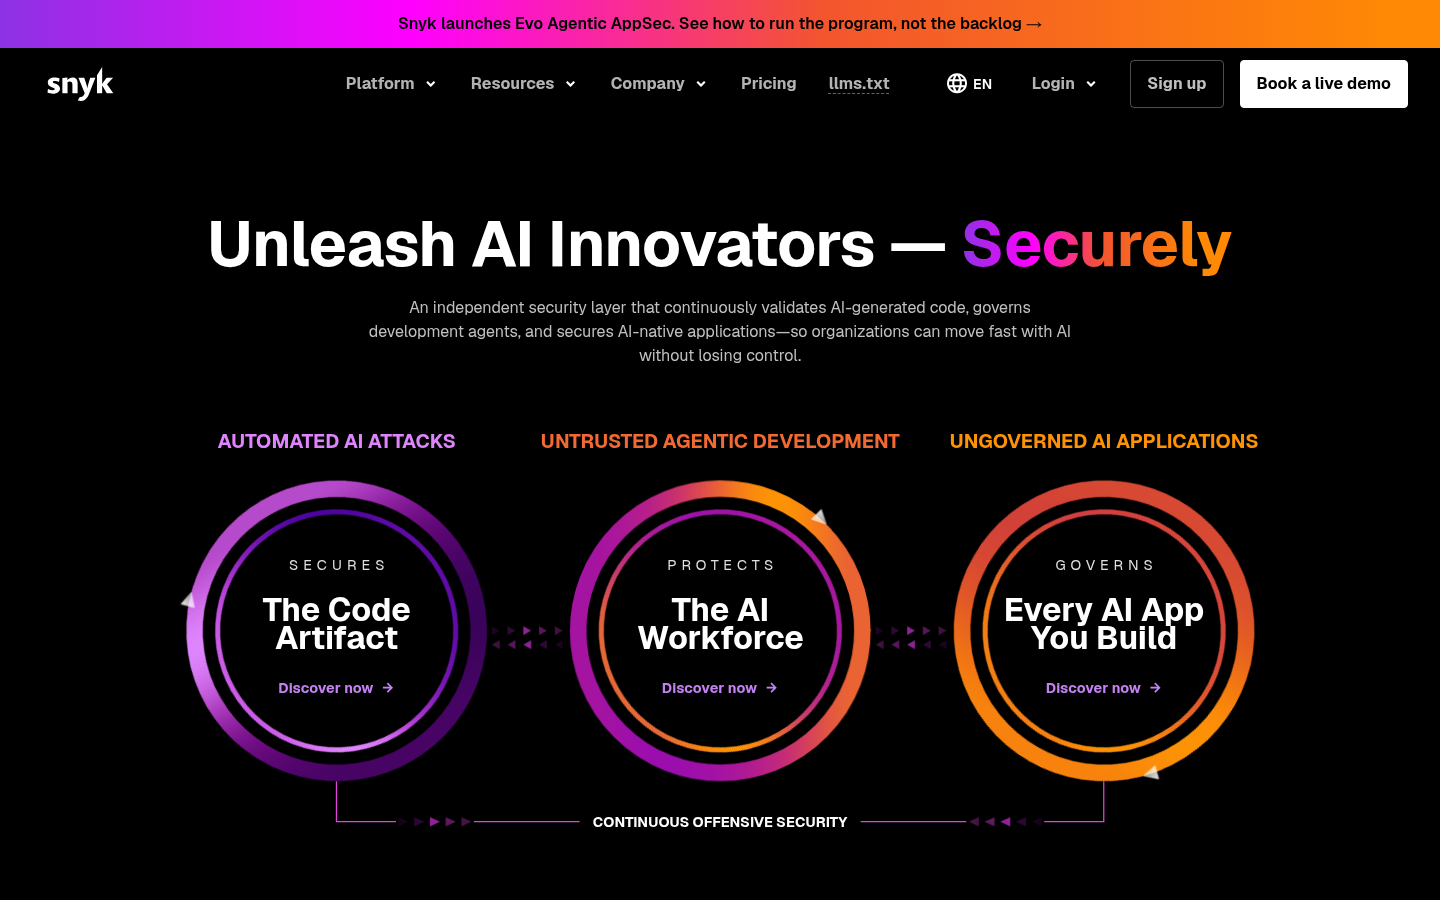
| features | Unleash AI Innovators — Securely | https://snyk.io/ |
| features | An independent security layer that continuously validates AI-generated code, governs development agents, and secures AI-native applications—so organizations can move fast with AI without losing control. | https://snyk.io/ |
| features | AUTOMATED AI ATTACKS | https://snyk.io/ |
| features | Discover now | https://snyk.io/ |
| features | UNTRUSTED AGENTIC DEVELOPMENT | https://snyk.io/ |
| features | Discover now | https://snyk.io/ |
| features | UNGOVERNED AI APPLICATIONS | https://snyk.io/ |
| features | Discover now | https://snyk.io/ |
| features | CONTINUOUS OFFENSIVE SECURITY | https://snyk.io/ |
| features | Three problems defining AI security | https://snyk.io/ |
| features | Machine-speed threats have eliminated the luxury of backlog. AI attacks chain multiple vulnerabilities autonomously — no human in the loop. What used to be a contained vulnerability becomes a full platform compromise before an analyst finishes reading the alert. | https://snyk.io/ |
| features | 65–70% of production code is now AI-generated — and nearly half contains vulnerabilities. AI agents write code, invoke tools, and commit changes with no security checkpoint between inception and production. Security debt is accumulating at machine speed and shrinking at human speed. | https://snyk.io/ |
| features | Security teams have no inventory of the models, workflows, or agents running in production. AI-native components are embedded everywhere — and you cannot enforce policy, pass an audit, or respond to an incident for systems you didn't know existed. | https://snyk.io/ |
| features | The Snyk AI Security Platform | https://snyk.io/ |
| features | Snyk is how organizations answer the one question every AI-building team faces: can we trust what we're shipping? The AI Security Platform secures the code AI writes, the agents it runs, and the applications it builds — from inception to production. | https://snyk.io/ |
| features | [Learn More](/platform/ "Learn More") | https://snyk.io/ |
| features | from improved productivity, improved risk posture, and cost savings on consolidated solutions with Snyk | https://snyk.io/ |
| features | Faster scan time | https://snyk.io/ |
Pricing and plans
| Page type | Evidence | Source |
|---|---|---|
| pricing | Snyk Free & Team subscription | https://snyk.io/plans/ |
| pricing | Join for free | https://snyk.io/plans/ |
| pricing | [Start free](https://app.snyk.io/login "Start free") | https://snyk.io/plans/ |
| pricing | Free plan, plus: | https://snyk.io/plans/ |
| pricing | Compare Free vs. Team plan | https://snyk.io/plans/ |
| pricing | \ | 1,000 tests / month \ |
| pricing | Currently, Snyk Evo capabilities are not available via the Free or Team plan. Access to these capabilities, such as AI Pentesting or Coding Agent security, requires an Enterprise Platform Subscription - book a demo here to contact sales | https://snyk.io/plans/ |
| pricing | Snyk keeps separate test counts for each Snyk product (Snyk Open Source, Snyk Code, Snyk Container, and Snyk IaC) and each Pricing plan. Want to see what counts as a test? Click here for more details. | https://snyk.io/plans/ |
| pricing | What are the test limits under the ‘Free’ plan? | https://snyk.io/plans/ |
| pricing | If you sign up with our ‘Free’ plan, the limits are: Open Source, 200 tests; Code, 100 tests; IaC, 300 tests; Container, 100 tests. Want to know more about the usage settings? Click here for more details. | https://snyk.io/plans/ |
| pricing | Start for free. | https://snyk.io/plans/ |
| pricing | [Join for free now](https://app.snyk.io/login "Join for free now") | https://snyk.io/plans/ |
| pricing | [Buy your Team plan now](/start/team/ "Buy your Team plan now") | https://snyk.io/plans/ |
| pricing | Contact Sales | https://snyk.io/plans/ |
| pricing | 1 credit = $1. The pricing unit for all capabilities. | https://snyk.io/plans/ |
| pricing | See full consumption details | https://snyk.io/plans/ |
| pricing | Real-time credit usage is visible in your Snyk admin dashboard, with per-capability breakdown and threshold alerts. See here for more information around our billing and usage settings. | https://snyk.io/plans/ |
| pricing | Post-remediation retesting is a follow-on workflow in which a vulnerability identified in an Assessment is fixed by the user, who may then prompt the agent to retest that same vulnerability to confirm its remediation. Upon retest, that same vulnerability is either confirmed as remediated, or it persists, in which case the retesting workflow can be repeated. Retesting is specific to vulnerabilities of an existing Assessment, is included as part of the original billing event in the ‘per Assessment’ rate and is not billed as a new event. | https://snyk.io/policies/credit-based-billing/ |
| pricing | Each Assessment tests a single Application and its secondary URLs. For especially complex targets with unique testing depth, a completed report may flag attack paths that merit deeper, dedicated testing; pursuing these is a separate Assessment that the customer chooses to run. During the testing stage, Snyk applies a token reasoning limit equivalent to $2,000 USD. If an Assessment approaches this limit, the agent identifies areas that require additional analysis, documents those areas in the report, and recommends a follow-up Assessment. The original Assessment still completes with a full Assessment report. The customer may choose to pursue the flagged areas as a separate billable Assessment. | https://snyk.io/policies/credit-based-billing/ |
Integrations and supported platforms
No supporting public-page evidence was collected for this category.
Product and company updates
No supporting public-page evidence was collected for this category.
Website intelligence — Scout synthesis
- Homepage (snyk.io/): Primary landing page focused on AI Security Platform messaging, with links to Evo capabilities W1W2W5.
- Pricing page (snyk.io/plans/): Details Free, Team, and Enterprise plans; includes FAQ on Evo availability and developer counting W25W26W46W48.
- Platform page (snyk.io/platform/): Overview of ADS, AI-SPM, COS, and Agentic AppSec W73W82W86W90.
- DeepCode AI page (snyk.io/platform/deepcode-ai/): Highlights AI-powered SAST with 25M+ data flow cases and 19+ languages W169W178.
- Compliance page (snyk.io/platform/compliance/): Covers SOC 2, ISO 27001, PCI DSS 4.0, CRA, and OWASP Top 10 W145W152.
- Deployment options page (snyk.io/platform/deployment-options/): Details SaaS, Private Cloud on AWS, and data residency options W193W201W216.
- IDE plugins page (snyk.io/platform/ide-plugins/): Lists plugins for JetBrains, VS Code, Eclipse, and Visual Studio W217W222.
- Blog post on Gemini integration (snyk.io/blog/...): Explains how to use Snyk within Gemini Code Assist W97W116W118.
- Landing pages: COS solution guide and on-demand demo pages capture leads via gated content W121W128W136.
Rank tracking
Persistent keyword baselines and position movement.
This analysis created the first position baseline at 2026-10-23T23:54:12.730Z. Movement appears after the next fresh analysis using the same location and language.
Features
Features and capabilities
Core functions and evidence-backed product capabilities.
| Capability | What it does |
|---|---|
| SAST scanning | Finds and auto-fixes code vulnerabilities using static analysis S18. |
| Open source and dependency scanning | Detects vulnerabilities and license issues in open source packages S31. |
| Container scanning | Scans container images for vulnerabilities S14. |
| Infrastructure as code scanning | Identifies misconfigurations in IaC S14. |
| CI/CD integration | Prevents vulnerabilities from entering production through pre-merge scanning S23. |
| IDE plugins | Provides real-time vulnerability scanning and fix advice in popular IDEs S66. |
| AI-powered autofix | Automatically fixes code vulnerabilities with Snyk Agent Fix S18. |
| Compliance automation | Automates compliance checks and generates audit-ready reports for standards like SOC 2 and ISO 27001 S31. |
Integrations and ecosystem
Connected products, exports, APIs, and workflow compatibility.
| Integration or interface | Type | What it enables |
|---|---|---|
| GitHub, Bitbucket, GitLab, Azure Repos | Integration | Natively integrates with source code management systems to scan repositories and pull requests S64. |
| Jenkins, CircleCI, GitHub Actions, AWS CodePipeline, Azure Pipelines, Bitbucket Pipelines, Maven, TeamCity, Terraform | Integration | Integrates with CI/CD tools to run security scans and provide fix advice S23. |
| JetBrains, VS Code, Eclipse, Visual Studio | Extension | Provides IDE plugins for real-time vulnerability scanning and fix advice S66. |
| Snyk API (via CLI) | API | Enables programmatic scanning and monitoring via command-line interface S14. |
Pricing
Pricing and plans
Published plans, free access, trials, credits, and pricing limitations.
| Plan or offer | Verified price and billing | Included | Limits |
|---|---|---|---|
| Free | $0 monthly S1 | 200 Open Source, 100 Code, 300 IaC, 100 Container tests per month S1 | 5 projects S1 |
| Team | From $25 per month, billed monthly S1 | 1,000 Code tests per month; other limits raised but not published S1 | 100 projects, Jira integration S1 |
| Enterprise | Contact sales; prepaid credits for contract term (1 credit = $1) S1 | Code and Open Source 1.0 credit per active contributor per day; Container 0.33 per image per day S1 | Secrets, API & Web and other capabilities by credit rate S1 |
Competition
Competitive landscape
Domains competing for the same organic search demand.
Sampled competitors
| Competitor | First-page appearances | Sampled queries | Average position | Queries observed |
|---|---|---|---|---|
| medium.com | 3 | 2 | 6 | 14.2 15, 15.5 12 |
| reddit.com | 2 | 2 | 3.5 | 14.2 15, 15.5 12 |
| nextjsweekly.com | 1 | 1 | 1 | 15.5 12 |
| reactnext-central.xyz | 1 | 1 | 2 | 14.2 15 |
| dev.to | 1 | 1 | 2 | 15.5 12 |
| iloveblogs.blog | 1 | 1 | 3 | 14.2 15 |
| x.com | 1 | 1 | 4 | 14.2 15 |
| linearloop.io | 1 | 1 | 4 | 15.5 12 |
| nvd.nist.gov | 1 | 1 | 5 | 15.5 12 |
| github.com | 1 | 1 | 6 | 14.2 15 |
Website intelligence — Collected evidence
Customers, testimonials, and first-party review claims
No supporting public-page evidence was collected for this category.
Independent review sources discovered
No links to supported independent review platforms were discovered on the collected pages.
Website intelligence — Scout synthesis
- Snyk positions itself against traditional scanners by highlighting AI Pentesting and Red Teaming for architectural flaws and chained business-logic vulnerabilities W91.
- The platform claims to find BOLA, privilege escalation, and cross-tenant leakage that signature-based tools cannot W124.
- Snyk's DeepCode AI is described as "the fastest, most accurate, and most comprehensive set of AppSec testing tools on the market" W171.
- Scout inference: Snyk differentiates on AI-native capabilities (ADS, AI-SPM, COS) rather than traditional SAST/SCA features, suggesting a competitive pivot toward AI security leaders like Protect AI or Wiz.
AI visibility
Measured ChatGPT and Google AI mentions with cited sources.
AI-assistant referral traffic
- Estimated current generative-AI referral share: 1.1%
| Month | Traffic share | Source |
|---|---|---|
| — | — | All AI assistants |
| — | — | All AI assistants |
| — | — | All AI assistants |
Website intelligence — Collected evidence
Site-stated AI capabilities
| Page type | Evidence | Source |
|---|---|---|
| features | Every AI-building team faces one question: can you trust what you're shipping? Snyk secures the code AI writes, the agents it runs, and the apps it builds. Get started for free or book a demo. | https://snyk.io/ |
| features | Machine-speed threats have eliminated the luxury of backlog. AI attacks chain multiple vulnerabilities autonomously — no human in the loop. What used to be a contained vulnerability becomes a full platform compromise before an analyst finishes reading the alert. | https://snyk.io/ |
| features | Security teams have no inventory of the models, workflows, or agents running in production. AI-native components are embedded everywhere — and you cannot enforce policy, pass an audit, or respond to an incident for systems you didn't know existed. | https://snyk.io/ |
| features | The Snyk AI Security Platform | https://snyk.io/ |
| features | Snyk is how organizations answer the one question every AI-building team faces: can we trust what we're shipping? The AI Security Platform secures the code AI writes, the agents it runs, and the applications it builds — from inception to production. | https://snyk.io/ |
| features | > “Every company is moving toward AI, and security has to move with it. Snyk is ready to support our AI initiatives by protecting us as we adopt and experiment with AI. That's exactly the kind of partner we want for this next phase.” | https://snyk.io/ |
| features | Snyk AI Security Platform | https://snyk.io/platform/ |
| features | The Snyk AI Security Platform | https://snyk.io/platform/ |
| features | Snyk’s AI-native and agentic platform helps organizations secure and govern development to unleash productivity, reduce business risk, and accelerate software delivery for the age of AI. | https://snyk.io/platform/ |
| features | Total visibility and machine-speed governance for AI applications | https://snyk.io/platform/ |
| features | The centralized command center for your AI security posture. Replace manual reviews with automated, code-first governance that turns business intent into enforceable guardrails. | https://snyk.io/platform/ |
| features | > In AI security, detection was never the bottleneck. By pairing Claude's capabilities with Snyk, enterprises can turn high-fidelity findings into action inside the workflows where software is built. | https://snyk.io/platform/ |
| features | A new generation of builders — humans, models, and autonomous agents — now creates software together. When creation accelerates beyond human speed, risk accelerates with it. Even the most capable model in the world cannot be trusted to govern its own cybersecurity output at scale. Snyk's AI Security Platform uses a mix of proprietary security engines, self-hosted models, and third-party frontier models through secure connections. | https://snyk.io/platform/ |
| features | Improved outcomes for AI fixes | https://snyk.io/platform/ |
| features | Deploy Evo, the agentic security orchestrator, to future-proof your defense and provide autonomous, runtime protection for non-deterministic AI-native applications. | https://snyk.io/platform/ |
| features | > Every company is moving toward AI, and security has to move with it. Snyk is ready to support our AI initiatives by protecting us as we adopt and experiment with AI. That's exactly the kind of partner we want for this next phase. | https://snyk.io/platform/ |
| features | Developers worldwide continue to adopt AI to speed up software delivery. But this speed often impacts security, as developers assume AI-generated code is secure without thoroughly checking for errors or vulnerabilities. | https://snyk.io/blog/snyk-security-solution-now-integrated-into-google-clouds-gemini-code-assist/ |
| features | To address these challenges, Snyk announced today the integration of Synk’s security solution into Gemini Code Assist Tools. Collaborating with Google Cloud is a natural progression from Synk’s groundbreaking plans in April 2024. Snyk, a leading trusted, modern developer-first AI security platform, is now integrated into Gemini Code Assist, a leading software development assistant AI coding tool. This empowers developers to access Snyk’s powerful functionalities with natural language prompts, communicating directly with Snyk’s pioneering industry-leading hybrid AI model through Gemini Code Assist’s chat interface. | https://snyk.io/blog/snyk-security-solution-now-integrated-into-google-clouds-gemini-code-assist/ |
| features | By integrating Snyk into Gemini Code Assist, application security can shift even further left, enabling teams to securely adopt and leverage AI at scale. | https://snyk.io/blog/snyk-security-solution-now-integrated-into-google-clouds-gemini-code-assist/ |
| features | Snyk’s collaboration with Google Cloud bridges the gap between innovation and security, solving many challenges modern AppSec teams face. Snyk’s integration into Gemini Code Assist empowers developers to use AI coding tools without sacrificing speed, productivity, or security while enabling security teams to maintain guardrails that keep businesses safe. | https://snyk.io/blog/snyk-security-solution-now-integrated-into-google-clouds-gemini-code-assist/ |
These are first-party product claims, not independent measurements of AI-search visibility.
Website intelligence — Scout synthesis
- Snyk's homepage prominently features AI security messaging, including "Unleash AI Innovators — Securely" and "An independent security layer that continuously validates AI-generated code" W3W4.
- The platform page emphasizes "Security at machine speed" and "AI-native security orchestration" W75W80.
- Snyk's blog covers AI security integrations, such as the Gemini Code Assist partnership W98W100.
- Scout inference: Snyk is heavily investing in AI-related content and keywords, which may improve visibility for AI security queries but could dilute traditional AppSec keyword rankings.
Marketing opportunities
Actions calculated directly from the collected evidence.
| Opportunity | Recommended action | Evidence |
|---|---|---|
| Competitor gap | Review the sampled queries where medium.com appears. | 3 first-page appearances across 14.2 15, 15.5 12 |
Website intelligence — Collected evidence
Website evidence gaps
- integrations: no usable public page was collected; verify whether the site publishes this evidence.
- customers: no usable public page was collected; verify whether the site publishes this evidence.
- reviews: no usable public page was collected; verify whether the site publishes this evidence.
- changes: no usable public page was collected; verify whether the site publishes this evidence.
- identity: no usable public page was collected; verify whether the site publishes this evidence.
- technical: no usable public page was collected; verify whether the site publishes this evidence.
Website intelligence — Scout synthesis
- Evo capabilities gated content: Snyk offers solution guides and white papers on COS and AI Security Fabric, indicating lead-gen opportunities W121W136.
- Free tier for open source: Snyk offers free access for open source maintainers, which can drive community adoption and backlinks W37W38W39.
- Compliance cheat sheets: Snyk promotes SOC 2 and ISO 27001 cheat sheets, suggesting demand for compliance-related content W162W166.
- On-demand demo: Snyk provides a 30-minute platform demo webinar, useful for mid-funnel conversion W128W130.
- Scout inference: Snyk could expand marketing around AI-specific compliance (e.g., EU AI Act) and agentic security use cases to capture emerging demand.
Trust and proof
Customers, proof, and reviews
Published proof, customer signals, and review evidence.
Independent reviews
| Platform | Page | How it was found | Note |
|---|---|---|---|
| Should I Use It | Snyk Review 2026: Pricing, Pros & Cons / Should I Use It | Grounded web search | - + 4.5/5 across 138 verified G2 reviews ... Praised for ease of use and seamless integrations - + Entry price far cheaper than rivals like Veracode ($15K/yr) - + Auto-fix pull requests and comprehensive vulnerability database - + Scans inside IDEs and CI |
| RFP.wiki | Snyk · What Buyers Need to Know (2026) | Grounded web search | / --- / --- / --- / / G2 / 4.5 ... 135 reviews / / / 4.6 / 21 reviews ... / Software Advice / 4.6 / 21 reviews / / Trustpilot / 3.0 / 5 reviews / / ... / 4.3 / 134 reviews / / / 4.3 / 28 reviews / / RFP.wiki Score / 4.5 / Review Sites Score Average: 4.2 |
| DevTune | Snyk AI visibility in DevSecOps & Application Security | Grounded web search | - High volume of false positive alerts requiring manual triage - Alert fatigue from excessive findings at scale - Slow and inconsistent customer support response times - High enterprise licensing cost relative to point solutions - DAST product operates in a separate non-integrated interface - Weak secrets detection compared to dedicated tools - Complex configuration for managing policies across many repositories - Limited IaC coverage for some environments |
| G2 | Recensioni Snyk 2026: Dettagli, Prezzi e Funzionalità / G2 | Grounded web search | Gli utenti lodano costantemente Snyk per la sua facilità d'uso e integrazione senza soluzione di continuità con le pipeline CI/CD, rendendolo uno strumento prezioso per identificare e affrontare le vulnerabilità nel codice. La capacità della piattaforma di fornire consigli di rimedio attuabili ne aumenta l'attrattiva, permettendo agli sviluppatori di risolvere rapidamente i problemi di sicurezza. Tuttavia, alcuni utenti notano una frequente occorrenza di falsi positivi nel rilevamento delle vuln |
| G2 | Compare Mend.io and Snyk Social Share Options | Grounded web search | Mend.io(112)4.3 out of 5Mend.io By Mend Snyk(122)4.5 out of 5Snyk By Snyk ... Star Rating (122) 4.5 out of 5 ... I think it is so easy to use. I like that it includes solutions to the issues I have, it can quickly scan a |
Customer proof
No named customers, testimonials, or customer case studies were found.
External links were grounded in one live web search. Search snippets are leads, not independently scraped page content; rejected links remain available in Review evidence.
Company, security, and trust
Ownership, policies, security signals, and public trust evidence.
| Signal | Finding | Source |
|---|---|---|
| Company and ownership | Visionary leadership | source |
| Contact and support | Not published on the collected pages. | — |
| Legal and privacy | Not published on the collected pages. | — |
| Security and compliance | Not published on the collected pages. | — |
| Uptime and status page | Security teams have no inventory of the models, workflows, or agents running in production. AI-native components are embedded everywhere — and you cannot enforce policy, pass an audit, or respond to an incident for syste | source |
Not found on the collected pages: contact and support, legal and privacy, security and compliance. This only means Scout did not find it on the pages it read; it says nothing about the company itself.
Documentation and product updates
Help resources, product guidance, and visible changes over time.
| Resource or update | Type | What is available | Date or freshness |
|---|---|---|---|
| Snyk AI Security Platform / Secure Code, Agents & Apps / Snyk | Release notes | Public product change history. (source) | Not dated |
Not found in the collected public sources: public roadmap, status page, separate help center or knowledge base.
Technical
Technical and delivery signals
Delivery model, platforms, API, data ownership, reliability claims and release activity.
| Signal | Finding | Source |
|---|---|---|
| Delivery model (cloud, self-hosted, desktop, browser extension) | Snyk offers cloud-first deployment options including multi-tenant SaaS and Private Cloud S49. | S49 |
| Platforms and apps | Snyk provides a CLI that supports many languages and integrates with IDEs S14 S66. | S14 S66 |
| API and extensibility (API, SDK, webhooks, MCP, plugins) | Snyk offers a CLI with API token authentication and IDE plugins S66. | S66 |
| Data ownership and export | Snyk places utmost importance on keeping data safe and offers a proxy service to limit access to sensitive information S49. | S49 |
| Performance and reliability claims | Snyk claims to reduce time to remediate by 84% or more S18. | S18 |
| Release activity | Snyk has plans and pricing that suggest ongoing updates S1. | S1 |
Measured infrastructure
Domain, certificate, and hosting signals, measured directly.
| Signal | Finding |
|---|---|
| First archived | 2015-07-09 — web archive |
| TLS certificate | DigiCert Inc, valid, expires 2026-12-08 |
| Security headers | HSTS, CSP, X-Content-Type-Options, Referrer-Policy |
| Headers not served | X-Frame-Options |
| Server header | Vercel |
| Mail handled by | aspmx.l.google.com, alt1.aspmx.l.google.com |
| Nameservers | a16-64.akam.net, a9-64.akam.net |
Not measurable: rdap: no RDAP server published for .io; rdap: exceeded the overall budget; wayback: exceeded the overall budget; tls: exceeded the overall budget; dns: exceeded the overall budget; headers: exceeded the overall budget. A gap here means the lookup was unavailable, not that the finding is negative.
Technical site audit
A bounded multi-page crawl with page-level issues and URLs.
Scout — Bounded technical crawl
- Pages crawled: 15 of 15 maximum
- Technical health: 97/100
- Critical issues: 0
- Warnings: 9
- Notices: 3
Issues
| Severity | Issue | Value | Affected URL |
|---|---|---|---|
| notice | Meta description length should be reviewed | 197 | https://snyk.io/ |
| warning | Title length should be reviewed | 83 | https://snyk.io/plans/ |
| warning | Page should have one primary H1 | 4 | https://snyk.io/plans/ |
| warning | Title length should be reviewed | 72 | https://snyk.io/platform/ |
| notice | Meta description length should be reviewed | 200 | https://snyk.io/platform/ |
| warning | Missing meta description | — | https://snyk.io/integrations/ |
| warning | Title length should be reviewed | 68 | https://snyk.io/platform/deepcode-ai/ |
| warning | Title length should be reviewed | 67 | https://snyk.io/evo/ |
| notice | Meta description length should be reviewed | 194 | https://snyk.io/evo/ |
| warning | Title length should be reviewed | 75 | https://snyk.io/product/snyk-code/ |
| warning | Title length should be reviewed | 100 | https://snyk.io/product/container-vulnerability-management/ |
| warning | Title length should be reviewed | 74 | https://snyk.io/product/infrastructure-as-code-security/ |
Crawled pages
| Status | Title | H1s | Words | Response | URL |
|---|---|---|---|---|---|
| 200 | Snyk AI Security Platform \ | Secure Code, Agents & Apps \ | Snyk | 1 | 1509 |
| 200 | Snyk Plans and Pricing \ | Try for Free or from $25/month \ | Get a Custom Quote \ | Snyk | 4 |
| 200 | See Snyk AI Security Solution in action - Book a live demo \ | Snyk | 1 | 255 | 255 ms |
| 200 | Snyk AI Security Platform \ | AI-Driven Developer Security Platform \ | Snyk | 1 | 1451 |
| 200 | Snyk Integrations \ | Snyk | 1 | 1173 | 351 ms |
| 200 | DeepCode AI \ | AI Code Review \ | AI Security for SAST \ | Snyk AI \ | Snyk |
| 200 | Security for Agentic AI Applications and Tools \ | Evo by Snyk \ | Snyk | 1 | 1248 |
| 200 | Evo Agentic Development Security \ | Snyk | 1 | 1124 | 435 ms |
| 200 | Evo AI-SPM: Security Posture Management for Agentic AI \ | Snyk | 1 | 940 | 253 ms |
| 200 | Evo Continuous Offensive Security \ | Snyk | 1 | 1325 | 312 ms |
| 200 | Evo Agentic AppSec \ | Snyk | 1 | 1567 | 231 ms |
| 200 | Snyk Code \ | SAST Code Scanning Tool \ | Code Security Analysis & Fixes \ | Snyk | 1 |
| 200 | Open Source Security Management \ | Open Source SCA Tool \ | Snyk | 1 | 1270 |
| 200 | Container vulnerability management \ | Container Security Tools \ | Kubernetes Security Solutions \ | Snyk | 1 |
| 200 | Infrastructure as Code Security \ | IaC Security Tools \ | IaC Scanning \ | Snyk | 1 |
This is a bounded Scout crawl. Core Web Vitals and Lighthouse scores are not claimed unless a dedicated performance audit is connected.
Search Console and Analytics
First-party search and behavioral data connection state.
Modeled acquisition channels
| Channel | Estimated share |
|---|---|
| direct | 38.9% |
| search | 45.4% |
| search organic | 44.0% |
| search paid | 1.4% |
| social | 2.6% |
| social organic | 2.5% |
| social paid | 0.1% |
| referrals | 10.0% |
| paid referrals | 0.9% |
| 1.2% | |
| gen ai | 1.1% |
| affiliate | 0.0% |
| other | 0.0% |
First-party connections
| Integration | Status | Data available after connection |
|---|---|---|
| Google Search Console | Not connected | Clicks, impressions, CTR, average position, queries, pages, countries, and devices |
| Google Analytics | Not connected | Organic sessions, engagement, landing pages, conversions, geography, and devices |
No first-party Search Console or Analytics numbers are shown until the site owner authorizes the corresponding Google account. Scout traffic model values above are modeled estimates, not private analytics totals.
Limits and method
Limitations and open questions
Known constraints and missing evidence from the collected pages.
The collected pages do not mention specific competitors. The evidence catalog contains no independent reviews or ratings; external review profiles were not collected. Pricing details are limited to the plans table; the Team plan's limits beyond Code tests are not fully published. The platform's AI security capabilities are described primarily in marketing terms with limited technical specifics.
Sources, method, and limitations
Evidence inventory, collection method, provider use, and constraints.
This report is based on 15 collected pages from snyk.io, including product pages, platform pages, and pricing pages. Static and browser rendering rendering were used; external proof search was enabled and completed. Evidence is cited by source tokens [S#]. The pricing table was derived from a researcher-reviewed page and may not reflect current offers. No customer reviews were independently verified beyond first-party testimonials.
- Official Websitehttps://snyk.io/Verified
- Official Websitehttps://snyk.io/about/Verified
- Official Websitehttps://snyk.io/platform/Verified
- Official Websitehttps://snyk.io/platform/snyk-cli/Verified
- Official Websitehttps://snyk.io/product/snyk-code/Verified
- Pricing Pagehttps://snyk.io/plans/Verified
- Pricing Pagehttps://snyk.io/jp/plans/Verified
- Official Websitehttps://snyk.io/government-security-solution/Verified
- Official Websitehttps://snyk.io/jp/platform/Verified
- Official Websitehttps://snyk.io/platform/ci-cd-pipeline-security/Verified
- Official Websitehttps://snyk.io/platform/compliance/Verified
- Official Websitehttps://snyk.io/platform/deepcode-ai/Verified
- Official Websitehttps://snyk.io/platform/deployment-options/Verified
- Official Websitehttps://snyk.io/platform/git-repository-security/Verified
- Official Websitehttps://snyk.io/platform/ide-plugins/Verified
- Review Sitehttps://shouldiuse.io/r/snykVerified
- Review Sitehttps://www.rfp.wiki/it-security/application-security-testing/snykVerified
- Review Sitehttps://devtune.ai/verticals/devsecops-application-security/snykVerified
- Review Sitehttps://www.g2.com/it/products/snyk/reviewsVerified
- Review Sitehttps://www.g2.com/compare/mend-io-vs-snykVerified