Overview
Summary
The useful answer before the supporting detail.
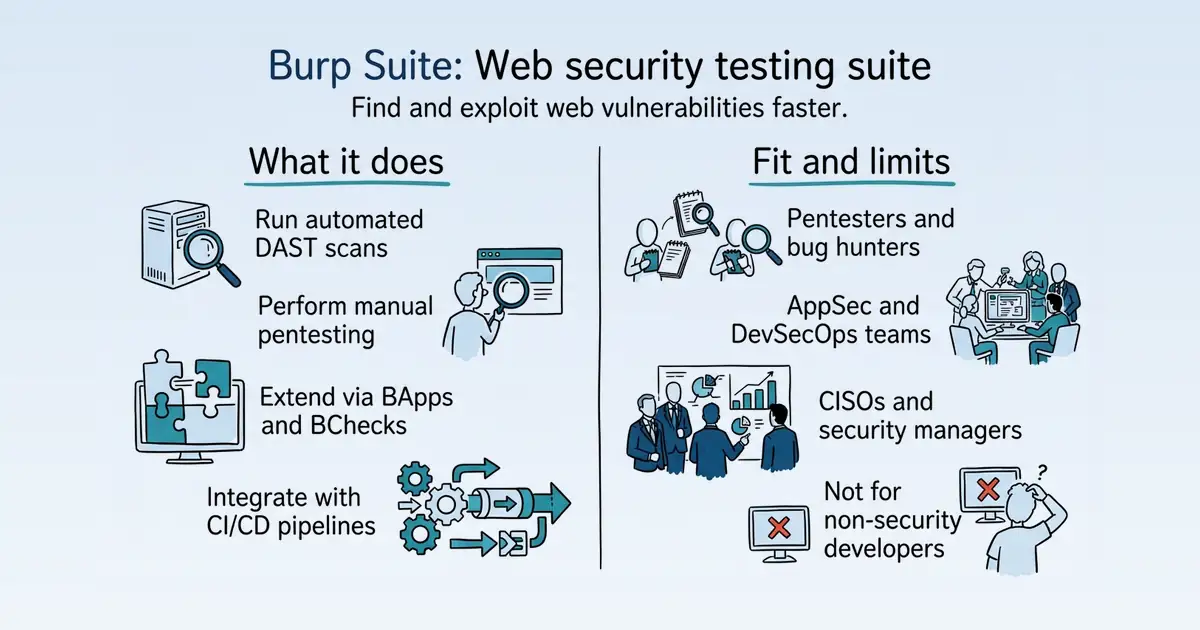
PortSwigger is a global leader in cybersecurity providing a suite of web application security testing tools called Burp Suite S1. It is used by pentesters, bug bounty hunters, and security teams to identify and exploit vulnerabilities in web applications S39 S47. The suite combines manual testing tools, automated scanning, and AI capabilities to help catch more vulnerabilities faster, while related products like the Web Security Academy enable skill development S1.
Product identity and positioning
Name, category, positioning, audience, and first-party claims.
- Identity: PortSwigger's Burp Suite, a comprehensive web application security testing toolkit S1 S39.
- Core purpose: Enables security professionals to test, find, and exploit vulnerabilities in web applications S39.
- Intended users: Penetration testers, bug bounty hunters, AppSec teams, and CISOs S39 S47.
- Product scope: A suite of integrated products and components, including Burp Suite Professional, Enterprise, and DAST S1 S20.
- Positioning: Burp Suite is positioned as "the most widely used web application security testing software" S39.
- Claimed distinction: Claimed distinction includes being the "true one-box solution" and having an extensive BApp ecosystem S47 S128.
Use cases and audiences
Who the product serves and the jobs it is designed to handle.
| Audience | Practical use case |
|---|---|
| Penetration testers | Use Burp Suite for manual and automated testing to catch vulnerabilities for clients S47 S45. |
| Bug bounty hunters | Use Pro's special tools to work faster and earn larger bounties S43 S47. |
| CISOs and security leaders | Use Burp Suite DAST's scalable scanning and reporting for portfolio-wide security S47. |
| AppSec managers | Own vulnerability management and drive secure development with automated scans S47. |
| Software engineers | Integrate security into the SDLC with CI-driven scanning S68 S47. |
| Managed Security Service Providers (MSSPs) | Monitor client assets and ensure compliance S47. |
Traffic and search
SEO analysis
Collected Oct 23, 2026portswigger.net: an estimated 1,565,350 total monthly visits and about 87,184 monthly organic visits across 5,990 ranking keywords. Scout crawled 15 pages and measured a technical health score of 98/100.
Search summary
The useful answer before the supporting detail.
We enable the world to secure the web. Burp Suite, the Web Security Academy, and world-leading research from PortSwigger — the AppSec community’s home. portswigger.net: an estimated 1,565,350 total monthly visits and about 87,184 monthly organic visits across 5,990 ranking keywords. Scout crawled 15 pages and measured a technical health score of 98/100.
- Total traffic (modeled): 1,565,350 monthly visits across all channels.
- Organic search traffic (estimated): 87,184 monthly visits from search.
- Strongest sampled ranking: all labs at position 1.
- Leading page in the collected evidence: https://portswigger.net/bappstore.
- Closest measured organic competitor: facebook.com, appearing 4 times in the sampled first-page SERPs.
- Technical crawl: 15 pages, health score 98/100.
Website intelligence — Collected evidence
Company identity and positioning
| Page type | Evidence | Source |
|---|---|---|
| trust | We enable the world to secure the web. Burp Suite, the Web Security Academy, and world-leading research from PortSwigger — the AppSec community’s home. | https://portswigger.net/ |
| features | Customers About Blog Careers Legal Contact Resellers | https://portswigger.net/solutions |
| features | My account Customers About Blog Careers Legal Contact Resellers | https://portswigger.net/solutions |
| features | Support Center Get help and advice from our experts on all things Burp. Documentation Tutorials and guides for Burp Suite. Get Started - Professional Get started with Burp Suite Professional. Get Started - DAST Get started with Burp Suite DAST. Downloads Download the latest version of Burp Suite. | https://portswigger.net/solutions |
| features | As an applications security manager, you are challenged to support multiple development teams and to secure many applications. Burp Suite DAST's automated scanning and dashboards are the safety net that allows you to keep your portfolio in check, giving you time to spend where it is needed most. | https://portswigger.net/solutions |
| features | Agile software engineers produce a lot of code. But how do you know that code is secure? Burp Suite DAST can scan every commit you make - right from your CI/CD pipeline. Scan for critical vulnerabilities, remediate bugs, and open the door to a true DevSecOps approach. | https://portswigger.net/solutions |
| features | Managed Security Service Providers (MSSPs) put customer security at the forefront of every process. Utilize Burp Suite DAST's advanced web security testing tools to maintain the security of your managed applications. Tailor scanning to customer requirements, and provide ongoing training and development with built-in remediation. | https://portswigger.net/solutions |
| features | The true one-box solution for finding and exploiting vulnerabilities in web applications. | https://portswigger.net/solutions |
| features | Hacking for reward, creatively overcoming limits, and protecting the web. | https://portswigger.net/solutions |
| features | What our customers say about us | https://portswigger.net/solutions |
| features | of our customers would recommend Burp Suite. | https://portswigger.net/solutions |
| features | See more customer stories | https://portswigger.net/solutions |
Domain performance
Modeled total traffic, six-month trend, engagement, countries, and domain identity.
Total website traffic
| Month | Modeled visits |
|---|---|
| 2026-04 | 1,749,602 |
| 2026-05 | 1,958,262 |
| 2026-06 | 1,437,868 |
| 2026-07 | 1,591,531 |
| 2026-08 | 1,596,814 |
| 2026-09 | 1,565,350 |
Top visitor countries
| Country | Name | Traffic share |
|---|---|---|
| IN | India | 24.1% |
| US | United States | 14.2% |
| MX | Mexico | 4.3% |
| ID | Indonesia | 4.2% |
| PK | Pakistan | 2.8% |
Domain identity
| Signal | Value |
|---|---|
| Registered | Sep 9, 2001 |
| Last changed | Aug 8, 2026 |
| Expires | Sep 9, 2027 |
| WHOIS server | whois.verisign-grs.com |
| DNSSEC | Not signed |
| Nameservers | NS-1337.AWSDNS-39.ORG, NS-194.AWSDNS-24.COM, NS-1955.AWSDNS-52.CO.UK, NS-573.AWSDNS-07.NET |
Website capture
Organic keywords
Top keywords and an independent Google result page.
Top organic keywords
| Keyword | Volume | CPC | Estimated value |
|---|---|---|---|
| burp suite | 83,940 | $1.71 | $65,360 |
| portswigger | 39,830 | $1.80 | $33,040 |
| burp suite download | 11,060 | $1.15 | $16,350 |
| burpsuite | 18,460 | $1.41 | $16,100 |
| portswigger web security academy | 12,400 | $2.89 | $11,220 |
Independent Google result page
Query: all labs
| Position | Title | URL | Description |
|---|---|---|---|
| 1 | All labs | Web Security Academy | https://portswigger.net/web-security/all-labs | All labs · SQL injection · Cross-site scripting · Cross-site request forgery (CSRF) · Clickjacking · DOM-based vulnerabilities · Cross-origin resource sharing ( ... |
| 2 | Walk-In Lab: Order Any Lab Test or Blood Tests Online | https://www.walkinlab.com/?srsltid=AYCX9vL7Gf_rsPRPhlnTalANbXqXwM5yNrCYghrhnTmpuagi3u-PvPq_ | Walk-In Lab provides affordable, convenient, and confidential lab testing directly to consumers. Order any lab test you need and save on healthcare costs. No ... |
| 3 | all labs - Apps on Google Play | https://play.google.com/store/apps/details?id=com.alllabs1.laboratories&hl=en_US | All Labs connects patients with certified medical laboratories, making it easy to book tests, track results, and manage your health from your ... |
| 4 | Locate Blood Testing Labs: Find a Labcorp or Quest Near Me | https://www.healthlabs.com/find-a-lab?srsltid=AYCX9vKws0Tfxd2WZVg3wzByyEXvublHizgKoxE0zN-APjLnRVxWA4FM | Use our lab locator to find a Quest Diagnostics or Labcorp near you. Enter your zip code to find a medical test center for routine outpatient blood work. |
| 5 | All Labs Today | https://www.baysidebusinessdirectory.org/businesses/all-labs-today | All Labs Today will offer a wide range of services, including on-site phlebotomy, and a full complement of testing menu such as routine and esoteric blood work. |
| 6 | All Labs Today (@alllabstoday) · Bradenton, FL | https://www.instagram.com/alllabstoday/ | At All Labs Today, we offer tests for cholesterol, blood sugar, and more to help you understand how stress might be affecting your health. Call us at (941) 280 ... |
| 7 | Outpatient Lab Program Information & Resources | https://www.hoag.org/outpatient-lab | At Hoag, the Department of Pathology and Laboratory Medicine provides laboratory testing services critical to high-quality care. |
| 8 | Alverno Laboratories | Illinois and Indiana | https://alvernolabs.com/ | Alverno Laboratories manages 32 hospital laboratories and provides laboratory services to two free standing emergency departments. Contact (800) 937-5521 |
| 9 | Lab Testing: Lab Access For ALL™ | https://www.labaccessforall.org/ | Lab Access For ALL™ makes it easy to get the lab work you need at the lab near you, at the comfort of your own home or in the setting that works best for you. |
| 10 | Laboratory Testing in Newport Beach 92663 | https://locations.labcorp.com/ca/newport-beach/51253/ | Need blood work or lab tests in Newport Beach, CA? Visit Labcorp for a wide range of services including labwork or drug testing. Options for online ordering ... |
Important pages
Pages earning the most estimated search traffic in the sample.
Website intelligence — Collected evidence
Prioritized website intelligence pages
| Type | Page | Words | Change | URL |
|---|---|---|---|---|
| trust | PortSwigger — Web security tools, training and research | 783 | new | https://portswigger.net/ |
| pricing | Burp AT pricing \ | static | 533 | new |
| pricing | Pricing - Burp Suite DAST | 560 | new | https://portswigger.net/burp/dast/pricing |
| features | Cybersecurity Solutions - PortSwigger. | 1,027 | new | https://portswigger.net/solutions |
| features | Automated DAST scanning without limits - with Burp Suite - PortSwigger | 707 | new | https://portswigger.net/solutions/attack-surface-visibility |
| features | Automated Web Application Security Testing - PortSwigger | 769 | new | https://portswigger.net/solutions/automated-security-testing |
| features | Bug Bounty Software - PortSwigger | 698 | new | https://portswigger.net/solutions/bug-bounty-hunting |
| features | CI-driven DAST scanning without limits - with Burp Suite - PortSwigger | 647 | new | https://portswigger.net/solutions/ci-driven-scanning |
| features | Cybersecurity Compliance Solutions - PortSwigger | 615 | new | https://portswigger.net/solutions/compliance |
| features | DevSecOps Software Solutions - PortSwigger | 662 | new | https://portswigger.net/solutions/devsecops |
| features | Penetration testing software - PortSwigger | 716 | new | https://portswigger.net/solutions/penetration-testing |
| features | Features - Burp Suite Enterprise Edition | 584 | new | https://portswigger.net/burp/dast/features |
| features | Features - Burp Suite Professional | 634 | new | https://portswigger.net/burp/pro/features |
| features | Bambdas - customize Burp Suite - PortSwigger | 663 | new | https://portswigger.net/burp/pro/features/bambdas |
| features | BChecks - Extending Burp Scanner | 818 | new | https://portswigger.net/burp/pro/features/bchecks |
Features
| Page type | Evidence | Source |
|---|---|---|
| features | My account | https://portswigger.net/solutions |
| features | Products Solutions Research Academy Support Company | https://portswigger.net/solutions |
| features | Customers About Blog Careers Legal Contact Resellers | https://portswigger.net/solutions |
| features | My account Customers About Blog Careers Legal Contact Resellers | https://portswigger.net/solutions |
| features | Burp AT Burp AT Agentic AI that extends human-led pentesting.Burp Suite DAST Burp Suite DAST The enterprise-enabled dynamic web vulnerability scanner. Burp Suite Professional Burp Suite Professional The world's #1 web penetration testing toolkit. Burp Suite Community Edition Burp Suite Community Edition The best manual tools to start web security testing. View all product editions | https://portswigger.net/solutions |
| features | Burp Scanner | https://portswigger.net/solutions |
| features | Burp Suite's web vulnerability scanner | https://portswigger.net/solutions |
| features | Attack surface visibility Improve security posture, prioritize manual testing, free up time. CI-driven scanning More proactive security - find and fix vulnerabilities earlier. Application security testing See how our software enables the world to secure the web. DevSecOps Catch critical bugs; ship more secure software, more quickly. Penetration testing Accelerate penetration testing - find more bugs, more quickly. Automated scanning Scale dynamic scanning. Reduce risk. Save time/money. Bug bounty hunting Level up your hacking and earn more bug bounties. Compliance Enhance security monitoring to comply with confidence. | https://portswigger.net/solutions |
| features | View all solutions | https://portswigger.net/solutions |
| features | Product comparison | https://portswigger.net/solutions |
| features | What's the difference between Pro and DAST? | https://portswigger.net/solutions |
| features | Support Center Get help and advice from our experts on all things Burp. Documentation Tutorials and guides for Burp Suite. Get Started - Professional Get started with Burp Suite Professional. Get Started - DAST Get started with Burp Suite DAST. Downloads Download the latest version of Burp Suite. | https://portswigger.net/solutions |
| features | Visit the Support Center | https://portswigger.net/solutions |
| features | Downloads | https://portswigger.net/solutions |
| features | Download the latest version of Burp Suite. | https://portswigger.net/solutions |
| features | PortSwigger enables the world to secure the web | https://portswigger.net/solutions |
| features | We provide software, training, and research, to those dedicated to keeping their organization safe | https://portswigger.net/solutions |
| features | Enterprise Cybersecurity Software | https://portswigger.net/solutions |
| features | Scan at scale, realize DevSecOps, and fully-integrate security into SDLCs. | https://portswigger.net/solutions |
| features | The enterprise-enabled web vulnerability scanner. | https://portswigger.net/solutions |
Pricing and plans
| Page type | Evidence | Source |
|---|---|---|
| pricing | Attack surface visibility Improve security posture, prioritize manual testing, free up time. CI-driven scanning More proactive security - find and fix vulnerabilities earlier. Application security testing See how our software enables the world to secure the web. DevSecOps Catch critical bugs; ship more secure software, more quickly. Penetration testing Accelerate penetration testing - find more bugs, more quickly. Automated scanning Scale dynamic scanning. Reduce risk. Save time/money. Bug bounty hunting Level up your hacking and earn more bug bounties. Compliance Enhance security monitoring to comply with confidence. | https://portswigger.net/burp/burp-at/pricing |
| pricing | Burp AT / Pricing | https://portswigger.net/burp/burp-at/pricing |
| pricing | Plan rollout across your organization | https://portswigger.net/burp/burp-at/pricing |
| pricing | Attack surface visibility Improve security posture, prioritize manual testing, free up time. CI-driven scanning More proactive security - find and fix vulnerabilities earlier. Application security testing See how our software enables the world to secure the web. DevSecOps Catch critical bugs; ship more secure software, more quickly. Penetration testing Accelerate penetration testing - find more bugs, more quickly. Automated scanning Scale dynamic scanning. Reduce risk. Save time/money. Bug bounty hunting Level up your hacking and earn more bug bounties. Compliance Enhance security monitoring to comply with confidence. | https://portswigger.net/burp/dast/pricing |
| pricing | Product OverviewRequest a demoBurp Suite EcosystemPricing | https://portswigger.net/burp/dast/pricing |
| pricing | - Request a demo- Pricing- Customer Stories- Explore Burp Suite DAST | https://portswigger.net/burp/dast/pricing |
Integrations and supported platforms
No supporting public-page evidence was collected for this category.
Product and company updates
No supporting public-page evidence was collected for this category.
Rank tracking
Persistent keyword baselines and position movement.
This analysis created the first position baseline at 2026-10-23T23:53:16.297Z. Movement appears after the next fresh analysis using the same location and language.
Features
Features and capabilities
Core functions and evidence-backed product capabilities.
| Capability | What it does |
|---|---|
| Automated DAST scanning | Scans web applications for vulnerabilities without limits, using over 160 scan checks S39 S42 S73. |
| Manual testing tools | Provides tools like Intruder, Repeater, and content discovery for hands-on testing S45 S128. |
| Burp Scanner | A web vulnerability scanner at the core, with capabilities like BChecks scripting to create custom scan checks S45 S139. |
| Agentic AI (Burp AT) | Extends human-led pentesting with AI that can be directed via natural language prompts inside tools like Repeater S1 S127. |
| JavaScript analysis | Includes a new experimental engine for static analysis of JavaScript code S149. |
| Attack surface visibility | Provides comprehensive dashboards and reporting for a clear overview of security posture S42. |
| BApp extensions | Over 250 community-developed extensions for customizing workflows S128 S1. |
| CI/CD integration | Integrates directly into CI pipelines for automated security scans with each build S68. |
Integrations and ecosystem
Connected products, exports, APIs, and workflow compatibility.
| Integration or interface | Type | What it enables |
|---|---|---|
| CI/CD pipelines | Integration | Automates security scans within existing build environments S68 S73. |
| BApp Store extensions | Extension framework | Adds over 250 community-built tools for specialized workflows S128 S1. |
| Burp Collaborator | Integration | Detects out-of-band interactions for OAST testing, with public or private servers S128. |
| BChecks scripting | Extension framework | Allows custom scan checks without developing full BApp extensions S139. |
| Burp AI natural language interface | AI interface | Lets users direct Burp AI within Repeater via prompts S127. |
| Platform plugins | Integration | Seamless integration with CI platform plugins S68. |
Pricing
Pricing and plans
Published plans, free access, trials, credits, and pricing limitations.
| Plan or offer | Verified price and billing | Included | Limits |
|---|---|---|---|
| Burp Suite Professional | $499, billing period not stated S1 | Manual testing tools with Burp Scanner S1 | Not published S1 |
| Burp Suite DAST | Contact sales, custom subscription S1 | Unlimited users S1 | Scanning by the hour or unlimited, self-hosted or cloud S1 |
| Burp Suite Community Edition | Free S1 | Manual testing tools S1 | Not published S1 |
| Burp AI | Free trial includes 10,000 free AI credits S127 | AI agentic capabilities S127 | Not published S127 |
Competition
Competitive landscape
Domains competing for the same organic search demand.
Sampled competitors
| Competitor | First-page appearances | Sampled queries | Average position | Queries observed |
|---|---|---|---|---|
| facebook.com | 4 | 2 | 4.3 | all labs, autorize |
| oed.com | 2 | 1 | 3.5 | autorize |
| yelp.com | 2 | 1 | 4 | all labs |
| anylabtestnow.com | 2 | 1 | 5 | all labs |
| walkinlab.com | 1 | 1 | 1 | all labs |
| kids.wordsmyth.net | 1 | 1 | 4 | autorize |
| store.directlabs.com | 1 | 1 | 6 | all labs |
| sapling.ai | 1 | 1 | 6 | autorize |
| alzlabs.org | 1 | 1 | 7 | all labs |
| manage.belizenic.bz | 1 | 1 | 7 | autorize |
Website intelligence — Collected evidence
Customers, testimonials, and first-party review claims
No supporting public-page evidence was collected for this category.
Independent review sources discovered
No links to supported independent review platforms were discovered on the collected pages.
Backlink profile
Authority and referring-domain signals.
Backlink comparison profile
- Domain rating: 85/100
- Backlinks: 343,879
- Referring domains: 19,743
- Dofollow backlinks: 84.0%
- Dofollow referring domains: 82.0%
Collection decision
The Scout search index remains intentionally excluded from automatic Scout analysis. This Scout traffic model profile costs 5 credits (0.5 cents) and is included in the first comparison run so its usefulness can be judged before the recurring collection is finalized.
AI visibility
Measured ChatGPT and Google AI mentions with cited sources.
AI-assistant referral traffic
- Estimated current generative-AI referral share: 4.2%
| Month | Traffic share | Source |
|---|---|---|
| — | — | All AI assistants |
| — | — | All AI assistants |
| — | — | All AI assistants |
Website intelligence — Collected evidence
Site-stated AI capabilities
| Page type | Evidence | Source |
|---|---|---|
| features | Burp AT Burp AT Agentic AI that extends human-led pentesting.Burp Suite DAST Burp Suite DAST The enterprise-enabled dynamic web vulnerability scanner. Burp Suite Professional Burp Suite Professional The world's #1 web penetration testing toolkit. Burp Suite Community Edition Burp Suite Community Edition The best manual tools to start web security testing. View all product editions | https://portswigger.net/solutions |
| features | Burp AT Burp AT Agentic AI that extends human-led pentesting.Burp Suite DAST Burp Suite DAST The enterprise-enabled dynamic web vulnerability scanner. Burp Suite Professional Burp Suite Professional The world's #1 web penetration testing toolkit. Burp Suite Community Edition Burp Suite Community Edition The best manual tools to start web security testing. View all product editions | https://portswigger.net/solutions/attack-surface-visibility |
| features | Burp AT Burp AT Agentic AI that extends human-led pentesting.Burp Suite DAST Burp Suite DAST The enterprise-enabled dynamic web vulnerability scanner. Burp Suite Professional Burp Suite Professional The world's #1 web penetration testing toolkit. Burp Suite Community Edition Burp Suite Community Edition The best manual tools to start web security testing. View all product editions | https://portswigger.net/solutions/automated-security-testing |
| features | Burp AT Burp AT Agentic AI that extends human-led pentesting.Burp Suite DAST Burp Suite DAST The enterprise-enabled dynamic web vulnerability scanner. Burp Suite Professional Burp Suite Professional The world's #1 web penetration testing toolkit. Burp Suite Community Edition Burp Suite Community Edition The best manual tools to start web security testing. View all product editions | https://portswigger.net/solutions/bug-bounty-hunting |
These are first-party product claims, not independent measurements of AI-search visibility.
Marketing opportunities
Actions calculated directly from the collected evidence.
| Opportunity | Recommended action | Evidence |
|---|---|---|
| Competitor gap | Review the sampled queries where facebook.com appears. | 4 first-page appearances across all labs, autorize |
Website intelligence — Collected evidence
Website evidence gaps
- integrations: no usable public page was collected; verify whether the site publishes this evidence.
- customers: no usable public page was collected; verify whether the site publishes this evidence.
- reviews: no usable public page was collected; verify whether the site publishes this evidence.
- changes: no usable public page was collected; verify whether the site publishes this evidence.
- identity: no usable public page was collected; verify whether the site publishes this evidence.
- technical: no usable public page was collected; verify whether the site publishes this evidence.
Trust and proof
Customers, proof, and reviews
Published proof, customer signals, and review evidence.
Independent reviews
| Platform | Page | How it was found | Note |
|---|---|---|---|
| G2 | Compare Burp Suite and Invicti (formerly Netsparker) | Grounded web search | Burp Suite(120)4.8 out of 5Burp Suite By PortSwigger Invicti (formerly Netsparker)(60)4.6 out of 5Invicti (formerly Netsparker) By Invicti Security ... Burp Suite Star Rating (120) 4.8 out of 5 Market Segments Mid-Market (40.5% of reviews) |
| Beagle Security Blog | Burp Suite review: Is it worth the investment? | Grounded web search | PortSwigger’s Burp Suite is one of the most widely used tools in web application security testing, especially among penetration testers, bug bounty hunters, and security researchers. For a lot of people working in AppSec, Burp is usually one of the first tools they learn and one they continue using for years. ... / G2 rating / Gartner rating / / --- / --- / / 4.8/5 (based on 128 reviews) / 4.6/5 (based on 310 reviews) / ... - Burp Suite gives testers a lot of control during security assessments. |
| PeerSpot | PortSwigger Burp Suite Professional reviews 2026 | Grounded web search | user interface. The pricing is deemed high, and there are performance issues, such as high CPU usage and slower scanning speeds. Users desire better documentation and more integration options across various platforms. |
| Gartner Peer Insights | Penetration Testing Tools Reviews and Ratings | Grounded web search | ### Burp Suite Professional By PortSwigger 4.7 (69 Ratings) customers choice 2024 OVERVIEWALTERNATIVES PortSwigger is a company that specializes in developing software tools used for security testing of web applications. The company's primary focus |
| G2 | Compare Acunetix by Invicti and Burp Suite Social Share Options | Grounded web search | response Burp Suite(120)4.8 out of 5Burp Suite By PortSwigger ... . Users say that the manual testing features in Burp Suite are more intuitive and user ... 's false positive rate of 6.6 is a concern, while |
| offensivelysecured.com | Review : Burp Suite Certified Practitioner (BSCP) / Offensively Secured | Grounded web search | ), it felt like a natural next step to go for PortSwigger’s Burp Suite ... However, I definitely underestimated the length of time it would take. What I initially ... to be 2 months of gruelling grind through an almost unbelievably comprehensive set of |
Customer proof
| Proof type | Named customer or source | Evidence |
|---|---|---|
| Case study | Håkon Lønmo | customer case study — I've also used it successfully for brute-forcing usernames or object references. (Case Studies - PortSwigger) |
Independent mentions
- Burp Suite / Which 50 — including an intercepting proxy to capture and modify HTTP/S requests, an automated vulnerability scanner, modules for manual testing such as ... and features for analyzing randomness and encoding. The suite supports project organization, customizable
- Burp - Web Application Security, Testing, & Scanning - PortSwigger — # What do you want to do? Hands-on web security testing Test, find, and exploit vulnerabilities faster with a complete suite of security testing tools. Best for pentesters and hands-on security professionals. Free up testing time with scalable,
- Burp Suite – Trackr.Live — plus a workbench of tools for tampering with HTTP by hand. PortSwigger built it in ... , with PortSwigger keeping control. That matters here only because vendor ownership is the thing that rots fastest in tool documentation, and the honest 2026 answer is
External links were grounded in one live web search. Search snippets are leads, not independently scraped page content; rejected links remain available in Review evidence.
Company, security, and trust
Ownership, policies, security signals, and public trust evidence.
| Signal | Finding | Source |
|---|---|---|
| Company and ownership | There's an outdated notion that securing your software is just a testing process that slows you down. But we see a new world, where security is an intrinsic part of all the products and services you deliver. Where web se | source |
| Contact and support | Not published on the collected pages. | — |
| Legal and privacy | In a future release, we may provide a UI similar to the active scan queue, containing a view of pending and current code analysis tasks, and enabling the user to pause, resume or cancel individual tasks. | source |
| Security and compliance | Burp AT Agentic AI that extends human-led pentesting. Burp Suite DAST The enterprise-enabled dynamic web vulnerability scanner. Burp Suite Professional The world's #1 web penetration testing toolkit. **Burp S | source |
| Uptime and status page | Not published on the collected pages. | — |
| Domain registered | 2001-09-09 | — |
| Domain expires | 2027-09-09 | — |
Not found on the collected pages: contact and support, uptime and status page. This only means Scout did not find it on the pages it read; it says nothing about the company itself.
Documentation and product updates
Help resources, product guidance, and visible changes over time.
| Resource or update | Type | What is available | Date or freshness |
|---|---|---|---|
| Burp Suite documentation - PortSwigger | Documentation | This documentation describes the functionality of all editions of Burp Suite and related components. Use the links below to get started: Burp Suite ... (source) | Not dated |
| 7 Burp Suite Professional-exclusive features to help you test smarter / Blog - PortSwigger | Roadmap | Public product roadmap. (source) | July 2022 |
| 7 Burp Suite Professional-exclusive features to help you test smarter / Blog - PortSwigger | Product update | Product update is publicly available. (source) | Not dated |
| 7 Burp Suite Professional-exclusive features to help you test smarter / Blog - PortSwigger | Guide | Public tutorials and product guidance. (source) | Not dated |
| 7 Burp Suite Professional-exclusive features to help you test smarter / Blog - PortSwigger | Changelog | Public product change history. (source) | Not dated |
Not found in the collected public sources: status page, separate help center or knowledge base.
Technical
Technical and delivery signals
Delivery model, platforms, API, data ownership, reliability claims and release activity.
| Signal | Finding | Source |
|---|---|---|
| Delivery model (cloud, self-hosted, desktop, browser extension) | Burp Suite DAST is available as self-hosted or PortSwigger cloud S1. | S1 |
| Platforms and apps | Burp Suite includes desktop applications for Professional and Community editions; the documentation covers all editions S20. | S20 |
| API and extensibility (API, SDK, webhooks, MCP, plugins) | Extensibility is provided through BApp extensions, BChecks scripting, and integration with CI/CD pipelines S128 S139 S68. | S128 S139 S68 |
| Data ownership and export | Not published on the collected pages. | — |
| Performance and reliability claims | Burp Scanner is "fine-tuned to understand complex application logic" for accurate and efficient detection S42. | S42 |
| Release activity | Documentation last updated October 22, 2026; recent blog posts announce new features (Burp AT, JS analysis) S20 S128 S149. | S20 S128 S149 |
Measured infrastructure
Domain, certificate, and hosting signals, measured directly.
| Signal | Finding |
|---|---|
| Domain registered | 2001-09-09 — Name.com, Inc. |
| Domain expires | 2027-09-09 |
| First archived | 2003-12-01 — web archive |
| TLS certificate | Amazon, valid, expires 2027-01-31 |
| Security headers | HSTS, CSP, X-Content-Type-Options, X-Frame-Options |
| Headers not served | Referrer-Policy |
| Server header | '; DELETE carlos FROM users -- |
| Mail handled by | aspmx.l.google.com, alt1.aspmx.l.google.com |
| Nameservers | ns-1337.awsdns-39.org, ns-194.awsdns-24.com |
Technical site audit
A bounded multi-page crawl with page-level issues and URLs.
Scout — Bounded technical crawl
- Pages crawled: 15 of 15 maximum
- Technical health: 98/100
- Critical issues: 0
- Warnings: 4
- Notices: 6
Issues
Crawled pages
| Status | Title | H1s | Words | Response | URL |
|---|---|---|---|---|---|
| 200 | PortSwigger — Web security tools, training and research | 1 | 753 | 22 ms | https://portswigger.net/ |
| 200 | Log in \ | portswigger.net | 1 | 38 | 487 ms |
| 200 | Web Security Research Papers - PortSwigger Research | 0 | 524 | 255 ms | https://portswigger.net/research |
| 200 | Web Security Academy: Free Online Training from PortSwigger | 1 | 1100 | 30 ms | https://portswigger.net/web-security |
| 200 | Case Studies - PortSwigger | 1 | 1183 | 395 ms | https://portswigger.net/customers |
| 200 | About us - PortSwigger | 1 | 869 | 273 ms | https://portswigger.net/about |
| 200 | Web Security Blog - PortSwigger | 1 | 461 | 201 ms | https://portswigger.net/blog |
| 200 | Careers — PortSwigger | 1 | 819 | 488 ms | https://portswigger.net/careers/ |
| 200 | Legal information - PortSwigger | 1 | 459 | 151 ms | https://portswigger.net/legal |
| 200 | Contact us - PortSwigger | 1 | 452 | 523 ms | https://portswigger.net/about/contact |
| 200 | Reseller Resource Center - PortSwigger | 1 | 1145 | 631 ms | https://portswigger.net/support/reseller-faqs |
| 200 | Burp AT \ | PortSwigger | 1 | 1769 | 250 ms |
| 200 | Burp Suite DAST \ | PortSwigger | 1 | 2433 | 492 ms |
| 200 | Burp Suite Professional - PortSwigger | 0 | 889 | 132 ms | https://portswigger.net/burp/pro |
| 200 | Download Burp Suite Community Edition - PortSwigger | 1 | 611 | 511 ms | https://portswigger.net/burp/communitydownload |
This is a bounded Scout crawl. Core Web Vitals and Lighthouse scores are not claimed unless a dedicated performance audit is connected.
Search Console and Analytics
First-party search and behavioral data connection state.
Modeled acquisition channels
| Channel | Estimated share |
|---|---|
| direct | 39.3% |
| search | 41.7% |
| search organic | 41.5% |
| search paid | 0.1% |
| social | 7.6% |
| social organic | 7.4% |
| social paid | 0.2% |
| referrals | 5.5% |
| paid referrals | 0.1% |
| 1.7% | |
| gen ai | 4.2% |
| affiliate | 0.0% |
| other | 0.0% |
First-party connections
| Integration | Status | Data available after connection |
|---|---|---|
| Google Search Console | Not connected | Clicks, impressions, CTR, average position, queries, pages, countries, and devices |
| Google Analytics | Not connected | Organic sessions, engagement, landing pages, conversions, geography, and devices |
No first-party Search Console or Analytics numbers are shown until the site owner authorizes the corresponding Google account. Scout traffic model values above are modeled estimates, not private analytics totals.
Limits and method
Limitations and open questions
Known constraints and missing evidence from the collected pages.
Collected pages mention no direct competitors. Gaps in evidence include: no specific pricing for Burp Suite Professional billing period; no details on security compliance certifications (e.g., SOC 2, ISO); no up-to-date customer count beyond 16,000 organizations; no independent review ratings; no details on data ownership for cloud deployments; and no explicit performance metrics or uptime figures.
Sources, method, and limitations
Evidence inventory, collection method, provider use, and constraints.
This report is based on 15 pages collected from portswigger.net on 2026-10-23, including product pages, solution pages, blog posts, and official pricing data. The collection used static and browser rendering rendering; external proof search was not used for verification. The report covers product capabilities, pricing, integrations, and customer testimonials as published. Limitations include lack of independent review data and incomplete information on legal, security, and compliance matters.
- Official Websitehttps://portswigger.net/burpVerified
- Official Websitehttps://portswigger.net/aboutVerified
- Documentationhttps://portswigger.net/burp/documentationVerified
- Official Websitehttps://portswigger.net/solutionsVerified
- Official Websitehttps://portswigger.net/blog/7-burp-suite-professional-exclusive-features-to-help-you-test-smarterVerified
- Official Websitehttps://portswigger.net/blog/bchecks-houston-we-have-a-solutionVerified
- Official Websitehttps://portswigger.net/blog/burp-ai-takes-on-a-vulnerable-web-app-watch-tib3rius-put-burps-new-agentic-capabilities-to-the-testVerified
- Official Websitehttps://portswigger.net/blog/burp-gets-new-javascript-analysis-capabilitiesVerified
- Official Websitehttps://portswigger.net/solutions/attack-surface-visibilityVerified
- Official Websitehttps://portswigger.net/solutions/automated-security-testingVerified
- Official Websitehttps://portswigger.net/solutions/bug-bounty-huntingVerified
- Official Websitehttps://portswigger.net/solutions/ci-driven-scanningVerified
- Official Websitehttps://portswigger.net/solutions/complianceVerified
- Official Websitehttps://portswigger.net/solutions/devsecopsVerified
- Official Websitehttps://portswigger.net/solutions/penetration-testingVerified
- Review Sitehttps://www.g2.com/compare/burp-suite-vs-invicti-formerly-netsparkerVerified
- Review Sitehttps://beaglesecurity.com/blog/article/burp-suite-review.htmlVerified
- Review Sitehttps://www.peerspot.com/products/portswigger-burp-suite-professional-reviewsVerified
- Review Sitehttps://www.gartner.com/reviews/market/penetration-testing-toolsVerified
- Articlehttps://portswigger.net/customersVerified
- Review Sitehttps://www.g2.com/compare/acunetix-by-invicti-vs-burp-suiteVerified
- Articlehttps://which-50.com/app/portswigger.net-burp/Verified
- Review Sitehttps://offensivelysecured.com/posts/review-burp-suite-certified-practitioner/Verified
- Articlehttps://www.trackr.live/scans/burp-suite/Verified