In simple English
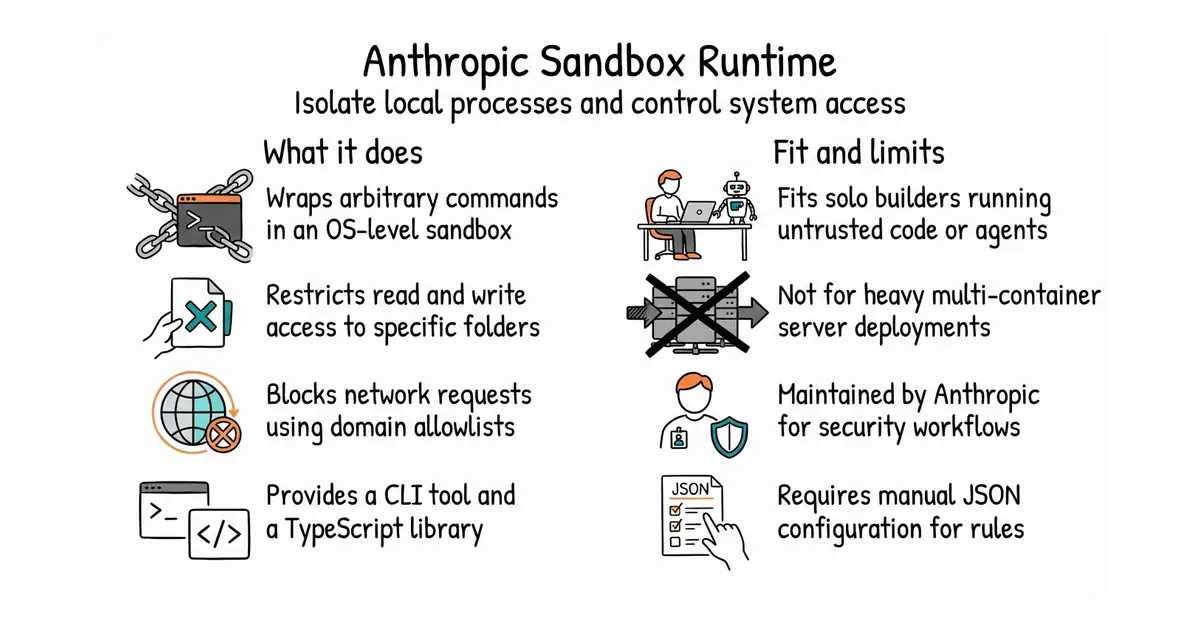
When you run third-party code or coding agents, you risk giving them free access to your entire computer. This tool wraps any program in a lightweight security fence at the operating system level. It stops unauthorized programs from reading your password files or sending your data to unknown servers. You configure simple allowlists for folders and web domains. It runs on macOS, Linux, and Windows without needing heavy containers.
What it is
Anthropic Sandbox Runtime is a command-line tool and TypeScript library that enforces strict filesystem and network boundaries on local processes. It uses native operating system features like sandbox-exec on macOS and bubblewrap on Linux to isolate execution trees.
What it is good for
Solo builders want to safely run untrusted coding agents, helper scripts, or command-line tools without risking data leaks or accidental damage to their project files.
- Enforces security restrictions at the operating system level without containers.
- Controls exact read and write access for specific folders and files.
- Blocks unauthorized network requests by domain name and network port.
- Setup requires configuring JSON settings files and command wrappers.
- Network proxy filtering can occasionally break complex SSL connections or local development tools.
- Requires Node.js or Bun installed on the host machine.
Running untrusted scripts directly in your local terminal without any isolation
Claude Code
- containers/bubblewrap9.2k stars
A low-level unprivileged sandboxing tool for Linux that forms the basis of many container runtimes.

- smallstep/certificates9.0k stars
A certificate authority you run yourself, for machines the public internet cannot reach.
- michelp/pgsodium614 stars
A PostgreSQL extension that brings libsodium's encryption functions into SQL, with a root key the database cannot read back.
- pgaudit/pgaudit1.7k stars
A PostgreSQL extension that records what was done to the database, in the database's own log.
npm install -g @anthropic-ai/sandbox-runtime