Overview
Summary
The useful answer before the supporting detail.
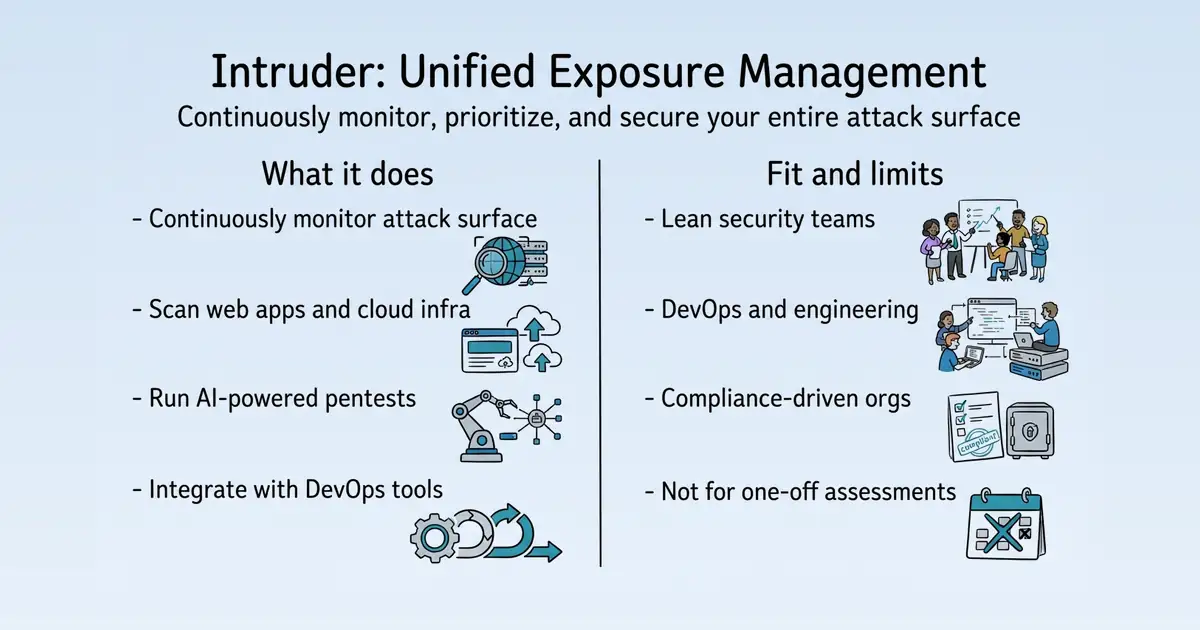
Intruder is a unified exposure management platform that combines attack surface monitoring, cloud security, vulnerability management, and AI pentesting for lean security teams S68. Founded in 2015, it solves the information overload crisis in vulnerability management by prioritizing what matters and reducing noise S1. Its practical value is continuous, proactive security coverage that helps teams remediate faster and stay compliant S68.
Product identity and positioning
Name, category, positioning, audience, and first-party claims.
- Identity: Intruder is a unified exposure management platform from Intruder.io S68.
- Core purpose: It helps organizations reduce cyber attack exposure by focusing on critical issues and filtering out noise S1.
- Intended users: Lean security and IT teams needing efficient vulnerability management S1.
- Product scope: A single platform for AI pentesting, attack surface monitoring, cloud security, and vulnerability management S68.
- Positioning: The vendor positions it as "effortless cyber security" with proactive exposure management S1.
- Claimed distinction: Its AI pentesting agents are built and trained by CREST-certified pentesters S14.
Use cases and audiences
Who the product serves and the jobs it is designed to handle.
| Audience | Practical use case |
|---|---|
| Lean security teams | Continuously monitor attack surface and remediate critical vulnerabilities with automated triage S1 S68. |
| DevOps teams | Integrate security scanning into CI/CD pipelines via API and issue trackers S8 S68. |
| Compliance managers | Generate evidence reports for SOC 2, ISO 27001, and HIPAA via automated scanning S130 |
| Cloud engineering teams | Agentless scanning across AWS, Azure, and GCP to catch misconfigurations and exposed secrets S68. |
| Development teams | Use AI pentesting on code repos to test on every release and get pentest reports within hours S14. |
Traffic and search
SEO analysis
Collected Oct 23, 2026intruder.io: an estimated 77,320 total monthly visits and about 49,241 monthly organic visits across 2,653 ranking keywords. Scout crawled 15 pages and measured a technical health score of 98/100.
Search summary
The useful answer before the supporting detail.
Unified, always-on exposure management for lean security teams. A single platform for vulnerability management, attack surface monitoring and cloud security. intruder.io: an estimated 77,320 total monthly visits and about 49,241 monthly organic visits across 2,653 ranking keywords. Scout crawled 15 pages and measured a technical health score of 98/100.
- Total traffic (modeled): 77,320 monthly visits across all channels.
- Organic search traffic (estimated): 49,241 monthly visits from search.
- Strongest sampled ranking: external penetration testing at position 2.
- Leading page in the collected evidence: https://www.intruder.io/use-cases/external-vulnerability-scanning.
- Closest measured organic competitor: reddit.com, appearing 4 times in the sampled first-page SERPs.
- Technical crawl: 15 pages, health score 98/100.
Website intelligence — Collected evidence
Company identity and positioning
| Page type | Evidence | Source |
|---|---|---|
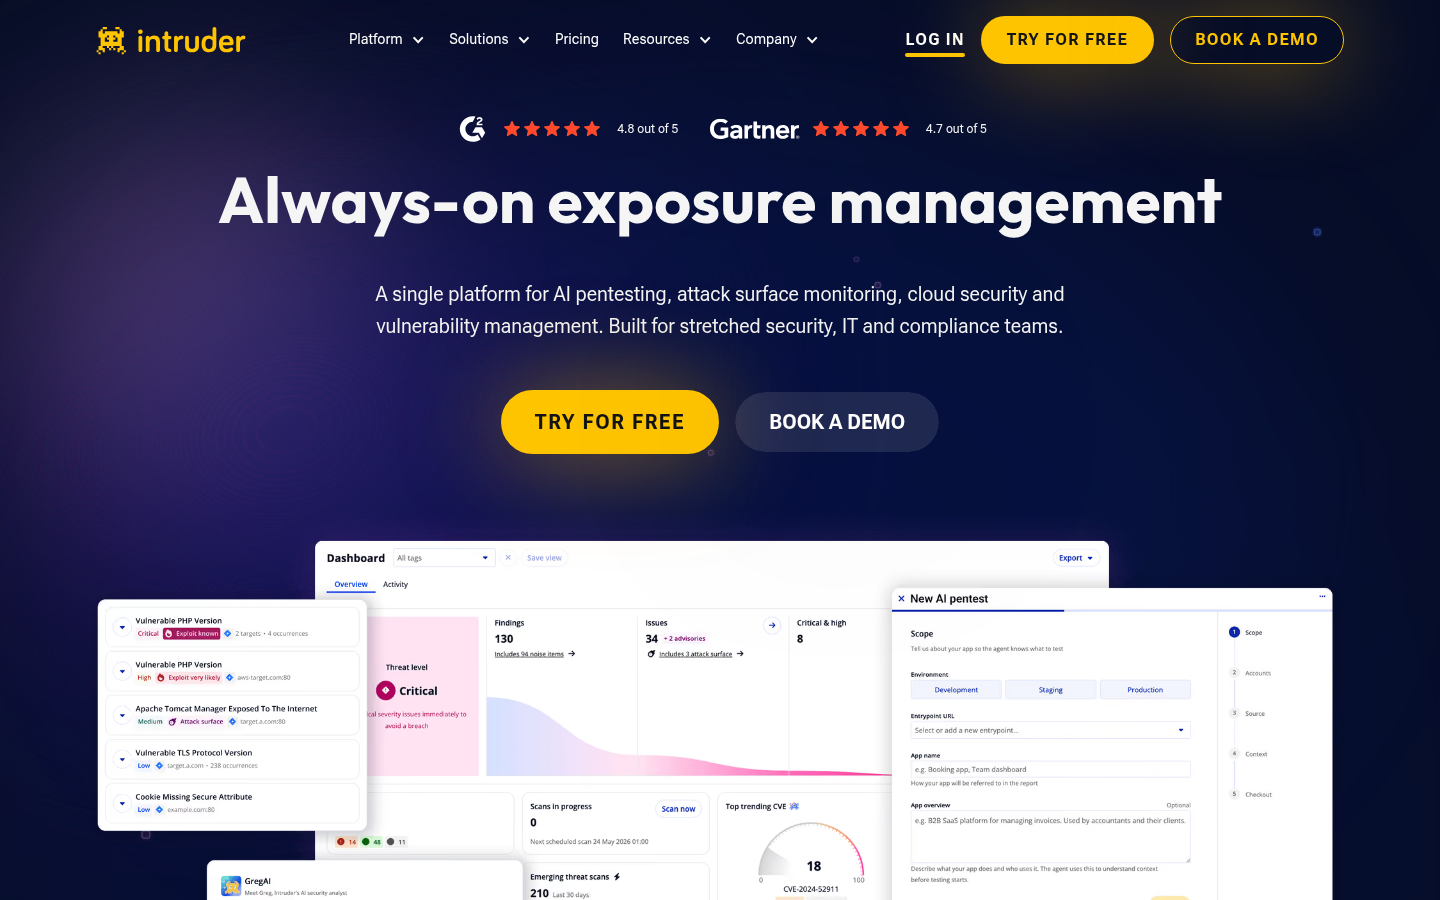
| other | Unified, always-on exposure management for lean security teams. A single platform for vulnerability management, attack surface monitoring and cloud security. Start your free trial today. | https://www.intruder.io/ |
| other | Try for free | https://www.intruder.io/ |
| other | A single platform for AI pentesting, attack surface monitoring, cloud security and vulnerability management. Built for stretched security, IT and compliance teams. | https://www.intruder.io/ |
| other | Perimeters change constantly as new ports open and cloud services spin up. Real-time change detection automatically scans new assets for vulnerabilities, delivering a complete view of every exposed service, technology and port. Detect shadow IT and remove what doesn't need to be exposed. | https://www.intruder.io/ |
| other | Annual pentests are misaligned to the realities of modern software development. Same day AI pentesting lets you pentest on-demand as your code base and risk profile shifts. Our AI agents are finding complex multi-step vulnerabilities that have evaded best in class human pentesters for years. Connect your code repos, scope and launch in minutes, get a compliance ready pentest report in a few hours. | https://www.intruder.io/ |
| other | Continuous scanning across your entire digital estate including infrastructure, apps and cloud environments in a single platform. Emerging threat scans run within hours of new critical vulnerabilities going public, issues are prioritized by real-world exploit likelihood, and clear remediation advice helps stretched teams fix what matters, fast. | https://www.intruder.io/ |
| other | Continuous dynamic application security testing (DAST) for web apps, single-page apps and underlying infrastructure, including authenticated scanning behind login pages. A ZAP-powered scanner runs over 75 application checks for injection flaws, misconfigurations and zero-days, integrates with CI/CD pipelines through GitHub, GitLab, Jira and Azure DevOps, and prioritizes results with remediation advice. | https://www.intruder.io/ |
| other | Continuously scan for vulnerabilities, misconfigs and attack surface issues. | https://www.intruder.io/ |
| other | Start for free | https://www.intruder.io/ |
| other | ](/platform/ai-security-analyst) | https://www.intruder.io/ |
| other | ](/platform/integrations) | https://www.intruder.io/ |
| other | Our customers love Intruder | https://www.intruder.io/ |
Domain performance
Modeled total traffic, six-month trend, engagement, countries, and domain identity.
Total website traffic
| Month | Modeled visits |
|---|---|
| 2026-04 | 91,067 |
| 2026-05 | 99,516 |
| 2026-06 | 85,442 |
| 2026-07 | 93,894 |
| 2026-08 | 73,670 |
| 2026-09 | 77,320 |
Top visitor countries
| Country | Name | Traffic share |
|---|---|---|
| GB | United Kingdom | 24.1% |
| US | United States | 16.9% |
| SA | Saudi Arabia | 4.3% |
| IN | India | 3.9% |
| RU | Russia | 3.5% |
Domain identity
| Signal | Value |
|---|---|
| Registered | Nov 5, 2014 |
| Last changed | Oct 11, 2026 |
| Expires | Nov 5, 2027 |
| WHOIS server | whois.nic.io |
| DNSSEC | — |
| Nameservers | elliot.ns.cloudflare.com, chloe.ns.cloudflare.com |
Website capture
Organic keywords
Top keywords and an independent Google result page.
Top organic keywords
| Keyword | Volume | CPC | Estimated value |
|---|---|---|---|
| owasp zap | 36,810 | $3.78 | $1,200 |
| burp suite | 83,940 | $1.71 | $970 |
| intruder | 16,820 | $4.87 | $460 |
| pen test tools for windows | 0 | $0.00 | $190 |
| intruder is big comapny? | 160 | $0.00 | $150 |
Independent Google result page
Query: external penetration testing
| Position | Title | URL | Description |
|---|---|---|---|
| 1 | What is an External Penetration Test? | https://www.vikingcloud.com/blog/what-is-an-external-penetration-test | External pen testing is designed to mimic typical hacking strategies used by cybercriminals. Therefore, the strategies used are highly accurate ... |
| 2 | What is an external pentest and how is it carried out? | https://www.intruder.io/blog/what-is-an-external-pentest | External penetration testing usually tests from the perspective of an attacker with no prior access to your systems or networks. This is ... |
| 3 | External Vs Internal Penetration Testing | https://purplesec.us/learn/external-vs-internal-network-penetration-tests/ | External penetration testing consists of testing vulnerabilities to review the chances of being attacked by any remote attacker. By exploiting the found ... |
| 4 | External Pentest for a Newbie | https://www.reddit.com/r/Pentesting/comments/1dvbjli/external_pentest_for_a_newbie/ | When an employer won't share IP ranges or domain names while asking for an external penetration test, that's dangerous, and frankly suspicious. |
| 5 | Internal vs External Penetration Testing: Key Differences ... | https://www.mitnicksecurity.com/blog/internal-vs-external-penetration-testing | What Is External Penetration Testing? External penetration testing evaluates how an outside attacker might compromise your internet-facing systems. It simulates ... |
| 6 | External Penetration Testing Methodology | https://medium.com/r3d-buck3t/external-penetration-testing-methodology-8ea5a69a9e68 | An external penetration test is a security assessment that simulates an attack on an organization's systems and defenses from the internet. The ... |
| 7 | External Penetration Test | 10-D Security Audit | https://10dsecurity.com/external-penetration-test.html | Our External Penetration Test Simulates A Real-World Cyberattack On Your Institution That Challenges Your Teams Monitoring & Alert Controls. Learn More! |
| 8 | External Network - Penetration Testing | https://www.netspi.com/netspi-ptaas/network-penetration-testing/external-network/ | Improve your external network security and meet compliance requirements with NetSPI's network penetration testing. Accurate results and actionable ... |
| 9 | External Network Penetration Testing | https://www.schellman.com/services/penetration-testing/external-network | An external network penetration test from Schellman simulates a real attack to identify vulnerabilities in your network infrastructure before attackers do. |
Important pages
Pages earning the most estimated search traffic in the sample.
Website intelligence — Collected evidence
Prioritized website intelligence pages
| Type | Page | Words | Change | URL |
|---|---|---|---|---|
| other | Intruder \ | static | 870 | new |
| pricing | AI Pentests - Pricing | 335 | new | https://www.intruder.io/pentest-pricing |
| pricing | Intruder Pricing \ | static | 1,066 | new |
| features | AI Pentesting | 231 | new | https://www.intruder.io/platform/ai-pentesting |
| features | GregAI: Your AI Security Analyst for Faster Security Workflows | 206 | new | https://www.intruder.io/platform/ai-security-analyst |
| features | Attack Surface Management Platform \ | static | 709 | new |
| features | Cloud Security Platform \ | static | 470 | new |
| features | Integration partners | 158 | new | https://www.intruder.io/platform/integrations |
| features | Continuous Vulnerability Management for Lean Security Teams | 257 | new | https://www.intruder.io/platform/vulnerability-management |
| features | OWASP Top 10 Scanner Online \ | static | 751 | new |
| features | SQL Injection Scanner Online \ | static | 993 | new |
| features | XSS Scanner Online \ | static | 898 | new |
| integrations | All you need to know about API security | 1,888 | new | https://www.intruder.io/blog/api-security |
| integrations | Intruder + Drata Integration \ | static | 387 | new |
| integrations | We found 28,000 .git repos sitting wide open. Here's what was inside | 1,930 | new | https://www.intruder.io/research/api-keys-bank-details-disciplinary-files-what-28-000-exposed-git-repos-gave-up |
Features
| Page type | Evidence | Source |
|---|---|---|
| features | Intruder logo | https://www.intruder.io/platform/ai-pentesting |
| features | ](https://accounts.intruder.io/login)[ | https://www.intruder.io/platform/ai-pentesting |
| features | Try for free | https://www.intruder.io/platform/ai-pentesting |
| features | ](https://portal.intruder.io/free_trial)[ | https://www.intruder.io/platform/ai-pentesting |
| features | ](/get-demo) | https://www.intruder.io/platform/ai-pentesting |
| features | Web app pentesting, on-demand | https://www.intruder.io/platform/ai-pentesting |
| features | Your annual pentest is expensive, slow and out of date the moment it's signed off. No lead time AI pentests find issues manual pentests miss and ensure security keeps up with every deploy. | https://www.intruder.io/platform/ai-pentesting |
| features | Sample Report | https://www.intruder.io/platform/ai-pentesting |
| features | ](/pentest-pricing) | https://www.intruder.io/platform/ai-pentesting |
| features | Launch pentest | https://www.intruder.io/platform/ai-pentesting |
| features | ](https://portal.intruder.io/free_trial) | https://www.intruder.io/platform/ai-pentesting |
| features | Thousands of happy customers worldwide | https://www.intruder.io/platform/ai-pentesting |
| features | Catch what your pentester has been missing | https://www.intruder.io/platform/ai-pentesting |
| features | Built and trained by our CREST-certified pentesters and operating with full code awareness, our pentesting agents surface issues that have been evading manual pentesters for years. Customers have uncovered broken authorization controls, IDORs, payment flaws that let a user move money they shouldn't, and a race condition with financial impact. | https://www.intruder.io/platform/ai-pentesting |
| features | See it in action | https://www.intruder.io/platform/ai-pentesting |
| features | Audit-ready reporting in hours, not months | https://www.intruder.io/platform/ai-pentesting |
| features | Connect your code repository via GitHub or GitLab, provide any context and credentials and launch a scan in minutes. Get a comprehensive pentest report within hours that can be used as evidence for security compliance frameworks including SOC 2 and ISO 27001. | https://www.intruder.io/platform/ai-pentesting |
| features | GET STARTED FOR FREE | https://www.intruder.io/platform/ai-pentesting |
| features | Streamline validation and remediation with issue level pentests | https://www.intruder.io/platform/ai-pentesting |
| features | Automate the triage and investigation of your issue backlog and eliminate false positives with micro pentesting investigations that go deep on specific findings surfaced by Intruder. | https://www.intruder.io/platform/ai-pentesting |
Pricing and plans
| Page type | Evidence | Source |
|---|---|---|
| pricing | Try for free | https://www.intruder.io/pentest-pricing |
| pricing | Platform subscribers pay | https://www.intruder.io/pentest-pricing |
| pricing | Pentests must be used within 1 year of purchase. | https://www.intruder.io/pentest-pricing |
| pricing | Test on every release instead of once a year. Scoped to your apps and deployment cycles | https://www.intruder.io/pentest-pricing |
| pricing | Securing a global AI platform requires continuous defense. While Yembo continues to leverage human pentesters, annual assessments alone leave dangerous windows of exposure. Intruder’s AI pentesting bridges that gap by delivering human-grade depth at machine speed to keep our platform permanently hardened. | https://www.intruder.io/pentest-pricing |
| pricing | Try for free | https://www.intruder.io/pricing |
| pricing | Security that works for the 99%. Pricing that does too. | https://www.intruder.io/pricing |
| pricing | Starting from $3,500 / test | https://www.intruder.io/pricing |
| pricing | see pentest pricing | https://www.intruder.io/pricing |
| pricing | ](/pentest-pricing) | https://www.intruder.io/pricing |
| pricing | annual (save 20%) | https://www.intruder.io/pricing |
| pricing | START FREE TRIAL | https://www.intruder.io/pricing |
| pricing | 14-DAY FREE TRIAL | https://www.intruder.io/pricing |
| pricing | All Free features + | https://www.intruder.io/pricing |
| pricing | Plan license details | https://www.intruder.io/pricing |
| pricing | Multi-year discount | https://www.intruder.io/pricing |
| pricing | What's included in the free trial? | https://www.intruder.io/pricing |
| pricing | Our free trial includes all the features of the Cloud plan, along with 5 free licenses which allow you to scan your systems and carry out authenticated web application scans. You can scan 5 targets as many times as you like during the 14 days. If you need more than 5, no problem - just get in touch! | https://www.intruder.io/pricing |
| pricing | On both annual and monthly plans, increases are pro-rated, and any decreases are credited to your account, up until the next billing period. | https://www.intruder.io/pricing |
| pricing | How is your pricing calculated? | https://www.intruder.io/pricing |
Integrations and supported platforms
| Page type | Evidence | Source |
|---|---|---|
| integrations | Intruder logo | https://www.intruder.io/blog/api-security |
| integrations | ](https://accounts.intruder.io/login)[ | https://www.intruder.io/blog/api-security |
| integrations | Try for free | https://www.intruder.io/blog/api-security |
| integrations | ](https://portal.intruder.io/free_trial)[ | https://www.intruder.io/blog/api-security |
| integrations | ](/get-demo) | https://www.intruder.io/blog/api-security |
| integrations | [.svg) | https://www.intruder.io/blog/api-security |
| integrations | Back to Blog | https://www.intruder.io/blog/api-security |
| integrations | All you need to know about API security | https://www.intruder.io/blog/api-security |
| integrations | James Harrison | https://www.intruder.io/blog/api-security |
| integrations | Senior Content Writer | https://www.intruder.io/blog/api-security |
| integrations | ](/author/james-harrison-3) | https://www.intruder.io/blog/api-security |
| integrations | April 25, 2025 | https://www.intruder.io/blog/api-security |
| integrations | March 8, 2023 | https://www.intruder.io/blog/api-security |
| integrations | Application security | https://www.intruder.io/blog/api-security |
| integrations | ](/blog-categories/application-security) | https://www.intruder.io/blog/api-security |
| integrations | [](#)[](#)[](#) | https://www.intruder.io/blog/api-security |
| integrations | ](/author/james-harrison-3) | https://www.intruder.io/blog/api-security |
| integrations | APIs are certainly not new, but now they’re all around us. Every time you use a rideshare app like Uber, send a Monzo mobile payment, change your Hive thermostat from your phone, or check your iPhone weather app, you’re using an API. | https://www.intruder.io/blog/api-security |
| integrations | And securing them has never been more important as they’re a goldmine for personal information for social engineering. In this article, we’ll look at how APIs work and how to use tools like Intruder to monitor and protect your APIs. | https://www.intruder.io/blog/api-security |
| integrations | What are web APIs? | https://www.intruder.io/blog/api-security |
Product and company updates
No supporting public-page evidence was collected for this category.
Rank tracking
Persistent keyword baselines and position movement.
This analysis created the first position baseline at 2026-10-23T23:52:20.596Z. Movement appears after the next fresh analysis using the same location and language.
Features
Features and capabilities
Core functions and evidence-backed product capabilities.
| Capability | What it does |
|---|---|
| Attack Surface Monitoring | Continuously monitors ports, services, and cloud infrastructure for new vulnerabilities and misconfigurations S68. |
| Cloud Security | Agentless scanning across AWS, Azure, and Google Cloud to catch misconfigurations, exposed secrets, and vulnerabilities S68. |
| Web App Scanning | Automated DAST scans for XSS and 75+ other vulnerabilities in web apps and APIs, including authenticated scanning behind login pages S8 S68. |
| AI Pentesting | AI agents connect to code repos (GitHub/GitLab) to launch pentests and produce compliance-ready reports in hours S14. |
| Vulnerability Management | Streamlines vulnerability management, tracks remediation time, and provides actionable prioritization S8. |
Integrations and ecosystem
Connected products, exports, APIs, and workflow compatibility.
| Integration or interface | Type | What it enables |
|---|---|---|
| AWS | Integration | Automatically includes internet-exposed AWS systems as scan targets S12. |
| Jira, GitHub, Azure DevOps | Integration | Exports security weaknesses to issue trackers and integrates with CI/CD pipelines S8 S68. |
| Slack, Teams, email | Integration | Sends critical vulnerability alerts and notifications S8 S12. |
| Vanta | Integration | Automatically sends compliance evidence for audits S12. |
| API | API | Integrates with CI/CD pipelines and custom workflows S8. |
| GitHub, GitLab, Bitbucket | Integration | Connects code repositories for AI pentesting scans S114 S14. |
Pricing
Pricing and plans
Published plans, free access, trials, credits, and pricing limitations.
| Plan or offer | Verified price and billing | Included | Limits |
|---|---|---|---|
| Free | $0 free forever | 5 infrastructure targets, 1 cloud account, 2 container images | 1 scheduled scan per month, ports 80/443, no web apps S114 |
| Cloud | $239/month monthly, or $2,870/year | 5 infrastructure targets, unlimited scans | Web app/API testing, 3 cloud accounts, daily container scans S114 |
| Pro | $399/month monthly, or $4,790/year | 5 infrastructure targets, unlimited scans | Internal agent scanning, 10 cloud accounts, top 50 ports S114 |
| Enterprise | Custom, not published | Unlimited scans, all ports, unlimited cloud accounts | Shadow IT discovery S114 |
| AI Pentest | Starting from $3,500 per test S117 | Must be used within 1 year of purchase S114 | Not established |
Competition
Competitive landscape
Domains competing for the same organic search demand.
Sampled competitors
| Competitor | First-page appearances | Sampled queries | Average position | Queries observed |
|---|---|---|---|---|
| reddit.com | 4 | 2 | 4.5 | external penetration testing, external vulnerability scanner |
| vikingcloud.com | 1 | 1 | 1 | external penetration testing |
| openvas.org | 1 | 1 | 1 | external vulnerability scanner |
| purplesec.us | 1 | 1 | 3 | external penetration testing |
| gartner.com | 1 | 1 | 4 | external vulnerability scanner |
| bishopfox.com | 1 | 1 | 5 | external penetration testing |
| mitnicksecurity.com | 1 | 1 | 6 | external penetration testing |
| charlesit.com | 1 | 1 | 6 | external vulnerability scanner |
| medium.com | 1 | 1 | 7 | external penetration testing |
| 10dsecurity.com | 1 | 1 | 8 | external penetration testing |
Website intelligence — Collected evidence
Customers, testimonials, and first-party review claims
No supporting public-page evidence was collected for this category.
Independent review sources discovered
No links to supported independent review platforms were discovered on the collected pages.
Backlink profile
Authority and referring-domain signals.
Backlink comparison profile
- Domain rating: 73/100
- Backlinks: 35,782
- Referring domains: 3,640
- Dofollow backlinks: 39.0%
- Dofollow referring domains: 63.0%
| Source DR | Source title | Anchor | Source URL | Target URL |
|---|---|---|---|---|
| 89 | Microsoft: Recent Windows updates may trigger Remote Desktop failures | Pentest your web apps on-demand. Find what humans miss. Scope and launch a pentest in minutes. Pentest your web apps on-demand. Find what humans miss. Scope and launch a pentest in minutes. | https://www.bleepingcomputer.com/news/security/microsoft-recent-windows-updates-may-trigger-remote-desktop-failures/ | https://www.intruder.io/pentest-pricing |
| 91 | Vulnerability Scanning Tools \ | OWASP Foundation | Intruder | https://community.owasp.org/Vulnerability_Scanning_Tools |
| 74 | 10 Best Penetration Testing Tools Reviewed in 2026 | Intruder | https://thectoclub.com/tools/best-penetration-testing-tools/ | https://www.intruder.io/automated-penetration-testing |
| 92 | How to Check a Website for Viruses: 6 Methods | Intruder | https://www.hostinger.com/ng/tutorials/how-to-check-a-website-for-viruses/ | https://www.intruder.io/ |
| 75 | Top 10 Best Dynamic Application Security Testing (DAST) Platforms in 2026 | Intruder Official Website | https://gbhackers.com/best-dynamic-application-security-testing-dast-platforms/ | https://www.intruder.io/ |
| 40 | Advantis Credit \ | DVLA | Protected by Intruder logo | https://www.advantiscredit.co.uk/dvla/ |
| 30 | Top 10 Cyber Security Services Provider (2026) » InfoMSP | intruder Cyber Security | https://infomsp.com/top-10-cyber-security-services-provider/ | https://www.intruder.io/ |
| 36 | Best Penetration Testing Tools in 2026: 16 Picks by Type | Intruder | https://www.complyjet.com/blog/best-penetration-testing-tools | https://www.intruder.io/ |
| 55 | Top 10 SaaS Security Companies for Data Protection | Intruder | https://www.strac.io/blog/saas-security-companies | https://www.intruder.io/ |
| 7 | Free Vulnerability Scanner for Windows, macOS, and Linux \ | TridentStack | Intruder: pricing and plan features | https://tridentstack.com/free-vulnerability-scanning |
Collection decision
The Scout search index remains intentionally excluded from automatic Scout analysis. This Scout traffic model profile costs 5 credits (0.5 cents) and is included in the first comparison run so its usefulness can be judged before the recurring collection is finalized.
AI visibility
Measured ChatGPT and Google AI mentions with cited sources.
AI-assistant referral traffic
- Estimated current generative-AI referral share: 1.3%
| Month | Traffic share | Source |
|---|---|---|
| — | — | All AI assistants |
Website intelligence — Collected evidence
Site-stated AI capabilities
| Page type | Evidence | Source |
|---|---|---|
| other | A single platform for AI pentesting, attack surface monitoring, cloud security and vulnerability management. Built for stretched security, IT and compliance teams. | https://www.intruder.io/ |
| other | Annual pentests are misaligned to the realities of modern software development. Same day AI pentesting lets you pentest on-demand as your code base and risk profile shifts. Our AI agents are finding complex multi-step vulnerabilities that have evaded best in class human pentesters for years. Connect your code repos, scope and launch in minutes, get a compliance ready pentest report in a few hours. | https://www.intruder.io/ |
| other | ](/platform/ai-security-analyst) | https://www.intruder.io/ |
| features | Your annual pentest is expensive, slow and out of date the moment it's signed off. No lead time AI pentests find issues manual pentests miss and ensure security keeps up with every deploy. | https://www.intruder.io/platform/ai-pentesting |
| features | Try AI pentesting today | https://www.intruder.io/platform/ai-pentesting |
| features | Work through vulnerability backlogs faster with your AI security analyst. | https://www.intruder.io/platform/ai-security-analyst |
| features | Connect Intruder to your own AI models | https://www.intruder.io/platform/ai-security-analyst |
| features | The Intruder MCP server enables you to connect Intruder to AI agents (like Claude) and manage critical security workflows through simple, natural language prompts. | https://www.intruder.io/platform/ai-security-analyst |
| pricing | Securing a global AI platform requires continuous defense. While Yembo continues to leverage human pentesters, annual assessments alone leave dangerous windows of exposure. Intruder’s AI pentesting bridges that gap by delivering human-grade depth at machine speed to keep our platform permanently hardened. | https://www.intruder.io/pentest-pricing |
These are first-party product claims, not independent measurements of AI-search visibility.
Marketing opportunities
Actions calculated directly from the collected evidence.
| Opportunity | Recommended action | Evidence |
|---|---|---|
| Competitor gap | Review the sampled queries where reddit.com appears. | 4 first-page appearances across external penetration testing, external vulnerability scanner |
Website intelligence — Collected evidence
Website evidence gaps
- customers: no usable public page was collected; verify whether the site publishes this evidence.
- reviews: no usable public page was collected; verify whether the site publishes this evidence.
- changes: no usable public page was collected; verify whether the site publishes this evidence.
- identity: no usable public page was collected; verify whether the site publishes this evidence.
- technical: no usable public page was collected; verify whether the site publishes this evidence.
Trust and proof
Customers, proof, and reviews
Published proof, customer signals, and review evidence.
Independent reviews
| Platform | Page | How it was found | Note |
|---|---|---|---|
| G2 | Compare Intruder and Tenable Nessus | Grounded web search | Intruder(171)4.8 out of 5Intruder By Intruder ... It was incredibly easy to get started and evaluate the tool which provided immediate value for our team. The ease of pointing the application to some endpoints and triggering the initial scan didn't |
| TrustRadius | Great scanner for networks of any size! / TrustRadius | Grounded web search | ### Use Cases and Deployment Scope We use Intruder to scan for external vulnerabilities across the various fleets of servers. #### Pros - Auto scanning. - New vulnerability detection. - Alert levels. #### Cons - Reports could contain more detail. |
| Beagle Security | Intruder review: Is it right for your team? | Grounded web search | This article is based entirely on publicly available sources. We aggregated user reviews from G2, Capterra, and similar trusted sources, drew on discussions from Reddit communities, and reviewed vendor documentation and feature pages. Rather than proprietary testing, our evaluation reflects the collective experience of security practitioners who have shared their insights publicly. ... / G2 rating / Gartner rating / / --- / --- / / 4.8/5 (based on 217 reviews) / 4.7/5 (based on 140 reviews) / |
| ToolRadar | Intruder Reviews, Pricing & Alternatives (2026) | Grounded web search | ## Ratings Across the Web 4.8(219 reviews) Intruder holds an aggregate rating of 4.8 out of 5 from 219 reviews across G2, last checked September 17, 2026. G2 219 reviews 4.8/5 Ratings aggregated from independent review platforms. Learn more |
| trustradius.com | Use Cases of Intruder 2025 | Grounded web search | Recommendations Users of Intruder commonly recommend giving the free trial a try for quick and easy vulnerability scanning ... helpful explanations of the tool. Additionally, users advise considering upgrading to a service tier |
| G2 | Intruder - AI Marketplace / G2 | Grounded web search | driven penetration testing, attack surface monitoring, cloud security, and vulnerability management. Targeted at security, IT ... teams, Intruder helps organizations scan for vulnerabilities, prioritize and remediate security risks, monitor multi-cloud |
| beaglesecurity.com | Intruder pricing 2026: Is it worth it? | Grounded web search | user reviews from G2, Capterra, and similar trusted sources, drew on discussions from Reddit communities, and reviewed vendor documentation and feature pages. Rather than proprietary testing, our evaluation reflects the collective experience of security |
Customer proof
| Proof type | Named customer or source | Evidence |
|---|---|---|
| Case study | Brainlabs, Litmus, Ravelin, Yembo | customer case study — Intruder B2B Case Studies & Customer Successes ... (Intruder B2B Case Studies & Customer Successes) |
| Case study | furza.co.uk | customer case study — Furza ran a comprehensive recruitment campaign for Intruder, generating over 1000 applications and running a 20-person assessment day of high calibre, eager junior sales talent. (Case Study: Intruder) |
Independent mentions
- Intruder / Stop Breaches Before They Start — It’s continuous, and it pretty much slaps you round the face if there’s an issue. If something hits the news, I know Intruder's already crawling our sites and confirming there’s no risk. ... I appreciate Intruder for its intuitive interface, effective
External links were grounded in one live web search. Search snippets are leads, not independently scraped page content; rejected links remain available in Review evidence.
Company, security, and trust
Ownership, policies, security signals, and public trust evidence.
| Signal | Finding | Source |
|---|---|---|
| Company and ownership | Intruder was founded in 2015 to help solve the information overload crisis in vulnerability management. Having worked both as an ethical hacker for tier one companies, and for blue teams defending critical national infra | source |
| Contact and support | Not published on the collected pages. | — |
| Legal and privacy | If your auditor rejects the report, we refund the test in full - no questions, no fine print. | source |
| Security and compliance | SOC 2, ISO, HIPAA, DORA | source |
| Uptime and status page | Not published on the collected pages. | — |
Not found on the collected pages: contact and support, uptime and status page. This only means Scout did not find it on the pages it read; it says nothing about the company itself.
Documentation and product updates
Help resources, product guidance, and visible changes over time.
| Resource or update | Type | What is available | Date or freshness |
|---|---|---|---|
| Expanding Our Pricing Plans: A Design Story of Heroes, Villains, and “Gregomon” | Product update | Product update is publicly available. (source) | September 2026 |
Not found in the collected public sources: public roadmap, changelog or release notes, status page, separate help center or knowledge base.
Technical
Technical and delivery signals
Delivery model, platforms, API, data ownership, reliability claims and release activity.
| Signal | Finding | Source |
|---|---|---|
| Delivery model (cloud, self-hosted, desktop, browser extension) | Cloud-based web platform S68. | S68 |
| Platforms and apps | Web application S68. | S68 |
| API and extensibility (API, SDK, webhooks, MCP, plugins) | Provides an API for CI/CD integration S8. | S8 |
| Data ownership and export | Export security weaknesses to Jira, GitHub, Azure DevOps S8. | S8 |
| Performance and reliability claims | 24/7 automatic scanning for new threats S8. | S8 |
| Release activity | Monthly product updates published S118. | S118 |
Measured infrastructure
Domain, certificate, and hosting signals, measured directly.
| Signal | Finding |
|---|---|
| First archived | 2015-07-11 — web archive |
| TLS certificate | Google Trust Services, valid, expires 2026-12-13 |
| Security headers | HSTS |
| Headers not served | CSP, X-Content-Type-Options, X-Frame-Options, Referrer-Policy |
| Server header | cloudflare |
| Mail handled by | intruder-io.mail.protection.outlook.com |
| Nameservers | elliot.ns.cloudflare.com, chloe.ns.cloudflare.com |
Not measurable: rdap: no RDAP server published for .io; rdap: exceeded the overall budget; wayback: exceeded the overall budget; tls: exceeded the overall budget; dns: exceeded the overall budget; headers: exceeded the overall budget. A gap here means the lookup was unavailable, not that the finding is negative.
Technical site audit
A bounded multi-page crawl with page-level issues and URLs.
Scout — Bounded technical crawl
- Pages crawled: 15 of 15 maximum
- Technical health: 98/100
- Critical issues: 0
- Warnings: 6
- Notices: 3
Issues
| Severity | Issue | Value | Affected URL |
|---|---|---|---|
| notice | Meta description length should be reviewed | 186 | https://www.intruder.io/ |
| notice | Meta description length should be reviewed | 186 | https://www.intruder.io/ |
| notice | Meta description length should be reviewed | 172 | https://www.intruder.io/platform/ai-pentesting |
| warning | Missing meta description | — | https://www.intruder.io/platform/integrations |
| warning | Title length should be reviewed | 74 | https://www.intruder.io/use-cases/asset-discovery |
| warning | Duplicate title in audit sample | 2 | https://www.intruder.io/ |
| warning | Duplicate title in audit sample | 2 | https://www.intruder.io/ |
| warning | Duplicate meta description in audit sample | 2 | https://www.intruder.io/ |
| warning | Duplicate meta description in audit sample | 2 | https://www.intruder.io/ |
Crawled pages
| Status | Title | H1s | Words | Response | URL |
|---|---|---|---|---|---|
| 200 | Intruder \ | Stop Breaches Before They Start | 1 | 1481 | 53 ms |
| 200 | Intruder \ | Stop Breaches Before They Start | 1 | 1481 | 63 ms |
| 200 | AI Pentesting | 1 | 540 | 26 ms | https://www.intruder.io/platform/ai-pentesting |
| 200 | Cloud Security Platform \ | Get Started For Free | 1 | 783 | 48 ms |
| 200 | Attack Surface Management Platform \ | Intruder | 1 | 1231 | 51 ms |
| 200 | GregAI: Your AI Security Analyst for Faster Security Workflows | 1 | 529 | 28 ms | https://www.intruder.io/platform/ai-security-analyst |
| 200 | Continuous Vulnerability Management for Lean Security Teams | 1 | 575 | 54 ms | https://www.intruder.io/platform/vulnerability-management |
| 200 | Integration partners | 1 | 805 | 24 ms | https://www.intruder.io/platform/integrations |
| 200 | External Vulnerability Scanning \ | Try For Free | 1 | 1233 | 31 ms |
| 200 | Continuous Attack Surface Monitoring \ | Find Exposures Fast | 1 | 557 | 52 ms |
| 200 | Web Application Vulnerability Scanner \ | Try for free | 1 | 1229 | 22 ms |
| 200 | Website Vulnerability Scanner \ | Get started for free | 1 | 1146 | 43 ms |
| 200 | Risk-Based Vulnerability Management \ | Prioritize Real Threats | 1 | 536 | 57 ms |
| 200 | API Scanner - Full Coverage API Security Tool - Try for Free | 1 | 1075 | 58 ms | https://www.intruder.io/use-cases/api-security |
| 200 | Attack Surface Discovery \ | Automatically Discover & Protect Unknown Assets | 1 | 1111 | 55 ms |
This is a bounded Scout crawl. Core Web Vitals and Lighthouse scores are not claimed unless a dedicated performance audit is connected.
Search Console and Analytics
First-party search and behavioral data connection state.
Modeled acquisition channels
| Channel | Estimated share |
|---|---|
| direct | 36.3% |
| search | 48.5% |
| search organic | 23.7% |
| search paid | 24.9% |
| social | 6.2% |
| social organic | 3.6% |
| social paid | 2.5% |
| referrals | 6.5% |
| paid referrals | 0.3% |
| 0.9% | |
| gen ai | 1.3% |
| affiliate | 0.0% |
| other | 0.0% |
First-party connections
| Integration | Status | Data available after connection |
|---|---|---|
| Google Search Console | Not connected | Clicks, impressions, CTR, average position, queries, pages, countries, and devices |
| Google Analytics | Not connected | Organic sessions, engagement, landing pages, conversions, geography, and devices |
No first-party Search Console or Analytics numbers are shown until the site owner authorizes the corresponding Google account. Scout traffic model values above are modeled estimates, not private analytics totals.
Limits and method
Limitations and open questions
Known constraints and missing evidence from the collected pages.
Supported limitations and evidence gaps from collected pages: The collected pages do not provide detailed legal, privacy, or uptime information. Specific customer outcomes and independent reviews beyond G2 rating are not verified. Integration list is not exhaustive; some integrations like Cloudflare, Microsoft Sentinel, Okta and Drata are mentioned in blog posts but not detailed on the integrations page S118. Competitor comparisons are not discussed on the collected pages.
Sources, method, and limitations
Evidence inventory, collection method, provider use, and constraints.
This report is based on 15 collected pages from intruder.io, including product, pricing, about, blog, and integration pages. Evidence was gathered via static and rendered page requests. External proof search was performed but snippets were not used as verified facts. Pricing data was confirmed via the pricing page as authoritative. Some claims (e.g., G2 ratings) are from Intruder's own pages and may not be independently verified.
- Official Websitehttps://www.intruder.io/Verified
- Official Websitehttps://www.intruder.io/about-usVerified
- Official Websitehttps://www.intruder.io/product/xss-scannerVerified
- Official Websitehttps://www.intruder.io/platform/integrationsVerified
- Official Websitehttps://www.intruder.io/platform/ai-pentestingVerified
- Official Websitehttps://www.intruder.io/glossary/what-is-cweVerified
- Pricing Pagehttps://www.intruder.io/pentest-pricingVerified
- Pricing Pagehttps://www.intruder.io/pricingVerified
- Pricing Pagehttps://www.intruder.io/blog/expanding-our-pricing-plans-a-design-story-of-villains-heroes-and-gregomonVerified
- Pricing Pagehttps://www.intruder.io/blog/introducing-our-free-plan--making-security-accessible-for-the-99Verified
- Official Websitehttps://www.intruder.io/solution-templateVerified
- Official Websitehttps://www.intruder.io/blog-categories/productVerified
- Official Websitehttps://www.intruder.io/blog/product-update-continuous-network-scanningVerified
- Official Websitehttps://www.intruder.io/blog/validate-and-remediate-faster-with-in-platform-commentingVerified
- Official Websitehttps://www.intruder.io/blog/whats-new-product-updates-from-intruder-april-2024Verified
- Review Sitehttps://www.g2.com/compare/intruder-vs-tenable-nessusVerified
- Review Sitehttps://www.trustradius.com/reviews/intruder-2022-02-06-13-32-17Verified
- Review Sitehttps://beaglesecurity.com/blog/article/intruder-review.htmlVerified
- Review Sitehttps://toolradar.com/tools/intruderVerified
- Articlehttps://www.casestudies.com/company/intruderVerified
- Articlehttps://furza.co.uk/resources/intruder-case-studyVerified
- Review Sitehttps://www.trustradius.com/products/intruder/reviews?qs=product-usageVerified
- Review Sitehttps://ai.g2.com/marketplace/tools/intruderVerified
- Review Sitehttps://beaglesecurity.com/blog/article/intruder-pricing.htmlVerified