Radar check
What we found when we opened it. Every bar is one fact, with its date.
Last code pushed 25 Oct 2026, the same day before this check.
Latest release v1.32.0 on 22 Oct 2026.
Public since December 2024, a little over 1 year.
3,236 stars and 283 forks.
662 commits and 36 new issues in the last 90 days.
241 contributors. 68 pull requests merged in 90 days.
A security policy says how to report a problem. No published security advisories.
How the bars are scored
- Alive. Days since the last code push: a week or less 100, a month 90, three months 70, six months 50, a year 30, eighteen months 15, older 0.
- Releases. Age of the latest GitHub release, on a similar scale; no bar when the project publishes no releases.
- Maturity. Age of the project: eight years 100, five 90, three 70, two 55, one 40, six months 25, younger 10.
- Adoption. Stars on a log scale: 100,000 stars is 100, 10,000 is 80, 1,000 is 60, 100 is 40.
- Activity. Commits in the last 90 days: 300 or more 100, 100 85, 30 65, 10 45, any 25.
- Community. People who have contributed: 100 or more 100, 30 80, 10 60, 5 40, 2 25, one 10.
- Security. A published security policy 80, none 40; published advisories are listed, not scored.
Checked by Repo Radar on 26 Oct 2026 from the repository on GitHub.
In simple English
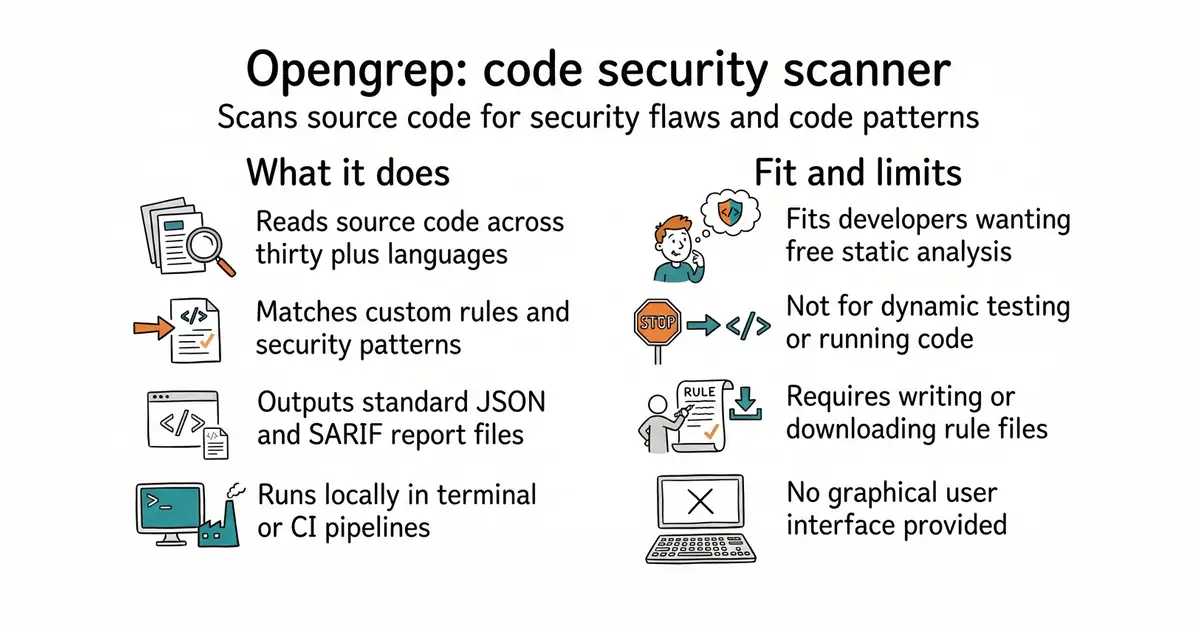
This tool reads your source code and checks it against rules to find security bugs. It spots problems before your users ever see them. It runs on your computer or inside your continuous integration server. It costs nothing to use and works with your existing rule files. You need to write or download rules to tell it what to look for.
What it is
Opengrep is a command-line utility (a program you run from your terminal by typing text commands) and a static analysis engine (software that inspects code for errors without running it). It was created as an open-source fork of Semgrep to keep advanced code analysis free.
What it is good for
Solo builders and small teams who want to scan their codebase for dangerous patterns, bugs, or security vulnerabilities before pushing code to production.
- Compatible with existing Semgrep rules so you do not have to rewrite your checks.
- Supports over thirty programming languages including Python, JavaScript, Rust, and Go.
- Provides standard JSON and SARIF (Static Analysis Results Interchange Format, a standard way for tools to report software bugs) outputs for easy integration.
- Requires you to write or find rule files before it can detect meaningful application-specific issues.
- Command-line tool with no built-in graphical interface for managing rules or viewing results.
- LGPL-2.1 licence places specific legal conditions on redistributing modified versions of the library.
Semgrep commercial tiers
GitHub Actions
- semgrep/semgrep17k stars
The original security analysis engine that Opengrep forked from to maintain open-source access.
- github/codeql10k stars
A powerful semantic code analysis engine by GitHub that queries code as data to find vulnerabilities.


- goauthentik/authentik26k stars
One place for people to sign in, which every other tool can ask instead of keeping its own passwords.
- cossacklabs/themis2.0k stars
Four ready-made encryption jobs with the choices already made, in fifteen languages.
- smallstep/certificates9.0k stars
A certificate authority you run yourself, for machines the public internet cannot reach.
curl -fsSL https://raw.githubusercontent.com/opengrep/opengrep/main/install.sh | bash