Radar check
What we found when we opened it. Every bar is one fact, with its date.
Last code pushed 23 Oct 2026, 2 days before this check.
No releases published on GitHub; the code date above is the one to trust.
Public since June 2026, 4 months.
1 stars and 0 forks.
29 commits and 0 new issues in the last 90 days.
3 contributors. 6 pull requests merged in 90 days. A small team carries it.
A security policy says how to report a problem. No published security advisories.
How the bars are scored
- Alive. Days since the last code push: a week or less 100, a month 90, three months 70, six months 50, a year 30, eighteen months 15, older 0.
- Releases. Age of the latest GitHub release, on a similar scale; no bar when the project publishes no releases.
- Maturity. Age of the project: eight years 100, five 90, three 70, two 55, one 40, six months 25, younger 10.
- Adoption. Stars on a log scale: 100,000 stars is 100, 10,000 is 80, 1,000 is 60, 100 is 40.
- Activity. Commits in the last 90 days: 300 or more 100, 100 85, 30 65, 10 45, any 25.
- Community. People who have contributed: 100 or more 100, 30 80, 10 60, 5 40, 2 25, one 10.
- Security. A published security policy 80, none 40; published advisories are listed, not scored.
Checked by Repo Radar on 26 Oct 2026 from the repository on GitHub.
In simple English
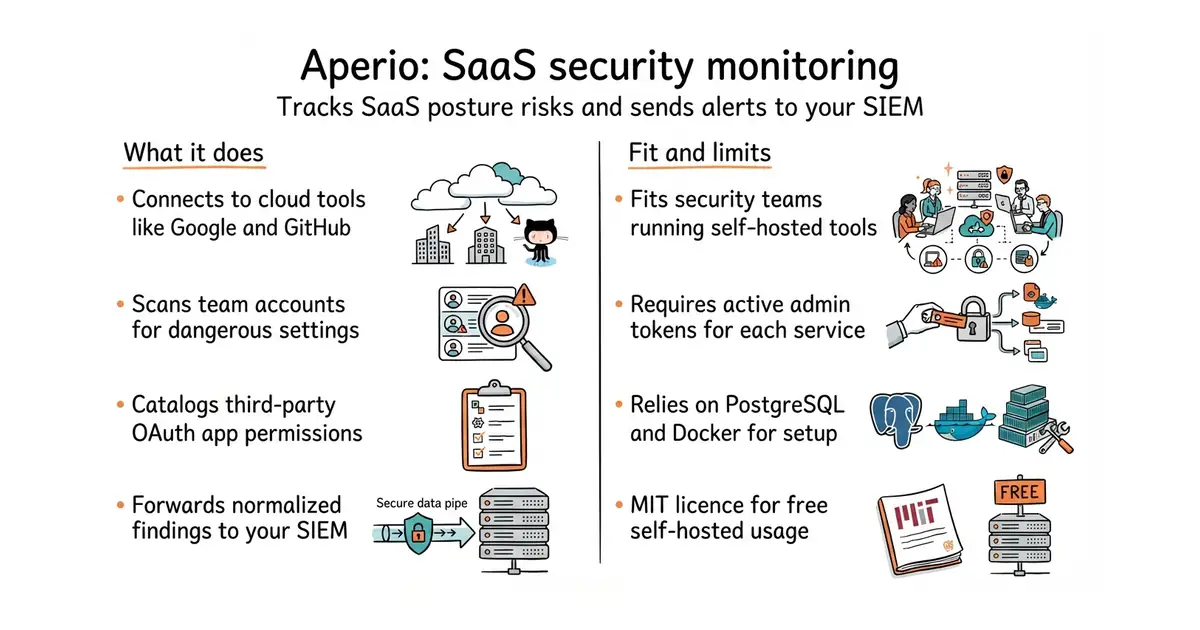
This tool checks your company accounts on cloud services like Google Workspace, GitHub, and Slack for security risks. It tracks what third-party programs your team has connected and alerts you to dangers like missing two-factor authentication. It sends all security warnings directly to your company log management system. You run this software on your own server using Docker. It is free to use under an MIT licence.
What it is
Aperio is an open-source SaaS Security Posture Management platform written in Go and TypeScript. It features a Next.js web dashboard, a Prisma database layer, background workers, and built-in SIEM dispatchers.
What it is good for
Security engineers and system administrators who need to audit cloud tool settings and third-party OAuth access permissions across an organization without paying for a commercial monitoring service.
- Connects directly to major platforms including Google Workspace, GitHub, Slack, and Microsoft 365.
- Sends security events to multiple SIEM destinations like Splunk, Datadog, and Elasticsearch.
- Includes human-gated approval steps before executing automated fixes.
- Requires running both Go processes and Node.js services alongside a PostgreSQL database.
- Needs valid administrator API tokens and OAuth client keys for each cloud service you want to monitor.
- Early-stage project with limited rule packs for several supported connector integrations.
manual security audits and expensive enterprise cloud posture tools
PostgreSQL
- prowler-cloud/prowler15k stars
An open-source security assessment tool for cloud environments, but focused heavily on infrastructure rather than SaaS apps.
- lacework/go-sdk40 stars
Commercial cloud security platforms that track posture risks, though usually run as managed services.


- goauthentik/authentik26k stars
One place for people to sign in, which every other tool can ask instead of keeping its own passwords.
- cossacklabs/themis2.0k stars
Four ready-made encryption jobs with the choices already made, in fifteen languages.
- smallstep/certificates9.0k stars
A certificate authority you run yourself, for machines the public internet cannot reach.
git clone https://github.com/writer/Aperio.git
cd Aperio
make setup
make dev