Overview
Summary
The useful answer before the supporting detail.
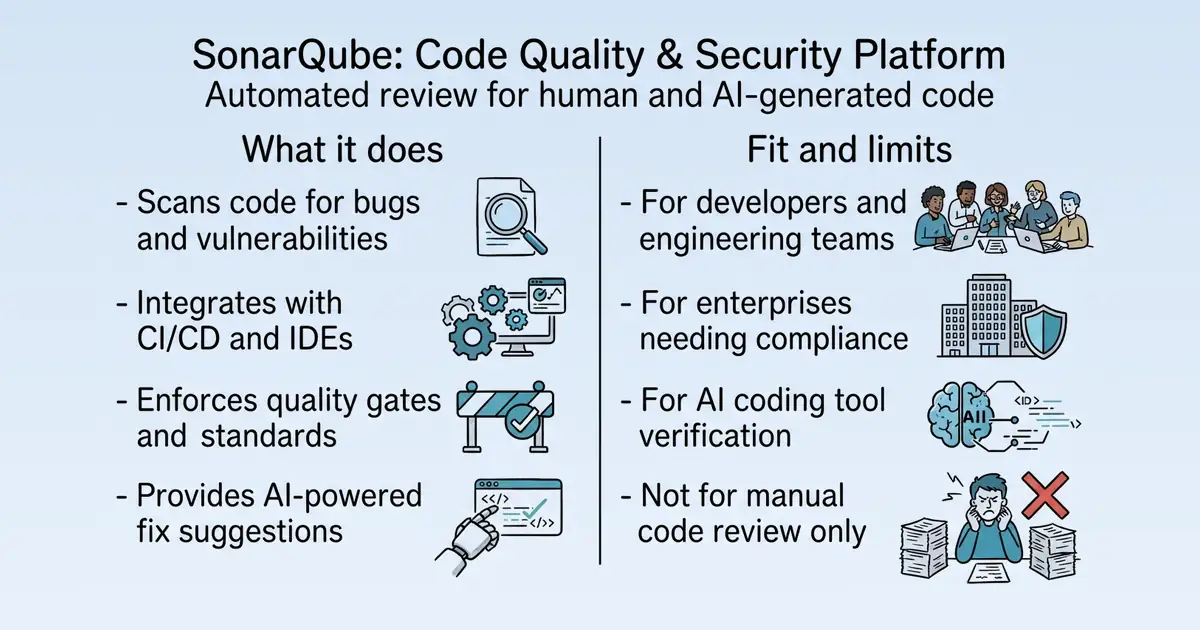
SonarQube is an automated code quality and security analysis platform that helps developers and organizations detect bugs, vulnerabilities, and code smells early in the development process S13. It is used by developers, enterprise organizations, and AI coding tools to ensure code reliability and security S1. The platform provides continuous review, monitoring, and improvement of codebases, with integrations for IDEs, CI/CD pipelines, and cloud or on-premises deployments S13. Its main practical value is enabling teams to enforce quality gates and security standards across their entire development workflow S13.
Product identity and positioning
Name, category, positioning, audience, and first-party claims.
- Identity: SonarQube is an industry-leading platform for automated code quality and security analysis S13.
- Core purpose: It solves the problem of detecting bugs, vulnerabilities, and code smells early in the development process S13.
- Intended users: Developers, enterprise organizations, and AI coding tools S1.
- Product scope: A platform that integrates into development environments and CI/CD processes for static analysis S13.
- Positioning: Sonar provides automated code review and deterministic verification to ensure AI-generated code meets reliability and security standards S1.
- Claimed distinction: Trusted by over 7 million developers and 75% of the Fortune 100 S1.
Use cases and audiences
Who the product serves and the jobs it is designed to handle.
| Audience | Practical use case |
|---|---|
| Developers | Get immediate feedback in IDE and CI/CD to fix issues as code is written S13. |
| Enterprise organizations | Enforce regulatory standards and corporate security policies with centralized oversight S1. |
| AI coding tools | Verify AI-generated code meets reliability and security standards S1. |
| Engineering leaders | Monitor risk, track compliance, and ensure coding standards with aggregated data S1. |
Traffic and search
SEO analysis
Collected Oct 26, 2026sonarsource.com: an estimated 546,743 total monthly visits and about 68,281 monthly organic visits across 7,985 ranking keywords. Scout crawled 15 pages and measured a technical health score of 98/100.
Search summary
The useful answer before the supporting detail.
Enforce consistent quality gates across every pull request and pipeline, from IDE to CI/CD, with automated code review for bugs and security issues. sonarsource.com: an estimated 546,743 total monthly visits and about 68,281 monthly organic visits across 7,985 ranking keywords. Scout crawled 15 pages and measured a technical health score of 98/100.
- Total traffic (modeled): 546,743 monthly visits across all channels.
- Organic search traffic (estimated): 68,281 monthly visits from search.
- Strongest sampled ranking: define sonarqube at position 1.
- Leading page in the collected evidence: https://www.sonarsource.com/products/sonarqube/.
- Closest measured organic competitor: medium.com, appearing 2 times in the sampled first-page SERPs.
- Technical crawl: 15 pages, health score 98/100.
Website intelligence — Collected evidence
Company identity and positioning
| Page type | Evidence | Source |
|---|---|---|
| reviews | Enforce consistent quality gates across every pull request and pipeline, from IDE to CI/CD, with automated code review for bugs and security issues. | https://www.sonarsource.com/ |
| features | Adds deeper comprehensive security coverage for dependencies | https://www.sonarsource.com/product-demos/ |
| features | These cookies are necessary for our websites to function and cannot be switched off in our systems. They are usually only set in response to actions made by you which amount to a request for services, such as setting your privacy preferences, logging in, or filling in forms. You can also set your browser to block or alert you about these cookies, but please note that some parts of the websites will not then work. These cookies do not store any personally identifiable information. | https://www.sonarsource.com/product-demos/ |
| features | These cookies allow us to count visits and traffic sources to measure and improve the performance of our websites. They help us to know which pages are the most and least popular and see how visitors move around the websites. If you do not allow these cookies, we will not know when you have visited our websites and will not monitor their performance. All information these cookies collect is aggregated and anonymous. | https://www.sonarsource.com/product-demos/ |
| features | SOLUTION BRIEFS | https://www.sonarsource.com/resources/solution-briefs/ |
| features | SOLUTION BRIEF | https://www.sonarsource.com/resources/solution-briefs/ |
| features | ](/resources/solution-briefs/leading-healthcare-organizations-use-sonarqube/)[ | https://www.sonarsource.com/resources/solution-briefs/ |
| features | ](/resources/solution-briefs/strengthen-your-misra-c-codebase-compliance-with-sonarqube/)[ | https://www.sonarsource.com/resources/solution-briefs/ |
| features | The Cyber Resilience Act (CRA) mandates that organizations deliver secure-by-design software, holding manufacturers legally responsible for vulnerabilities in their products. | https://www.sonarsource.com/resources/solution-briefs/ |
| features | ](/resources/solution-briefs/streamline-your-codebase-compliance-with-cra-using-sonarqube/)[ | https://www.sonarsource.com/resources/solution-briefs/ |
| features | The Digital Operational Resilience Act (DORA) mandates a unified framework for managing ICT risk, requiring financial entities to build resilience into their systems from the ground up. | https://www.sonarsource.com/resources/solution-briefs/ |
| features | ](/resources/solution-briefs/strengthen-your-codebase-compliance-with-dora-using-sonarqube/)[ | https://www.sonarsource.com/resources/solution-briefs/ |
Domain performance
Modeled total traffic, six-month trend, engagement, countries, and domain identity.
Total website traffic
| Month | Modeled visits |
|---|---|
| 2026-04 | 855,693 |
| 2026-05 | 726,059 |
| 2026-06 | 586,500 |
| 2026-07 | 538,635 |
| 2026-08 | 511,139 |
| 2026-09 | 546,743 |
Top visitor countries
| Country | Name | Traffic share |
|---|---|---|
| US | United States | 17.5% |
| IN | India | 9.7% |
| DE | Germany | 7.4% |
| FR | France | 4.8% |
| GB | United Kingdom | 4.8% |
Domain identity
| Signal | Value |
|---|---|
| Registered | Jun 22, 2008 |
| Last changed | Jan 7, 2026 |
| Expires | Jun 22, 2027 |
| WHOIS server | whois.verisign-grs.com |
| DNSSEC | Not signed |
| Nameservers | NS-119-B.GANDI.NET, NS-199-A.GANDI.NET, NS-245-C.GANDI.NET, Z.DNS.GANDI.NET |
Website capture
Organic keywords
Top keywords and an independent Google result page.
Top organic keywords
| Keyword | Volume | CPC | Estimated value |
|---|---|---|---|
| sonarqube | 72,820 | $11.46 | $25,740 |
| sonarcube | 3,760 | $4.61 | $1,730 |
| sonarsource | 2,600 | $9.85 | $1,390 |
| sonar | 59,840 | $3.22 | $1,250 |
| sonarqube mcp | 1,230 | $0.50 | $970 |
Independent Google result page
Query: define sonarqube
| Position | Title | URL | Description |
|---|---|---|---|
| 1 | SonarQube | Code Quality, Security & Verification Tools | Sonar | https://www.sonarsource.com/products/sonarqube/ | SonarQube is an industry-leading platform for automated code quality and security analysis. It enables organizations and individual developers to continuously ... |
| 2 | SonarQube | https://en.wikipedia.org/wiki/SonarQube | SonarQube is an open-core static code analysis platform developed by Sonar. [2] It scans source code to detect issues like bugs, vulnerabilities and code smells |
| 3 | Homepage | SonarQube Server | https://docs.sonarsource.com/sonarqube-server | SonarQube Server is an industry-standard on-premises automated code review and static analysis tool designed to detect coding issues in 40+ ... |
| 4 | What is SonarQube and How it works? An Overview and Its ... | https://www.devopsschool.com/blog/what-is-sonarqube-and-how-it-works-an-overview-and-its-use-cases/ | SonarQube is a Code Quality Assurance tool that collects and analyzes source code, and provides reports for the code quality of your project. |
| 5 | What is SonarQube? | https://www.geeksforgeeks.org/devops/sonarqube/ | SonarQube is a code quality analysis tool that analyzes the code in terms of its quality. The tool generates a detailed analysis report of the ... |
| 6 | What Is SonarQube | Static Code Analysis & Verification ... | https://www.youtube.com/watch?v=xeTwG9XFFTE | SonarQube is a code quality and security platform that helps developers and organizations systematically detect and fix issues before they ... |
| 7 | SonarQube: Open Source Security Automation - Semaphore | https://semaphore.io/blog/sonarqube | SonarQube is an open-source static code analysis tool. It allows you to continuously monitor, analyze, and improve your code. |
| 8 | Comprehensive Guide to SonarQube: Understanding ... | https://medium.com/@piyushkashyap045/comprehensive-guide-to-sonarqube-understanding-benefits-setup-and-code-quality-analysis-with-caffbc8afa0f | SonarQube is an open-source platform for continuous inspection of code quality. It provides automatic analysis of your code to identify bugs, ... |
| 9 | SonarQube Security: Detect Code Vulnerabilities in 2026 | https://www.qiminfo.ch/en/sonarqube-security/ | Definition and Role. SonarQube is a static code analysis (SAST) platform that helps development teams detect vulnerabilities, bugs, and quality ... |
| 10 | What is SonarQube and how does it work? | https://bugfender.com/blog/sonarqube/ | SonarQube is a code quality and security platform that helps teams detect bugs, vulnerabilities, and maintainability issues early in development ... |
Important pages
Pages earning the most estimated search traffic in the sample.
Website intelligence — Collected evidence
Prioritized website intelligence pages
| Type | Page | Words | Change | URL |
|---|---|---|---|---|
| reviews | AI Code Review & Verification Tools \ | Sonar | static | 1,277 |
| pricing | Plans & Pricing: Enterprise & Team Plans for Developers \ | playwright | 1,878 | new |
| pricing | Malicious Package Detection \ | Sonar | playwright | 1,709 |
| pricing | Contact SonarQube Sales Team \ | Sonar | playwright | 612 |
| pricing | Pricing \ | Sonar | playwright | 1,525 |
| pricing | SonarQube Server Plans & Pricing \ | Sonar | playwright | 1,803 |
| features | Product Demos \ | playwright | 507 | new |
| features | Resources \ | Sonar | playwright | 959 |
| features | AI Coding Tools \ | Sonar | playwright | 2,107 |
| features | AI Code Quality \ | Sonar | static | 592 |
| features | Software Architecture Analysis \ | Sonar | static | 2,254 |
| features | Automated Code Review \ | Sonar | static | 2,126 |
| features | Code Coverage Tools \ | Sonar | static | 2,018 |
| features | Code Governance \ | Sonar | static | 948 |
| features | Code Review Software \ | Sonar | static | 2,779 |
Features
| Page type | Evidence | Source |
|---|---|---|
| features | PRODUCT DEMOS | https://www.sonarsource.com/product-demos/ |
| features | Sonar's code quality and security solutions | https://www.sonarsource.com/product-demos/ |
| features | Explore interactive product demos at your own pace. Click into features and use cases or request a customized demo. | https://www.sonarsource.com/product-demos/ |
| features | Request a demoExplore pricing | https://www.sonarsource.com/product-demos/ |
| features | SonarQube Cloud | https://www.sonarsource.com/product-demos/ |
| features | Discover key product features | https://www.sonarsource.com/product-demos/ |
| features | Interactive demo | https://www.sonarsource.com/product-demos/ |
| features | SonarQube Server | https://www.sonarsource.com/product-demos/ |
| features | Walk through product reporting capabilities | https://www.sonarsource.com/product-demos/ |
| features | Advanced Security | https://www.sonarsource.com/product-demos/ |
| features | Adds deeper comprehensive security coverage for dependencies | https://www.sonarsource.com/product-demos/ |
| features | Fix bugs, vulnerabilities, and quality issues with a click | https://www.sonarsource.com/product-demos/ |
| features | Privacy Preference Center | https://www.sonarsource.com/product-demos/ |
| features | When you visit any website, it may store or retrieve information on your browser, mostly in the form of cookies. This information might be about you, your preferences, or your device, and is mostly used to make the site work as you expect. The information does not usually identify you directly, but it can give you a more personalized web experience. Because we respect your right to privacy, you can choose not to allow some types of cookies. Click on the different category headings to learn more and change our default settings. Blocking some types of cookies may impact your experience of the site and the services we are able to offer. | https://www.sonarsource.com/product-demos/ |
| features | Cookie Policy at SonarSource | https://www.sonarsource.com/product-demos/ |
| features | Manage Consent Preferences | https://www.sonarsource.com/product-demos/ |
| features | Strictly Necessary Cookies | https://www.sonarsource.com/product-demos/ |
| features | Always Active | https://www.sonarsource.com/product-demos/ |
| features | These cookies are necessary for our websites to function and cannot be switched off in our systems. They are usually only set in response to actions made by you which amount to a request for services, such as setting your privacy preferences, logging in, or filling in forms. You can also set your browser to block or alert you about these cookies, but please note that some parts of the websites will not then work. These cookies do not store any personally identifiable information. | https://www.sonarsource.com/product-demos/ |
| features | Performance Cookies | https://www.sonarsource.com/product-demos/ |
Pricing and plans
| Page type | Evidence | Source |
|---|---|---|
| pricing | Plans and pricing | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Find the plan that fits your team | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Code quality, security, and AI code review on one platform. Start in minutes with a 14-day trial, no credit card. Free tier never expires. | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | SonarQube Team plan | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Start free SonarQube trial | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Gitar AI Code Review, Core Plan | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Start free Gitar trial | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Over 50 developers · one conversation, whole platform. Custom pricing | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | SonarQube Enterprise plan | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Outcome-based pricing per PR, not per seat, with unlimited iterations | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Contact sales | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Free forever | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Public, OSI-licensed repos get SonarQube for OSS and Gitar AI Code Review for OSS, with the same features as the paid Pro plan. | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | SonarQube Team Plan, free for your private projects up to 50k LOC. No card, no expiry. | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Start for free | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Open source and free. Bring analysis into any MCP-capable agent. | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Free extension. On-the-fly analysis and guidance as you type. | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | How does pricing work for private projects? | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | Subscribing to a paid plan on SonarQube allows you to create a private organization containing private projects. | https://www.sonarsource.com/plans-and-pricing/ |
| pricing | SonarQube plan pricing starts at $34 monthly for analysis of up to 100k LOC. Other LOC increments are available. | https://www.sonarsource.com/plans-and-pricing/ |
Integrations and supported platforms
No supporting public-page evidence was collected for this category.
Product and company updates
No supporting public-page evidence was collected for this category.
Rank tracking
Persistent keyword baselines and position movement.
This analysis created the first position baseline at 2026-10-26T07:18:07.706Z. Movement appears after the next fresh analysis using the same location and language.
Features
Features and capabilities
Core functions and evidence-backed product capabilities.
| Capability | What it does |
|---|---|
| Automated code review | Scans all branches, pull requests, and merges automatically upon commit or push S13. |
| Multi-language support | Static analysis for over 35 programming languages and frameworks S13. |
| Secrets detection | Identifies and prevents exposure of sensitive credentials, API keys, and secrets in IDEs, commits, and PRs S1. |
| Software Composition Analysis (SCA) | Identifies third-party open-source components to manage vulnerabilities, license compliance, and supply chain risks S1. |
| AI-powered fixes | Generates context-aware fix suggestions for detected issues S1. |
| Architecture management | Visualizes and enforces system design to ensure code adheres to a modular framework S1. |
| Quality gates | Customizable thresholds enforcing go/no-go deployment decisions S13. |
Integrations and ecosystem
Connected products, exports, APIs, and workflow compatibility.
| Integration or interface | Type | What it enables |
|---|---|---|
| GitHub, GitLab, Azure DevOps | Integration | Seamless DevOps integration for automated quality checks S1. |
| IDE (SonarQube for IDE) | Integration | Real-time analysis and issue highlighting in the IDE S13. |
| CI/CD pipelines | Integration | Automated branch analysis and pull request reviews S13. |
| MCP Server | AI interface | Integration with AI-native IDEs and coding tools S1. |
| LDAP/SAML | Integration | Enterprise authentication and SSO S1. |
Pricing
Pricing and plans
Published plans, free access, trials, credits, and pricing limitations.
| Plan or offer | Verified price and billing | Included | Limits |
|---|---|---|---|
| Free | $0 S174 | Private projects up to 50k lines of code S174 | Community support only S174 |
| Team | $34 per month S174 | Up to 100k lines of code S174 | Under 50 developers; 30+ languages S174 |
| Enterprise | Contact sales S174 | Custom S174 | 45+ languages, SSO/SCIM, portfolios, advanced security add-on S174 |
| SonarQube Server | Not published S174 | Per instance, by lines of code S174 | Self-managed Developer, Enterprise, Data Center editions S174 |
Competition
Competitive landscape
Domains competing for the same organic search demand.
Sampled competitors
| Competitor | First-page appearances | Sampled queries | Average position | Queries observed |
|---|---|---|---|---|
| medium.com | 2 | 2 | 5 | define sonarqube, definition of a software bug |
| qiminfo.ch | 1 | 1 | 1 | define sonarqube |
| dbvis.com | 1 | 1 | 1 | definition of a software bug |
| docs.sonarsource.com | 1 | 1 | 2 | define sonarqube |
| accelq.com | 1 | 1 | 2 | definition of a software bug |
| community.sonarsource.com | 1 | 1 | 3 | define sonarqube |
| testmatick.com | 1 | 1 | 3 | definition of a software bug |
| freecodecamp.org | 1 | 1 | 4 | define sonarqube |
| facebook.com | 1 | 1 | 4 | definition of a software bug |
| gartner.com | 1 | 1 | 6 | define sonarqube |
Website intelligence — Collected evidence
Customers, testimonials, and first-party review claims
| Page type | Evidence | Source |
|---|---|---|
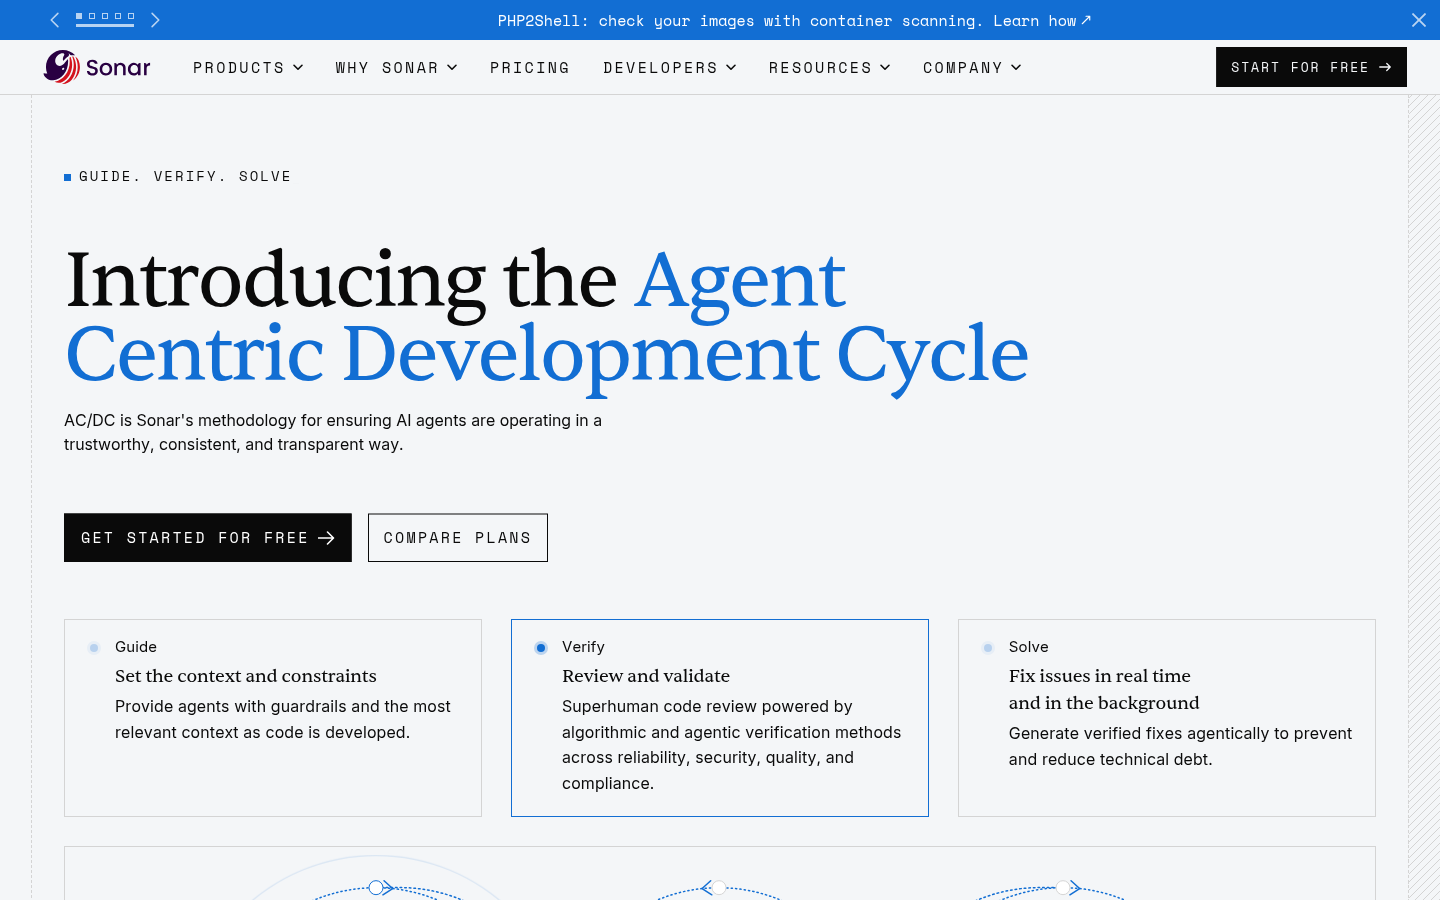
| reviews | Guide. Verify. Solve | https://www.sonarsource.com/ |
| reviews | Introducing the Agent Centric Development Cycle | https://www.sonarsource.com/ |
| reviews | AC/DC is Sonar's methodology for ensuring AI agents are operating in a trustworthy, consistent, and transparent way. | https://www.sonarsource.com/ |
| reviews | Get started for free Compare plans | https://www.sonarsource.com/ |
| reviews | GuideSet the context and constraintsProvide agents with guardrails and the most relevant context as code is developed. VerifyReview and validateSuperhuman code review powered by algorithmic and agentic verification methods across reliability, security, quality, and compliance. SolveFix issues in real time and in the backgroundGenerate verified fixes agentically to prevent and reduce technical debt. | https://www.sonarsource.com/ |
| reviews | Agentic CI Verification Code Maintenance | https://www.sonarsource.com/ |
| reviews | Agentic Loop | https://www.sonarsource.com/ |
| reviews | Verify Guide Solve | https://www.sonarsource.com/ |
| reviews | CI Verification Loop | https://www.sonarsource.com/ |
| reviews | Code Maintenance Loop | https://www.sonarsource.com/ |
| reviews | Agentic LoopWhere agents iteratively buildOptimize code generated within the agentic sandbox. Improve agent effectiveness. Reduce token costs, improve output quality, and reduce risk. | https://www.sonarsource.com/ |
| reviews | CI Verification LoopThe validation pipeline for all codeCode review, with zero-trust, multi-layered verification and a quality gate at sandbox exit. Merge fixes at high velocity and volume with confidence. | https://www.sonarsource.com/ |
| reviews | Code Maintenance LoopBackground remediation of tech debtContinuously patrol to address legacy issues in the background agentically. Cleaner code makes it easier for coding agents to work efficiently. | https://www.sonarsource.com/ |
| reviews | Trusted by over 7M developers and 75% of the Fortune 100 | https://www.sonarsource.com/ |
| reviews | Explore our offerings | https://www.sonarsource.com/ |
| reviews | Everything you need to verify AI code | https://www.sonarsource.com/ |
| reviews | Server · Cloud · Community | https://www.sonarsource.com/ |
| reviews | The most comprehensive and accurate zero trust code verification platform. Provides multi-layered review of all code, and findings that are consistent, explainable, repeatable, and auditable. | https://www.sonarsource.com/ |
| reviews | Server Cloud | https://www.sonarsource.com/ |
| reviews | SonarQube Advanced Security | https://www.sonarsource.com/ |
Independent review sources discovered
No links to supported independent review platforms were discovered on the collected pages.
AI visibility
Measured ChatGPT and Google AI mentions with cited sources.
AI-assistant referral traffic
- Estimated current generative-AI referral share: 2.8%
| Month | Traffic share | Source |
|---|---|---|
| — | — | All AI assistants |
| — | — | All AI assistants |
| — | — | All AI assistants |
Website intelligence — Collected evidence
Site-stated AI capabilities
| Page type | Evidence | Source |
|---|---|---|
| features | As AI tools write more code, teams often accept it without proper vetting. When defects reach production, ownership gets murky. Catching issues early keeps every change accountable to your quality and security standards. | https://www.sonarsource.com/solutions/ai/ |
| features | Your standards, automatically applied — No new rules to define. Vortex uses the quality profiles your team already enforces in SonarQube, across every AI tool on the team. | https://www.sonarsource.com/solutions/ai/ |
| features | One standard across every AI tool — One verification standard for every AI coding tool your team uses. Consistent code quality no matter which assistant a developer picks. | https://www.sonarsource.com/solutions/ai/ |
| features | Brings trusted SonarQube analysis into the AI tools and agents your team already uses. | https://www.sonarsource.com/solutions/ai/ |
| features | Guardrails for AI code | https://www.sonarsource.com/solutions/ai/ |
| features | Compliance for AI code | https://www.sonarsource.com/solutions/ai/ |
| features | AI coding tools are exponentially increasing the quantity of code being created. This code will be more difficult to manage, and strain the review bandwidth of the developers accountable for its quality. The gap between them is the engineering productivity paradox. | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | Ensuring that AI-generated code consistently follows your team’s coding standards and best practices is a major challenge. | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | SonarQube helps development teams fuel AI-enabled development and build trust into every line of code, ensuring that AI adoption is controlled and meets the code quality needs of your organization. | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | Empower developers to review AI generated code while protecting their bandwidth for other work, protecting your organization’s long-term security and code health. | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | “SonarQube’s ability to analyze all code — whether first-party, AI-generated or open source — helps developers take ownership of code bases regardless of where code is coming from.” | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | Key capabilities for secure, verified AI coding | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | Trusted quality gates for AI-generated code, ensuring it meets the same high standards as human-written code before it can be merged | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | Automatic feedback on AI code quality, security, and compliance in pull requests and branches, directly in the DevOps platform where developers work | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | Why choose SonarQube for secure, verified AI coding? | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | We are the only solution that can integrate analysis of quality and security for AI-generated code. | https://www.sonarsource.com/solutions/ai-code-quality/ |
| features | <table><tbody><tr><td><p><br></p></td><td><p><strong>For Architects / Project Owners</strong></p></td><td><p><strong>For Developers</strong></p></td></tr><tr><td><p><strong>Architectural Integrity</strong></p></td><td><p>Maintain control by deciding when and how to enforce architecture violations in the code. Ensure that AI code doesn't violate the intended architecture.</p></td><td><p>Receive live documentation of the current architecture, providing full context awareness, reducing guesswork and guiding changes.</p></td></tr><tr><td><p><strong>Velocity and Productivity </strong></p></td><td><p>Instantly see a project’s current architecture reducing time consuming reviews to reverse engineer. Building your intended architecture is a snap; start light and evolve it over time to suit your needs.</p></td><td><p>Build a clear understanding of expectations for writing code that aligns with the intended architecture. Resolve architectural issues immediately to pass the quality gate.</p></td></tr><tr><td><p><strong>AI Governance</strong></p></td><td><p>Enable LLMs to leverage the current and intended architectures as context to generate better results.</p></td><td><p>Get instant notification when AI generated code violates the architecture, allowing for timely, in-workflow fixes.</p></td></tr></tbody></table> | https://www.sonarsource.com/solutions/architecture/ |
| features | From a risk perspective, unmanaged architectural debt eventually pushes organizations toward full application rewrites, which stalls innovation and delays time to market. By keeping architecture intentional and visible, you reduce complexity, make it easier for new team members (and AI coding assistants) to contribute safely, and prevent your code from drifting away from the intended architecture. | https://www.sonarsource.com/solutions/architecture/ |
| features | Protect your codebase health with SonarQube, by giving developers common standards for secure, high-quality code even as they adopt AI coding assistants. Drive consistency across teams and prevent issues before they reach production. | https://www.sonarsource.com/solutions/automated-code-review/ |
| features | Traditional code review processes are struggling to keep up. Development teams face mounting pressure to deliver faster, and the explosion of AI-generated code only adds to the volume. This leads to significant challenges. As a result, organizations increasingly turn to automation to review and maintain code quality and security at scale. | https://www.sonarsource.com/solutions/automated-code-review/ |
These are first-party product claims, not independent measurements of AI-search visibility.
Marketing opportunities
Actions calculated directly from the collected evidence.
| Opportunity | Recommended action | Evidence |
|---|---|---|
| Competitor gap | Review the sampled queries where medium.com appears. | 2 first-page appearances across define sonarqube, definition of a software bug |
Website intelligence — Collected evidence
Website evidence gaps
- integrations: no usable public page was collected; verify whether the site publishes this evidence.
- customers: no usable public page was collected; verify whether the site publishes this evidence.
- changes: no usable public page was collected; verify whether the site publishes this evidence.
- identity: no usable public page was collected; verify whether the site publishes this evidence.
- technical: no usable public page was collected; verify whether the site publishes this evidence.
Trust and proof
Customers, proof, and reviews
Published proof, customer signals, and review evidence.
Independent reviews
| Platform | Page | How it was found | Note |
|---|---|---|---|
| G2 | SonarSource S.A Profile | Grounded web search | # SonarSource S.A 4.4 out of 5 stars 5 star 69% 4 star 25% 3 star 3% 2 star 0% 1 star 0% 120 reviews ... Server (formerly SonarQube)90 reviewsSonarQube is a code quality and vulnerability solution for development teams that integrates with |
| MakerStack | SonarQube Review (2026) - MakerStack | Grounded web search | SonarQube is the most mature and comprehensive static analysis platform available. The Quality Gates feature alone justifies the setup effort for mid-to- ... need one tool to enforce code quality across multiple languages in a CI/CD pipeline, SonarQube is |
| PeerSpot | SonarQube reviews 2026 | Grounded web search | # SonarQube Reviews Vendor: SonarSource Sàrl 4.0 out of 5 - 139 reviews - 84% willing to recommend ... SonarQube requires improvements in security features and code vulnerability detection. Users report limited support for new |
| AuditXYZ | SonarQube Review 2026: Pricing, Features, and Verdict Review | Grounded web search | Security analysis depth trails dedicated SAST platforms. While SonarQube's security rules have improved significantly, the taint analysis and ... No DAST or SCA means SonarQube covers only static code analysis. Organizations need additional tools for |
Customer proof
| Proof type | Named customer or source | Evidence |
|---|---|---|
| Case study | CleverTap | customer case study — The value CleverTap sees in SonarQube Server is to enforce code quality levels with quality gates in the CI pipeline and ensure a ... (CleverTap Case Study / Sonar) |
| Case study | DATEV | customer case study — Good code quality has transitioned from being a mandated requirement to a self-evident norm across teams. (DATEV Case Study / Sonar) |
| Case study | Wolters Kluwer | customer case study — Wolters Kluwer recognized that they needed more than just a tool; they needed a transformation. (Wolters Kluwer Cuts Scan Times and Costs while Improving Code Quality Standards) |
| Case study | IMSA | customer case study — By making SonarQube a cornerstone of its software factory, IMSA created a culture of accountability. (How IMSA reduces production bugs by creating a unified standard of code health with SonarQube) |
| Case study | Recognyte | customer case study — The result has been an increase in code quality and developer productivity with a more reliable and secure software development process. (Recognyte Case Study / Sonar) |
Independent mentions
- Customer Stories & Organizations Successfully Implementing Sonar / Sonar — ### Global financial leader A global financial leader managing a massive technology estate with approximately 20,000 software engineers uses SonarQube to stay ahead while meeting the high standards of the banking industry
External links were grounded in one live web search. Search snippets are leads, not independently scraped page content; rejected links remain available in Review evidence.
Company, security, and trust
Ownership, policies, security signals, and public trust evidence.
| Signal | Finding | Source |
|---|---|---|
| Company and ownership | Sriharsha Chintalapani Co-founder & CTO Collate (OpenMetadata) | source |
| Contact and support | Not published on the collected pages. | — |
| Legal and privacy | SOC 2 Type II ISO 27001 GDPR Zero Data Retention | source |
| Security and compliance | 99.9% uptime SLA · SOC 2 Type II | source |
| Uptime and status page | 99.9% uptime SLA · SOC 2 Type II | source |
| Domain registered | 2008-06-22 | — |
| Domain expires | 2027-06-22 | — |
Not found on the collected pages: contact and support. This only means Scout did not find it on the pages it read; it says nothing about the company itself.
Documentation and product updates
Help resources, product guidance, and visible changes over time.
| Resource or update | Type | What is available | Date or freshness |
|---|---|---|---|
| Contact and support | Support | Public contact and support channel. (source) | Not dated |
| Contact and support | Support | Public contact and support channel. (source) | Not dated |
Not found in the collected public sources: public roadmap, changelog or release notes, status page, separate help center or knowledge base.
Technical
Technical and delivery signals
Delivery model, platforms, API, data ownership, reliability claims and release activity.
| Signal | Finding | Source |
|---|---|---|
| Delivery model (cloud, self-hosted, desktop, browser extension) | Available as SonarQube Cloud (SaaS) and SonarQube Server (self-managed) S1. | S1 |
| Platforms and apps | Supports over 35 programming languages and frameworks S13. | S13 |
| API and extensibility (API, SDK, webhooks, MCP, plugins) | Integrates with AI-native IDEs, MCP Server, CI/CD, and DevOps platforms S1. | S1 |
| Data ownership and export | Self-managed deployment allows full data residency and control S1. | S1 |
| Performance and reliability claims | 99.9% uptime SLA S1. | S1 |
| Release activity | Not published on the collected pages. | — |
Measured infrastructure
Domain, certificate, and hosting signals, measured directly.
| Signal | Finding |
|---|---|
| Domain registered | 2008-06-22 — Gandi SAS |
| Domain expires | 2027-06-22 |
| TLS certificate | Let's Encrypt, valid, expires 2026-12-16 |
| Security headers | HSTS, CSP, X-Content-Type-Options, X-Frame-Options, Referrer-Policy |
| Server header | Netlify |
| Mail handled by | ASPMX.L.GOOGLE.com, SMTP.GOOGLE.com |
| Nameservers | z.dns.gandi.net, ns-245-c.gandi.net |
Not measurable: wayback: rate limited by archive.org, ladder stopped after 1 probe(s). A gap here means the lookup was unavailable, not that the finding is negative.
Technical site audit
A bounded multi-page crawl with page-level issues and URLs.
Scout — Bounded technical crawl
- Pages crawled: 15 of 15 maximum
- Technical health: 98/100
- Critical issues: 0
- Warnings: 4
- Notices: 4
Issues
| Severity | Issue | Value | Affected URL |
|---|---|---|---|
| notice | Images are missing alt text | 2 | https://www.sonarsource.com/products/sonarqube/ |
| notice | Images are missing alt text | 2 | https://www.sonarsource.com/products/sonarqube/advanced-security/ |
| notice | Images are missing alt text | 2 | https://www.sonarsource.com/products/sonarqube/hunter-agent/ |
| notice | Images are missing alt text | 3 | https://www.sonarsource.com/products/sonarqube/ide/ |
| warning | Duplicate title in audit sample | 2 | https://www.sonarsource.com/ |
| warning | Duplicate title in audit sample | 2 | https://www.sonarsource.com/ |
| warning | Duplicate meta description in audit sample | 2 | https://www.sonarsource.com/ |
| warning | Duplicate meta description in audit sample | 2 | https://www.sonarsource.com/ |
Crawled pages
| Status | Title | H1s | Words | Response | URL |
|---|---|---|---|---|---|
| 200 | AI Code Review & Verification Tools \ | Code Security \ | Sonar | 1 | 1712 |
| 200 | SonarQube container scanning is now in open beta \ | Sonar | 1 | 2024 | 284 ms |
| 200 | AI Code Review & Verification Tools \ | Code Security \ | Sonar | 1 | 1712 |
| 200 | SonarQube \ | Code Quality, Security & Verification Tools \ | Sonar | 1 | 4193 |
| 200 | SonarQube Cloud \ | Cloud-Native Code Quality & Security \ | Sonar | 1 | 3424 |
| 200 | SonarQube Server \ | On-Prem AI Code Quality & Security \ | Sonar | 1 | 3449 |
| 200 | SonarQube Advanced Security \ | SAST & SCA Tools \ | Sonar | 1 | 2115 |
| 200 | Gitar \ | AI-Powered Code Review & PR Automation Tools \ | Sonar | 1 | 2501 |
| 200 | Sonar Vortex \ | AI Context Engine For Coding Agents \ | Sonar | 1 | 1696 |
| 200 | SonarQube Remediation Agent \ | Technical Debt Tools \ | Sonar | 1 | 1688 |
| 200 | SonarQube Hunter Agent \ | AI Logic Flaw Detection Tools \ | Sonar | 1 | 1349 |
| 200 | SonarQube for IDE \ | Free AI Code Verification Extension \ | Sonar | 1 | 2806 |
| 200 | SonarQube CLI — sonarsource.com/sonarqube/cli | 1 | 444 | 117 ms | https://www.sonarsource.com/sonarqube/cli/ |
| 200 | SonarQube MCP Server \ | Code Context For AI Agents \ | Sonar | 1 | 2582 |
| 200 | Now available: SonarQube plugin for AI modelCode \ | Sonar | 1 | 1487 | 755 ms |
This is a bounded Scout crawl. Core Web Vitals and Lighthouse scores are not claimed unless a dedicated performance audit is connected.
Search Console and Analytics
First-party search and behavioral data connection state.
Modeled acquisition channels
| Channel | Estimated share |
|---|---|
| direct | 29.5% |
| search | 49.6% |
| search organic | 35.6% |
| search paid | 14.0% |
| social | 2.1% |
| social organic | 1.8% |
| social paid | 0.4% |
| referrals | 13.0% |
| paid referrals | 1.3% |
| 1.3% | |
| gen ai | 2.8% |
| affiliate | 0.3% |
| other | 0.0% |
First-party connections
| Integration | Status | Data available after connection |
|---|---|---|
| Google Search Console | Not connected | Clicks, impressions, CTR, average position, queries, pages, countries, and devices |
| Google Analytics | Not connected | Organic sessions, engagement, landing pages, conversions, geography, and devices |
No first-party Search Console or Analytics numbers are shown until the site owner authorizes the corresponding Google account. Scout traffic model values above are modeled estimates, not private analytics totals.
Limits and method
Limitations and open questions
Known constraints and missing evidence from the collected pages.
The collected pages do not mention specific competitors. Evidence gaps include lack of detailed pricing for SonarQube Server, no explicit customer support contact information, and no release history or changelog. Open questions remain about the exact capabilities of the AI-powered agent and the specifics of the Advanced Security add-on.
Sources, method, and limitations
Evidence inventory, collection method, provider use, and constraints.
This report is based on 15 collected pages from sonarsource.com, including product pages, pricing, and integration documentation. The evidence catalog includes 174 items, with sources ranging from product descriptions to pricing tables. External proof search was enabled but only verified the existence of linked results, not their content. Limitations include potential marketing bias in product descriptions and lack of independent verification of claims.
- Official Websitehttps://www.sonarsource.com/products/sonarqube/Verified
- Documentationhttps://www.sonarsource.com/why-sonar/Verified
- Official Websitehttps://www.sonarsource.com/products/gitar/Verified
- Official Websitehttps://www.sonarsource.com/jp/get-started/Verified
- Pricing Pagehttps://www.sonarsource.com/plans-and-pricing/Verified
- Pricing Pagehttps://www.sonarsource.com/jp/plans-and-pricing/Verified
- Pricing Pagehttps://www.sonarsource.com/plans-and-pricing/contact-sales/Verified
- Pricing Pagehttps://www.sonarsource.com/plans-and-pricing/data-center/Verified
- Pricing Pagehttps://www.sonarsource.com/plans-and-pricing/gitar/Verified
- Pricing Pagehttps://www.sonarsource.com/plans-and-pricing/sonarqube/Verified
- Pricing Pagehttps://www.sonarsource.com/jp/plans-and-pricing/contact-sales/Verified
- Pricing Pagehttps://www.sonarsource.com/jp/plans-and-pricing/data-center/Verified
- Official Websitehttps://www.sonarsource.com/product-demos/Verified
- Official Websitehttps://www.sonarsource.com/resources/solution-briefs/Verified
- Review Sitehttps://www.g2.com/sellers/sonarsource-s-aVerified
- Review Sitehttps://makerstack.co/reviews/sonarqube-review/Verified
- Articlehttps://www.sonarsource.com/customer-stories/clevertap/Verified
- Articlehttps://www.sonarsource.com/customer-stories/datev/Verified
- Review Sitehttps://www.peerspot.com/products/sonarqube-reviewsVerified
- Articlehttps://www.sonarsource.com/customer-stories/wolters-kluwer/Verified
- Articlehttps://www.sonarsource.com/imsa-customer-story-2025.pdfVerified
- Articlehttps://www.sonarsource.com/customer-stories/recognyte/Verified
- Review Sitehttps://www.auditxyz.com/tools/security-compliance-devsecops/sonarqubeVerified
- Articlehttps://www.sonarsource.com/customer-stories/Verified