Overview
Summary
The useful answer before the supporting detail.
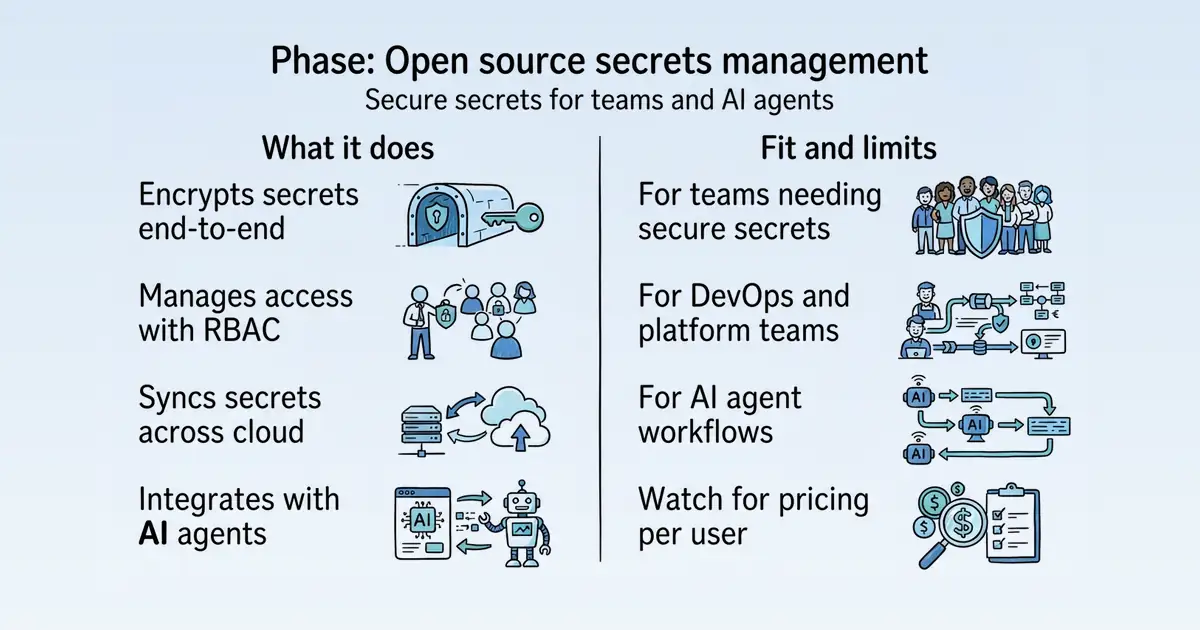
Phase is an open source platform for teams and AI agents to securely access, manage, and deploy application secrets from development to production S1. It solves the problem of secret sprawl and insecure handling by providing end-to-end encryption, granular access control, and audit logging S1. Its practical value lies in centralizing secret management, automating deployment across infrastructure, and enabling AI agents to use secrets safely with dynamic credentials S1.
Product identity and positioning
Name, category, positioning, audience, and first-party claims.
- Identity: Phase is an open source secrets management platform S1.
- Core purpose: It solves the problem of securely accessing, managing, and deploying application secrets across environments S1.
- Intended users: Teams and AI agents that need to handle application secrets S1.
- Product scope: A platform, not a single app, offering a console, CLI, SDKs, and integrations S67.
- Positioning: Positioned as a secure, open source alternative for modern secret management S1.
- Claimed distinction: Claims end-to-end encryption and independent security audits S1.
Use cases and audiences
Who the product serves and the jobs it is designed to handle.
| Audience | Practical use case |
|---|---|
| Development teams | Manage and deploy application secrets across development, staging, and production environments S1. |
| DevOps / Platform teams | Automate secret deployment pipelines and sync secrets to cloud services and CI/CD tools S1 S67. |
| Security teams | Enforce access control, audit secret changes, and ensure compliance with SOC 2 S1. |
| AI agents | Securely access secrets and use dynamic credentials for outbound requests S1. |
| Machine identities | Authenticate workloads using cloud platform identities like AWS SigV4 or Azure managed identity S1. |
Features
Features and capabilities
Core functions and evidence-backed product capabilities.
| Capability | What it does |
|---|---|
| End-to-end encryption | Encrypts all secrets, ensuring they are secure in transit and at rest S1. |
| Role-based access control | Manages authentication, RBAC, and network access policies from one place S1. |
| Audit logging | Captures every management action org-wide with actor, timestamp, and before/after diffs S1. |
| Dynamic secrets | Generates temporary, on-demand secrets for workloads and agents S1. |
| Secret syncing | Syncs secrets to external services like AWS Secrets Manager, GitHub Actions, and Kubernetes S67. |
| AI agent integration | Allows AI coding agents like AI modelCode and Cursor to manage secrets via natural language S86. |
| Write-only secrets | Allows saving secrets that are never visible or editable in the UI again S1. |
| Offline mode | Provides an encrypted local cache fallback for secrets when the network is unavailable S67. |
Integrations and ecosystem
Connected products, exports, APIs, and workflow compatibility.
| Integration or interface | Type | What it enables |
|---|---|---|
| AWS Secrets Manager | Integration | Sync secrets to AWS Secrets Manager, using Phase as a single source of truth S99. |
| GitHub Actions | Integration | Inject secrets into GitHub Actions workflows automatically S128. |
| GitLab CI | Integration | Sync secrets and variables to GitLab CI pipelines and jobs S131. |
| Hashicorp Vault | Integration | Sync secrets with Vault, allowing existing Vault setups to remain in place S141. |
| Hashicorp Nomad | Integration | Sync secrets to Nomad variables for use in Nomad jobs S134. |
| AI modelCode | Integration | Manage Phase secrets directly from AI modelCode via natural language S86. |
| Public REST API | API | Manage application secrets programmatically via a public REST API S72. |
| Kubernetes | Integration | Securely sync secrets to Kubernetes clusters S67. |
Pricing
Pricing and plans
Published plans, free access, trials, credits, and pricing limitations.
| Plan or offer | Verified price and billing | Included | Limits |
|---|---|---|---|
| Free | $0 S67 | Core platform features S67 | 5 users or service accounts; 3 apps; 3 environments; 24-hour audit logs S67 |
| Pro | $10 per user per month, billed annually at $120 (struck through $144) S67 | Everything in Free, unlimited users, service accounts and apps S67 | 10 environments; 90-day audit logs S67 |
| Enterprise | $25 per user per month, billed annually at $300 (struck through $360) S67 | OIDC SSO, SCIM, dynamic secrets, third-party KMS, SIEM S67 | Not established |
| Trial | 14-day free trial on Pro and Enterprise S67 | Not established | Not established |
Trust and proof
Customers, proof, and reviews
Published proof, customer signals, and review evidence.
Independent reviews
No citation-grounded independent review links were found.
Customer proof
| Proof type | Named customer or source | Evidence |
|---|---|---|
| Testimonial | Shivam (Lead Product Engineer @ Chatwoot), Ash (Security Services Team Lead @ Arctic Wolf), Mary (Co-founder @ Voxify), | testimonial — Stories ... (Secrets management for teams and AI agents) |
Independent mentions
- Unlocking encryption for developers / Phase Blog — ## Building Phase ... If we ... Phase is our attempt at unlocking the potential of encryption for app developers. We took all the lessons we learned from trying to build encryption into hobby projects, open-source apps and enterprise software, and combined them into a single solution — an open-source platform for managing keys, tracking key usage with logs, and SDKs to easily integrate with any application. We believe that encryption is the best defense against data breaches, and that putting th
- Speedrunning SOC 2 Type 2 — # Speedrunning SOC 2 Type 2 A guide for any early-stage technical founders to get SOC 2 Type 2 compliance as quickly as possible on a budget. Nimish 2025.11.21 Share on X Share on LinkedIn Share by email Copy URL
- Secrets management foryour entire stack. — # Secrets management foryour entire stack. Integrate, don't replace. Phase works hand-in-hand with your favorite tools, platforms and AI coding agents to keep your application secrets secure and synced across your infrastructure.
- Guides, engineering tales& company updates — # Guides, engineering tales& company updates Engineering guides, security deep dives, and company updates from the Phase team. ... 2 Type 2 CompliantWe are officially SOC 2 Type 2 compliant — here's what that means for you and your data.Nimish2026.02.28
- phase.dev — best way to implement all the best practices discussed above. They provide a centralized place where secrets can be stored and managed. These tools also provide ... . They allow your team members to collaborate and work with secrets efficiently and
- Console — The Phase Console has tools to manage all your Apps, collaborate with your team securely via end-to-end encryption and integrates seamlessly with the Phase CLI for local development, CI environments or full-fledged production setups.
- Announcing our pre-seed round — We are happy to announce we have raised a pre-seed round from Balaji Srinivasan. ... We are happy to announce we have raised a pre-seed round from Balaji Srinivasan. ... in many important crypto protocols including Bitcoin, Ethereum, Solana, and
- Simple pricing foreffortless security. — Trusted by thousands of teams ++ RoadmapCommunity-driven Request a feature We build features based on community requests and feedback. Looking for a specific feature or have a use-case in mind? Reach out to us.
External links were grounded in one live web search. Search snippets are leads, not independently scraped page content; rejected links remain available in Review evidence.
Company, security, and trust
Ownership, policies, security signals, and public trust evidence.
| Signal | Finding | Source |
|---|---|---|
| Company and ownership | MaryCo-founder @ Voxify#03 | source |
| Contact and support | Not published on the collected pages. | — |
| Legal and privacy | Not published on the collected pages. | — |
| Security and compliance | End-to-end encryption for all secrets. High-entropy keys for every environment, user, agent and machine. Access is controlled by encryption keys that only you hold. | source |
| Uptime and status page | Every management action captured org-wide — actor, timestamp, and before/after diffs — built for compliance and incident response. | source |
| Domain registered | 2023-02-03 | — |
| Domain expires | 2027-02-03 | — |
Not found on the collected pages: contact and support, legal and privacy. This only means Scout did not find it on the pages it read; it says nothing about the company itself.
Documentation and product updates
Help resources, product guidance, and visible changes over time.
| Resource or update | Type | What is available | Date or freshness |
|---|---|---|---|
| AWS Secrets Manager Integration / Phase Changelog | Changelog | You can now sync secrets with AWS Secrets Manager (source) | Not dated |
| GitHub Actions Integration / Phase Changelog | Changelog | You can now inject secrets from Phase into your GitHub Actions workflows (source) | Not dated |
| GitLab CI Integration / Phase Changelog | Changelog | You can now automatically sync secrets and variables to GitLab CI on managed and self-hosted instances. (source) | Not dated |
| Hashicorp Nomad Integration & more / Phase Changelog | Changelog | Native integration for Hashicorp Nomad is now live, along with a host of new QoL updates, features and bugfixes. (source) | Not dated |
| Hashicorp Vault Integration / Phase Changelog | Changelog | You can now sync secrets with Hashicorp Vault (source) | Not dated |
| Integrations / Phase Changelog | Changelog | You can now sync your secrets in Phase with 3rd party services. (source) | Not dated |
| Public REST API / Phase Changelog | Changelog | You can now manage your application secrets programmatically via a public REST API. (source) | Not dated |
| Railway Integration / Phase Changelog | Changelog | You can now automatically sync secrets and variables to Projects and Services on Railway. (source) | Not dated |
Not found in the collected public sources: public roadmap, status page, separate help center or knowledge base.
Technical
Technical and delivery signals
Delivery model, platforms, API, data ownership, reliability claims and release activity.
| Signal | Finding | Source |
|---|---|---|
| Delivery model (cloud, self-hosted, desktop, browser extension) | Available as a fully managed cloud service or self-hosted on your own infrastructure S99 S67. | S99 S67 |
| Platforms and apps | Web-based console; CLI and SDKs are available S67. | S67 |
| API and extensibility (API, SDK, webhooks, MCP, plugins) | Offers a public REST API for programmatic secret management S72. | S72 |
| Data ownership and export | Supports exporting secrets as .env files S1. | S1 |
| Performance and reliability claims | Not published on the collected pages. | — |
| Release activity | Changelog documents multiple feature releases, including integrations and API updates S99 S128 S131. | S99 S128 S131 |
Measured infrastructure
Domain, certificate, and hosting signals, measured directly.
| Signal | Finding |
|---|---|
| Domain registered | 2023-02-03 — CloudFlare, Inc. |
| Domain expires | 2027-02-03 |
| TLS certificate | Google Trust Services, valid, expires 2026-12-03 |
| Security headers | HSTS, X-Content-Type-Options, Referrer-Policy |
| Headers not served | CSP, X-Frame-Options |
| Server header | cloudflare |
| Mail handled by | aspmx.l.google.com, alt1.aspmx.l.google.com |
| Nameservers | mona.ns.cloudflare.com, derek.ns.cloudflare.com |
Not measurable: wayback: rate limited by archive.org, ladder stopped after 1 probe(s). A gap here means the lookup was unavailable, not that the finding is negative.
Limits and method
Limitations and open questions
Known constraints and missing evidence from the collected pages.
The collected pages do not mention specific competitors by name. Evidence gaps include lack of detailed pricing for Enterprise plan limits, absence of customer counts beyond generic claims, and no independent review ratings. Open questions remain about the specifics of the security architecture and the full scope of AI agent capabilities.
Sources, method, and limitations
Evidence inventory, collection method, provider use, and constraints.
This report is based on 15 collected pages from phase.dev, including the homepage, pricing, integrations, and changelog pages. The evidence catalog includes 180 items, with 15 pages fully collected via static and browser rendering rendering. External proof search was enabled but only verified the existence of linked results, not their content. Limitations include potential marketing bias from vendor pages and lack of independent verification of claims.
- Official Websitehttps://phase.dev/Verified
- Pricing Pagehttps://phase.dev/pricing/Verified
- Pricing Pagehttps://phase.dev/blog/2026-pricing-updates/Verified
- Documentationhttps://phase.dev/integrations/Verified
- Documentationhttps://phase.dev/changelog/aws-sm-integration/Verified
- Documentationhttps://phase.dev/changelog/github-actions-integration/Verified
- Documentationhttps://phase.dev/changelog/gitlab-ci-integration/Verified
- Documentationhttps://phase.dev/changelog/hashicorp-nomad-integration/Verified
- Documentationhttps://phase.dev/changelog/hashicorp-vault-integration/Verified
- Documentationhttps://phase.dev/changelog/integrations/Verified
- Documentationhttps://phase.dev/changelog/public-api/Verified
- Documentationhttps://phase.dev/changelog/railway-integration/Verified
- Documentationhttps://phase.dev/changelog/vercel-integration/Verified
- Documentationhttps://phase.dev/changelog/tag/api/Verified
- Documentationhttps://phase.dev/changelog/tag/integrations/Verified
- Articlehttps://phase.dev/blog/starting-phaseVerified
- Articlehttps://phase.dev/blog/speedrun-soc2/Verified
- Articlehttps://phase.dev/blog/Verified
- Articlehttps://phase.dev/blog/what-is-secrets-management/Verified
- Articlehttps://docs.phase.dev/consoleVerified
- Articlehttps://phase.dev/blog/announcing-pre-seed/Verified
- Articlehttps://phase.dev/changelog/Verified